

fibratus
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
defensive-toolsforensicsincident-response+3
rabbitstack/fibratusSecurity sensor for realtime threat detection and protection
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 volatilityfoundation/community
Community-maintained Volatility plugin collection for memory forensics, extending memory dump analysis with modules for malware and process…
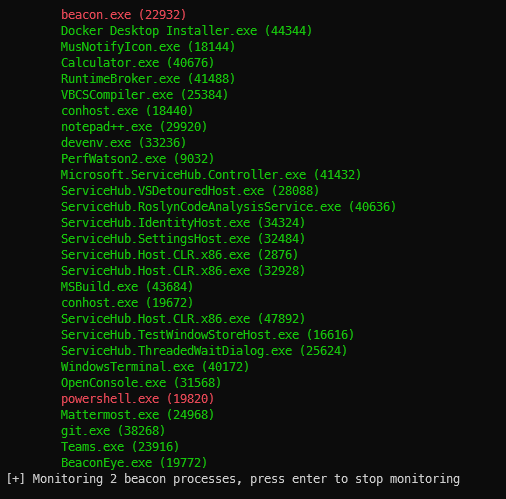 ccob/beaconeye
Hunts out CobaltStrike beacons and logs operator command output
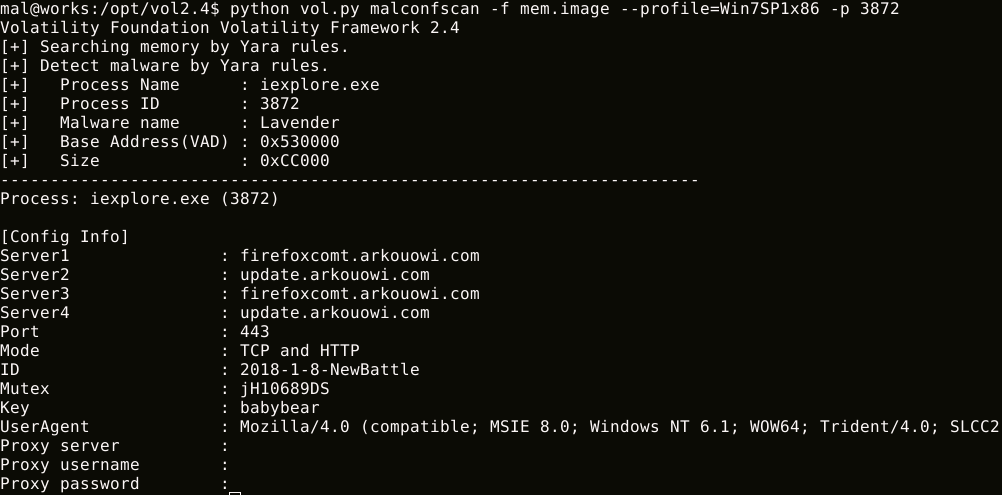 jpcertcc/malconfscan
Volatility plugin for extracts configuration data of known malware
 marcosd4h/memhunter
Live hunting of code injection techniques
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 bohops/rogueassemblyhunter
Rogue Assembly Hunter is a utility for discovering 'interesting' .NET CLR modules in running processes.
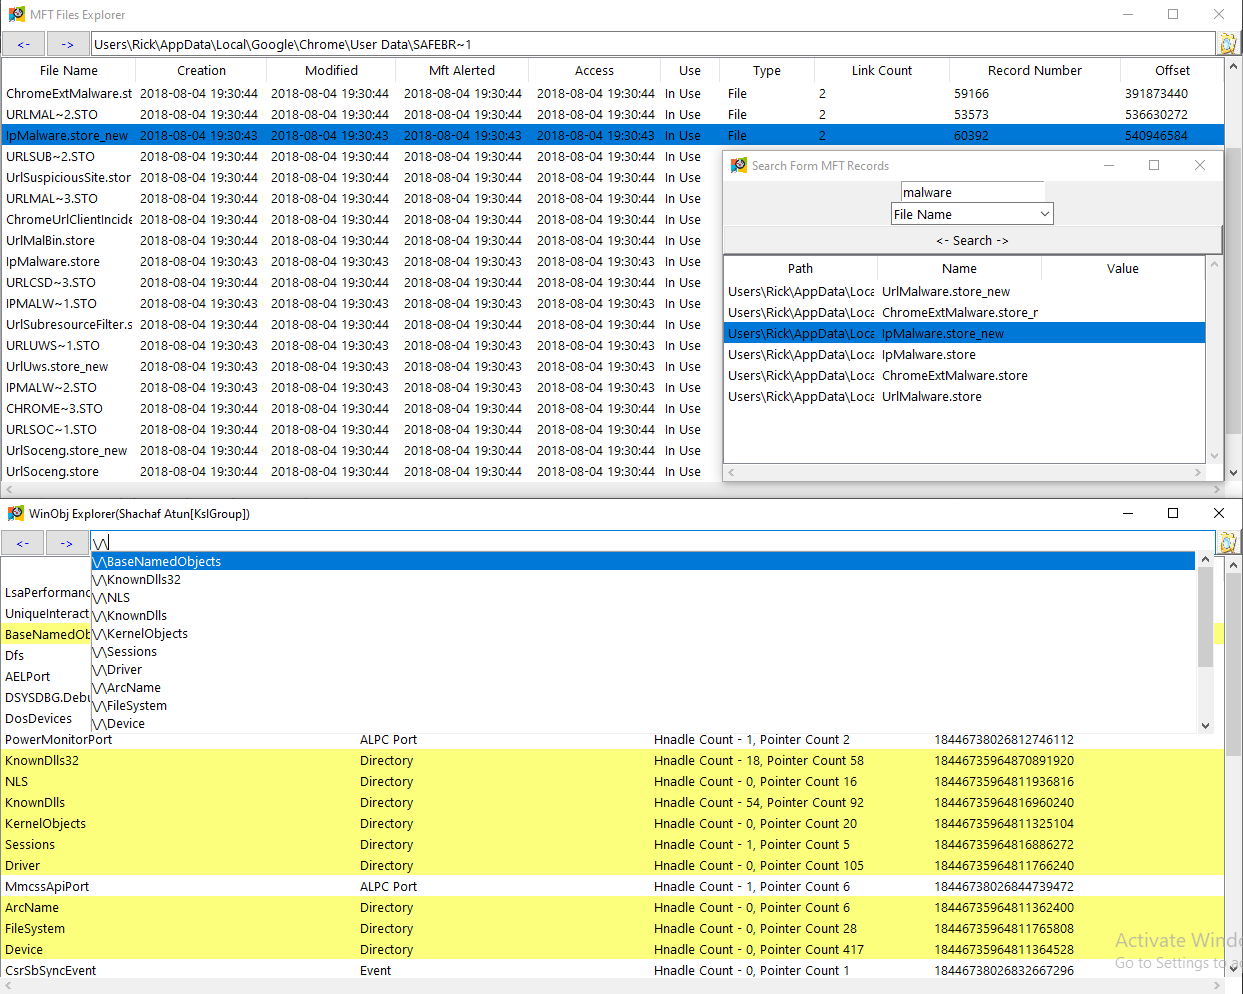 memoryforensics1/volexp
volatility explorer (volatility 2)
 opensourcesec/cirtkit
Tools for the Computer Incident Response Team :computer:
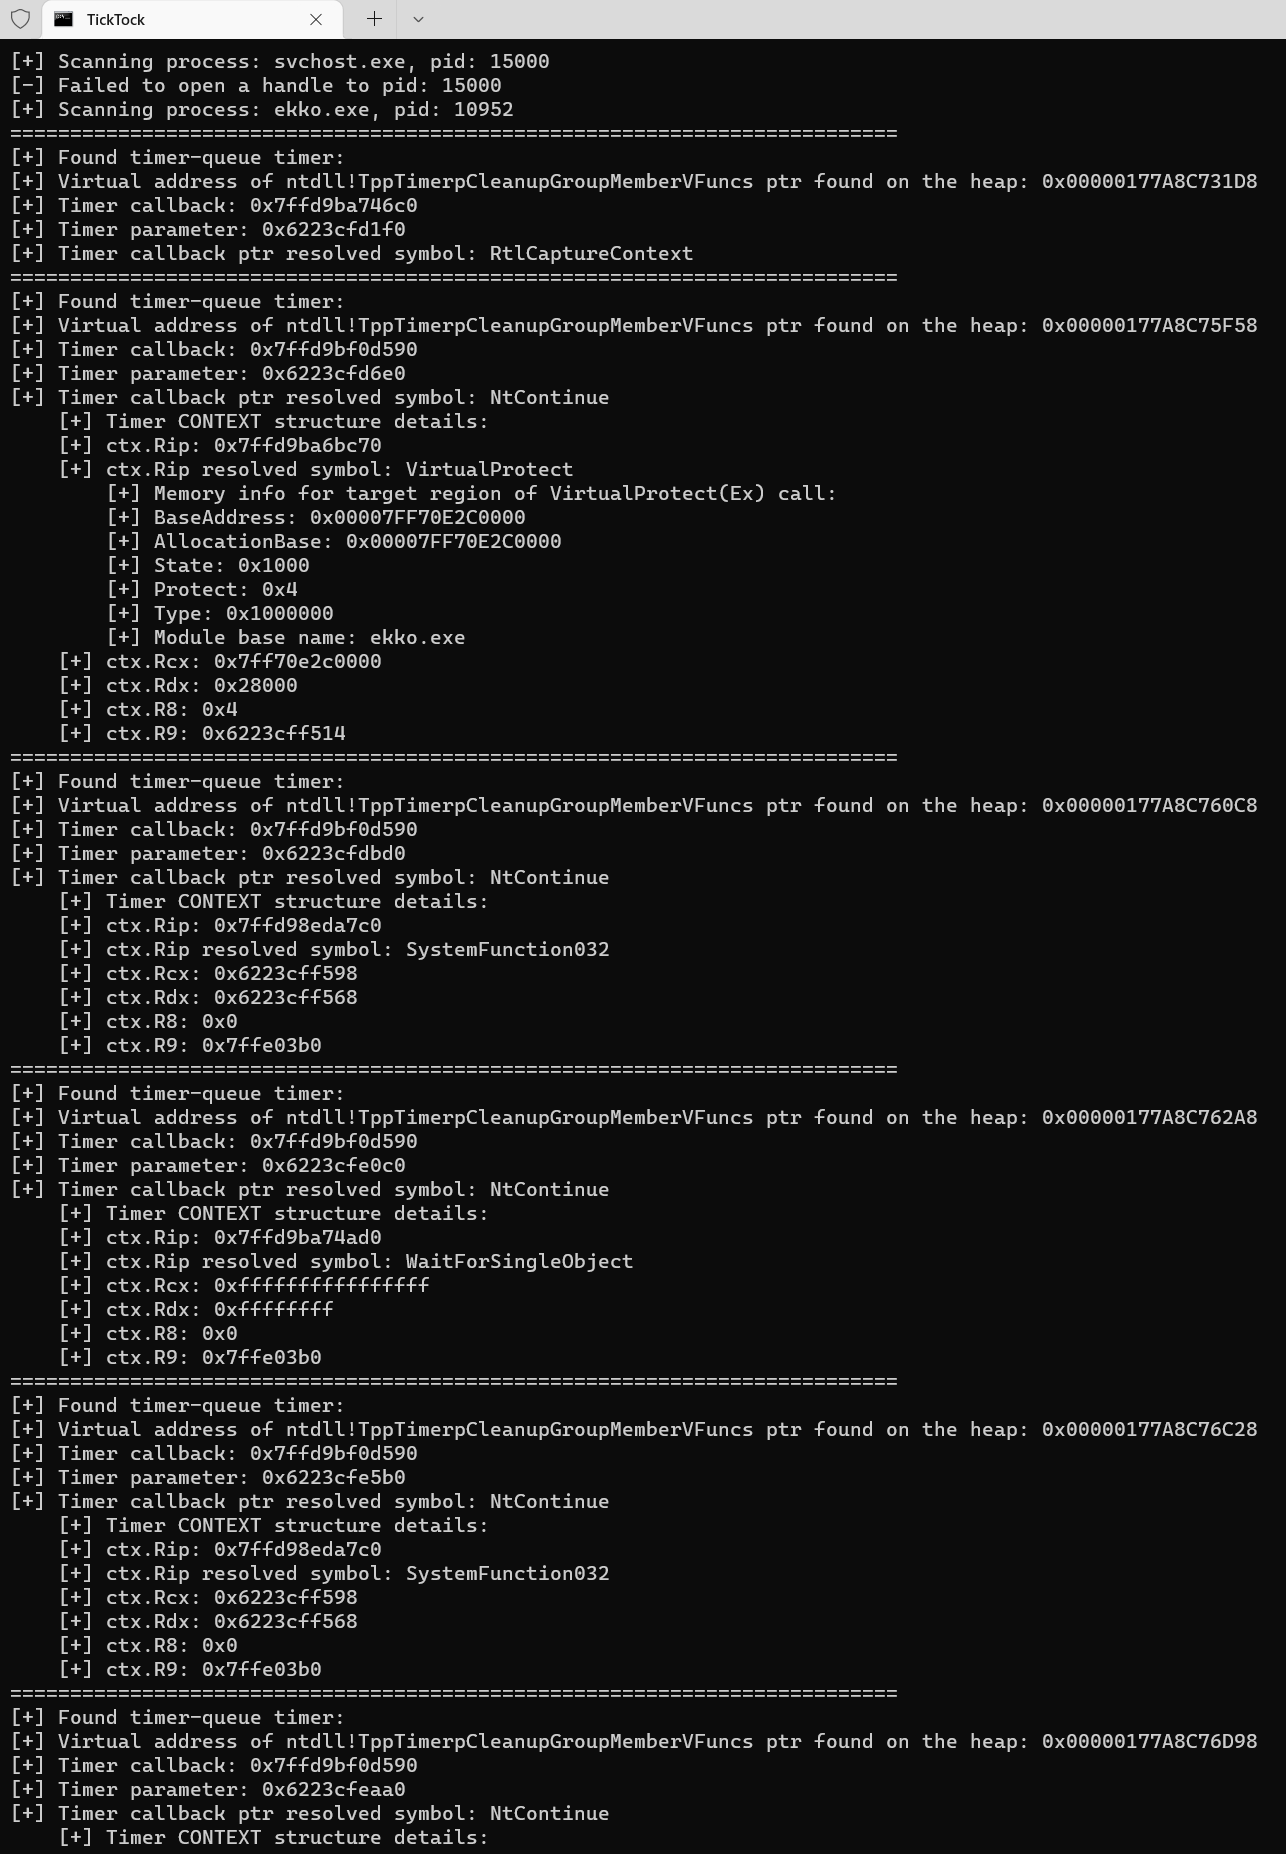 withsecurelabs/ticktock
Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…
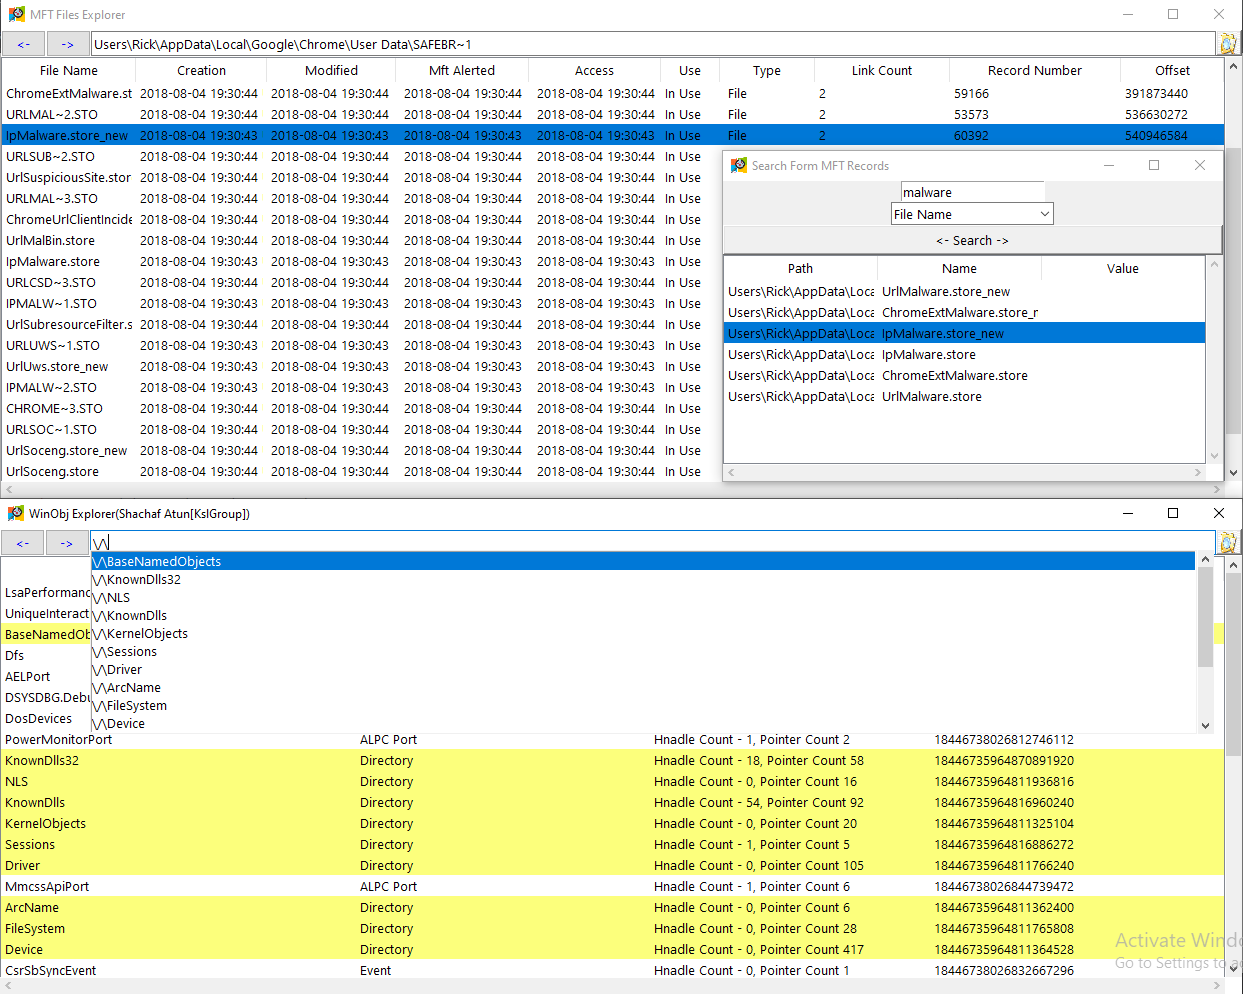 memoryforensics1/vol3xp
Volatility Explorer Suit (volatility 3)
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…