Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
ImageMagick-CVE-2017-15277 preview

ImageMagick-CVE-2017-15277

GitHubhexrom/imagemagick-cve-2017-15277

Proof-of-concept exploit for ImageMagick CVE-2017-15277 memory leak vulnerability, designed for use with the gifoeb fuzzing framework.
binary-analysisexploitationfuzzing+2
5
6 years ago
CVE-2014-4481 preview

CVE-2014-4481

GitHubfeliam/cve-2014-4481

Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…
binary-exploitationexploitationios-security+3
511 years ago
chakra-exploit-framework preview

chakra-exploit-framework

GitHubntdelta/chakra-exploit-framework

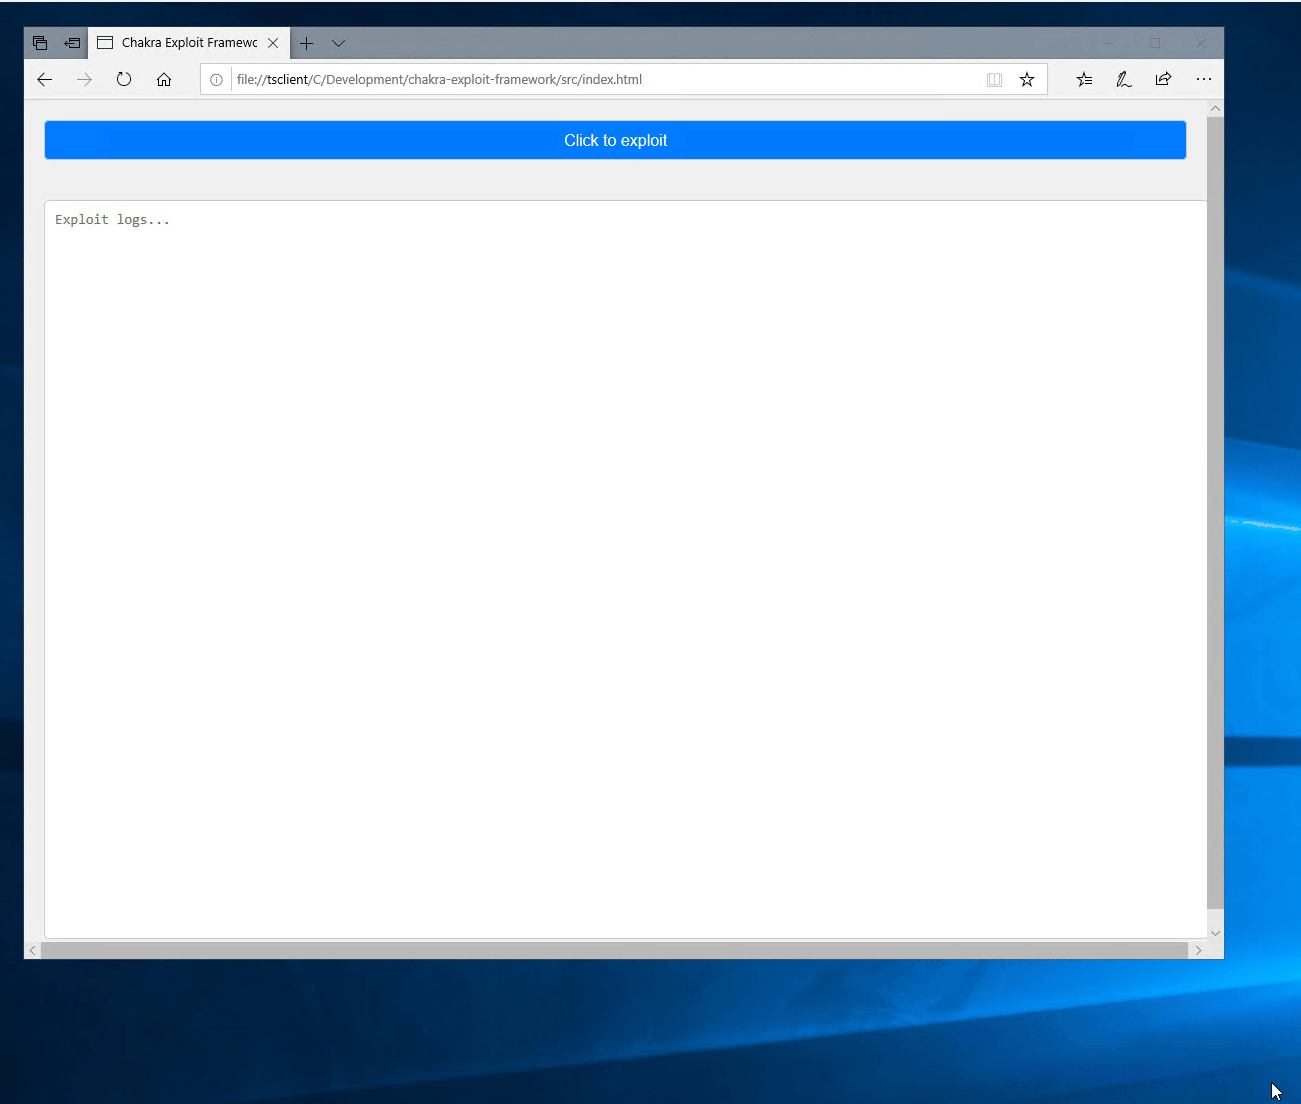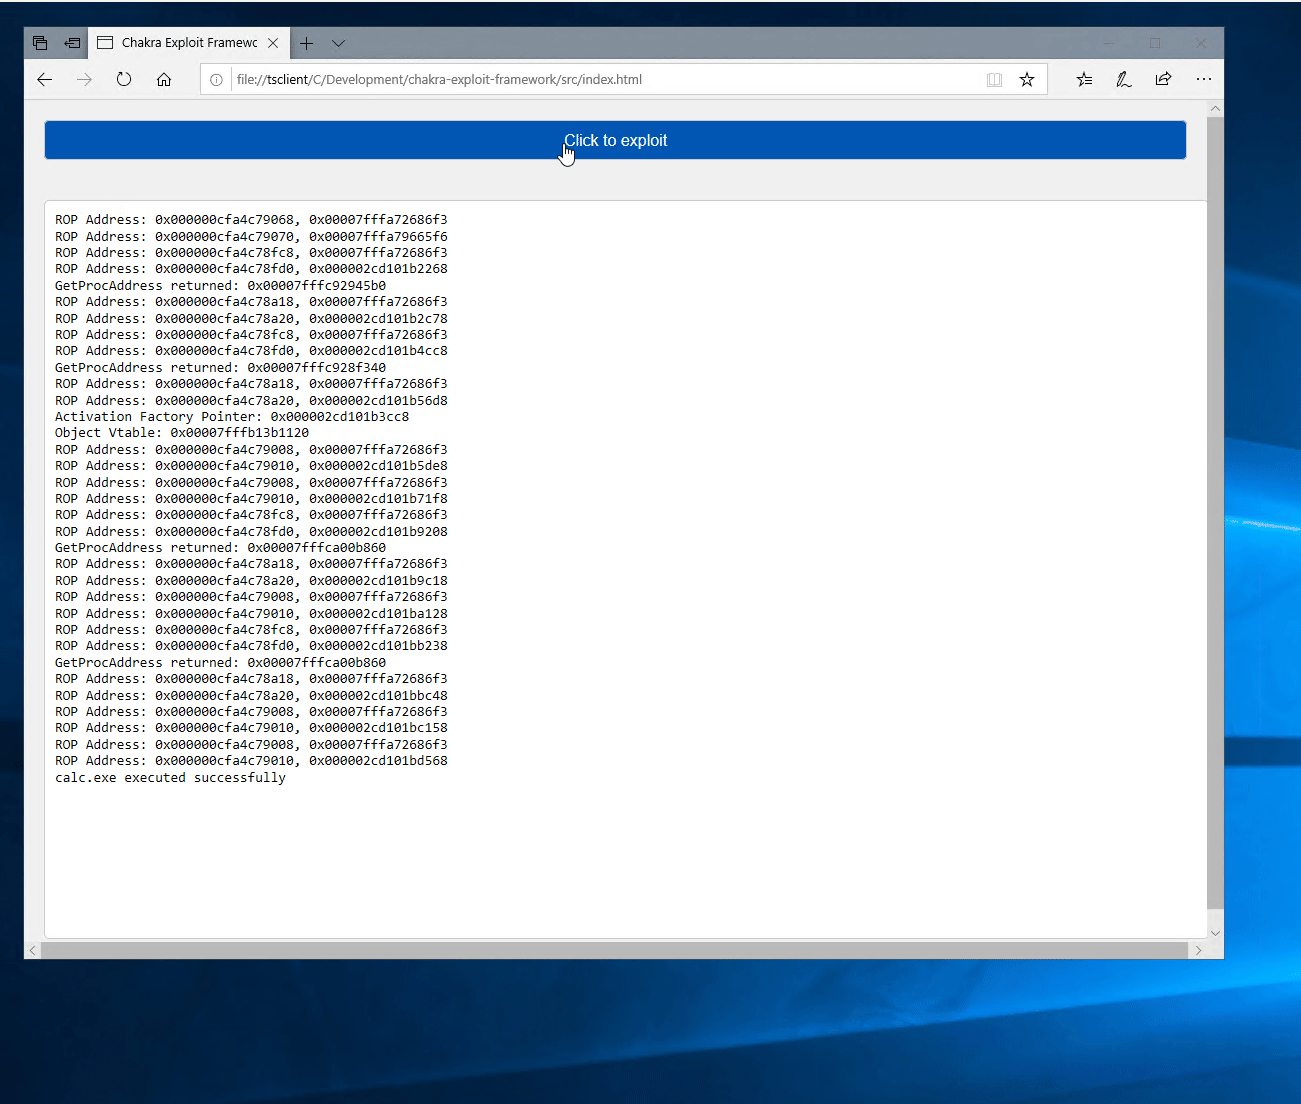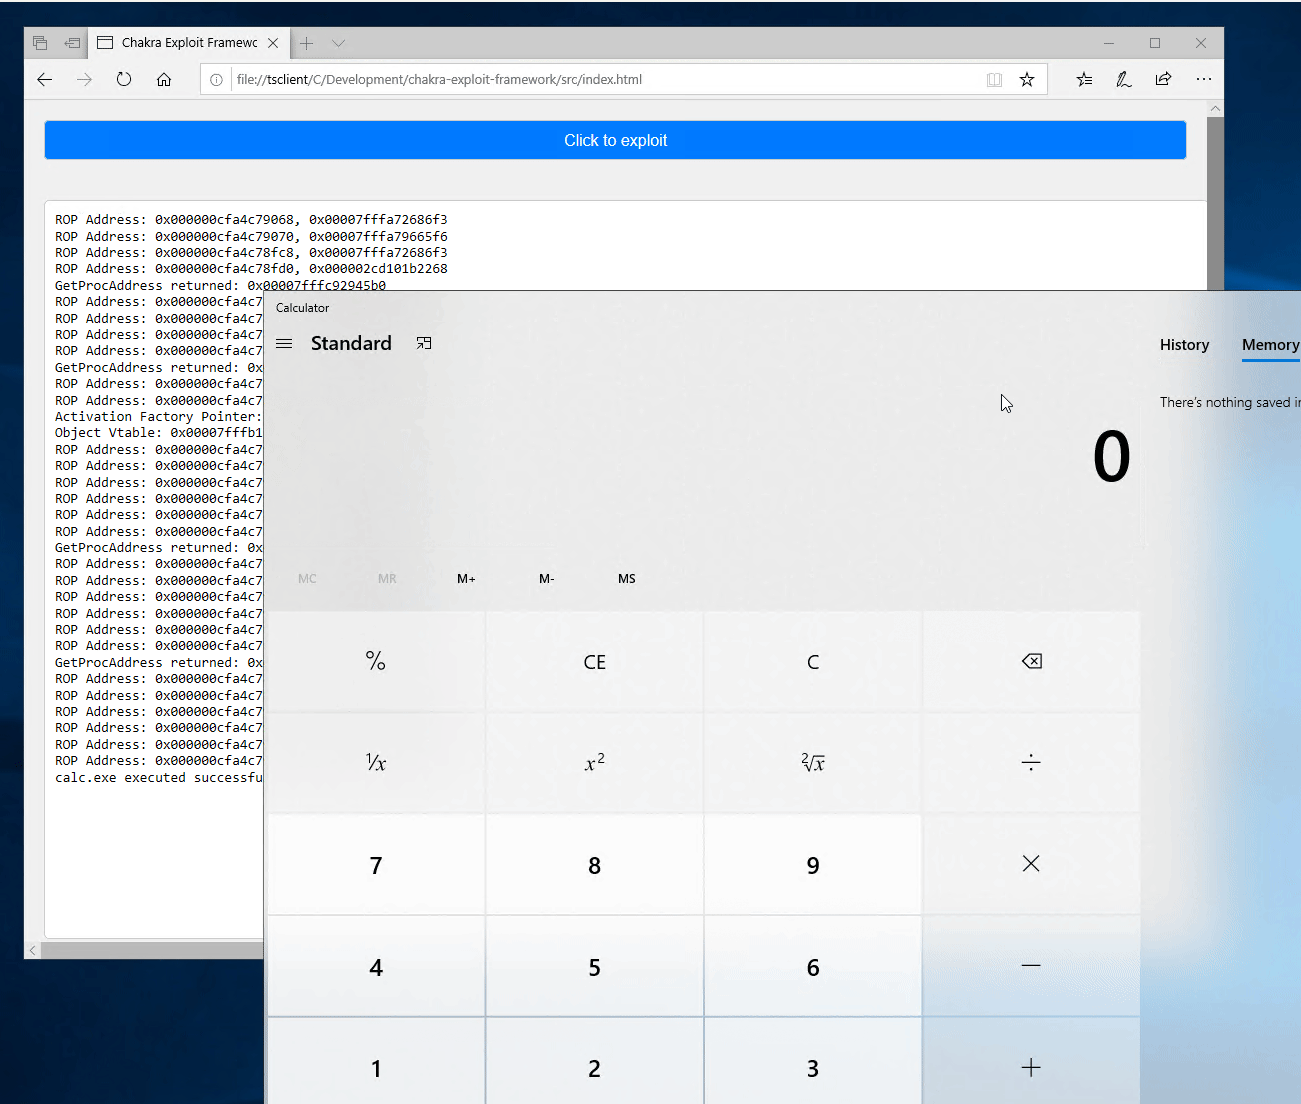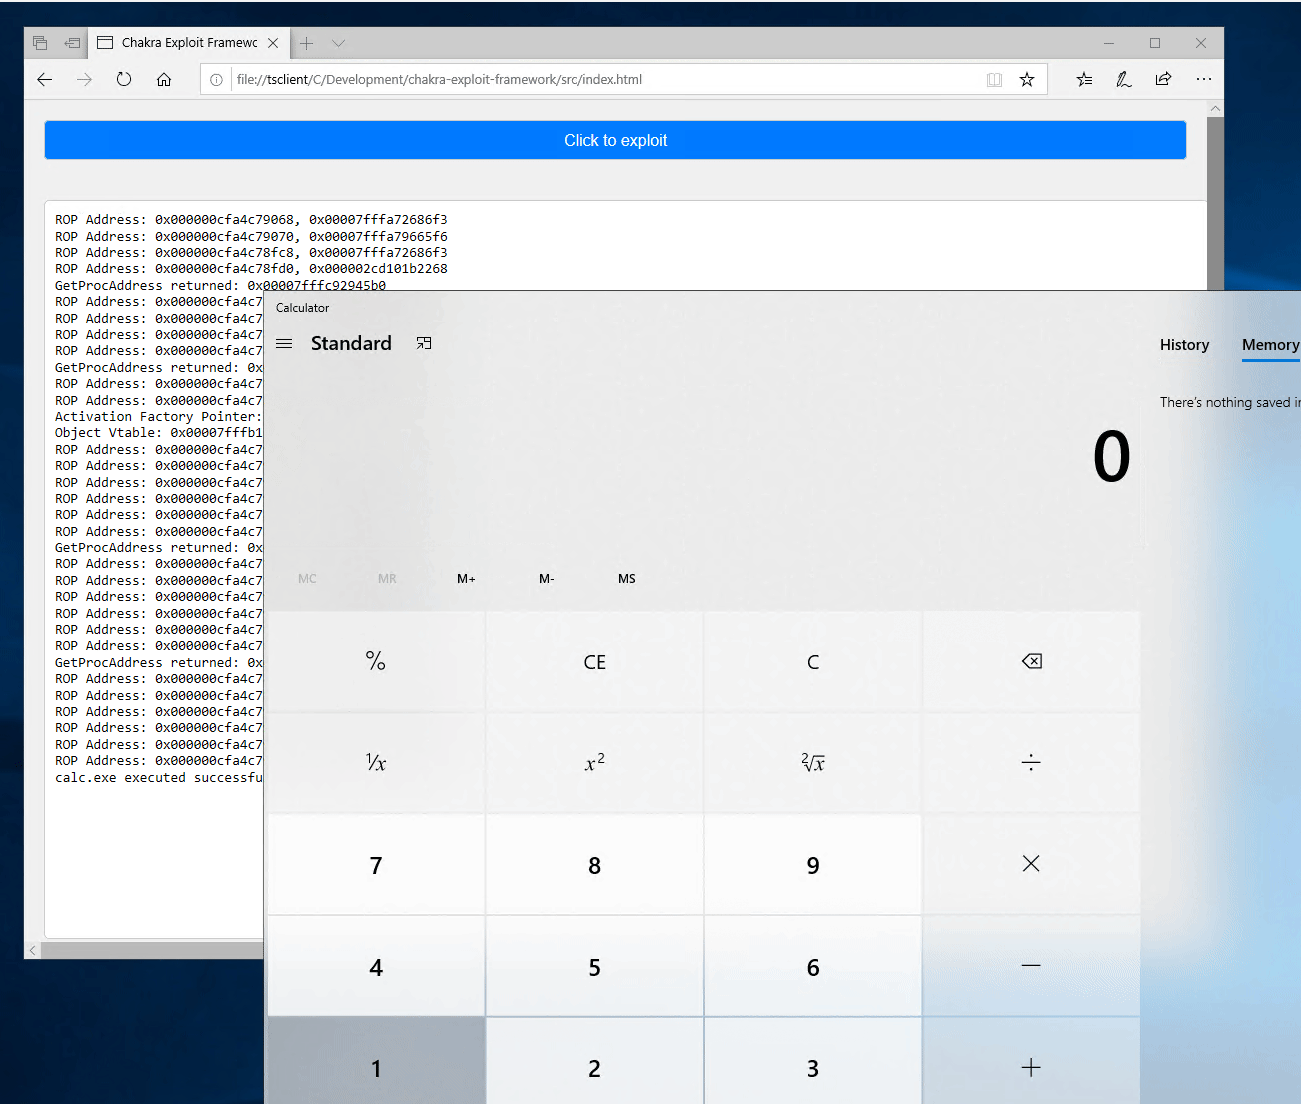
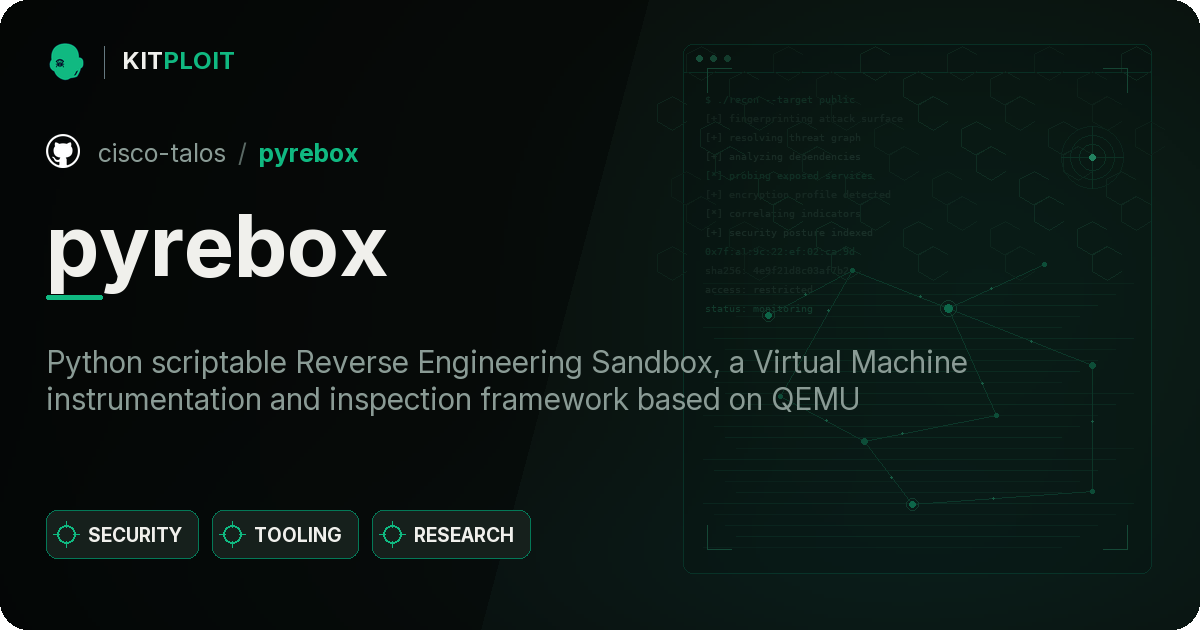
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
binary-exploitationeducationexploit-frameworks+6
11 year ago
pyrebox preview
Archived

pyrebox

GitHubcisco-talos/pyrebox

Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU

binary-analysisdebuggersdigital-forensics+5
1.7k2 years ago
rekall preview
Archived

rekall

GitHubgoogle/rekall

Rekall Memory Forensic Framework

digital-forensicsforensicsincident-response+3
2.0k5 years ago
angr preview

angr

GitHubangr/angr

A powerful and user-friendly binary analysis platform!
ai-assisted-reversingbinary-analysisbinary-exploitation+12
9.2k1 day ago
StegoForge preview

StegoForge

GitHubnour833/stegoforge

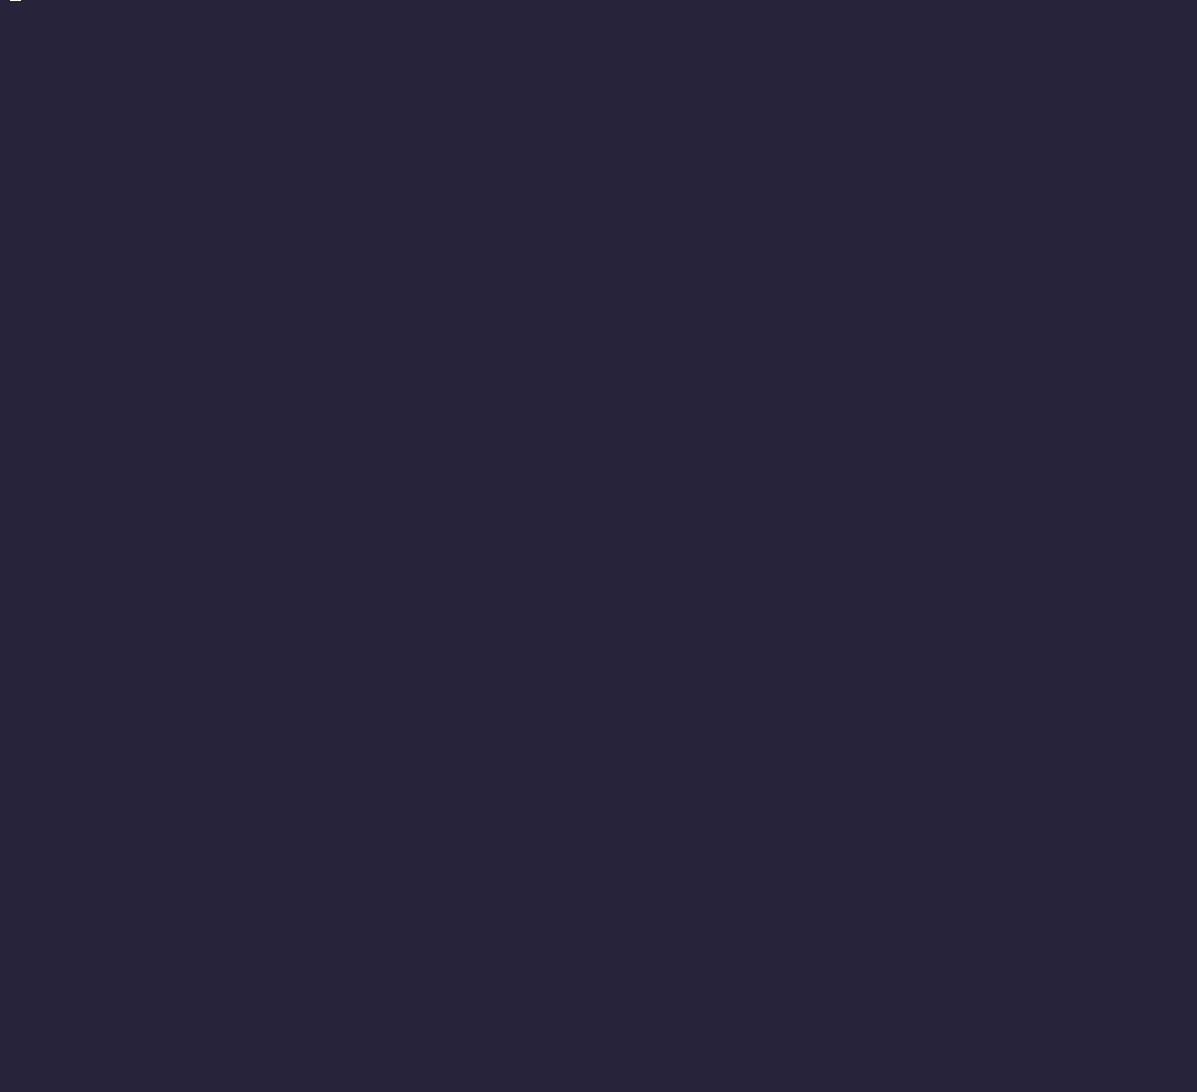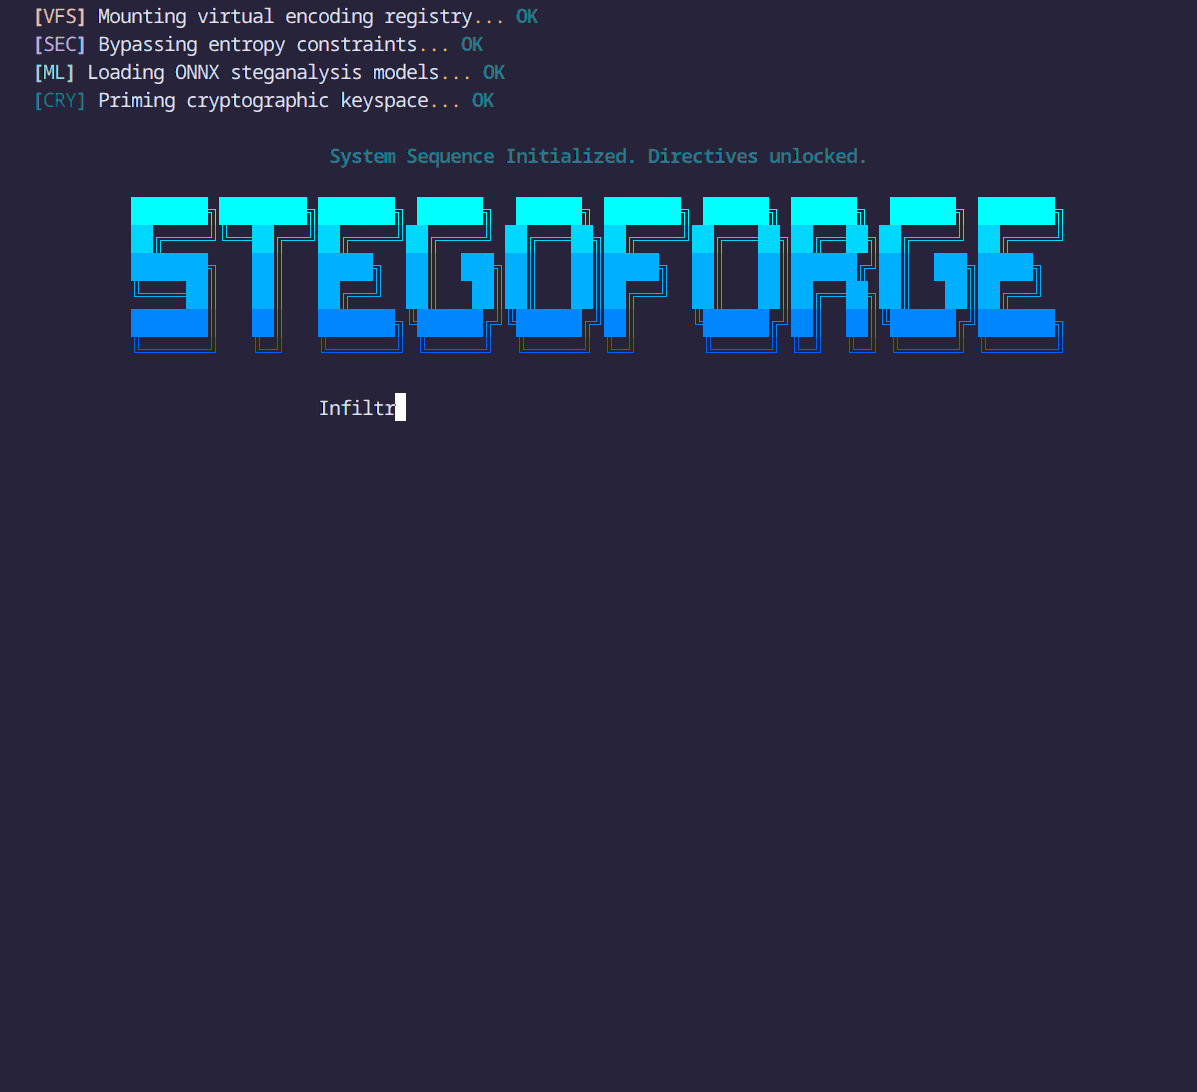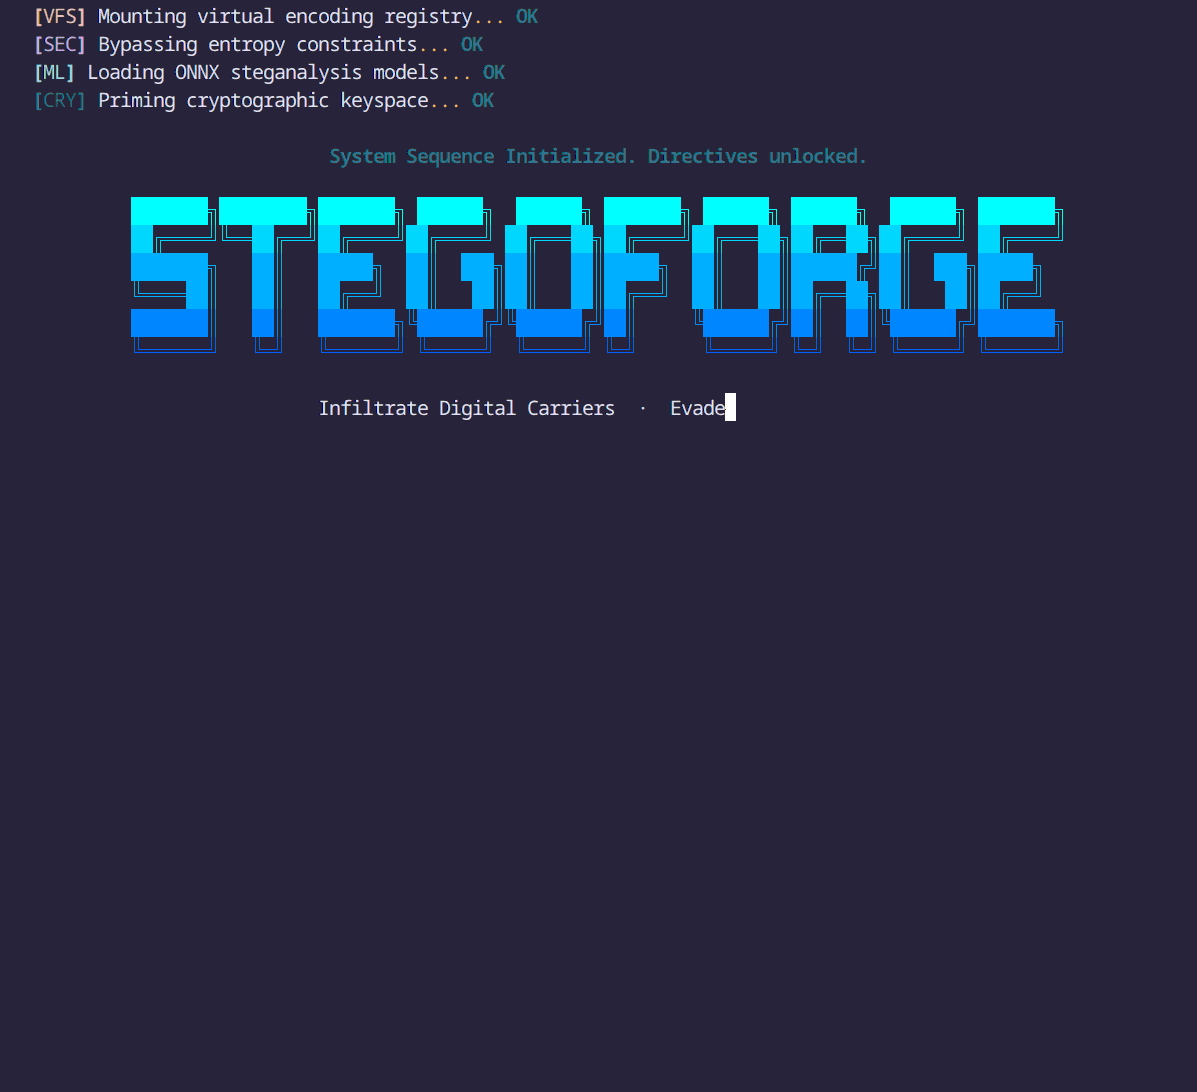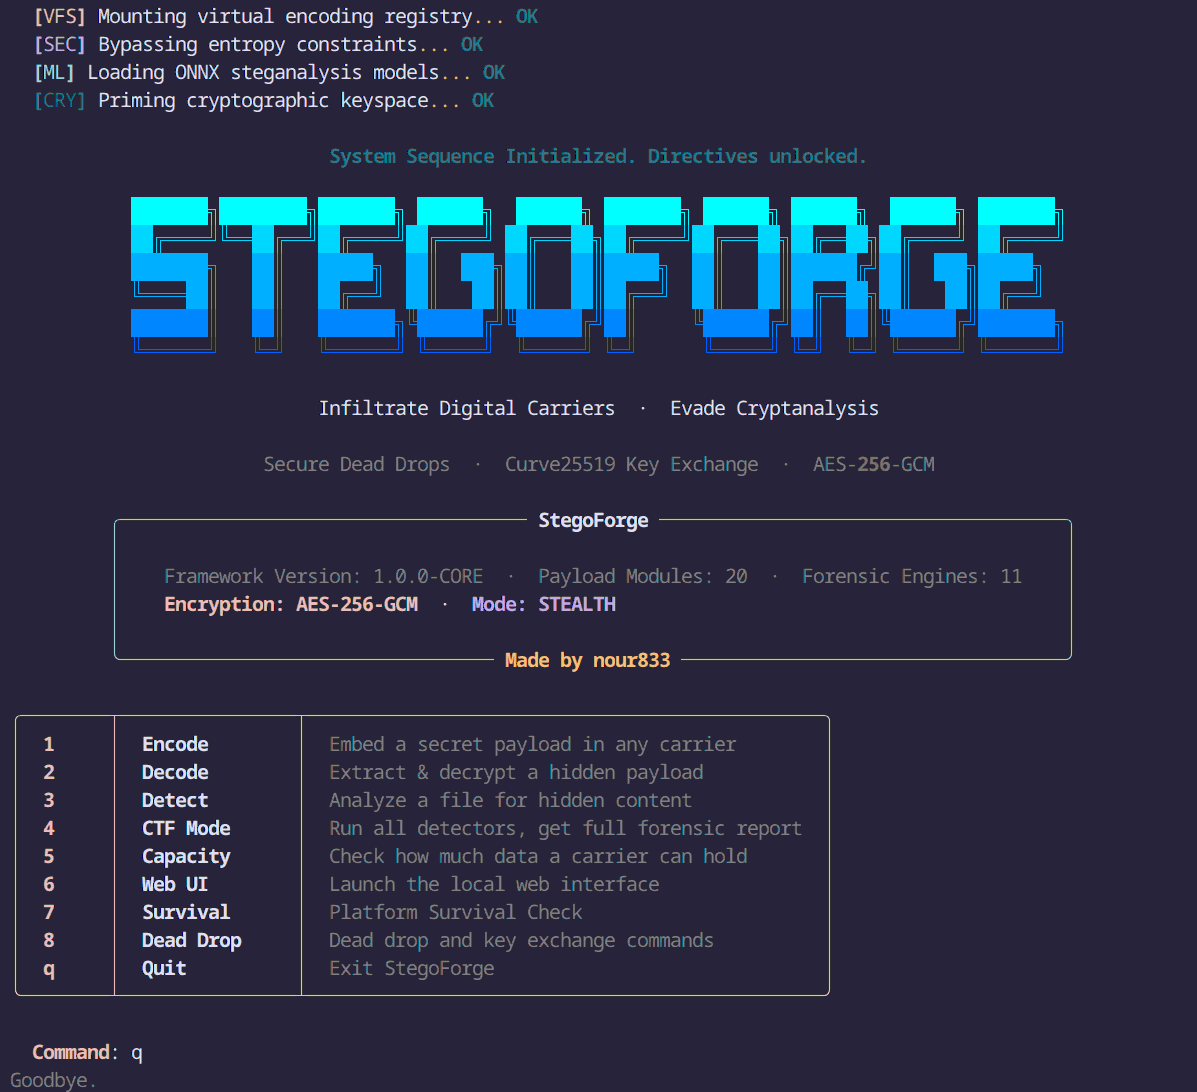
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
cryptographyctfdata-exfiltration+8
5985 months ago
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
19610 days ago
CVE-2025-43300 preview

CVE-2025-43300

GitHubhunters-sec/cve-2025-43300

This is POC for IOS 0click CVE-2025-43300
binary-exploitationeducationembedded-systems-security+7
1191 year ago
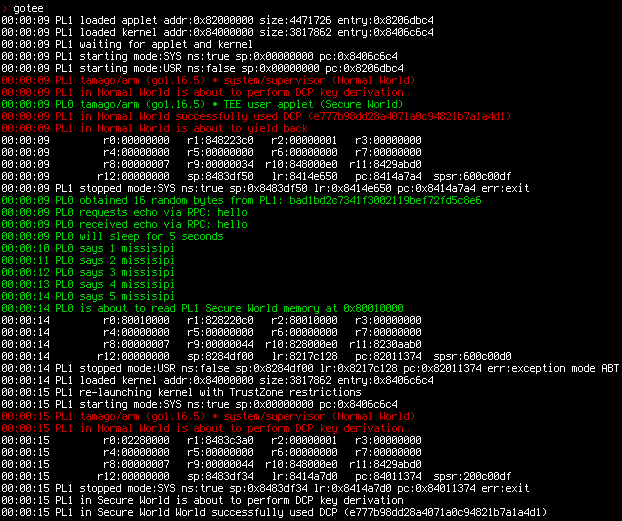
GoTEE-example preview

GoTEE-example

GitHubusbarmory/gotee-example

GoTEE - example application
debuggersembedded-systems-securityhardware-security+2
1721 days ago
CVE-2025-31200 preview

CVE-2025-31200

GitHubhunters-sec/cve-2025-31200

IOS audio buffer overflow CVE-2025-31200 POC
binary-exploitationeducationexploitation+6
121 year ago
CVE-2022-26711 preview

CVE-2022-26711

GitHubxpcmdshell/cve-2022-26711

Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
binary-exploitationexploitationfuzzing+3
49 months ago
CVE-2025 preview

CVE-2025

GitHubdark-life944/cve-2025

This is POC for IOS 0click CVE-2025-43300

binary-exploitationeducationexploitation+3
11 year ago
lithium-kernel preview

lithium-kernel

GitHubgmh5225/lithium-kernel

Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
anti-botbinary-exploitationmemory-forensics+1
2 months ago
ThreadStackSpoofer preview

ThreadStackSpoofer

GitHubmgeeky/threadstackspoofer

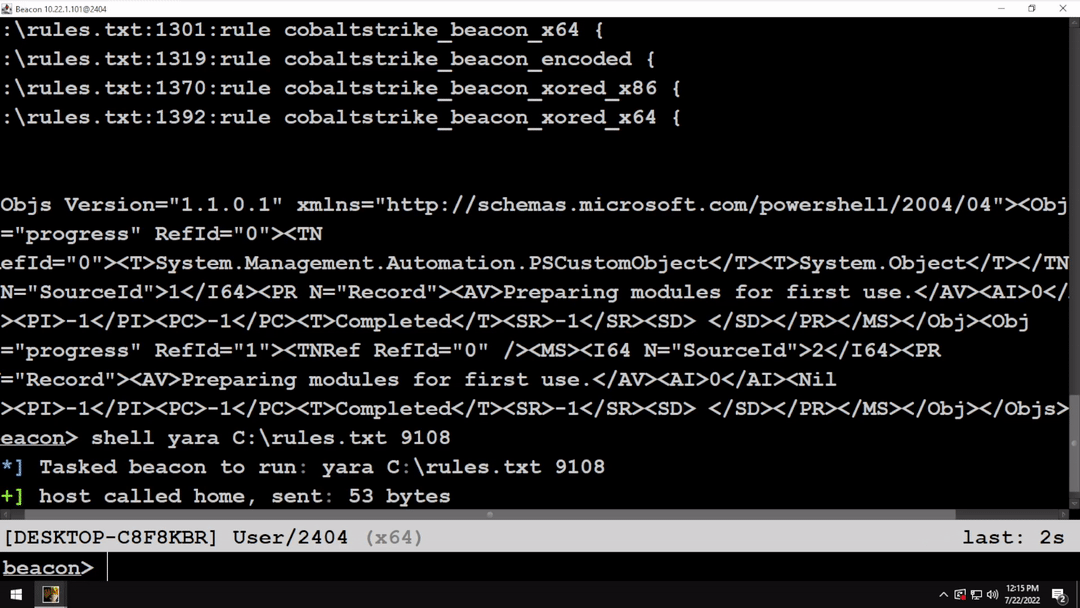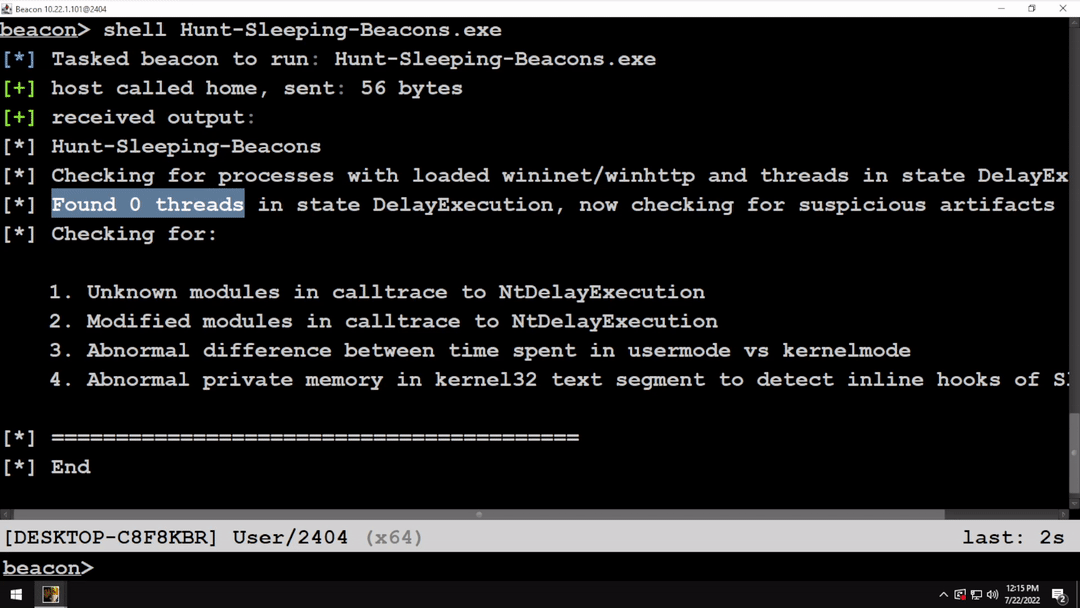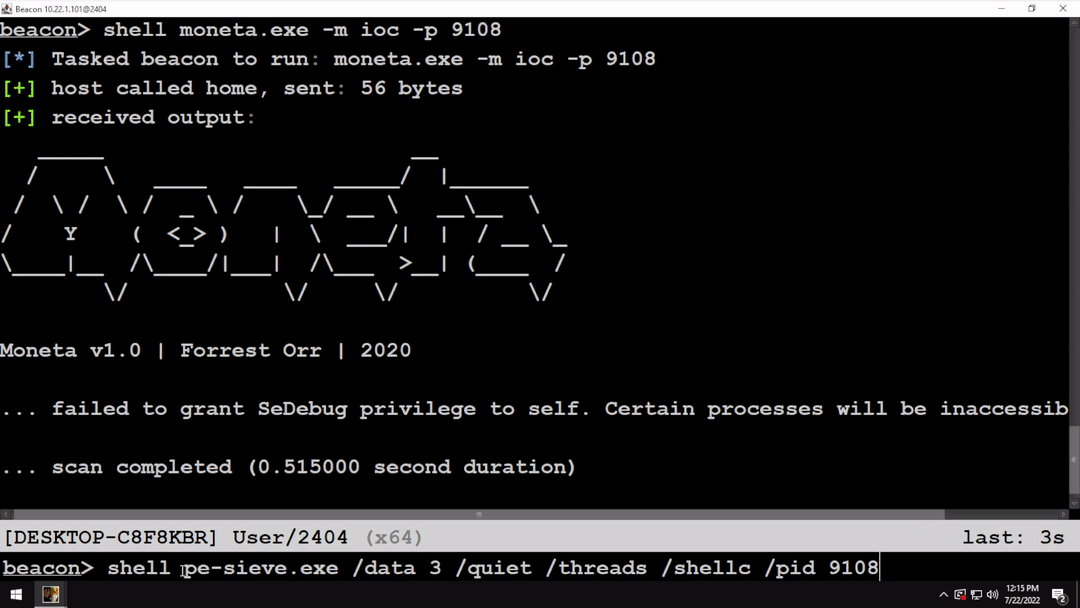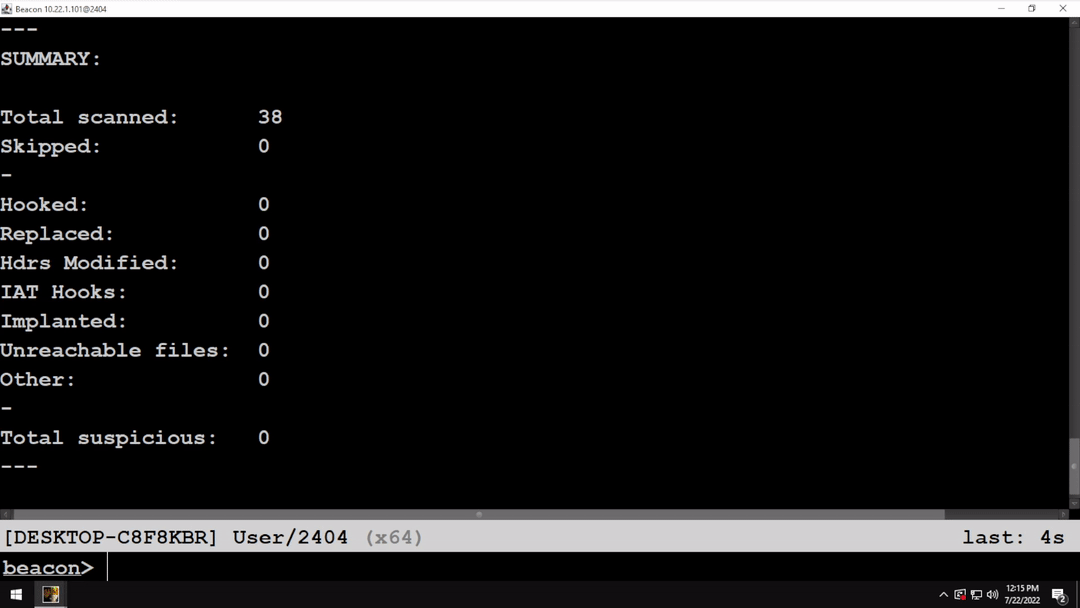
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
exploit-frameworksmalware-analysismemory-forensics+4
1.3k4 years ago
AceLdr preview

AceLdr

GitHubkyleavery/aceldr

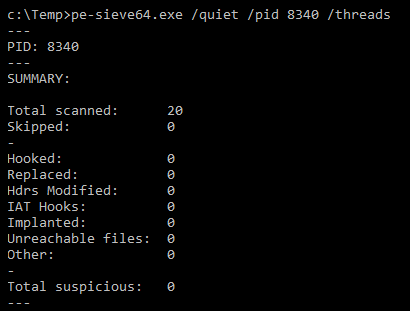
Cobalt Strike UDRL for memory scanner evasion.
exploit-frameworksmemory-forensicspayload-development+2
1.0k3 years ago
Shelter preview

Shelter

GitHubkudaes/shelter

ROP-based sleep obfuscation to evade memory scanners
exploit-frameworksmemory-forensicsred-teaming
3921 year ago
Astral_Projection preview

Astral_Projection

GitHubkuwaitist/astral_projection

Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…

exploit-frameworksmemory-forensicspayload-development+4
735 months ago
Previous123Next