
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
107 results
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

digital-forensicsforensicsincident-response+3
1.4k1 month ago
avml preview

avml

GitHubmicrosoft/avml

Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
digital-forensicsforensicsincident-response+1
1.1k12 days ago
inception preview

inception

GitHubcarmaa/inception

Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
digital-forensicsexploitationhardware-security+6
1.6k1 year ago
3snake preview

3snake

GitHubblendin/3snake

Tool for extracting information from newly spawned processes
data-exfiltrationmemory-forensicspassword-attacks+4
7911 year ago
extractTVpasswords preview

extractTVpasswords

GitHubvah13/extracttvpasswords

tool to extract passwords from TeamViewer memory using Frida

exploitationmemory-forensicspassword-cracking+3
4638 years ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
digital-forensicsforensicsioc-management+3
8392 years ago
apk-medit preview

apk-medit

GitHubsterrasec/apk-medit

memory search and patch tool on debuggable apk without root & ndk
android-securitybinary-analysismemory-forensics+2
4311 month ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

digital-forensicsdisk-forensicsforensics+3
5215 years ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
2188 years ago
RansomLord preview

RansomLord

GitHubmalvuln/ransomlord

RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…

binary-exploitationdefensive-toolsexploitation+4
5161 year ago
asatools preview

asatools

GitHubnccgroup/asatools

Main repository to pull all NCC Group Cisco ASA-related tool projects.
binary-analysisdebuggersembedded-systems-security+3
2388 years ago
dfirtriage preview

dfirtriage

GitHubtravisfoley/dfirtriage

Digital forensic acquisition tool for Windows based incident response.
digital-forensicsforensicsincident-response+1
3482 years ago
MemITM preview

MemITM

GitHubamossys/memitm

Tool to make in memory man in the middle
binary-analysisdebuggersdynamic-analysis-sandboxing+4
1268 years ago
Platbox preview

Platbox

GitHubioactive/platbox

Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…

binary-analysisfirmware-analysisfuzzing+3
2211 year ago
LsassReflectDumping preview

LsassReflectDumping

GitHuboffensive-panda/lsassreflectdumping

This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
memory-forensicspassword-attackspost-exploitation+1
2202 years ago
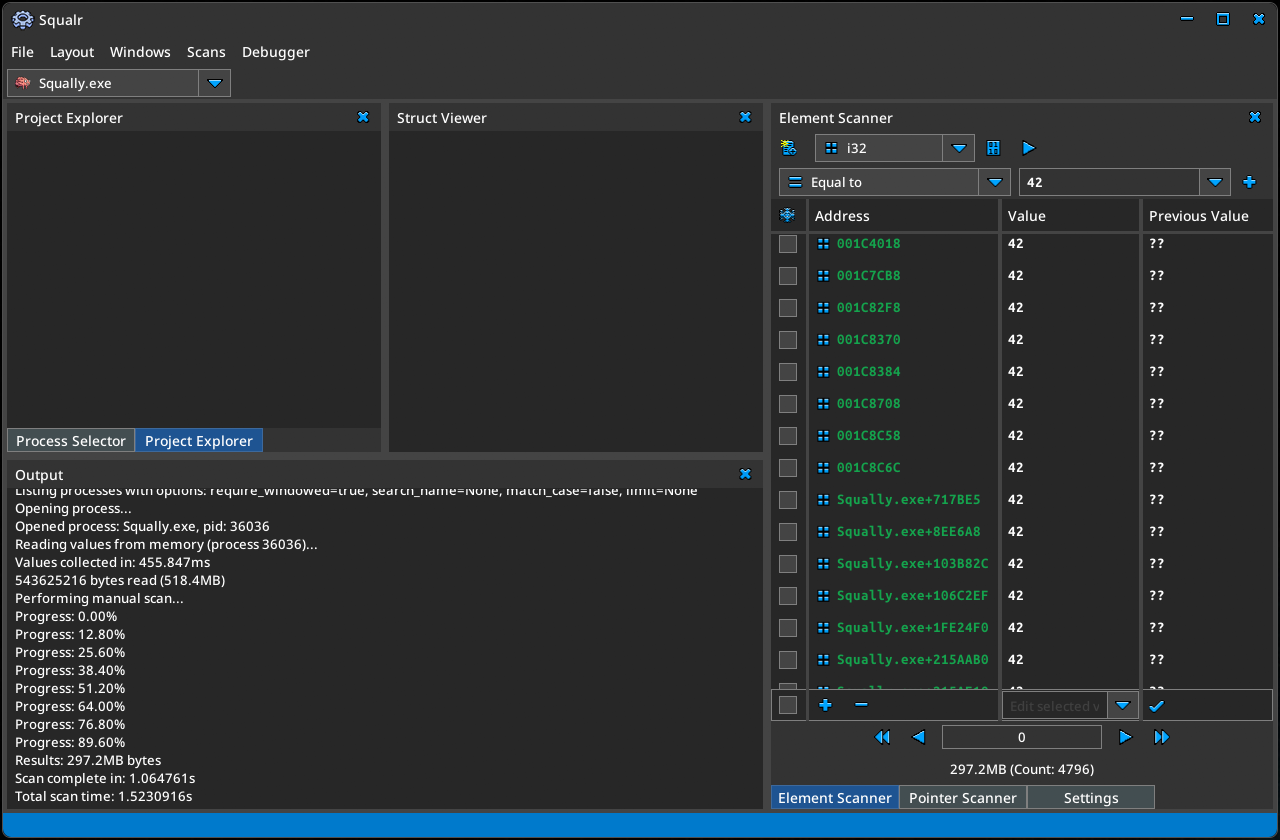
Squalr preview

Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.

binary-analysisdebuggersdynamic-analysis-sandboxing+5
1514 months ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
binary-analysisdebuggersdynamic-code-analysis+6
8217 days ago
ipa-medit preview

ipa-medit

GitHubsterrasec/ipa-medit

Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.

binary-analysisios-securitymemory-forensics+3
2071 year ago
Previous123456Next