

GhostKatz
 rainbowdynamix/ghostkatz
Dump LSASS via physical memory read primitives in vulnerable kernel drivers
binary-exploitationexploitationmemory-forensics+4
338
rainbowdynamix/ghostkatzDump LSASS via physical memory read primitives in vulnerable kernel drivers
 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 nccgroup/asatools
Main repository to pull all NCC Group Cisco ASA-related tool projects.
 jas502n/cve-2018-17182
Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
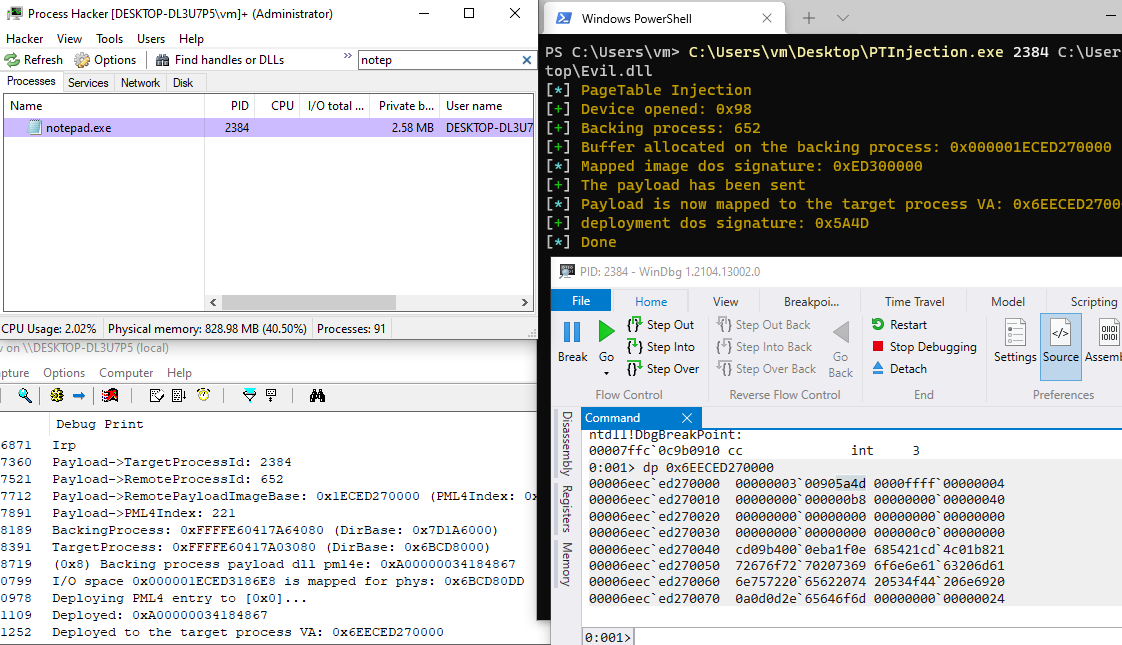 kkent030315/pagetableinjection
Code Injection, Inject malicious payload via pagetables pml4.
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver