

EVENSTAR
 winterknife/evenstar
Intel 64/Windows low-level experiments
binary-analysisbinary-exploitationdebuggers+5
winterknife/evenstarIntel 64/Windows low-level experiments
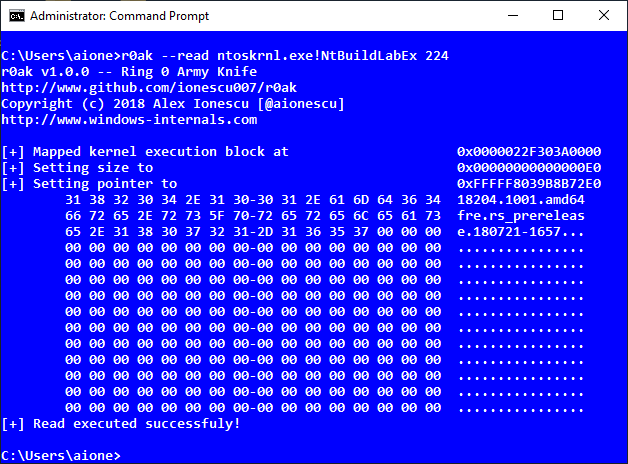 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
 leesh3288/cve-2025-32023
PoC & Exploit for CVE-2025-32023 / PlaidCTF 2025 "Zerodeo"
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
 ynwarcs/cve-2025-21298
Proof of concept & details for CVE-2025-21298
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 h4k6/cve-2023-0179-poc
针对(CVE-2023-0179)漏洞利用 该漏洞被分配为CVE-2023-0179,影响了从5.5到6.2-rc3的所有Linux版本,该漏洞在6.1.6上被测试。 漏洞的细节和文章可以在os-security上找到。
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
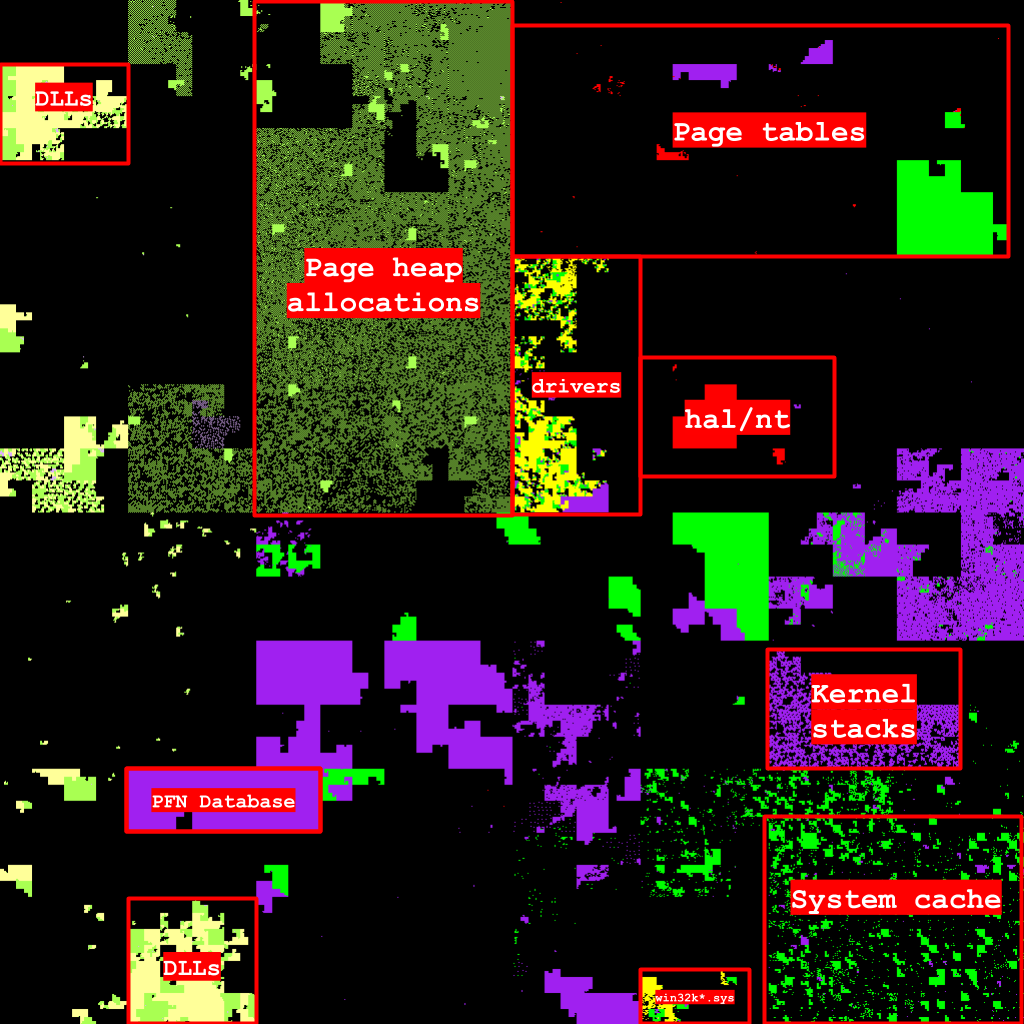 0vercl0k/clairvoyance
Visualize the virtual address space of a Windows process on a Hilbert curve.
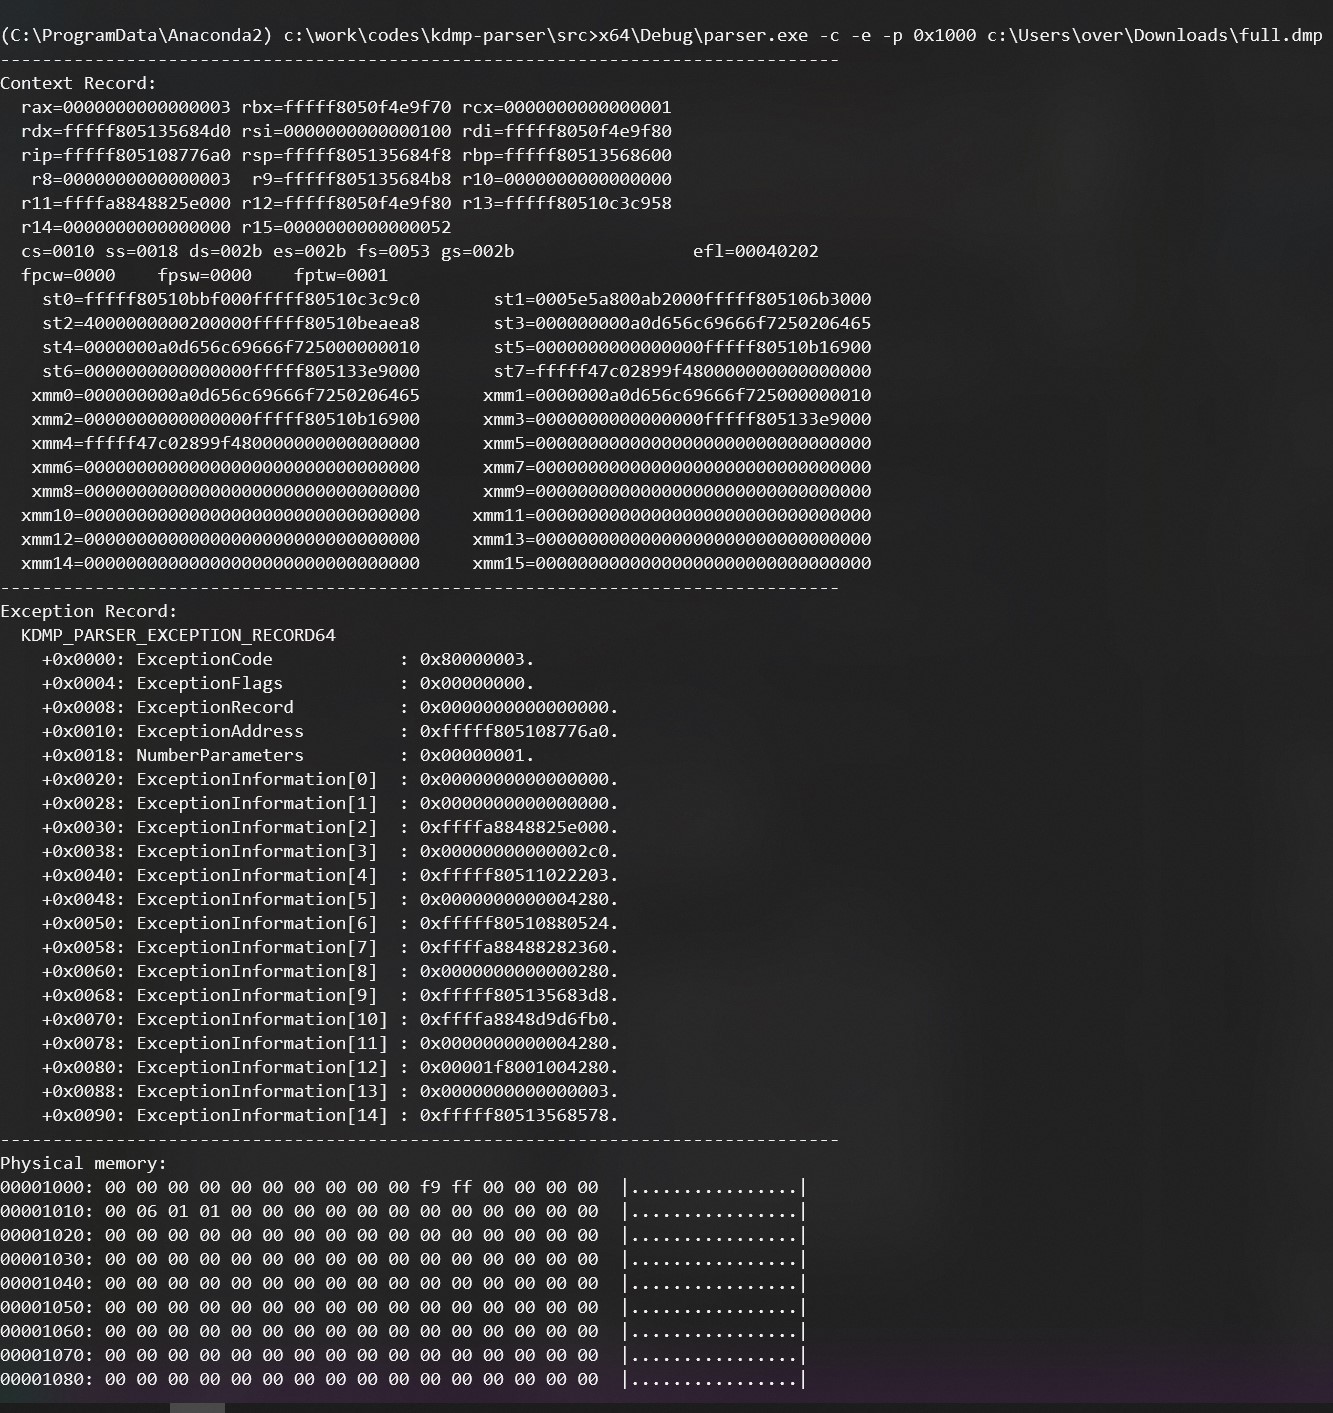 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
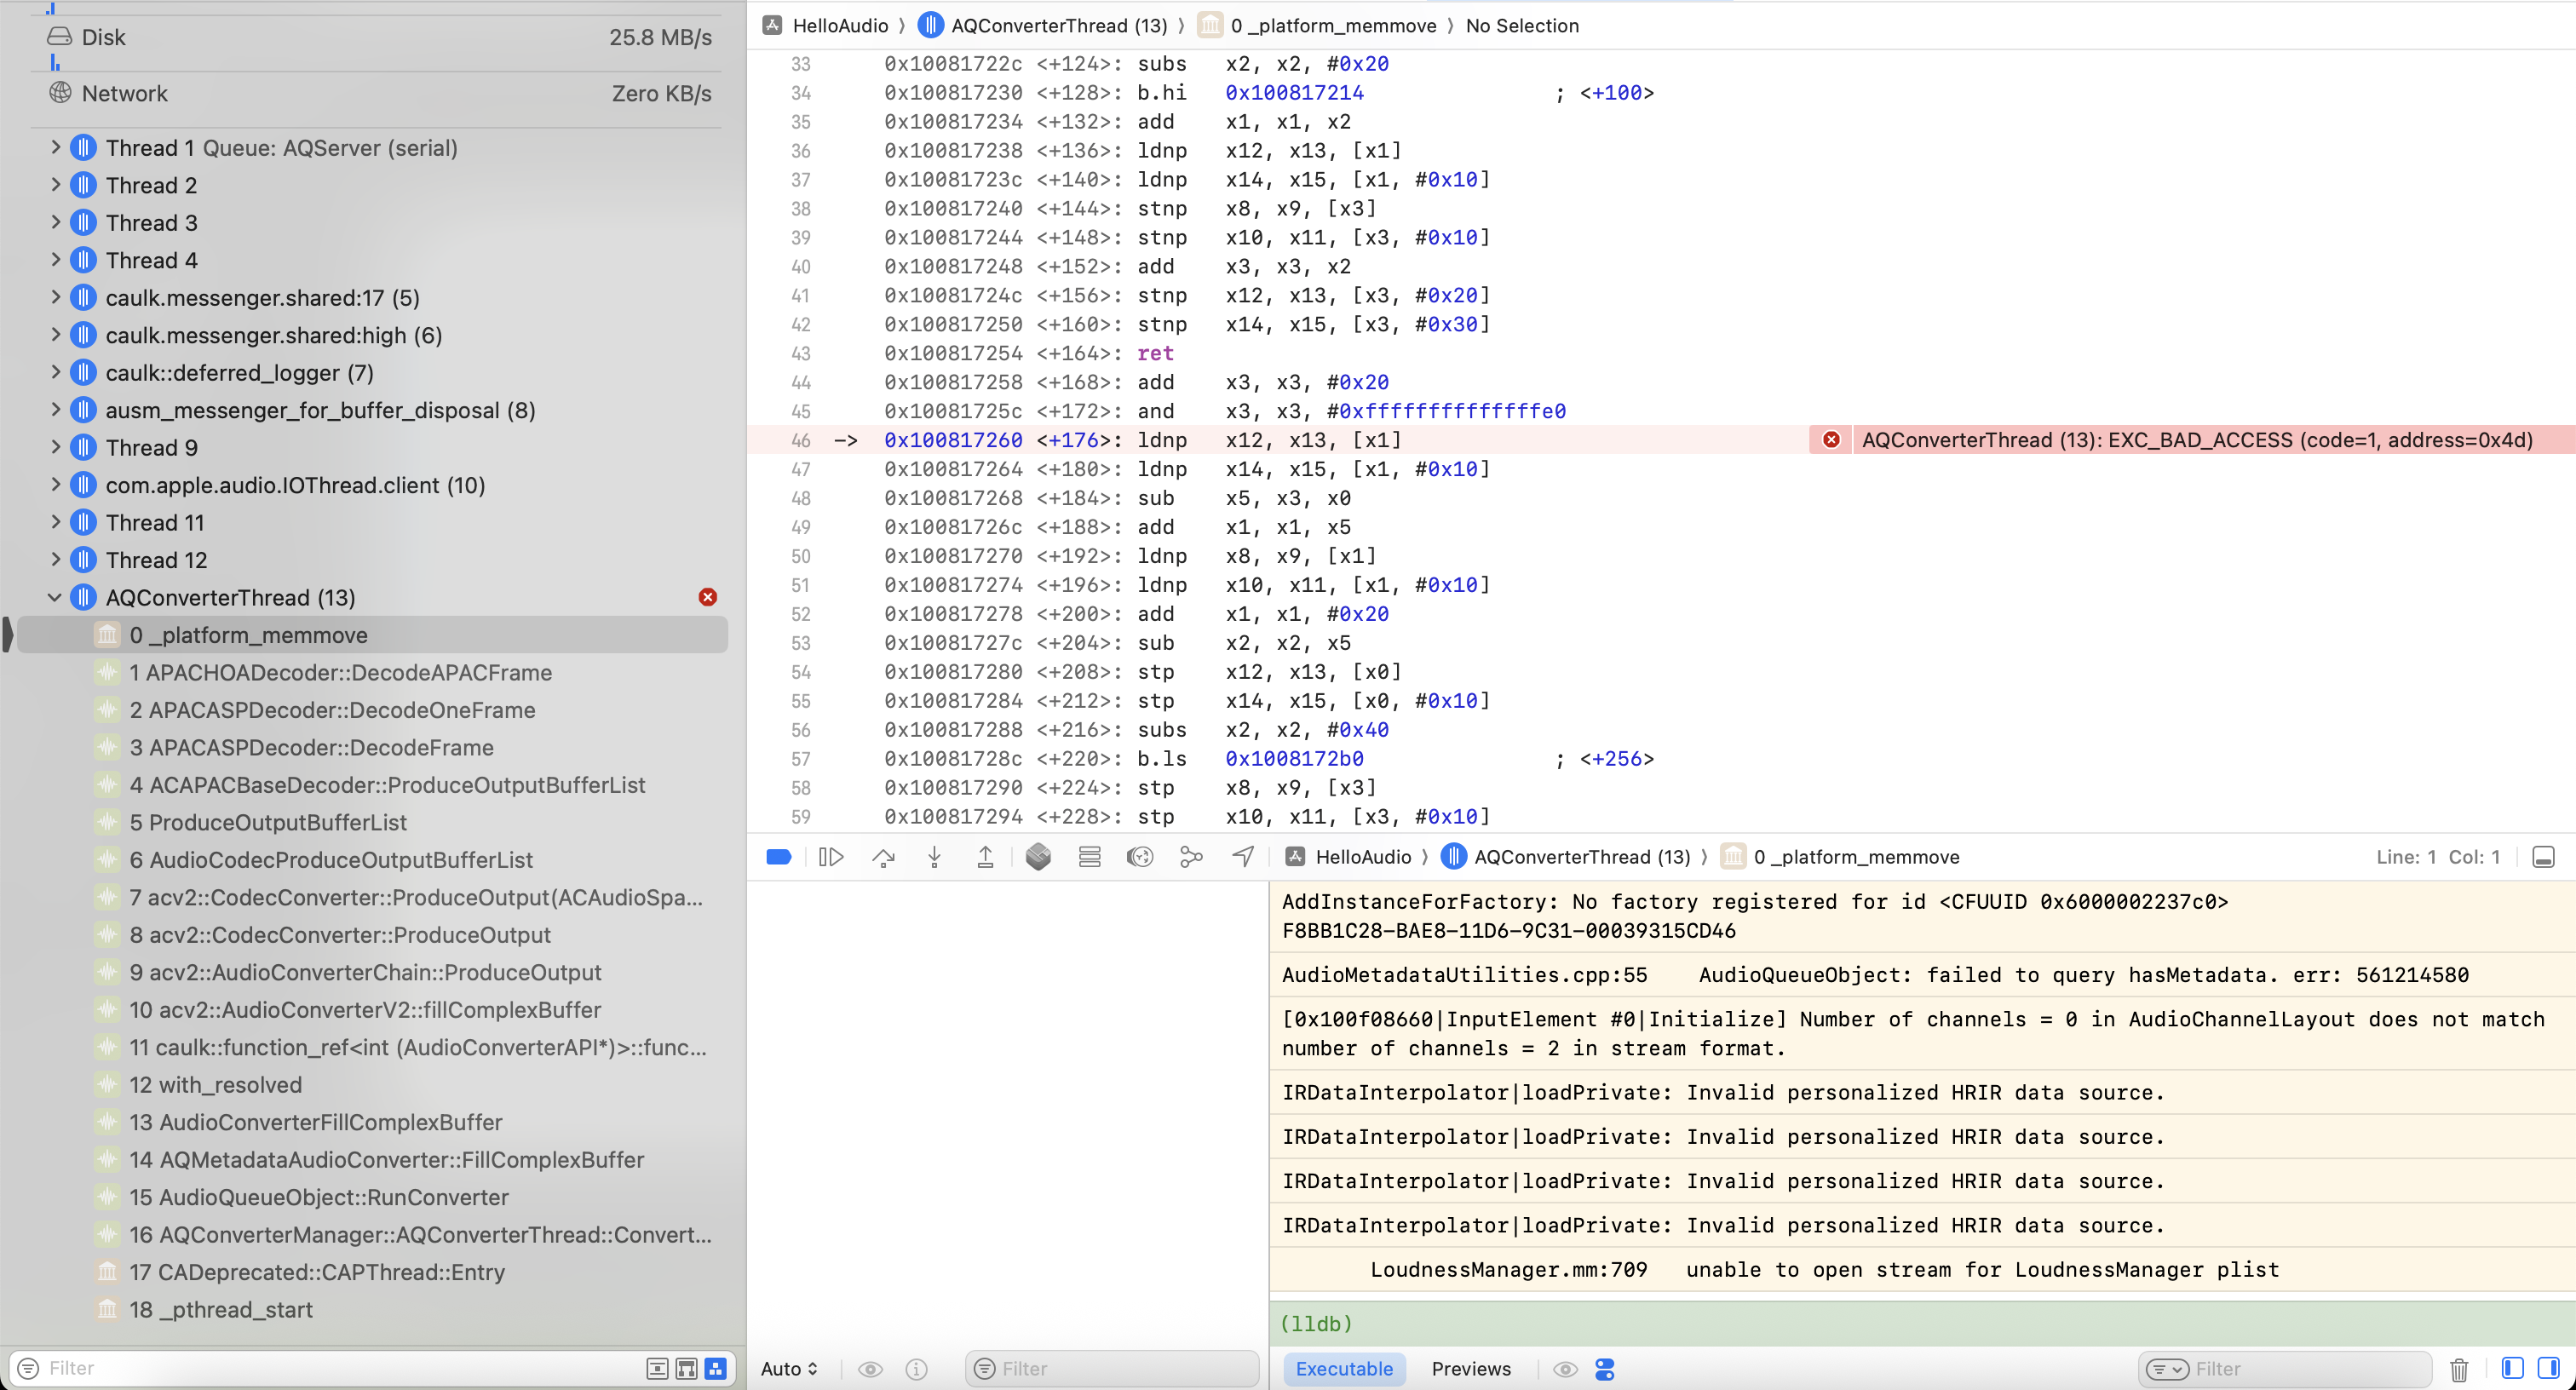 zhuowei/apple-positional-audio-codec-invalid-header
CVE-2025-31200 - @Noahhw46 figured it out
 codewhitesec/unmarshalpwn
POC for CVE-2018-0824
 opsxcq/exploit-cve-2017-5715
Spectre exploit
 tin-z/cve-2025-27363
Integer overflow in FreeType software, which also affects Chrome
 muirey03/cve-2022-32832
Proof-of-concept and write-up for the CVE-2022-32832 vulnerability patched in iOS 15.6
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 maldiohead/cve-2019-6207
xnu kernel heap info leak