
libptmalloc
 nccgroup/libptmalloc
Heap analysis tooling for ptmalloc
binary-analysisdebuggersmemory-forensics+1
464 years ago
nccgroup/libptmallocHeap analysis tooling for ptmalloc
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 bazad/gsscred-move-uaf
CVE-2018-4343: Proof-of-concept for a use-after-free in the GSSCred daemon on macOS and iOS.
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
 h4k6/cve-2023-0179-poc
针对(CVE-2023-0179)漏洞利用 该漏洞被分配为CVE-2023-0179,影响了从5.5到6.2-rc3的所有Linux版本,该漏洞在6.1.6上被测试。 漏洞的细节和文章可以在os-security上找到。
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 adamkadaban/cve-2024-30085
Proof-of-concept exploit for CVE-2024-30085, a heap-based buffer overflow in the Windows CLDLFT driver leading to local privilege escalation on…
 z3usx01/cve-2021-23017-poc
The issue only affects nginx if the "resolver" directive is used in the configuration file. Further, the attack is only possible if an attacker is…
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 tare05/intel-cve-2015-2291
PoC exploit for CVE-2015-2291
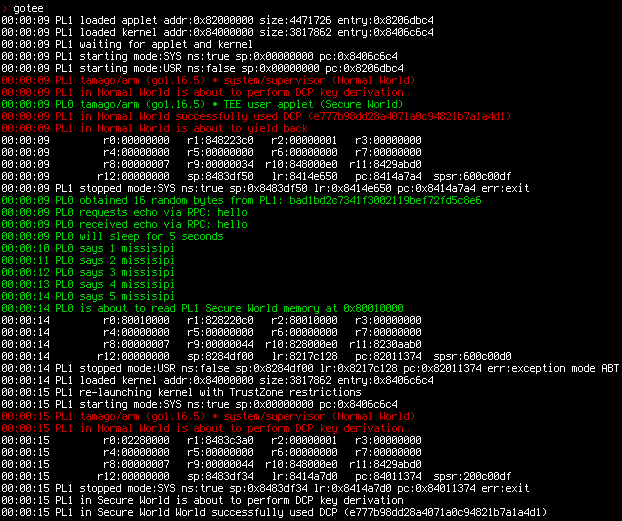 usbarmory/gotee-example
GoTEE - example application
 jaf0rk/cve-2026-5281
Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…
 volatilityfoundation/volatility
An advanced memory forensics framework
 spydomain/cve-2022-0435-poc
Stack overflow exploit for CVE-2022-0435 in the TIPC module, providing local privilege escalation to root on Ubuntu kernels.
 business1sg00d/cve-2023-25136
Looking into the memory when sshd 9.1p1 aborts due to a double free bug.
 shaikusaf/linux-4.19.72_cve-2020-10757
Linux kernel source tree modified to demonstrate CVE-2020-10757, a use-after-free vulnerability in the AF_PACKET socket, for educational and research…