Archived
rekall
 google/rekall
Rekall Memory Forensic Framework
digital-forensicsforensicsincident-response+3
2.0k
 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
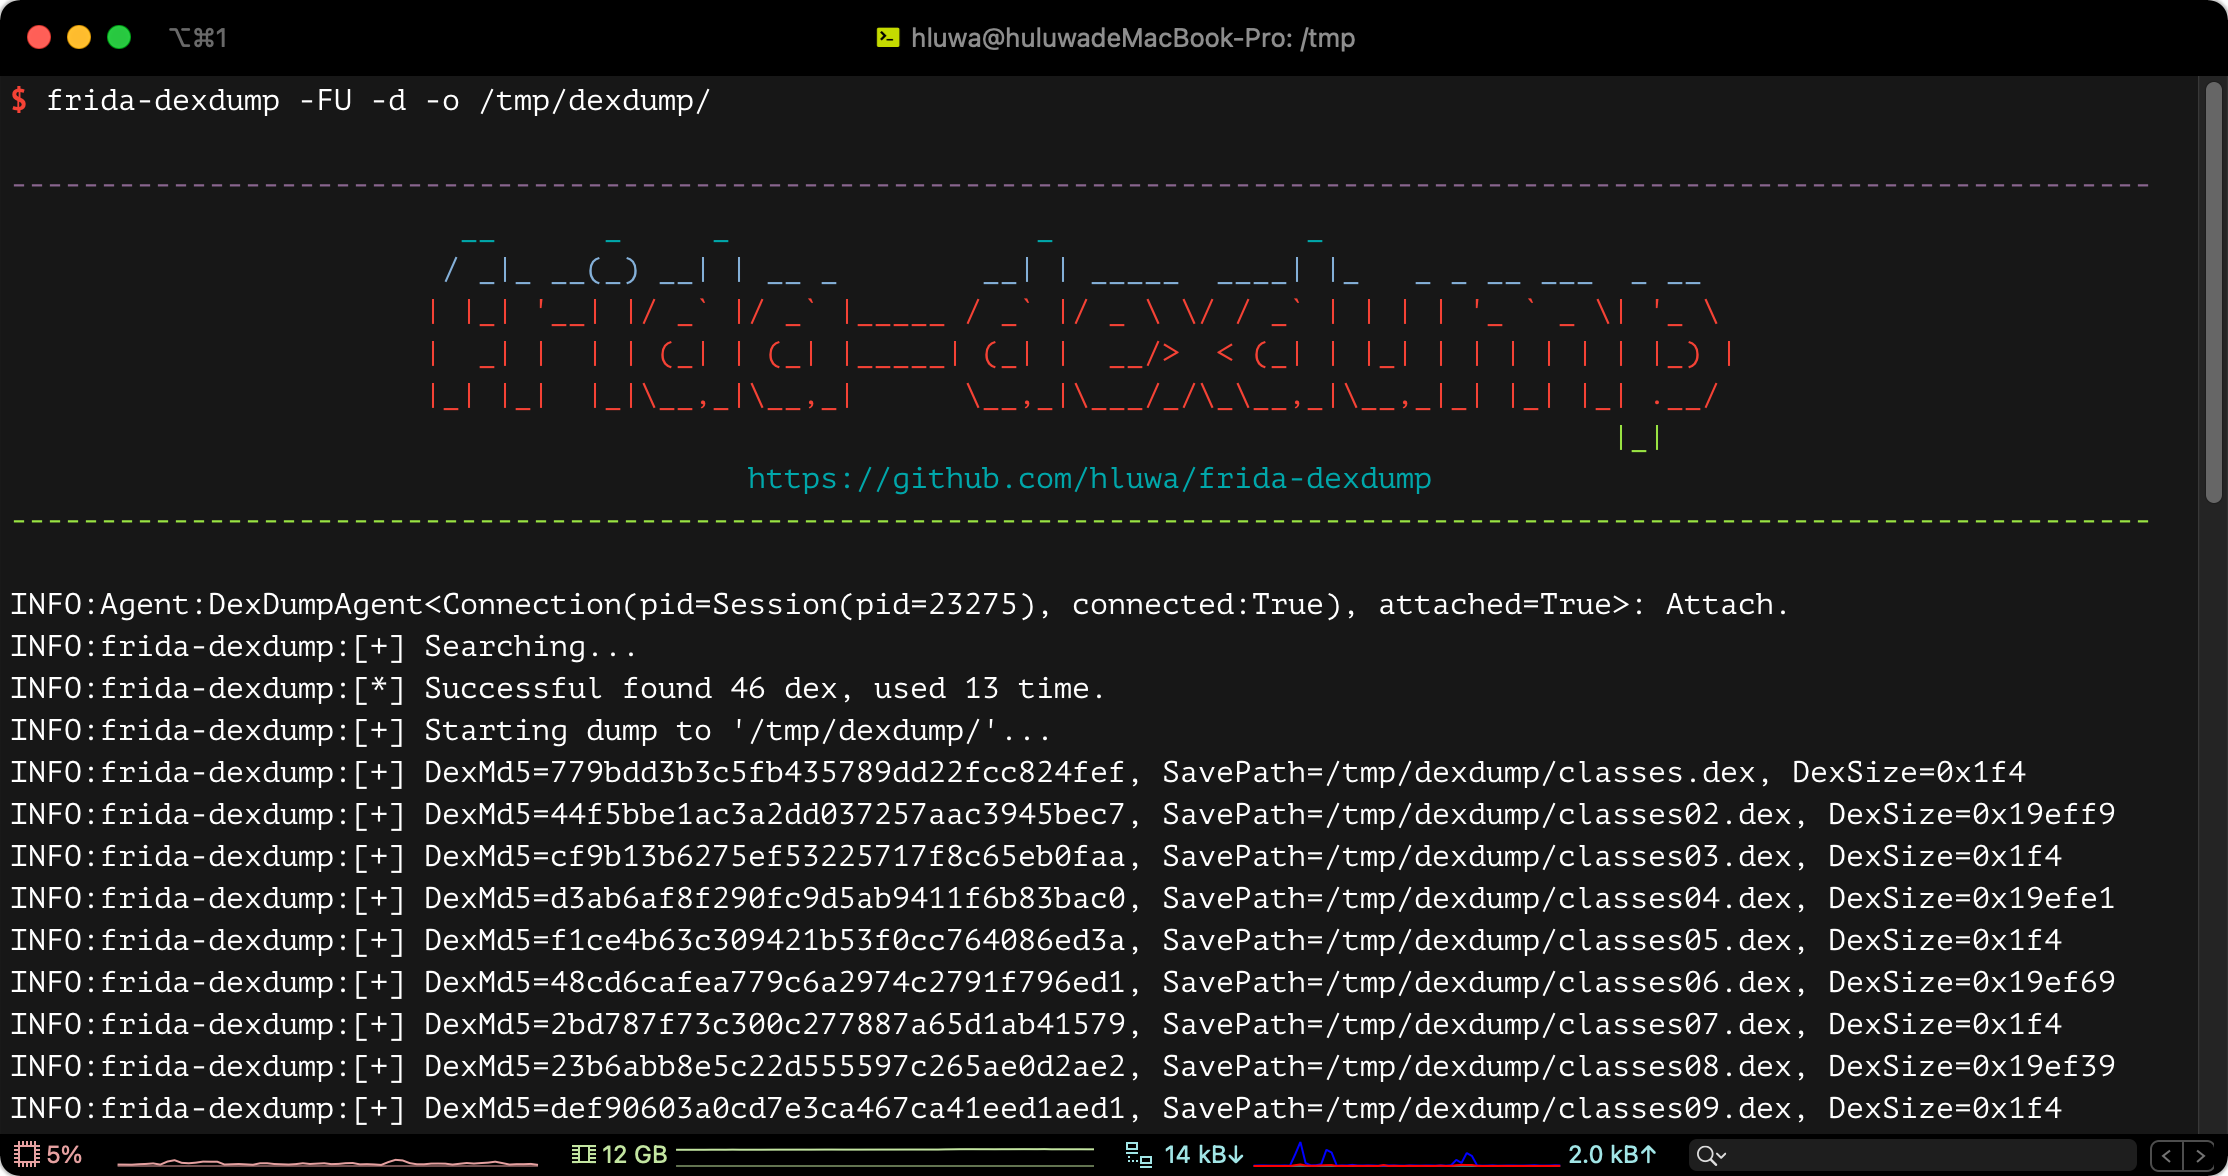 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
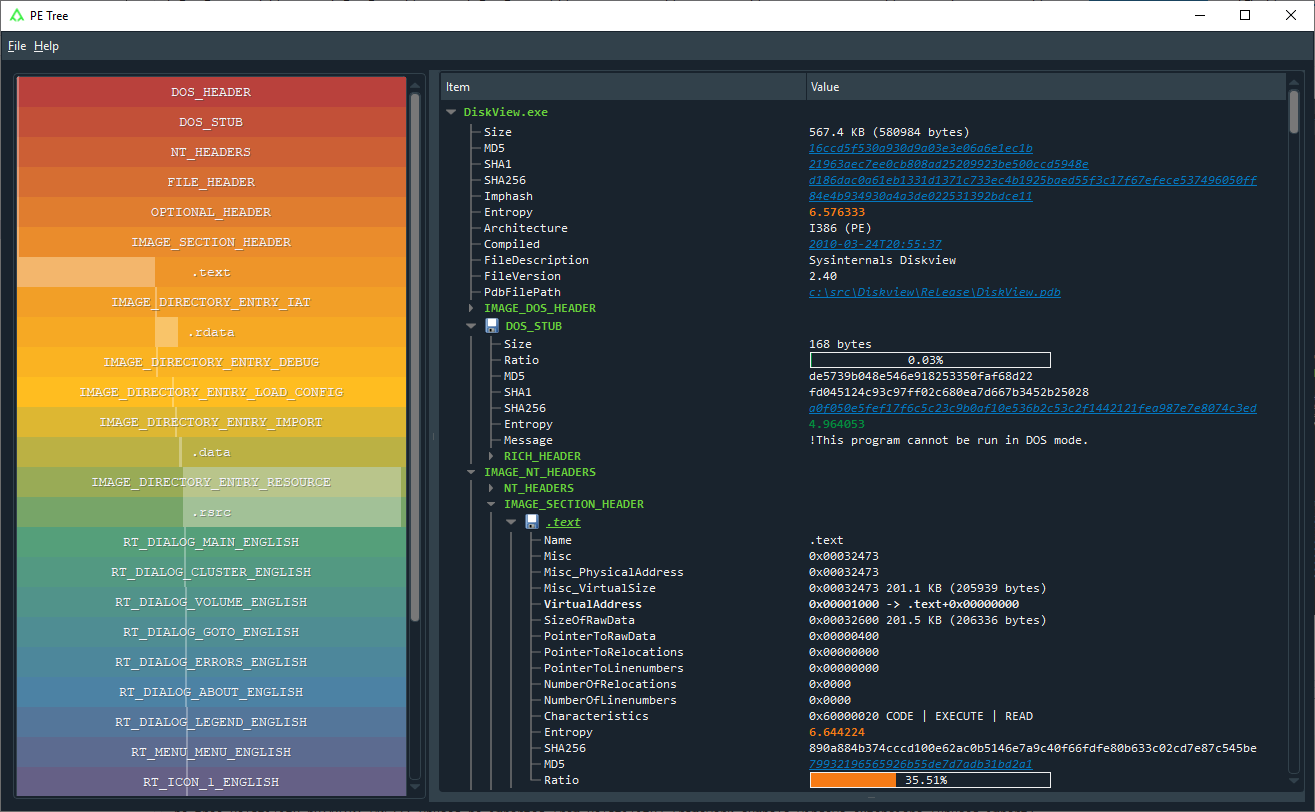 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…