CAPEv2
 kevoreilly/capev2
Malware Configuration And Payload Extraction
debuggersdynamic-analysis-sandboxingeducation+6
kevoreilly/capev2Malware Configuration And Payload Extraction
 dumpanalysis/prologwindbg
Use Prolog to analyze memory dumps and stopped live processes in WinDbg.
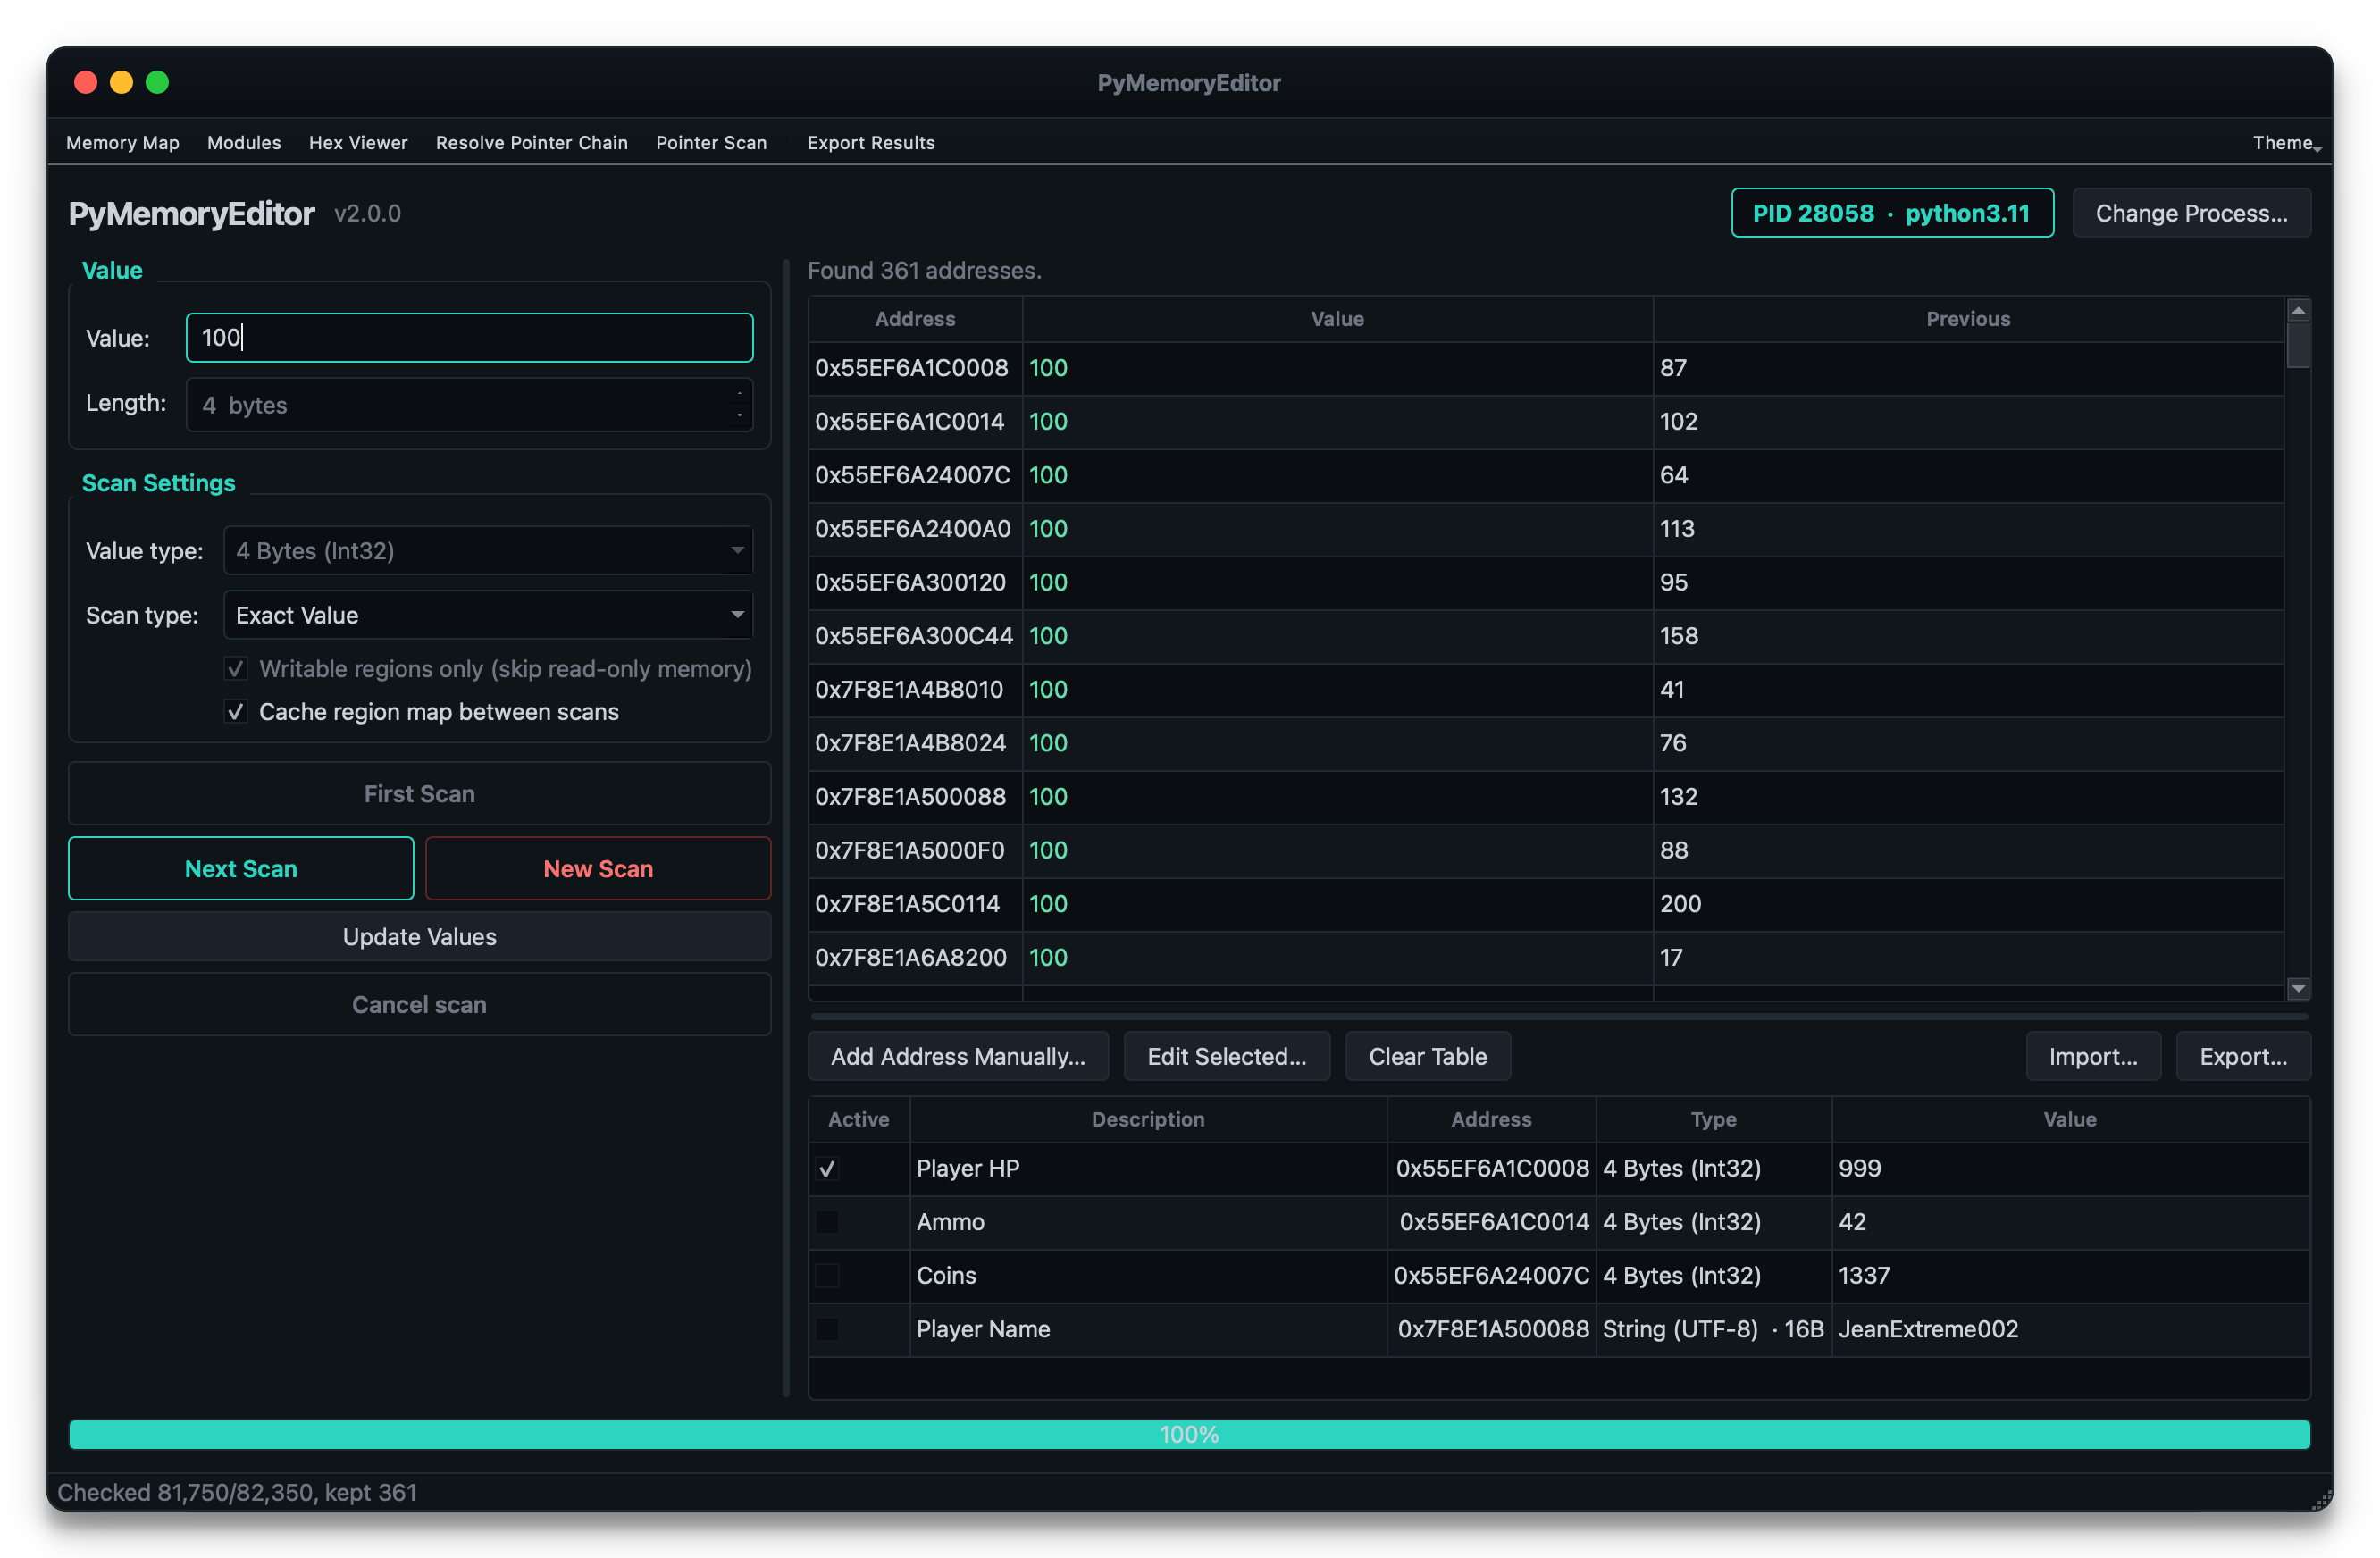 jeanextreme002/pymemoryeditor
A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 abraxas/cve-2026-19445-sni-uaf
Proof-of-concept lab for CVE-2026-19445, a CPython ssl SNI SSLContext use-after-free where a remote TLS client frees the server's dispatch context…
 gengstah/windbg-mcp
An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
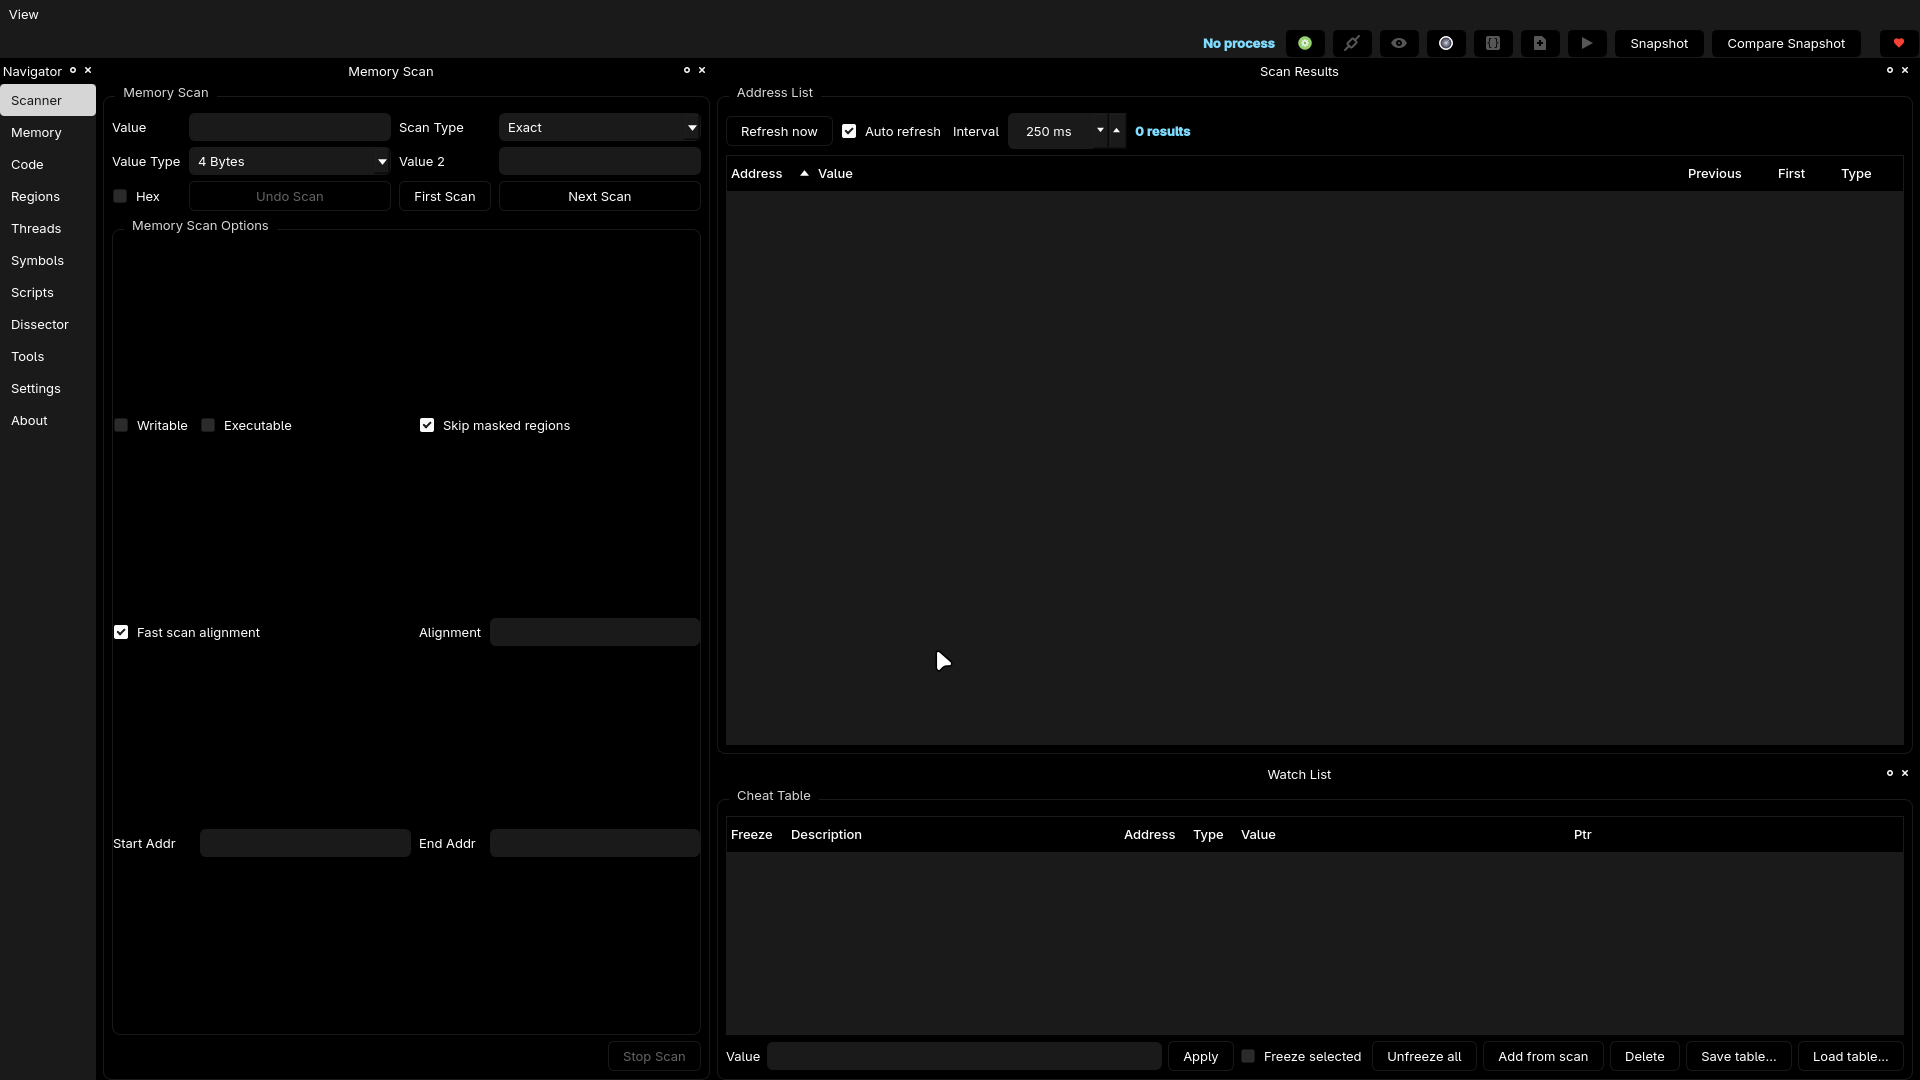 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 yezzfusl/cve_2023_38831_scanner
This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
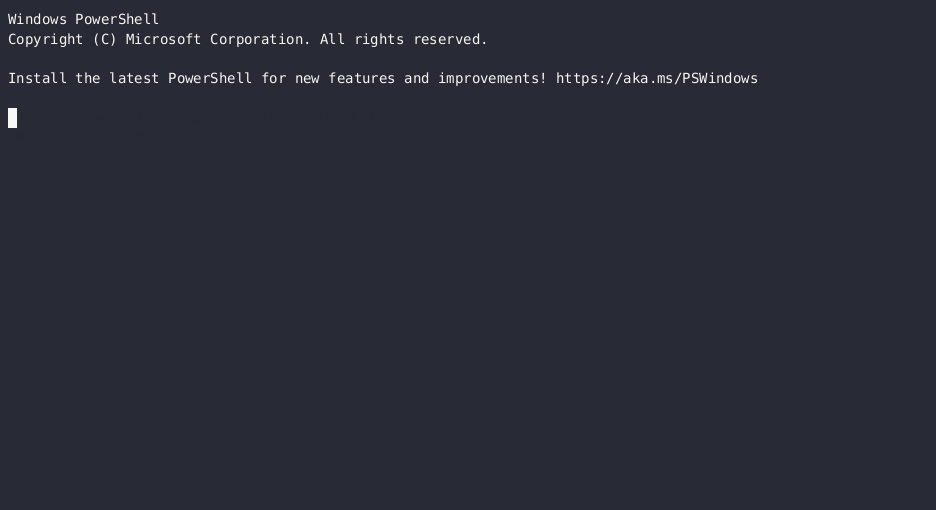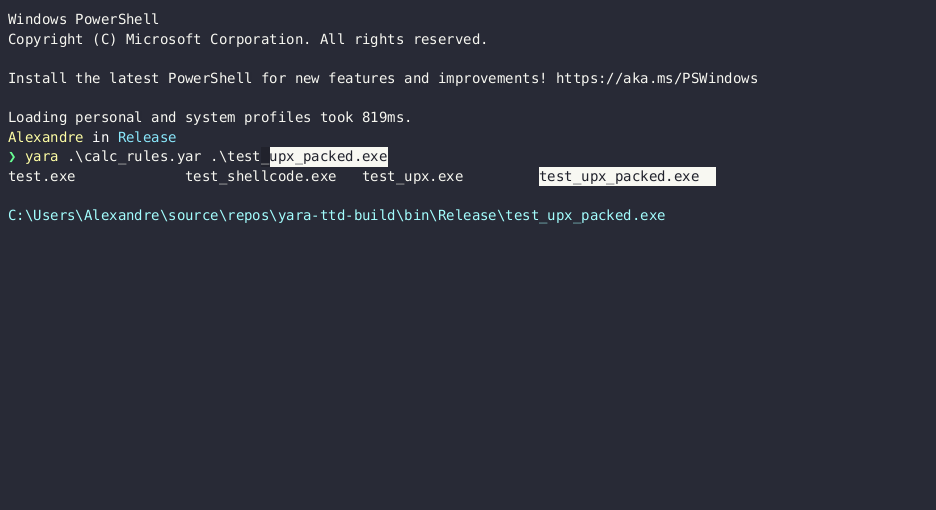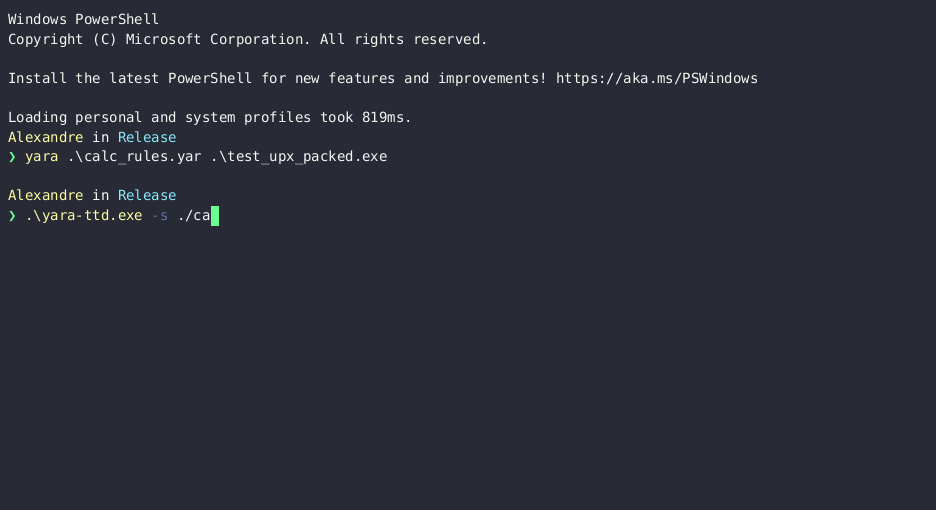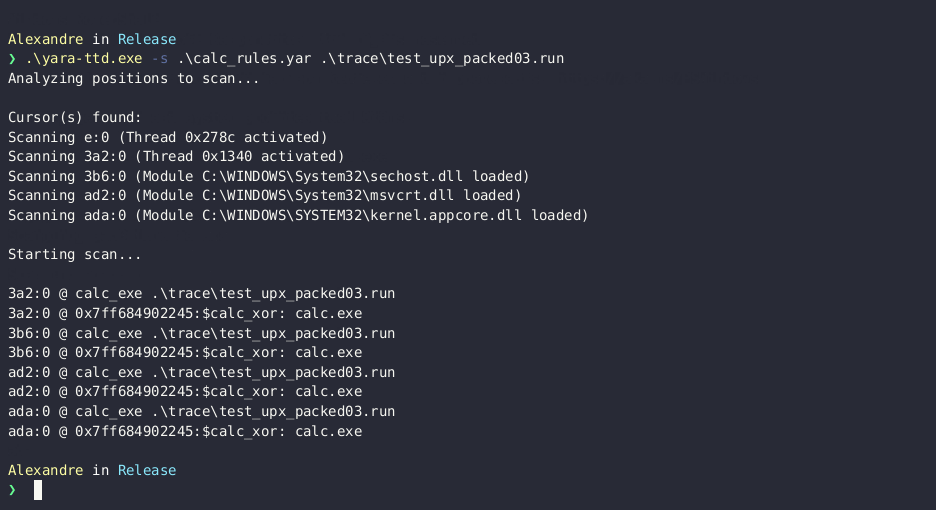 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
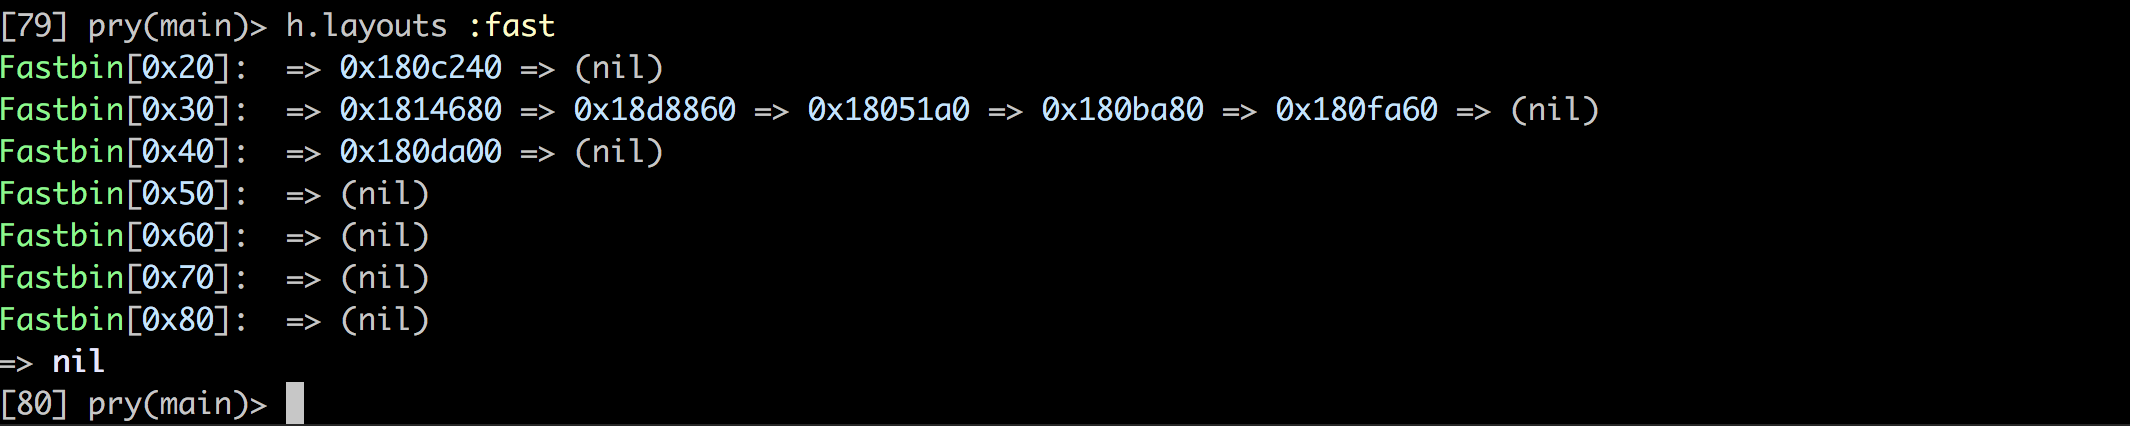 david942j/heapinfo
An interactive memory info for pwning / exploiting
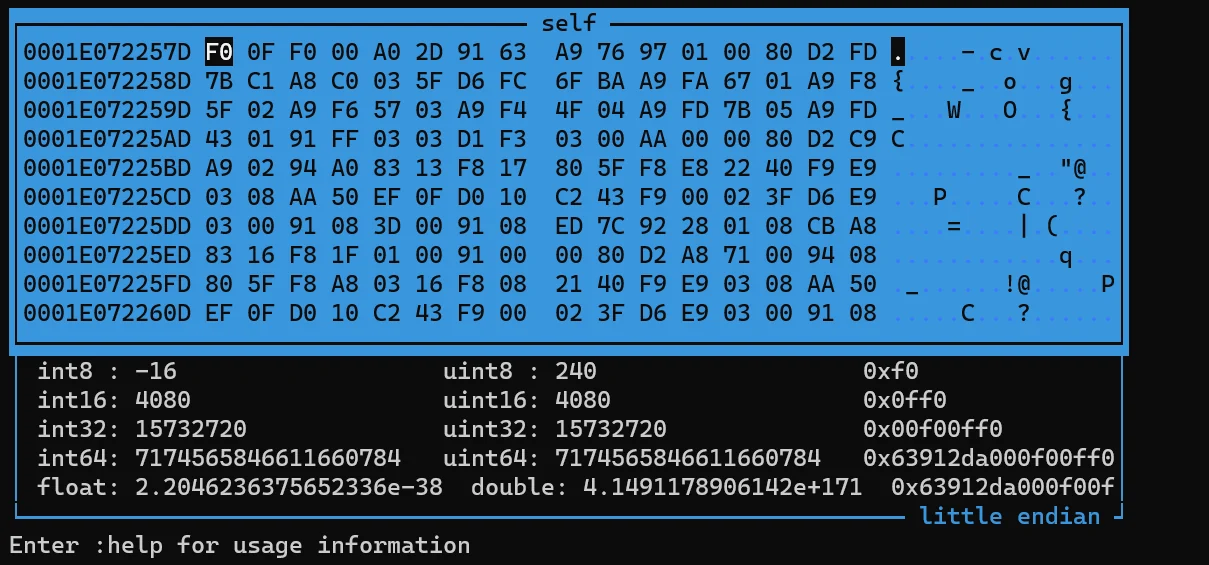 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
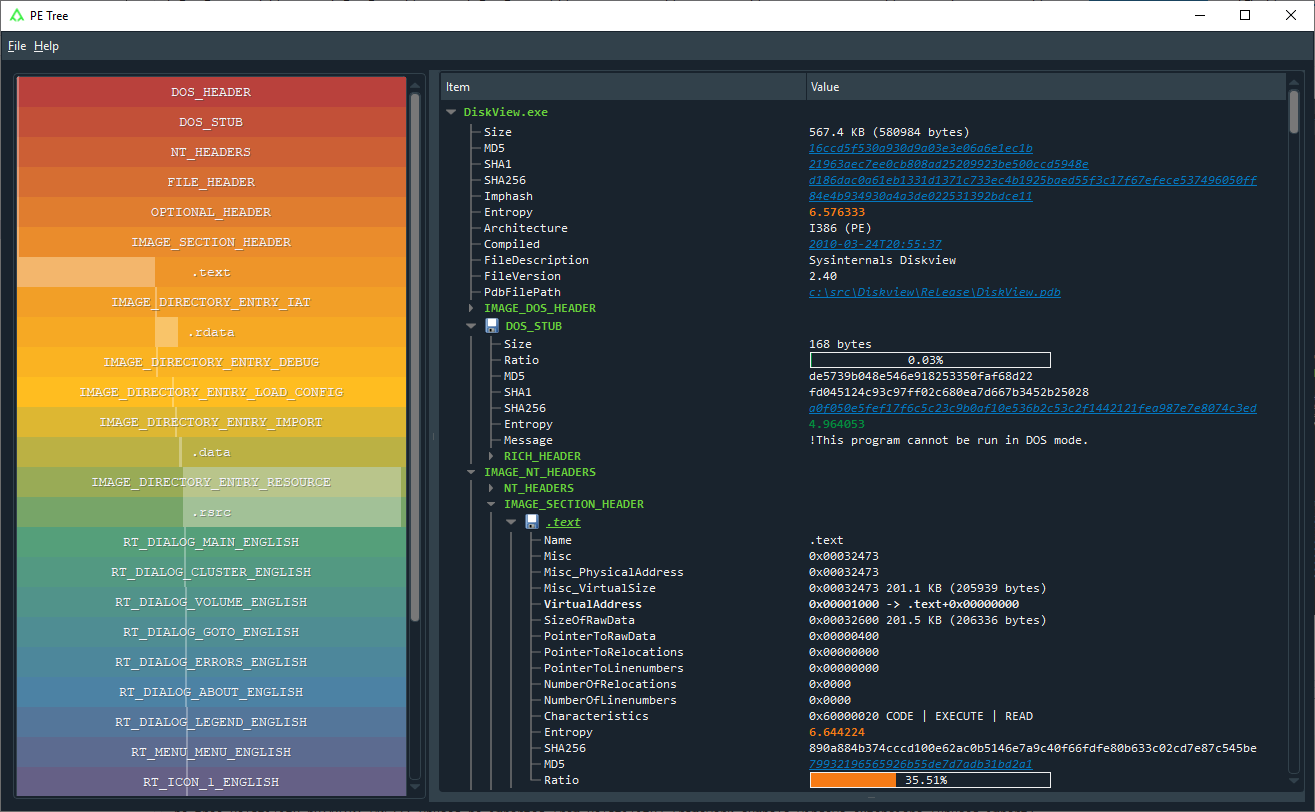 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 nccgroup/libptmalloc
Heap analysis tooling for ptmalloc
 nccgroup/libmempool
Heap analysis tooling for mempool
 nccgroup/libdlmalloc
Heap analysis tooling for dlmalloc