
PSI_BOF
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
binary-analysisdebuggersmemory-forensics+4
whokilleddb/psi_bofA BOF designed to inspect processes memory and addresses
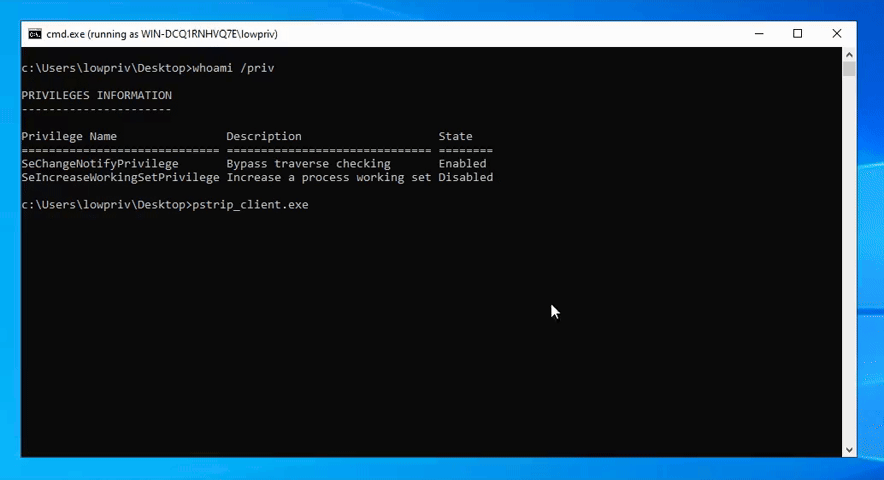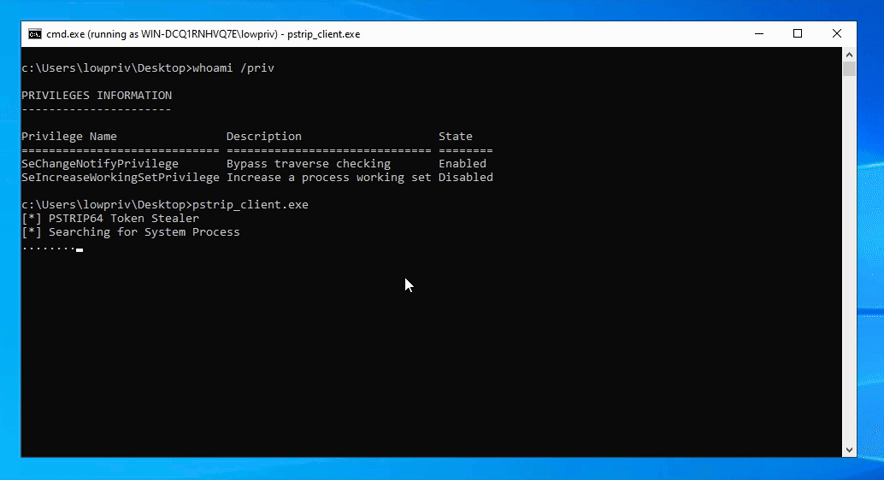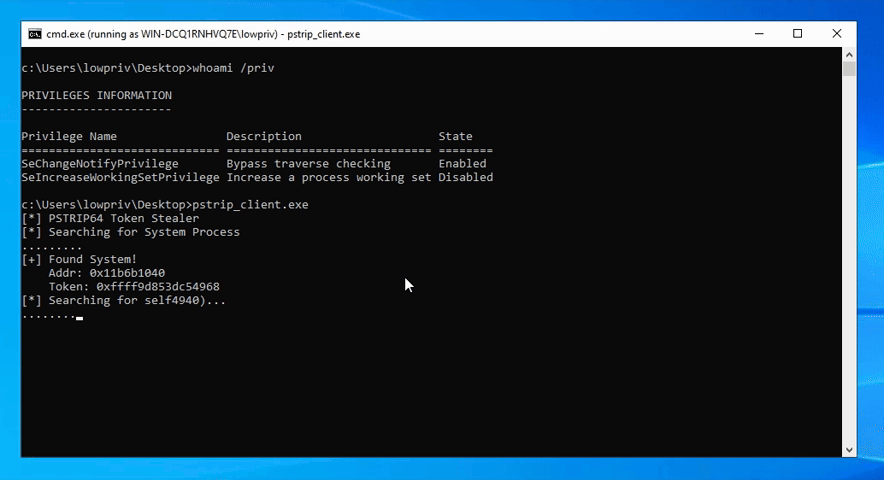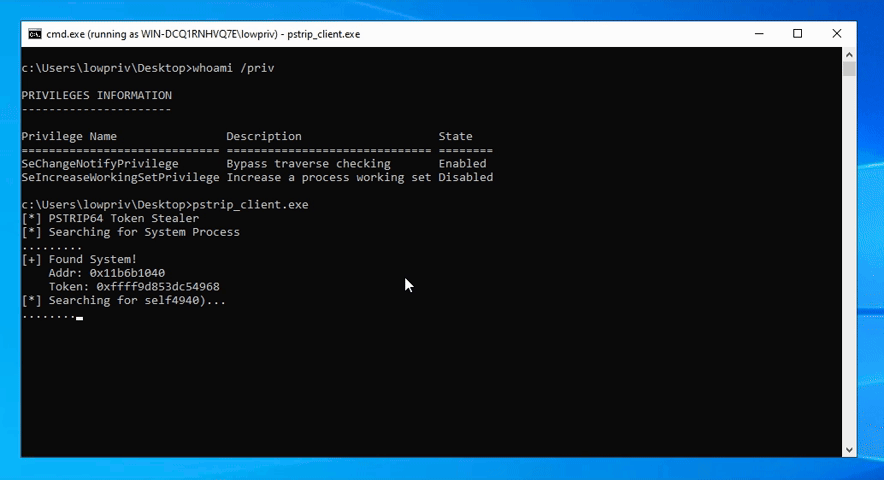 smarttfoxx/cve-2026-29923
The pstrip64.sys kernel driver exposes an IOCTL that allows low-privileged users to map arbitrary ranges of physical memory into their own virtual…
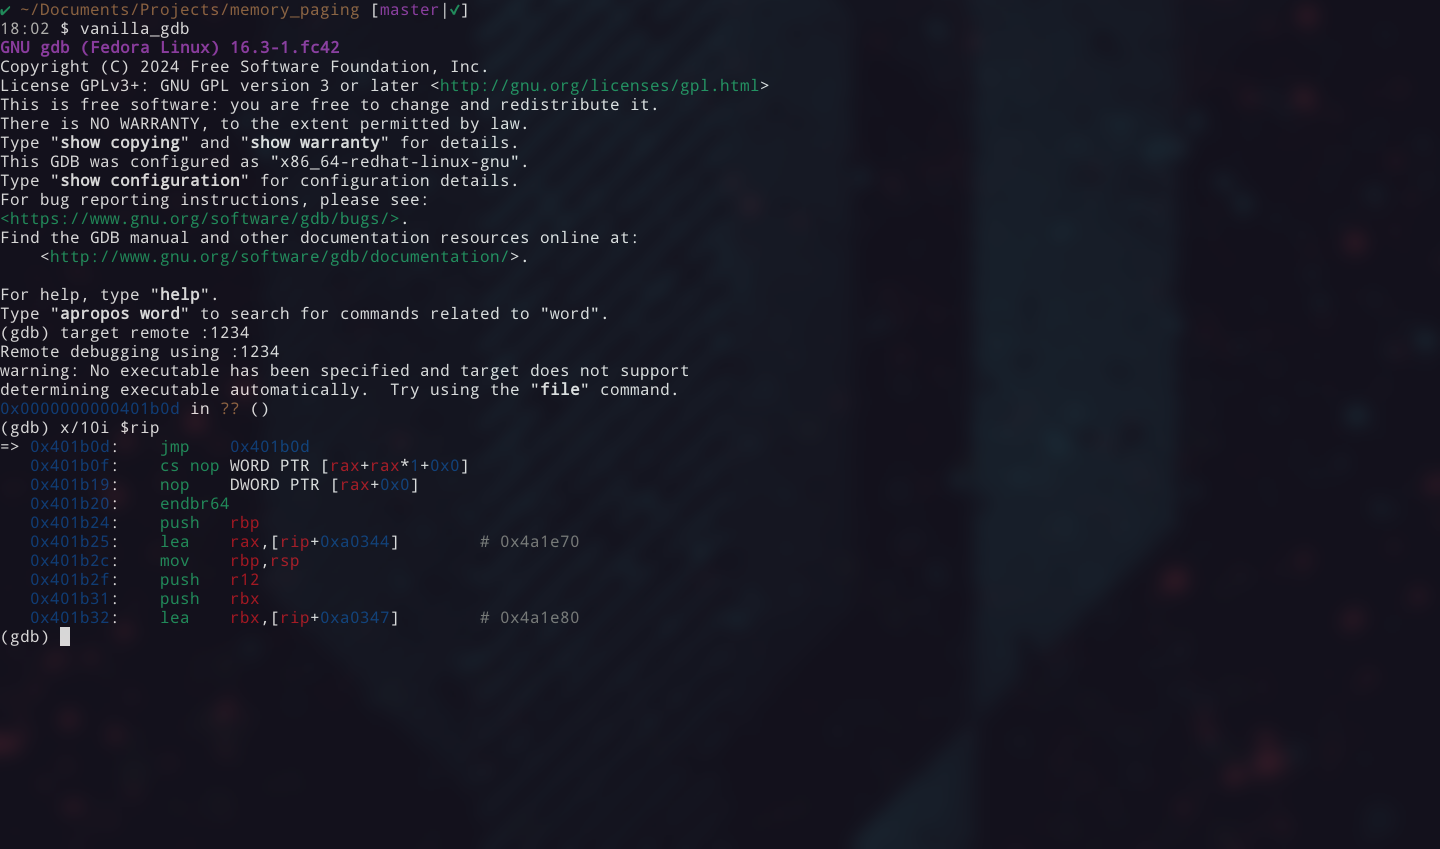 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 lzty/cve-2025-7771
Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
 velocidex/linpmem
Linux kernel driver for physical memory acquisition, enabling read access to any physical address including reserved memory and memory holes, with…
 rebelle3/cve-2017-7117
Educational exploit for CVE-2017-7117, a type-confusion and use-after-free vulnerability in iOS 10.3.4 JavaScriptCore, demonstrating memory spraying…
 chunzhennn/cve-2023-21987-poc
Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 crackercat/cve-2021-44852
An issue was discovered in BS_RCIO64.sys in Biostar RACING GT Evo 2.1.1905.1700. A low-integrity process can open the driver's device object and…
 delsploit/cve-2022-2078
Proof-of-concept exploit for CVE-2022-2078 demonstrating kernel memory leak via buffer manipulation, with leaked kernel address disclosure.
 springsec/cve-2022-22620
Webkit (Safari) - Exploit
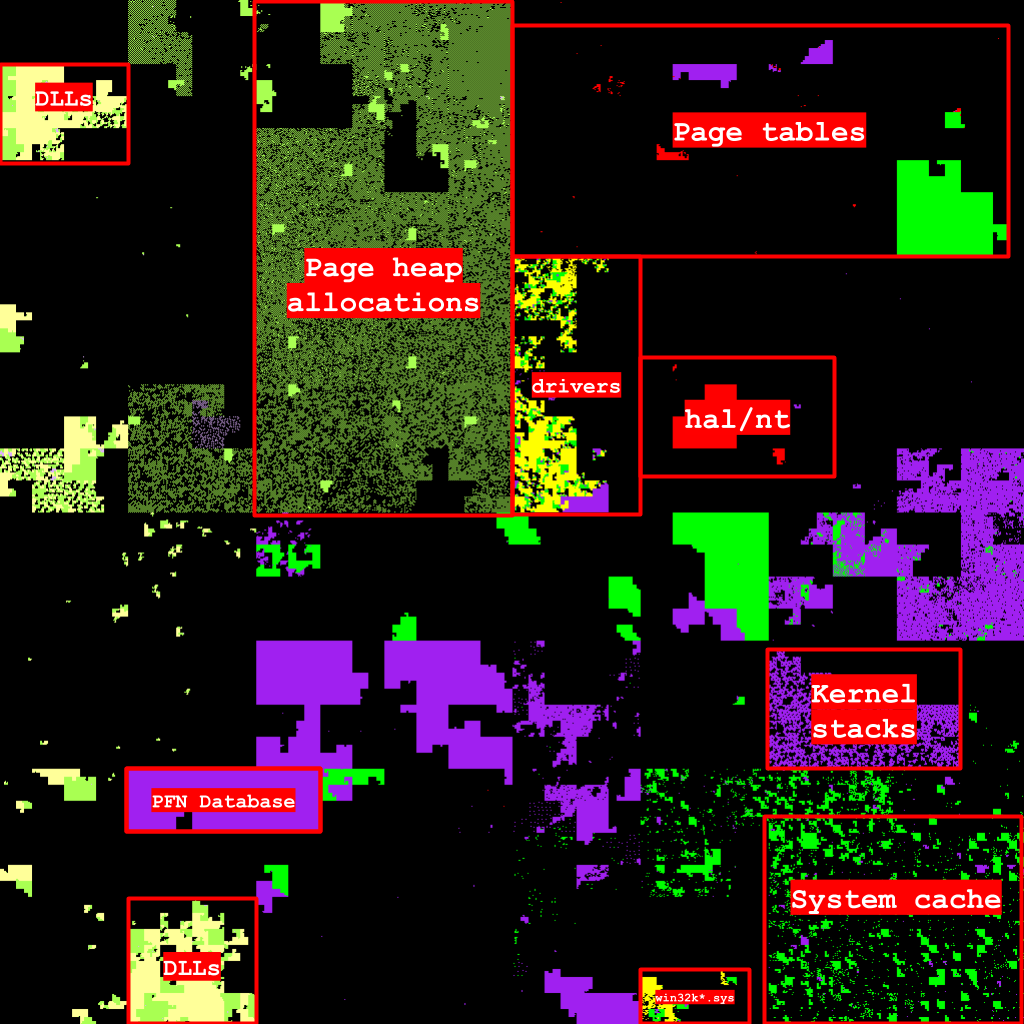 0vercl0k/clairvoyance
Visualize the virtual address space of a Windows process on a Hilbert curve.
 nccgroup/memaddressanalysis
Research project related to memory address analysis