
libextractor-ole2-rce
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
binary-exploitationexploitationlabs-practice+4
haitam-lazaar/libextractor-ole2-rcePoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 skelsec/pypykatz
Mimikatz implementation in pure Python
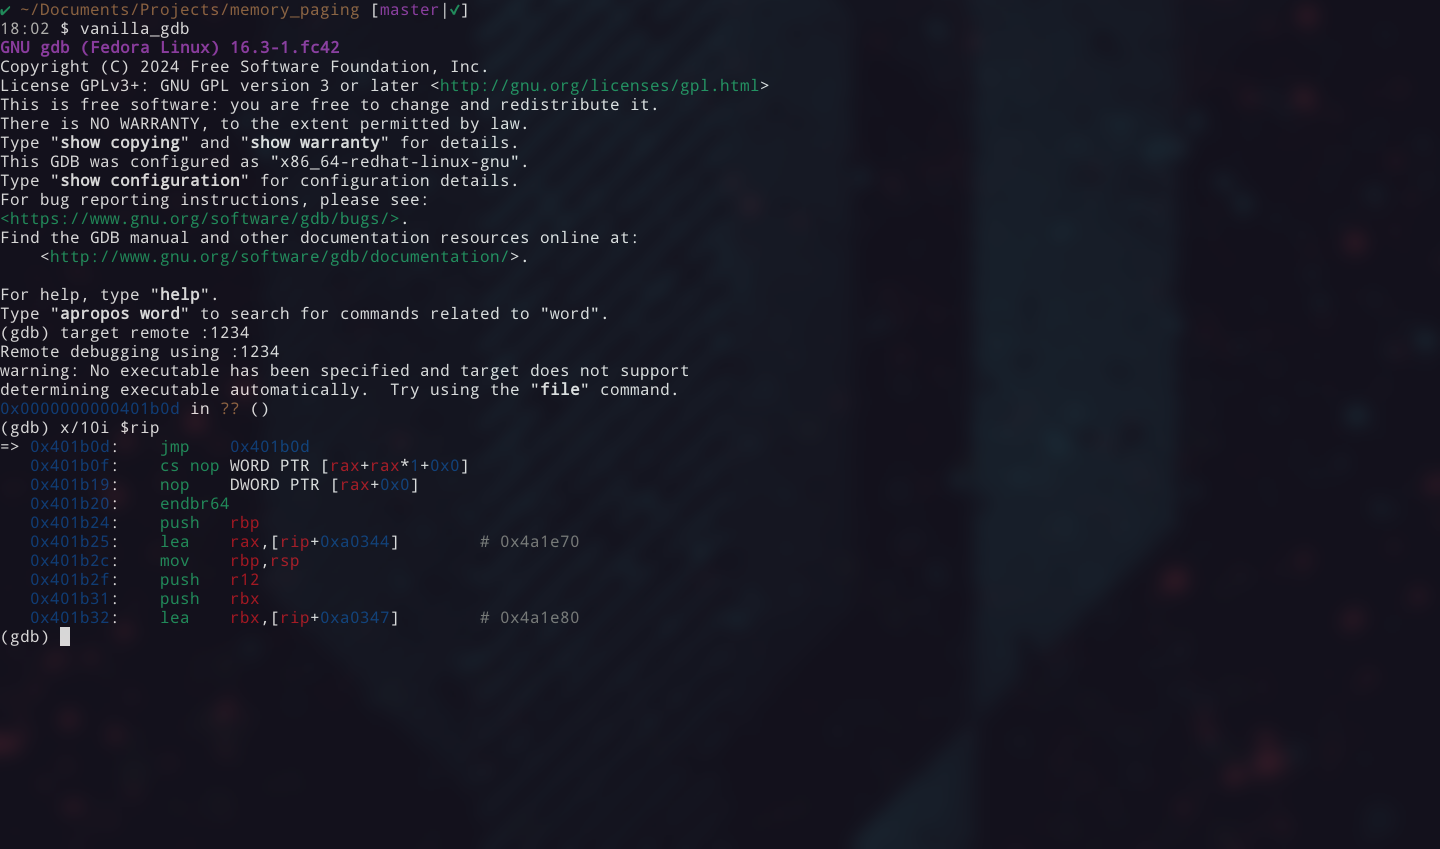 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 andreafortuna/autotimeliner
Automagically extract forensic timeline from volatile memory dump
 d0rb/cve-2023-49606
Critical use-after-free vulnerability discovered in Tinyproxy
 h4k6/cve-2023-0179-poc
针对(CVE-2023-0179)漏洞利用 该漏洞被分配为CVE-2023-0179,影响了从5.5到6.2-rc3的所有Linux版本,该漏洞在6.1.6上被测试。 漏洞的细节和文章可以在os-security上找到。
 ekknod/amdryzenmastercheat
Exploit tool leveraging CVE-2020-12928 (AMD RyzenMaster driver) for game memory manipulation and anti-cheat bypass on Windows 10 with AMD Ryzen CPUs.
 jackhuyh/cve-2016-3308
Use CVE-2016-3308 corrupt win32k desktop heap