

dissect
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
data-recoverydigital-forensicsdisk-forensics+5
1.2k
fox-it/dissectDissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 velocidex/winpmem
The multi-platform memory acquisition tool.
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.

 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
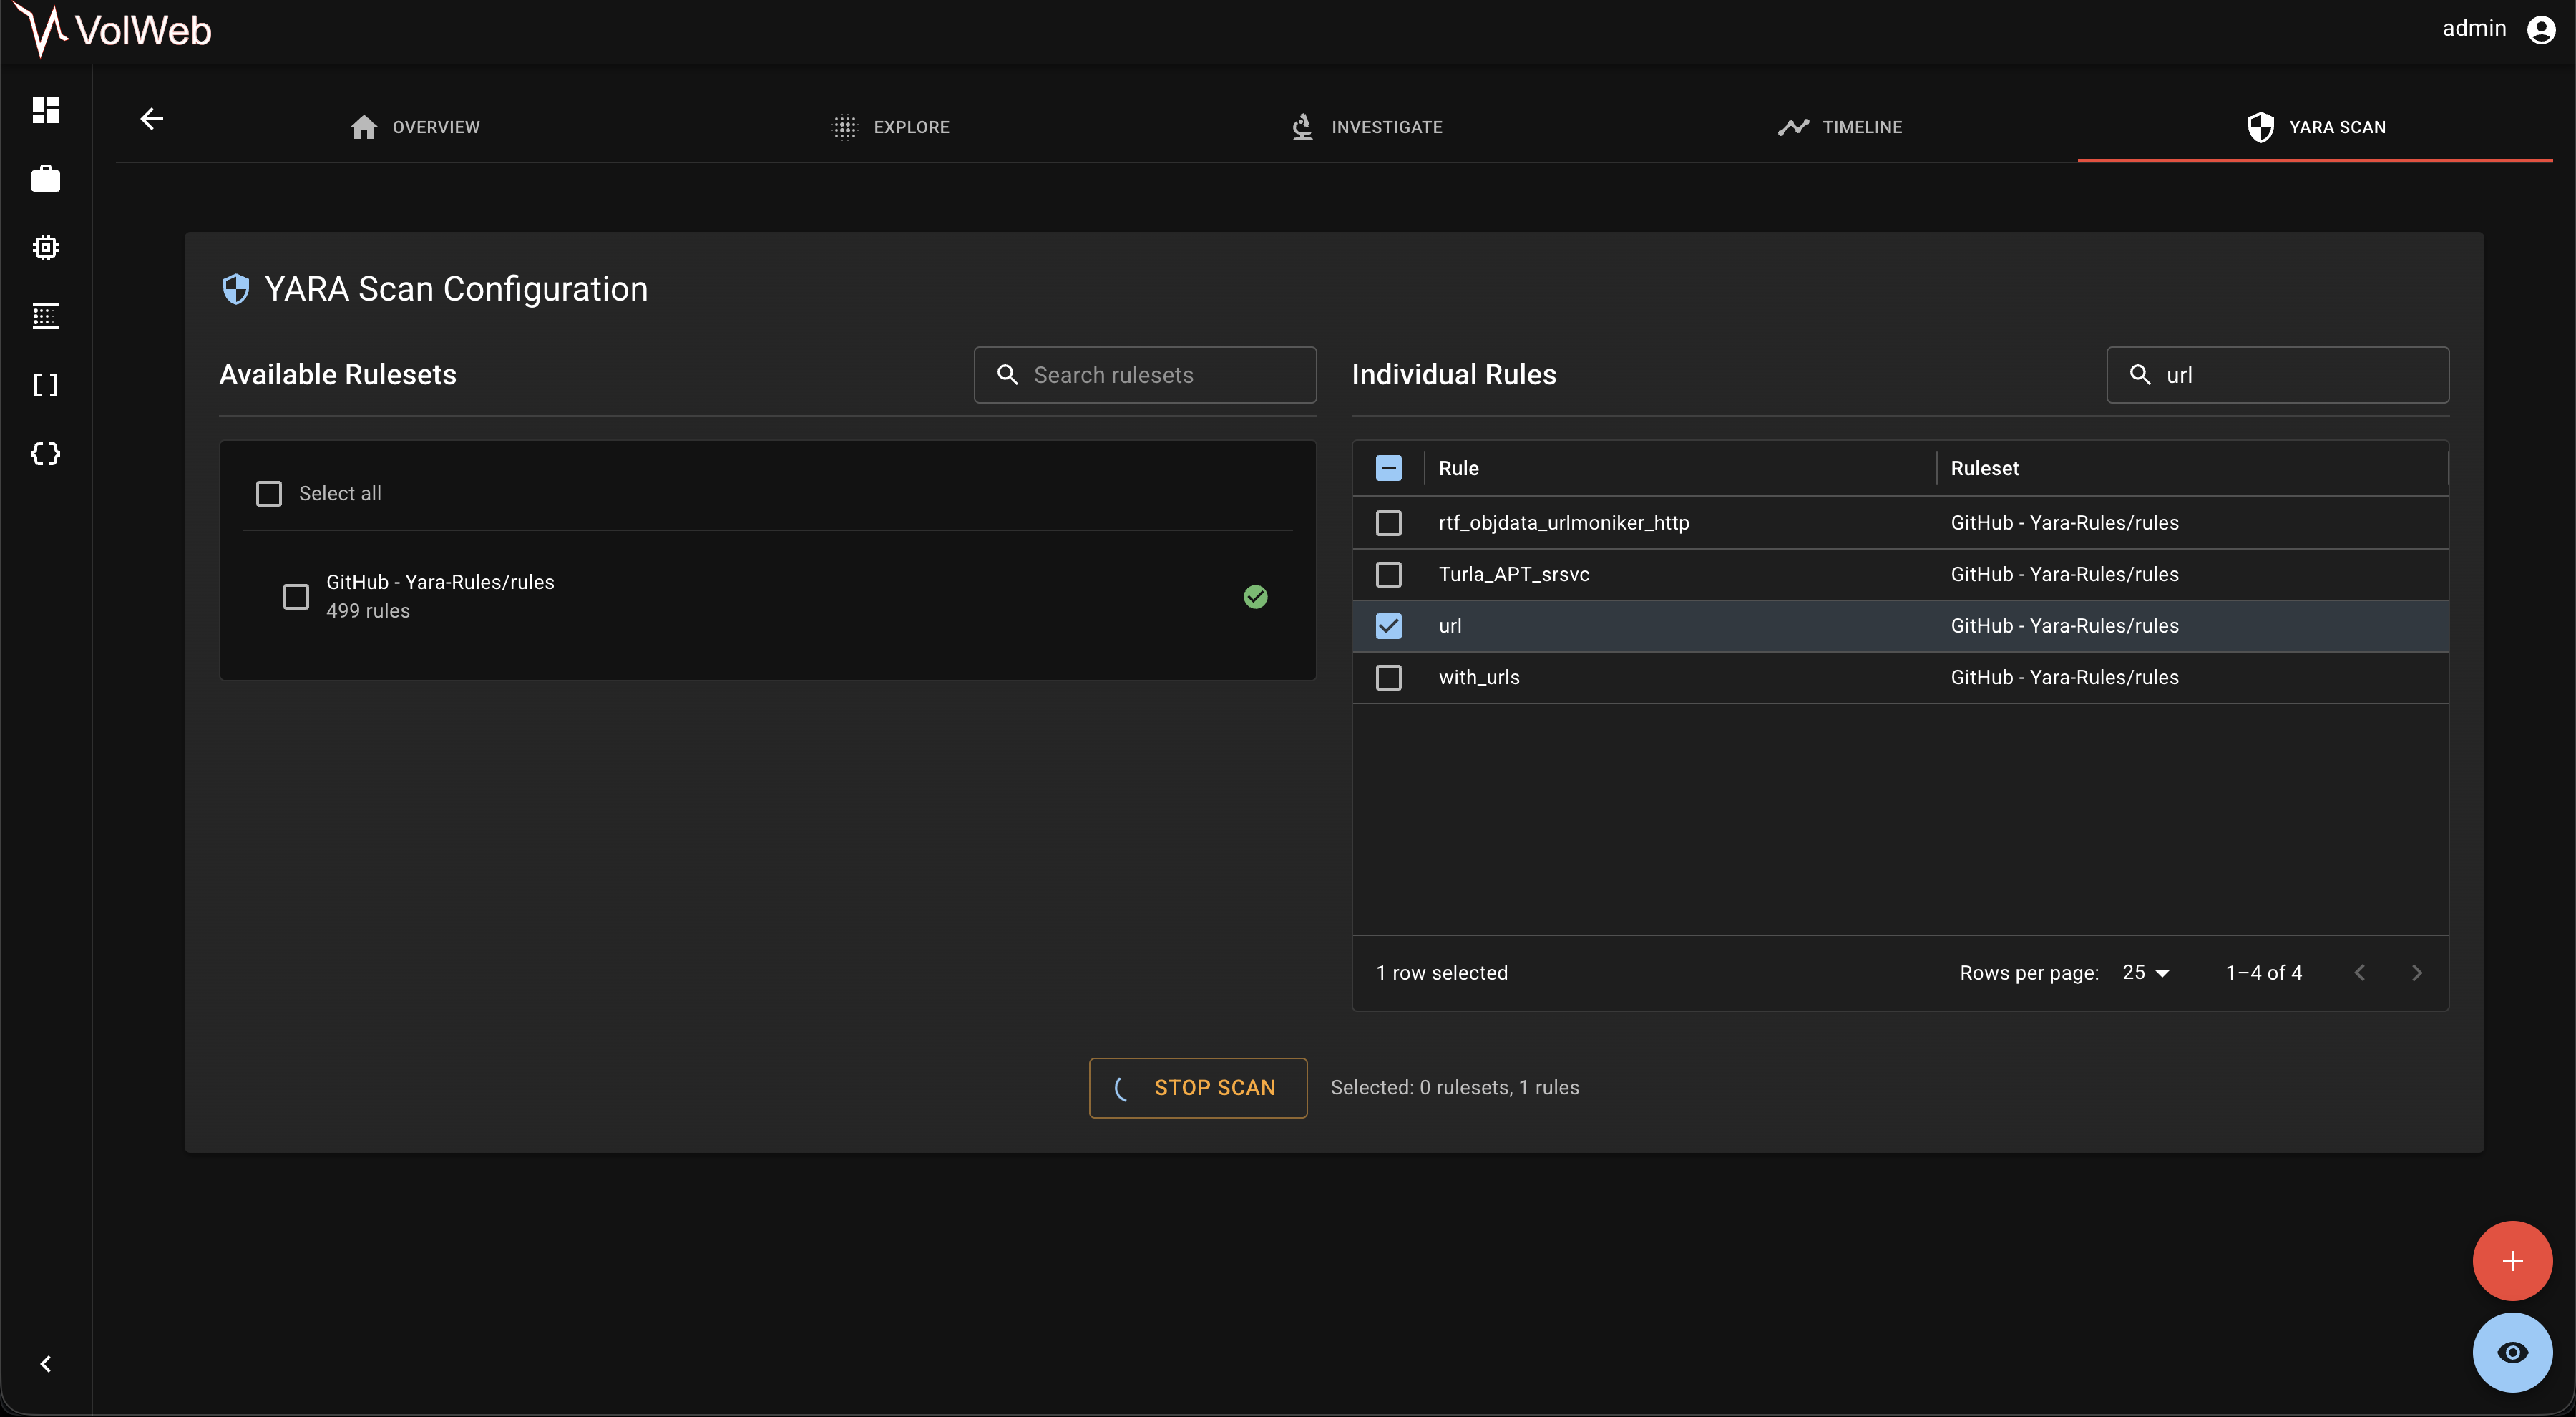 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 antisurveillanceagency/shadownet
ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…