

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 angr/angr
A powerful and user-friendly binary analysis platform!
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
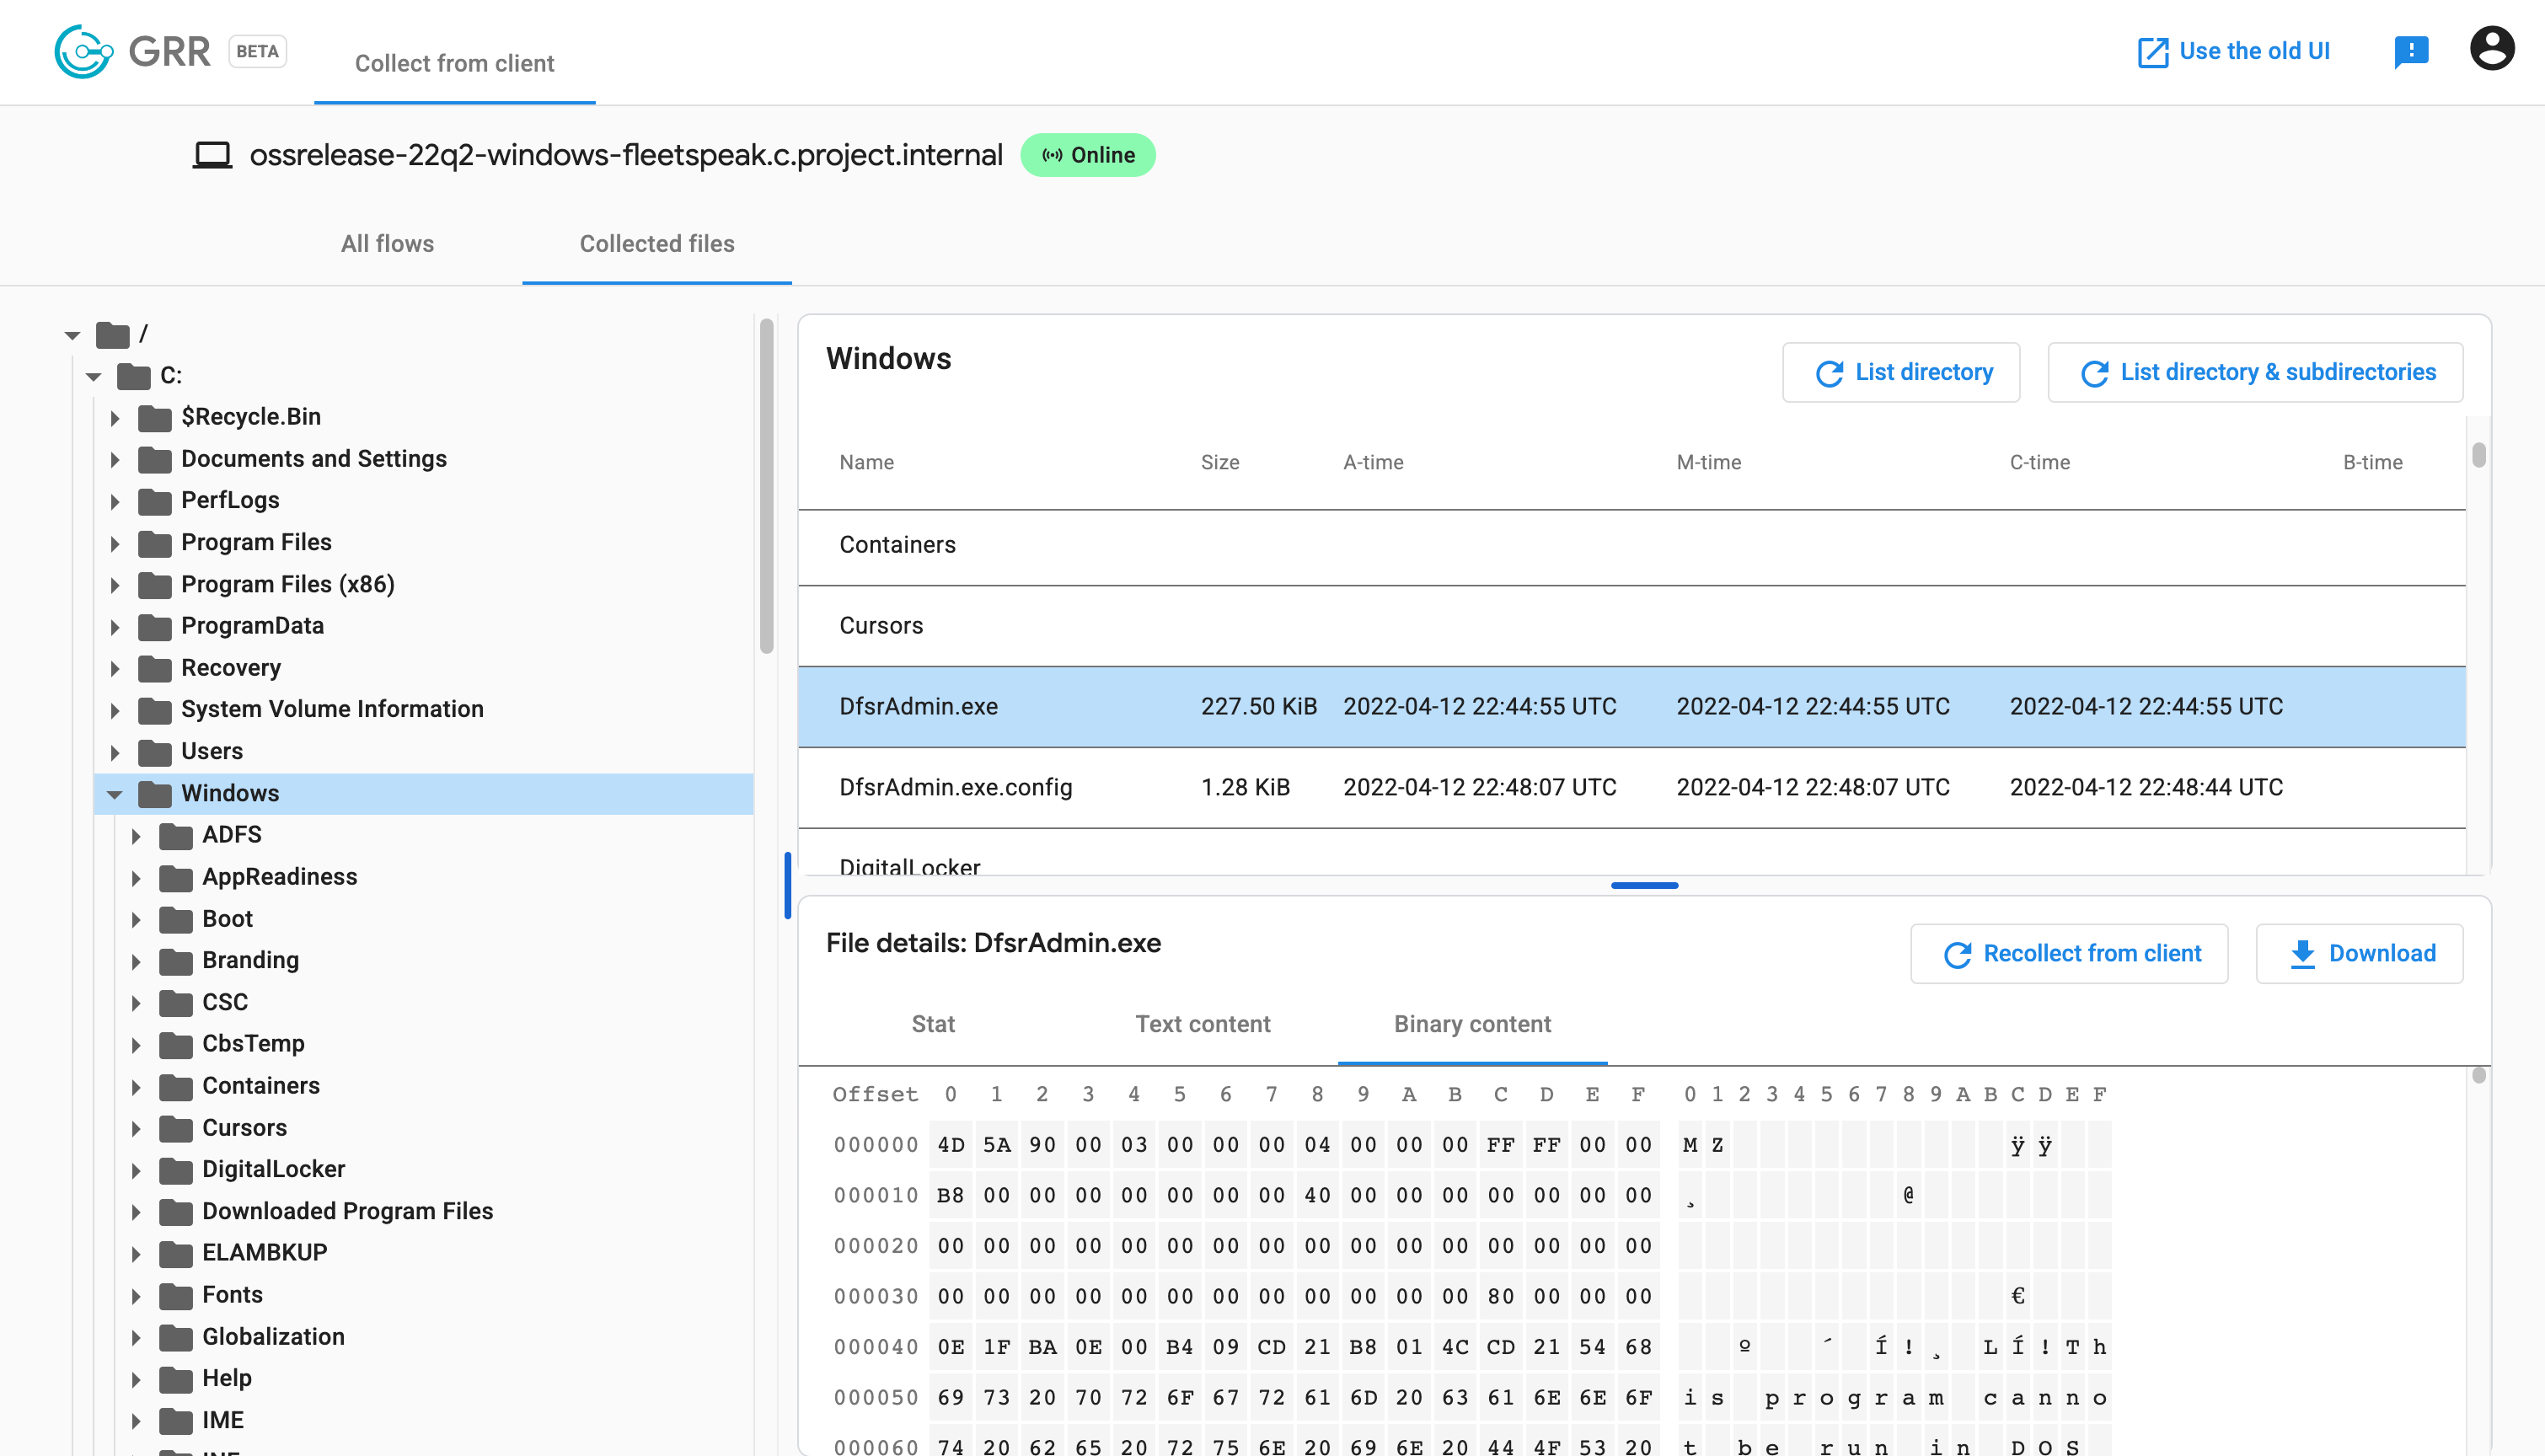 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 hunters-sec/cve-2025-31200
IOS audio buffer overflow CVE-2025-31200 POC
 dark-life944/cve-2025
This is POC for IOS 0click CVE-2025-43300
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
 kudaes/shelter
ROP-based sleep obfuscation to evade memory scanners
 volatilityfoundation/volatility
An advanced memory forensics framework
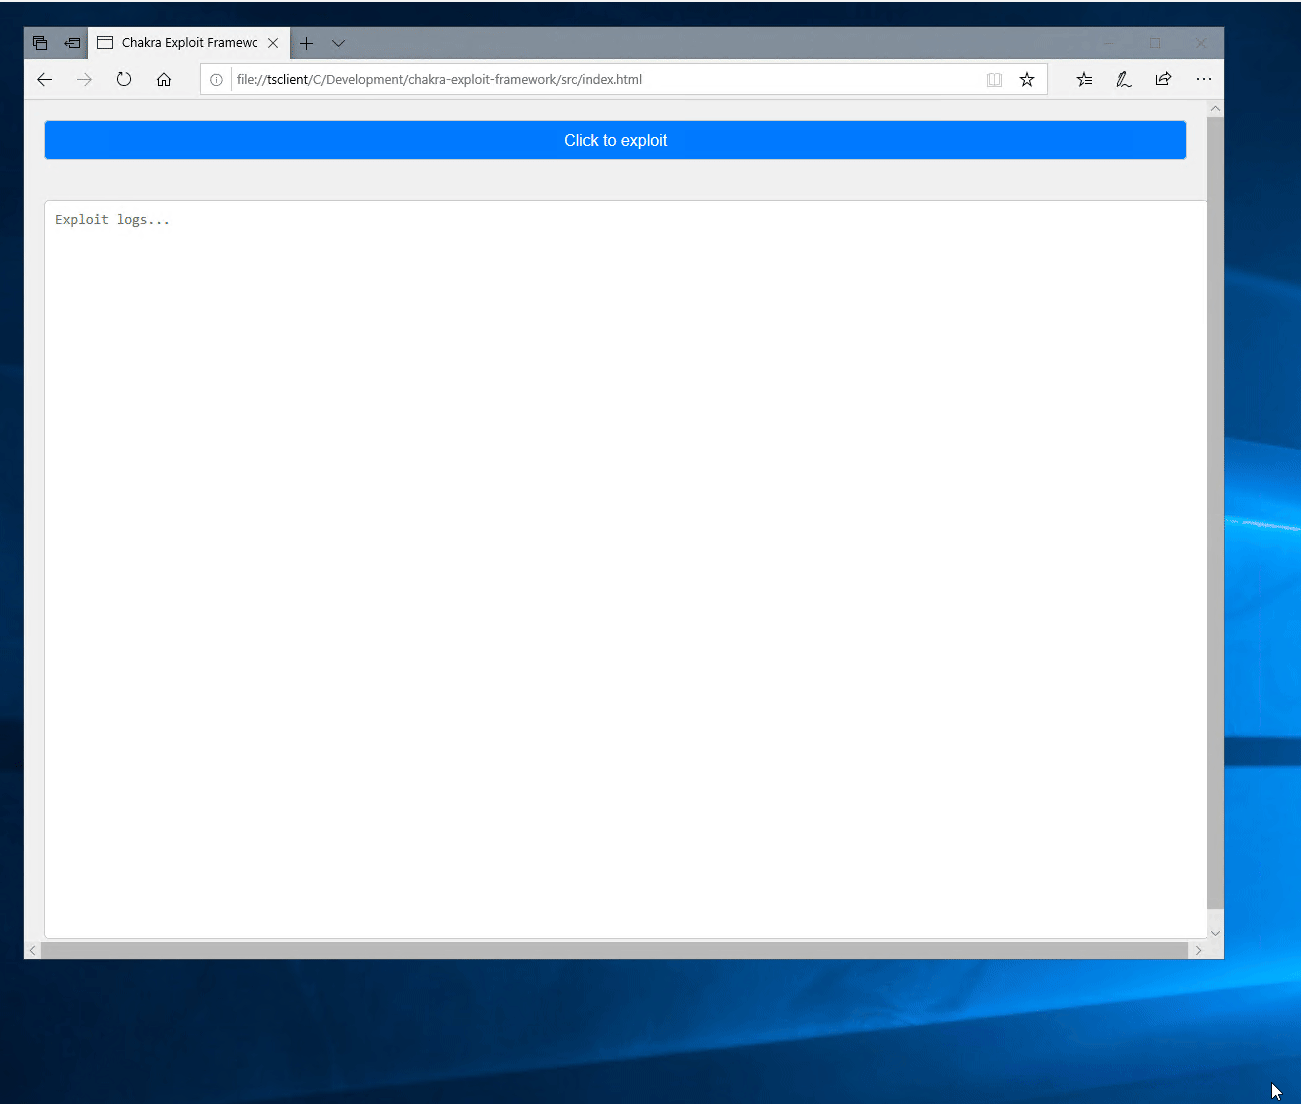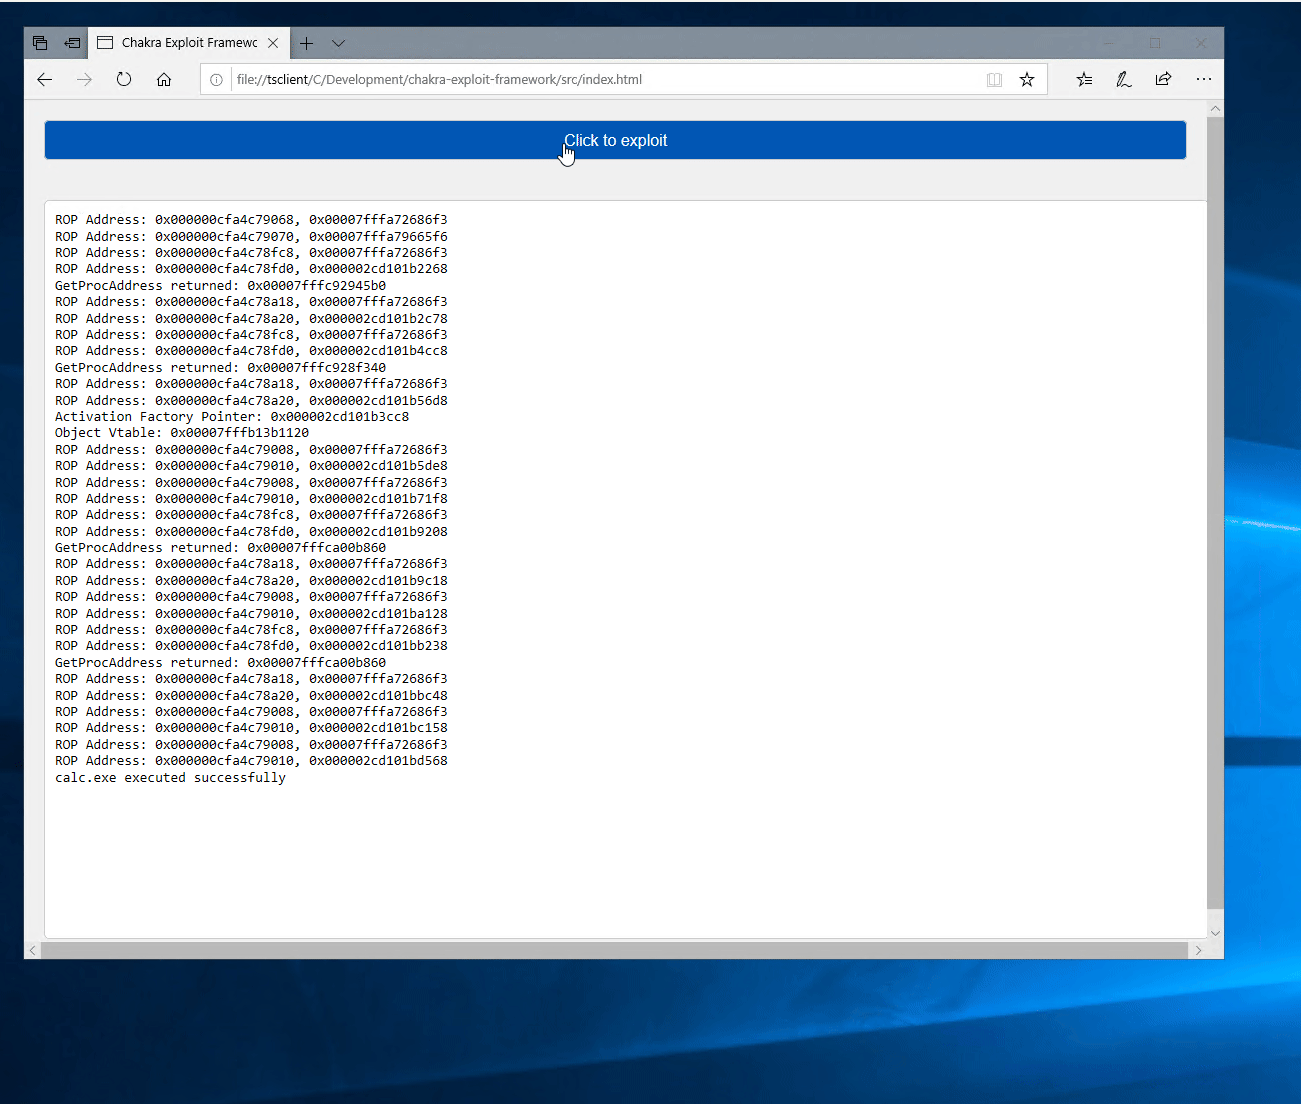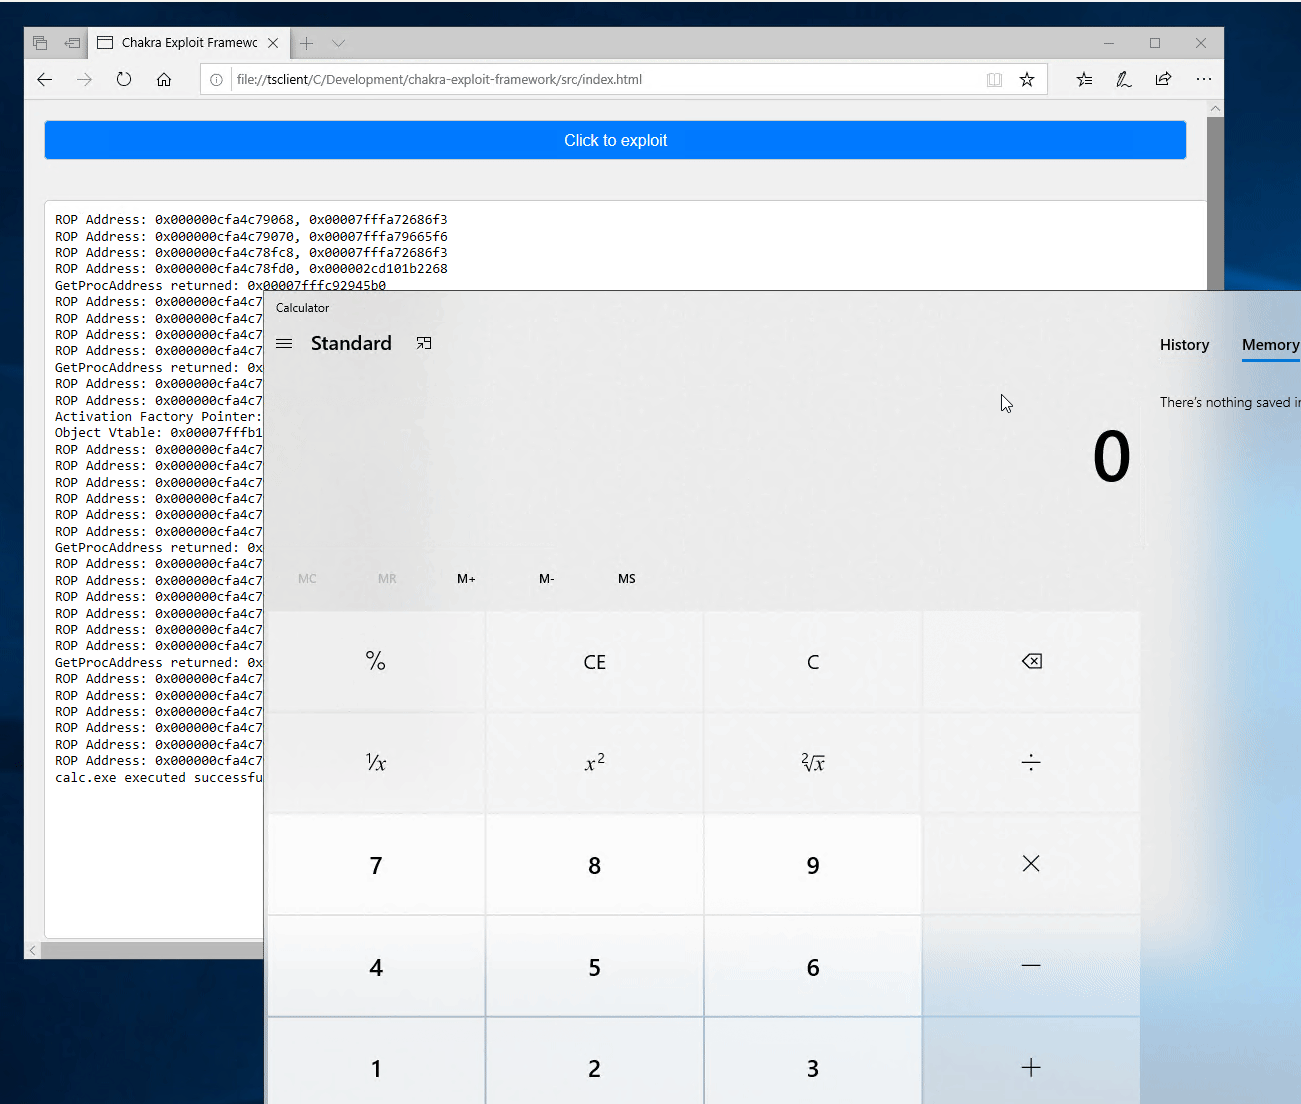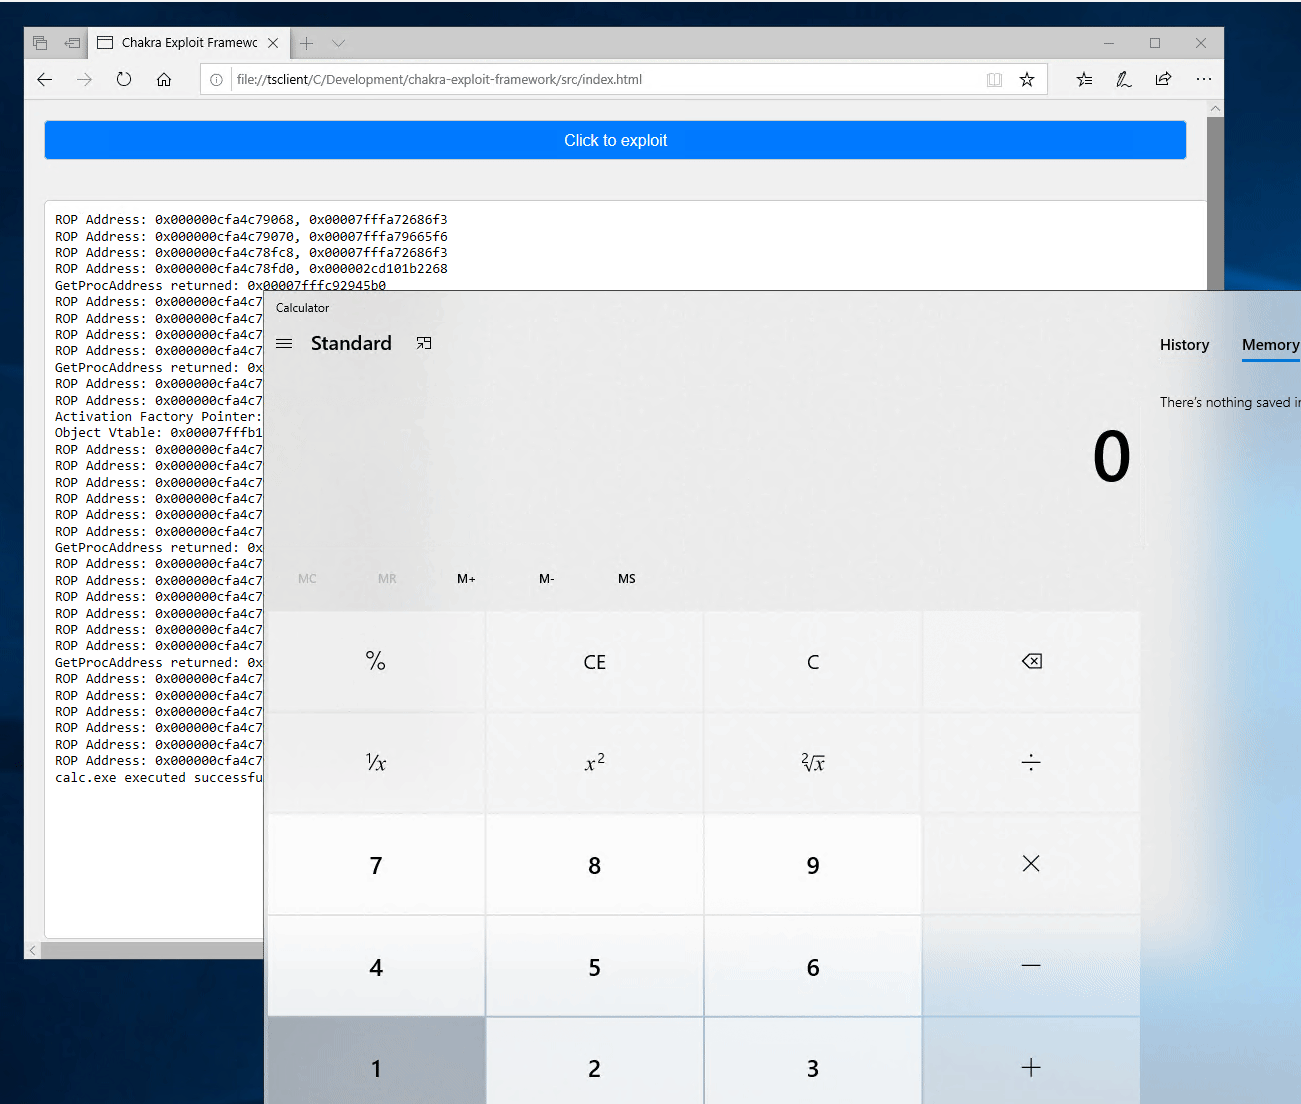 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 kyleavery/aceldr
Cobalt Strike UDRL for memory scanner evasion.
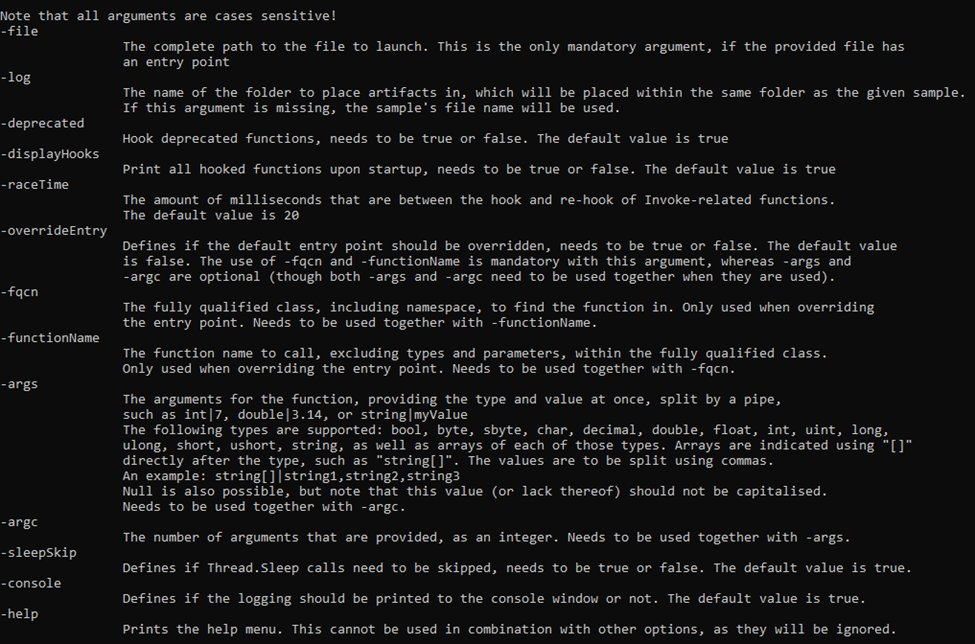 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files