
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
13 results
NativeDump preview

NativeDump

GitHubricardojoserf/nativedump

Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)

memory-forensicspost-exploitationred-teaming
74928 days ago
TrickDump preview

TrickDump

GitHubricardojoserf/trickdump

Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
memory-forensicspost-exploitationred-teaming
60128 days ago
cisco-CVE-2023-31488 preview

cisco-CVE-2023-31488

GitHubly1g3/cisco-cve-2023-31488

Cisco Email Security Appliance: Email to zero-click RCE as root - Remote Code Execution/Memory Corruption/ROP-chain

binary-exploitationemail-securityexploitation+8
12 months ago
Astral_Projection preview

Astral_Projection

GitHubkuwaitist/astral_projection

Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…

exploit-frameworksmemory-forensicspayload-development+4
734 months ago
BOF_RunPe preview

BOF_RunPe

GitHubntdallas/bof_runpe

BOF to run PE in Cobalt Strike Beacon without console creation

memory-forensicspost-exploitationred-teaming+1
2019 months ago
Shelter preview

Shelter

GitHubkudaes/shelter

ROP-based sleep obfuscation to evade memory scanners

exploit-frameworksmemory-forensicsred-teaming
3931 year ago
mimikatz preview

mimikatz

GitHubparrotsec/mimikatz

Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…

authenticationexploitationlateral-movement+5
2.6k2 years ago
AceLdr preview

AceLdr

GitHubkyleavery/aceldr

Cobalt Strike UDRL for memory scanner evasion.
exploit-frameworksmemory-forensicspayload-development+2
1.0k2 years ago
CrossC2Kit preview

CrossC2Kit

GitHubcrossc2/crossc2kit

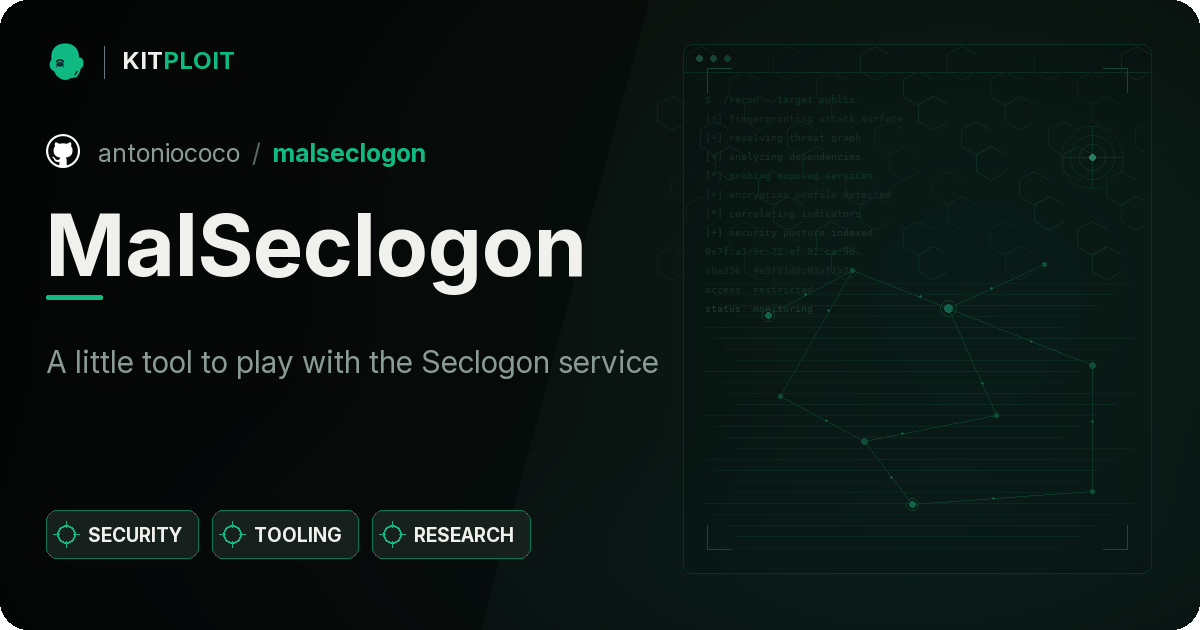
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
command-and-controlexploit-frameworksinformation-gathering+7
2293 years ago
MalSeclogon preview

MalSeclogon

GitHubantoniococo/malseclogon

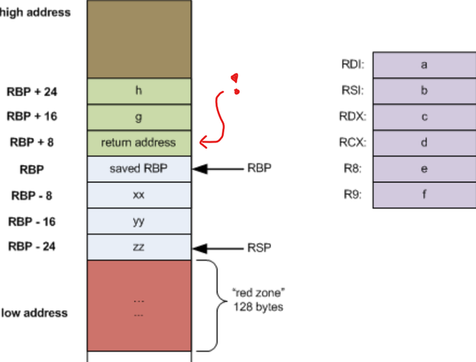
A little tool to play with the Seclogon service
exploitationlateral-movementmemory-forensics+3
3284 years ago
ThreadStackSpoofer preview

ThreadStackSpoofer

GitHubmgeeky/threadstackspoofer

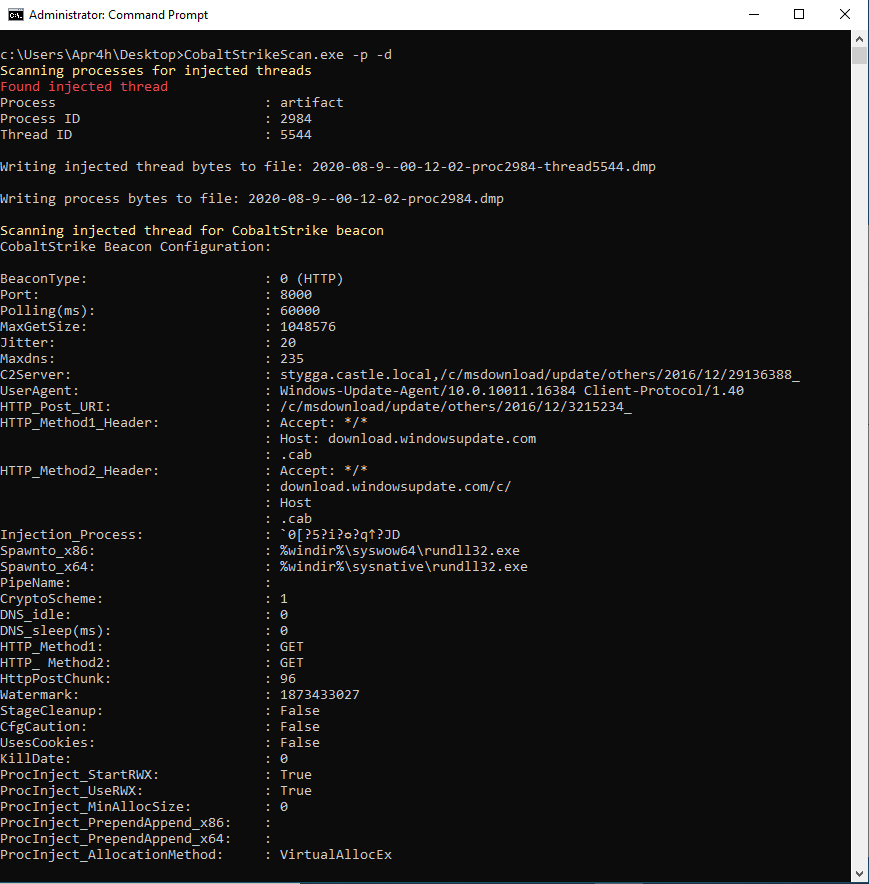
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
exploit-frameworksmalware-analysismemory-forensics+4
1.2k4 years ago
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

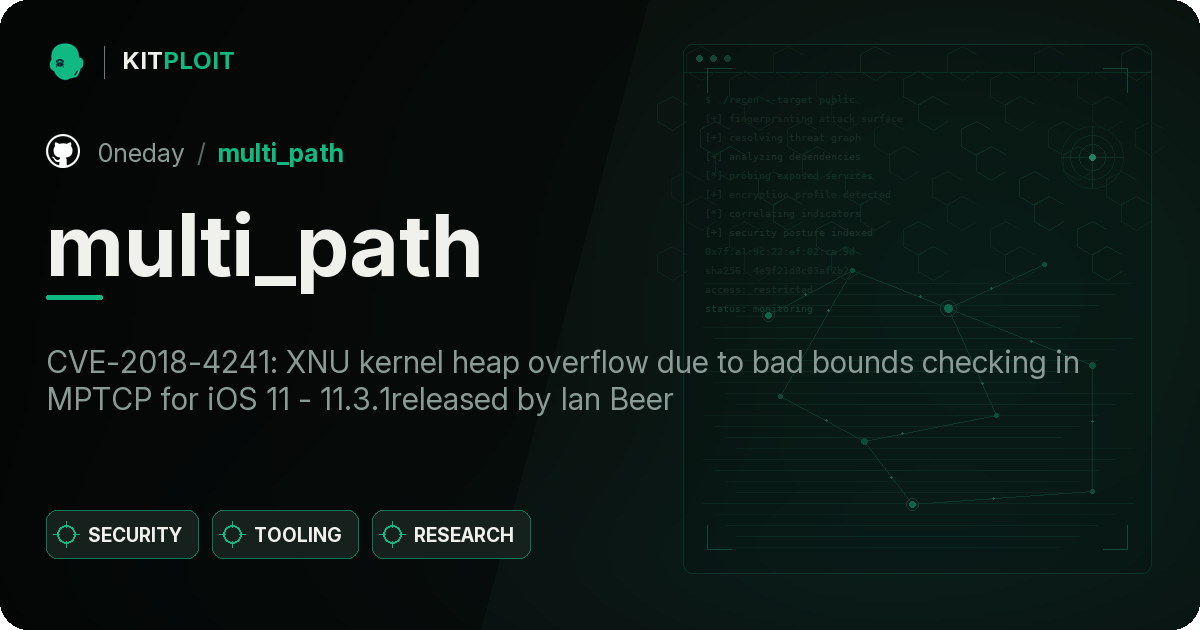
Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
9185 years ago
multi_path preview

multi_path

GitHub0neday/multi_path

CVE-2018-4241: XNU kernel heap overflow due to bad bounds checking in MPTCP for iOS 11 - 11.3.1released by Ian Beer

binary-exploitationexploitationexploit-frameworks+4
48 years ago