
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
59 results
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…


data-recoverydigital-forensicsdisk-forensics+9
3.0k
3h 34m ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.3k7h 21m ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k1 day ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

digital-forensicsdisk-forensicsforensics+4
5.1k1 day ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

data-recoverydigital-forensicsdisk-forensics+7
3.4k2 days ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
54.9k3 days ago
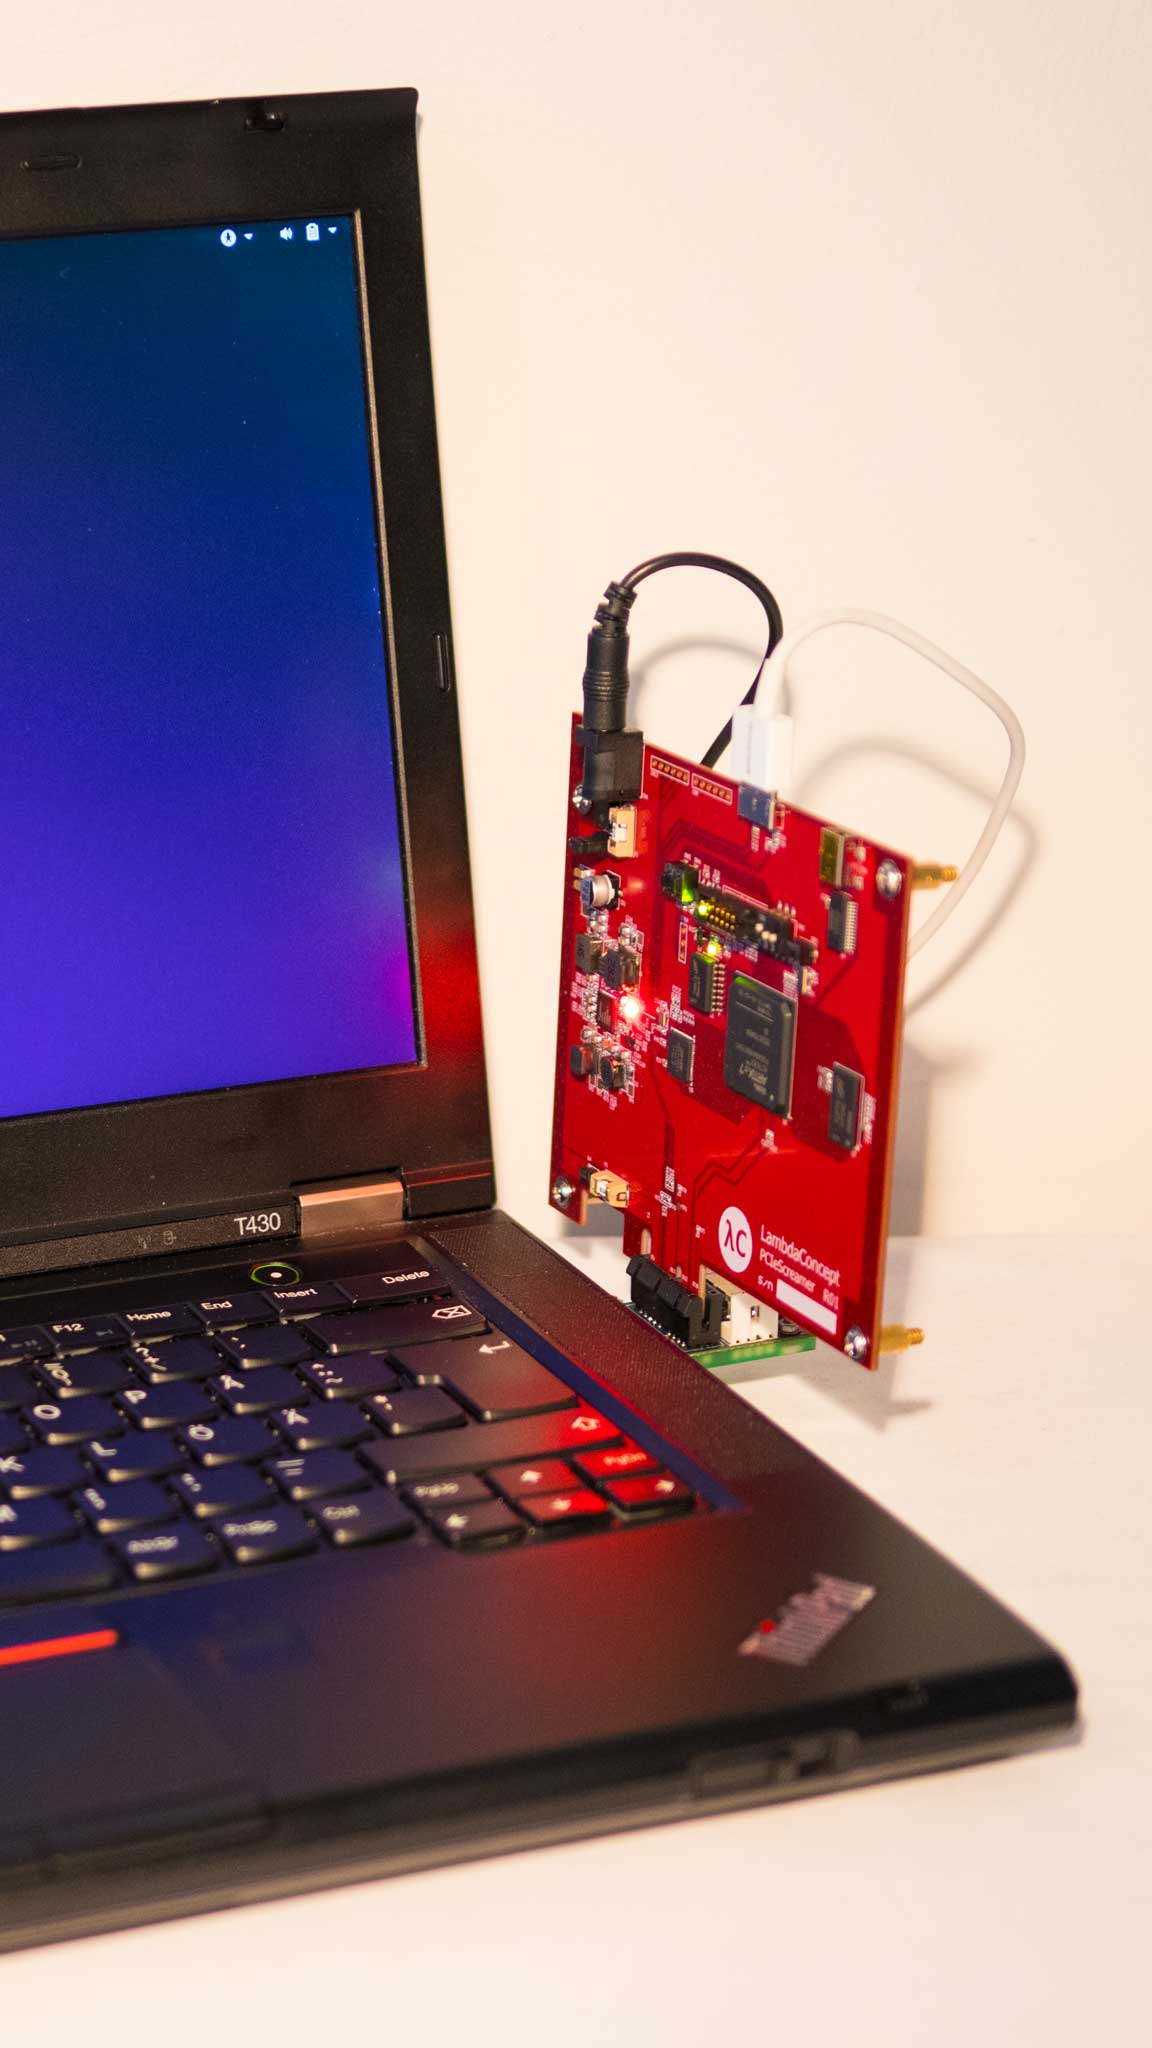
CVE-2026-28609-matroska-pcm-oob preview

CVE-2026-28609-matroska-pcm-oob

GitHubdevrodt2/cve-2026-28609-matroska-pcm-oob

Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
android-securitybinary-exploitationexploitation+5
5 days ago
libextractor-ole2-rce preview

libextractor-ole2-rce

GitHubhaitam-lazaar/libextractor-ole2-rce

PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…

binary-exploitationexploitationlabs-practice+4
11 days ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.4k11 days ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

digital-forensicsdisk-forensicsforensics+7
37018 days ago
KslKatzBof preview

KslKatzBof

GitHubprinciplecheck/kslkatzbof

Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…

exploitationmemory-forensicspayload-development+4
8923 days ago
bulk_extractor preview

bulk_extractor

GitHubsimsong/bulk_extractor

This is the development tree. Production downloads are at:
data-recoverydigital-forensicsdisk-forensics+9
1.4k25 days ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
431 month ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

binary-analysiscontainer-escapedata-recovery+7
101 month ago
forensictools preview

forensictools

GitHubcristianzsh/forensictools

Collection of forensic tools

binary-analysisdata-recoverydigital-forensics+7
7041 month ago
TrickDump preview

TrickDump

GitHubricardojoserf/trickdump

Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
memory-forensicspost-exploitationred-teaming
6031 month ago
CVE-2026-14431 preview

CVE-2026-14431

GitHubjaf0rk/cve-2026-14431

Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
binary-exploitationexploitationmemory-forensics+2
2 months ago
BareMetal-RAM-Dumper preview

BareMetal-RAM-Dumper

GitHubpiat0n/baremetal-ram-dumper

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.

data-recoverydigital-forensicsexploitation+3
1042 months ago
Previous1234Next
