
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
22 results
lithium-kernel preview

lithium-kernel

GitHubgmh5225/lithium-kernel

Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…

anti-botbinary-exploitationmemory-forensics+1
3 months ago
DMA-ProcessDumper preview

DMA-ProcessDumper

GitHubgmh5225/dma-processdumper

Simple Process Dumper using DMA over a PCIe FPGA device
data-exfiltrationforensicshardware-hacking+3
4 years ago
clairvoyance preview

clairvoyance

GitHub0vercl0k/clairvoyance

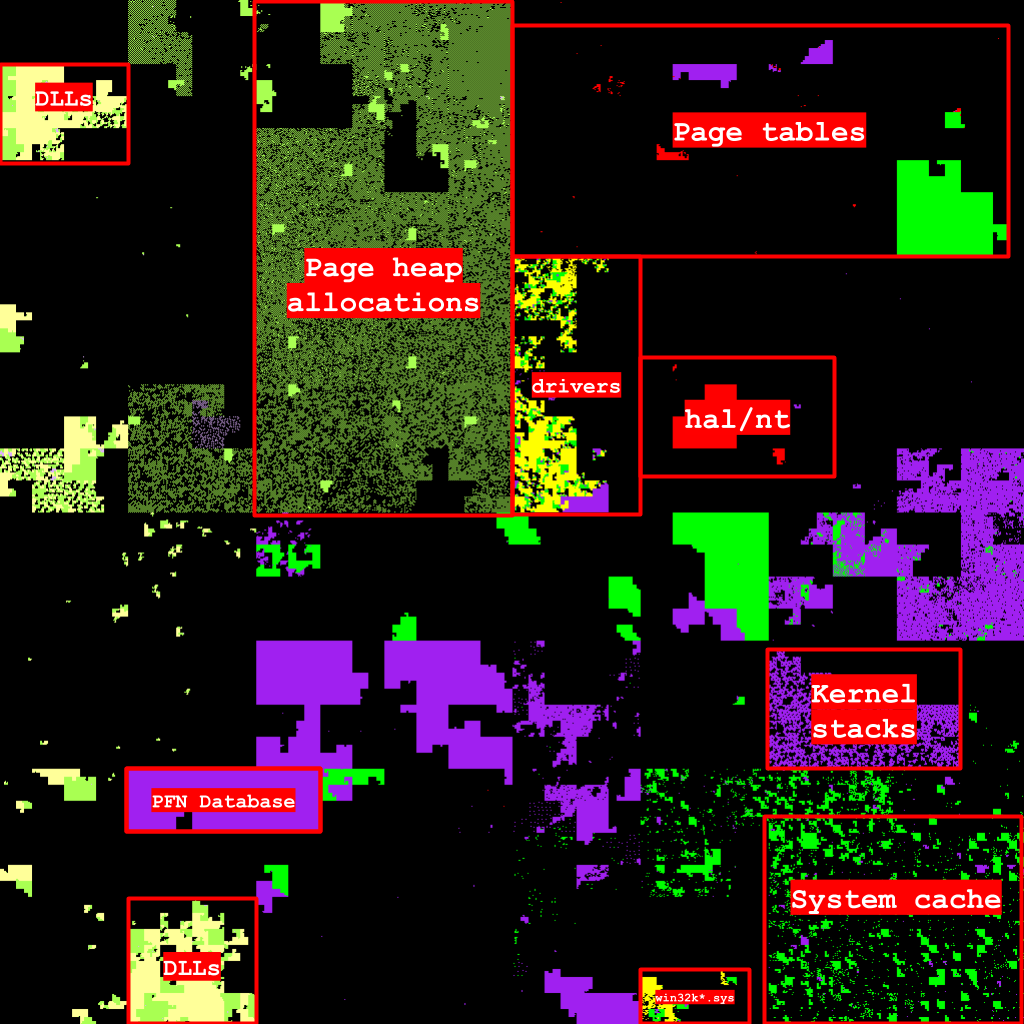
Visualize the virtual address space of a Windows process on a Hilbert curve.
digital-forensicsforensicsmemory-forensics
3125 years ago
empty_list preview

empty_list

GitHubjailbreaks/empty_list

empty_list - exploit for p0 issue 1564 (CVE-2018-4243) iOS 11.0 - 11.3.1 kernel r/w
binary-exploitationexploitationios-security+3
188 years ago
dtrace-memaccess_cve-2020-27949 preview

dtrace-memaccess_cve-2020-27949

GitHubseemoo-lab/dtrace-memaccess_cve-2020-27949

Proof-of-concept exploit for CVE-2020-27949, demonstrating arbitrary memory read/write in macOS processes via DTrace fasttrap ioctl without elevated…
binary-exploitationexploitationmemory-forensics+3
335 years ago
CVE-2026-50416-writeup-and-poc preview

CVE-2026-50416-writeup-and-poc

GitHubkarollooool/cve-2026-50416-writeup-and-poc

CVE-2026-50416: Windows 11 KASLR bypass

binary-analysisctfeducation+7
5017 days ago
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
50.1k2 days ago
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
digital-forensicsforensicsincident-response+3
3 months ago
gluegate preview

gluegate

GitHubsbousseaden/gluegate

Memory API proxy via signed mozglue.dll
defensive-toolsids-ips-evasionmemory-forensics+2
414 months ago
ctl_ctloutput-leak preview

ctl_ctloutput-leak

GitHubbazad/ctl_ctloutput-leak

CVE-2017-13868: Information leak of uninitialized kernel heap data in XNU.
binary-exploitationexploitationinformation-gathering+2
278 years ago
CVE-2022-3699 preview

CVE-2022-3699

GitHubalfarom256/cve-2022-3699

Lenovo Diagnostics Driver EoP - Arbitrary R/W
binary-exploitationexploitationhardware-security+3
1783 years ago
CVE-2021-4034 preview

CVE-2021-4034

GitHubdevianntsec/cve-2021-4034

Master's thesis research on CVE-2021-4034 (PwnKit) local privilege escalation. Multi-payload Python exploit with 7 modes including interactive shell,…
binary-exploitationeducationexploitation+7
17 months ago
GhostKatz preview

GhostKatz

GitHubrainbowdynamix/ghostkatz

Dump LSASS via physical memory read primitives in vulnerable kernel drivers
binary-exploitationexploitationmemory-forensics+4
3449 months ago
cormem-read-poc preview

cormem-read-poc

GitHub4d4j/cormem-read-poc

This tool demonstrates CVE-2026-38194, a vulnerability in Teledyne Digital Imaging Sapera Memory Manager (v9.0.0.0 and below). The CORMEM.SYS kernel…
binary-exploitationeducationexploitation+3
94 months ago
CVE-2026-46215-POC preview

CVE-2026-46215-POC

GitHub0xcyberstan/cve-2026-46215-poc

Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…
binary-exploitationctfeducation+4
114 months ago
Astral_Projection preview

Astral_Projection

GitHubkuwaitist/astral_projection

Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
exploit-frameworksmemory-forensicspayload-development+4
756 months ago
splinter preview

splinter

GitHubawrped/splinter

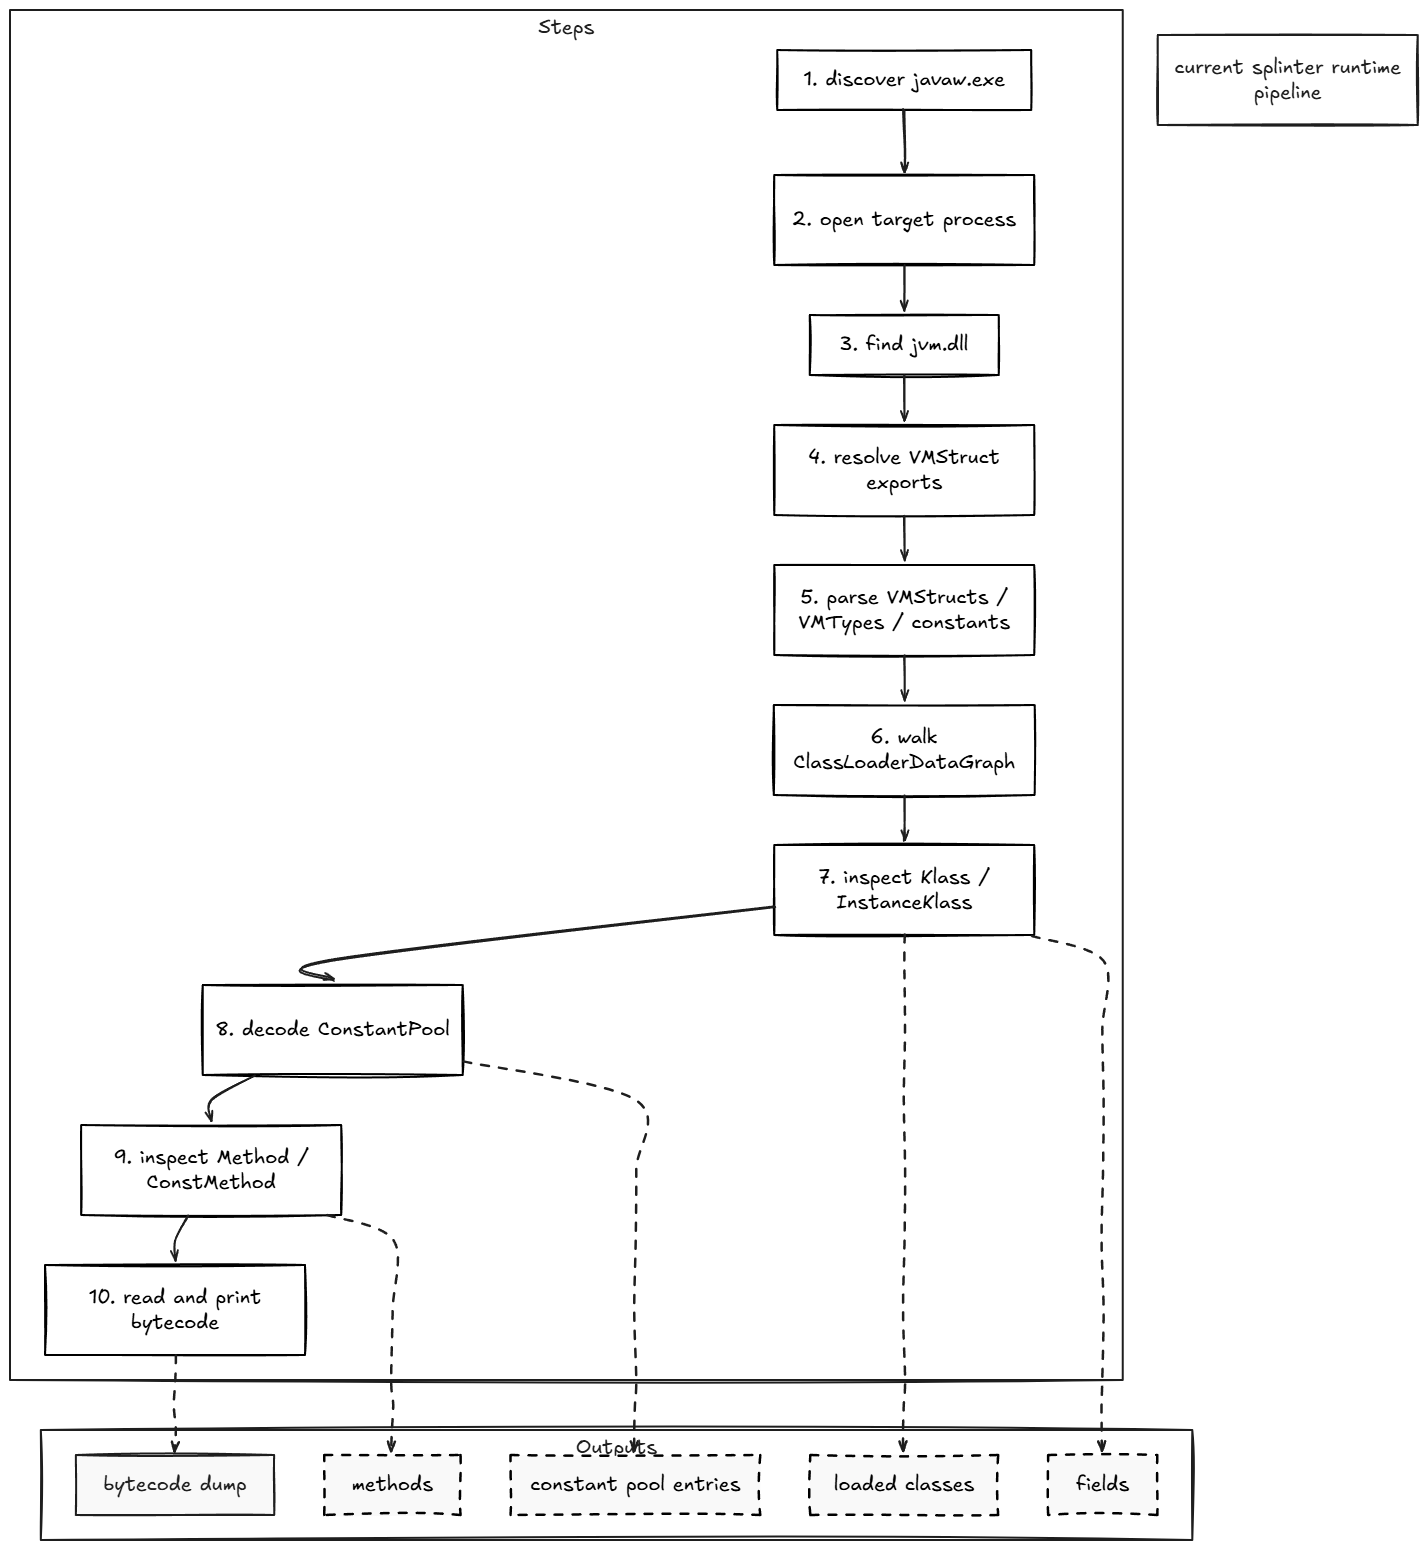
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
binary-analysisdebuggersdynamic-analysis-sandboxing+4
912 months ago
icebox preview

icebox

GitHubthalium/icebox

Virtual Machine Introspection, Tracing & Debugging

debuggersdynamic-analysis-sandboxingforensics+3
6034 years ago
Previous12Next