
CVE-2026-85046
 jamezx32/cve-2026-85046
V8 inlined Array.prototype.sort elements-kind confusion - PoC + addrof (N-day research)
exploitationmemory-forensicspapers-research+3
jamezx32/cve-2026-85046V8 inlined Array.prototype.sort elements-kind confusion - PoC + addrof (N-day research)
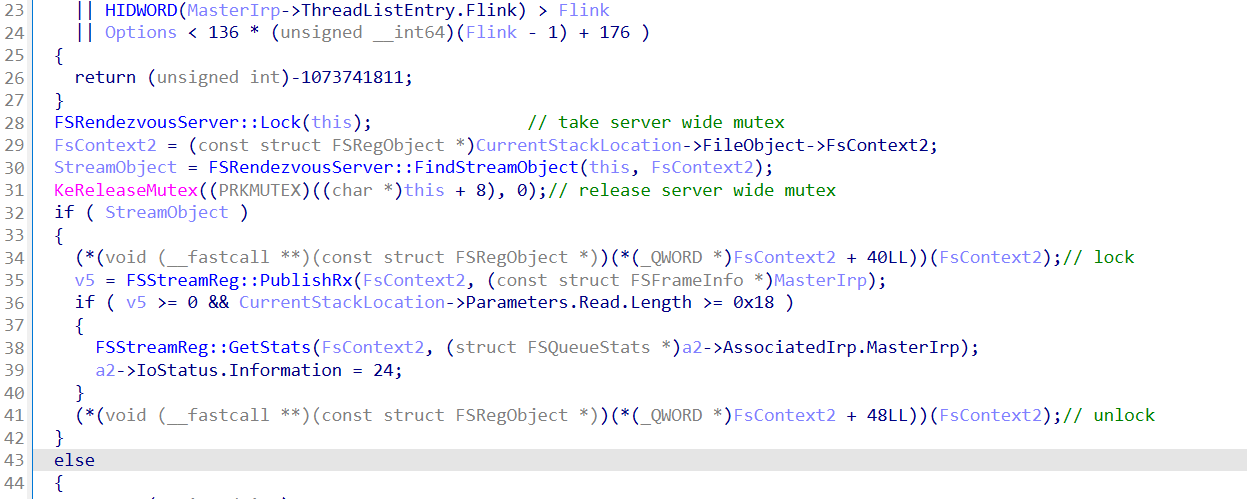 wkpwn/cve-2026-83834
Analysis of a use-after-free race in FSRendezvousServer::PublishRx and ConsumeTx, where Close() can free an FSStreamReg object between mutex release…
 saretawa/cve-2026-77396
Proof-of-concept that crafts a malicious AVI file to trigger a heap out-of-bounds write in the PJSIP AVI parser (CVE-2026-77396), with ASan…
 34zy/cve-2026-86950
Exploitation framework for CVE-2026-86950, a CoreGraphics integer overflow: crafts malicious TrueType fonts and PDFs, extracts ASLR leaks, and builds…
 0xsemizzz/cve-2026-86476
Proof of concept for CVE-2026-86476: GStreamer GstVideoMeta heap out-of-bounds read/write via unixfd deserialization, with ASan repro and RCE chain.
 nilondal/libtar-cve-2021-33644-followup
libtar: incomplete fix for CVE-2021-33643/CVE-2021-33644 (heap OOB read in GNU long-name handling)
 ylh440104/infinitycore-android-cve-2026-98260
ARM64 Android proof-of-concept for CVE-2026-98260, a POSIX timer UAF in the kernel Timer subsystem, with a full race, heap spray, and root escalation…
 01luyicheng/cve-2026-99999
Simulation-only proof of concept for CVE-2026-99999, a Linux kernel virtio-net IPv4 csum_start validation bug enabling guest-to-host heap memory…
 offline-ant/tcp2kaslr
CVE-2026-98432: a plain IPv4 TCP server is vulnerable, MPTCP is not the trigger. Bug trigger, evidence and analysis.
 addxemmm/cve-2026-98260-pudding-android
Target-specific Android CVE-2026-98260 research port for Xiaomi 17 (pudding)
 sganggs/cve-2026-98260-brm-an00
CVE-2026-98260 temporary root for HONOR Win2 BRM-AN00, handed to BakaSU. No flashing.
 yukonga/cve-2026-98260
Android kernel POSIX CPU timer use-after-free exploit for 6.12.69 that achieves uid=0 shell or KernelSU late-load via fake credentials.
 woshigenm/cve-2026-98260
Android kernel LPE research for CVE-2026-98260 (posix-cpu-timers UAF): trigger PoC, fake-cred and real-cred uid-0 shell chains, plus a…
 cuteaplane/cve-2026-98260-for-opd2501
Android kernel LPE exploit for CVE-2026-98260 (POSIX CPU timer UAF), ported to OPPO Pad Air 5 / MT6878, gaining temporary root and loading KernelSU.
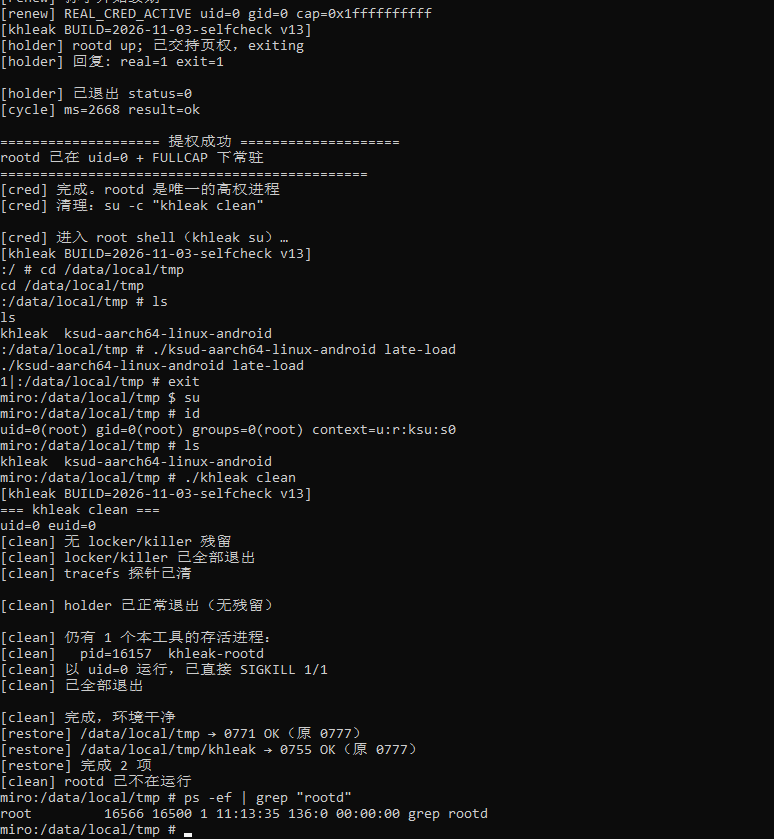 rmdycz/k80pro-miro-cve-2026-98260
Device-bound CVE-2026-98260 adaptation for RedMi K80pro miro OS 3.0.305.0
 ylh440104/infinitycore-android-cve-2026-98256
ARM64 Android port of the official PoC for CVE-2026-98256, a Signal subsystem kernel race-condition local privilege escalation with hardcoded heap…
 malhyuk/cve-2026-98180
Proof-of-concept and KASAN-confirmed KUnit reproducer for CVE-2026-98180, a drm/msm use-after-free of scheduler-containing ring and VM objects…
 ylh440104/infinitycore-android-cve-2026-97941
ARM64 Android port of the official PoC for CVE-2026-97941, a SLAB subsystem kernel vulnerability, with ported race timing and heap layout for 7.0/7.2…