
memdumper
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
digital-forensicsids-ips-evasioninformation-gathering+4
1
cenobyte-vincit/memdumperAbuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
 nccgroup/windowsfirewallhookdriverenumeration
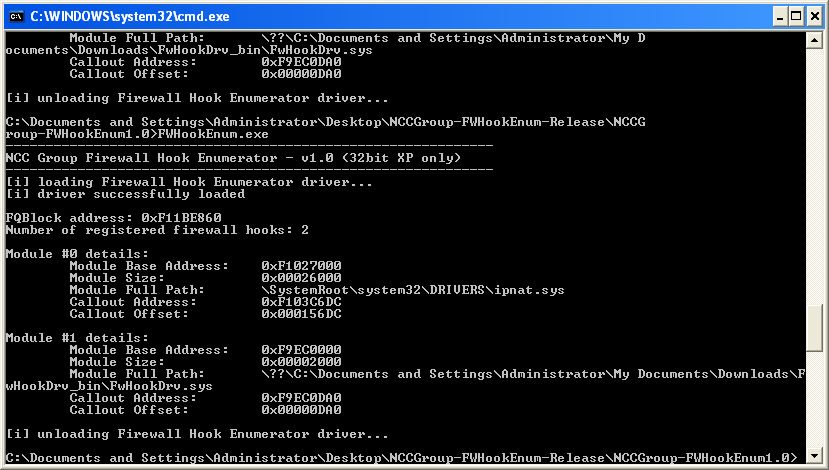
Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003
 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
 idov31/novahypervisor
Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…