

LiME
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
digital-forensicsforensicsincident-response+2
2.1k
jtsylve/limeKernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 nccgroup/killedprocesscanary
A canary designed to minimize the impact from certain Ransomware actors
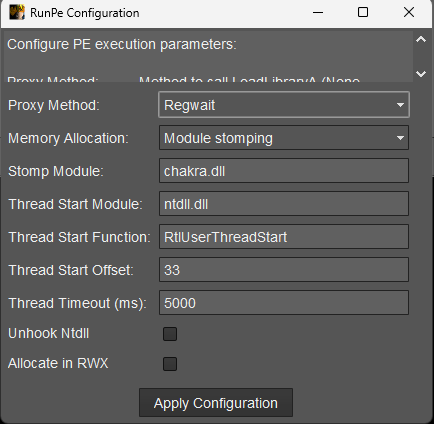 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 renukaselvar/libunwind_cve-2015-3239
C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…
 renukaselvar/libunwind_cve-2015-3239_after
Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.