
libextractor-ole2-rce
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
binary-exploitationexploitationlabs-practice+4
haitam-lazaar/libextractor-ole2-rcePoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
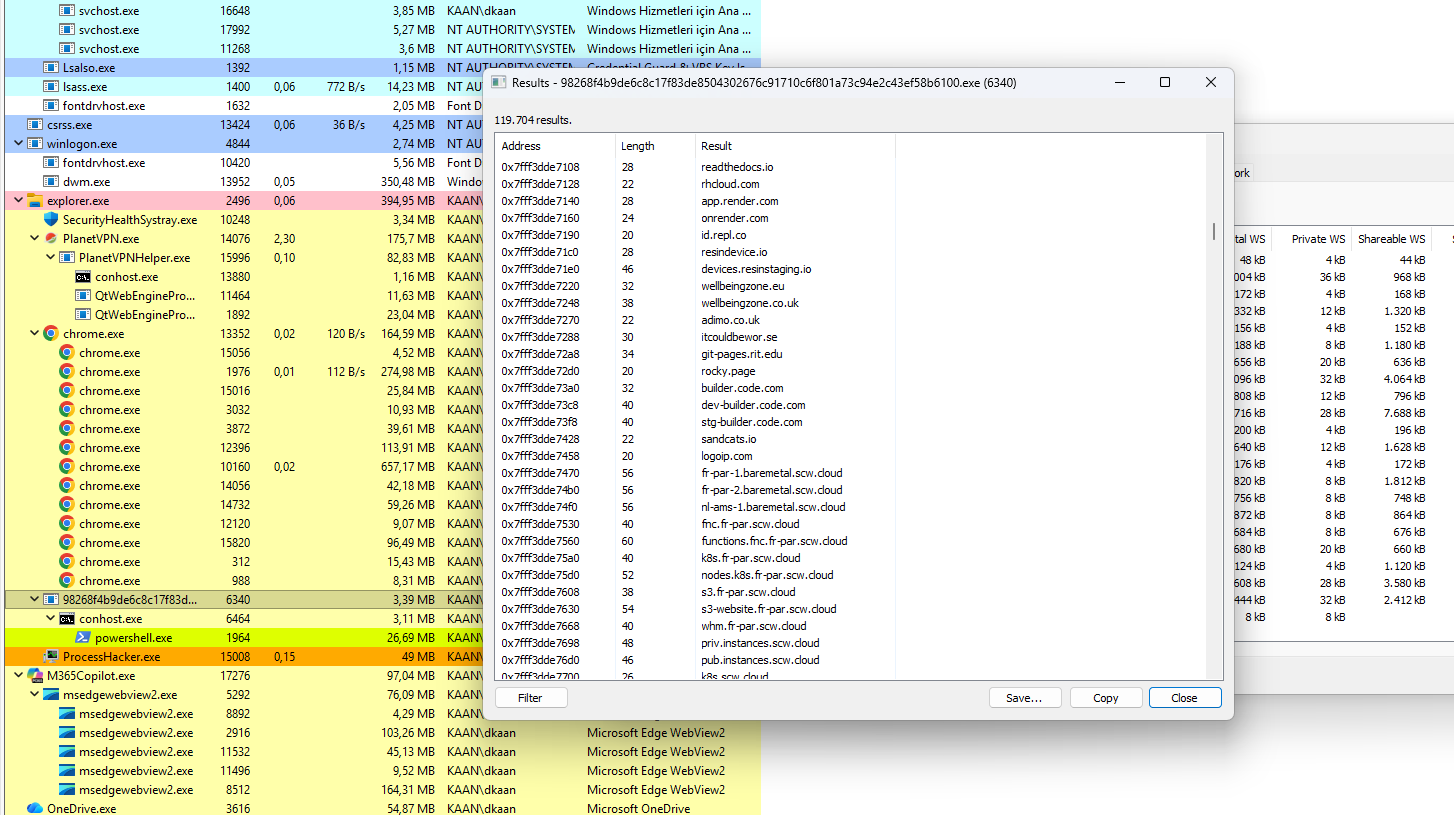 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
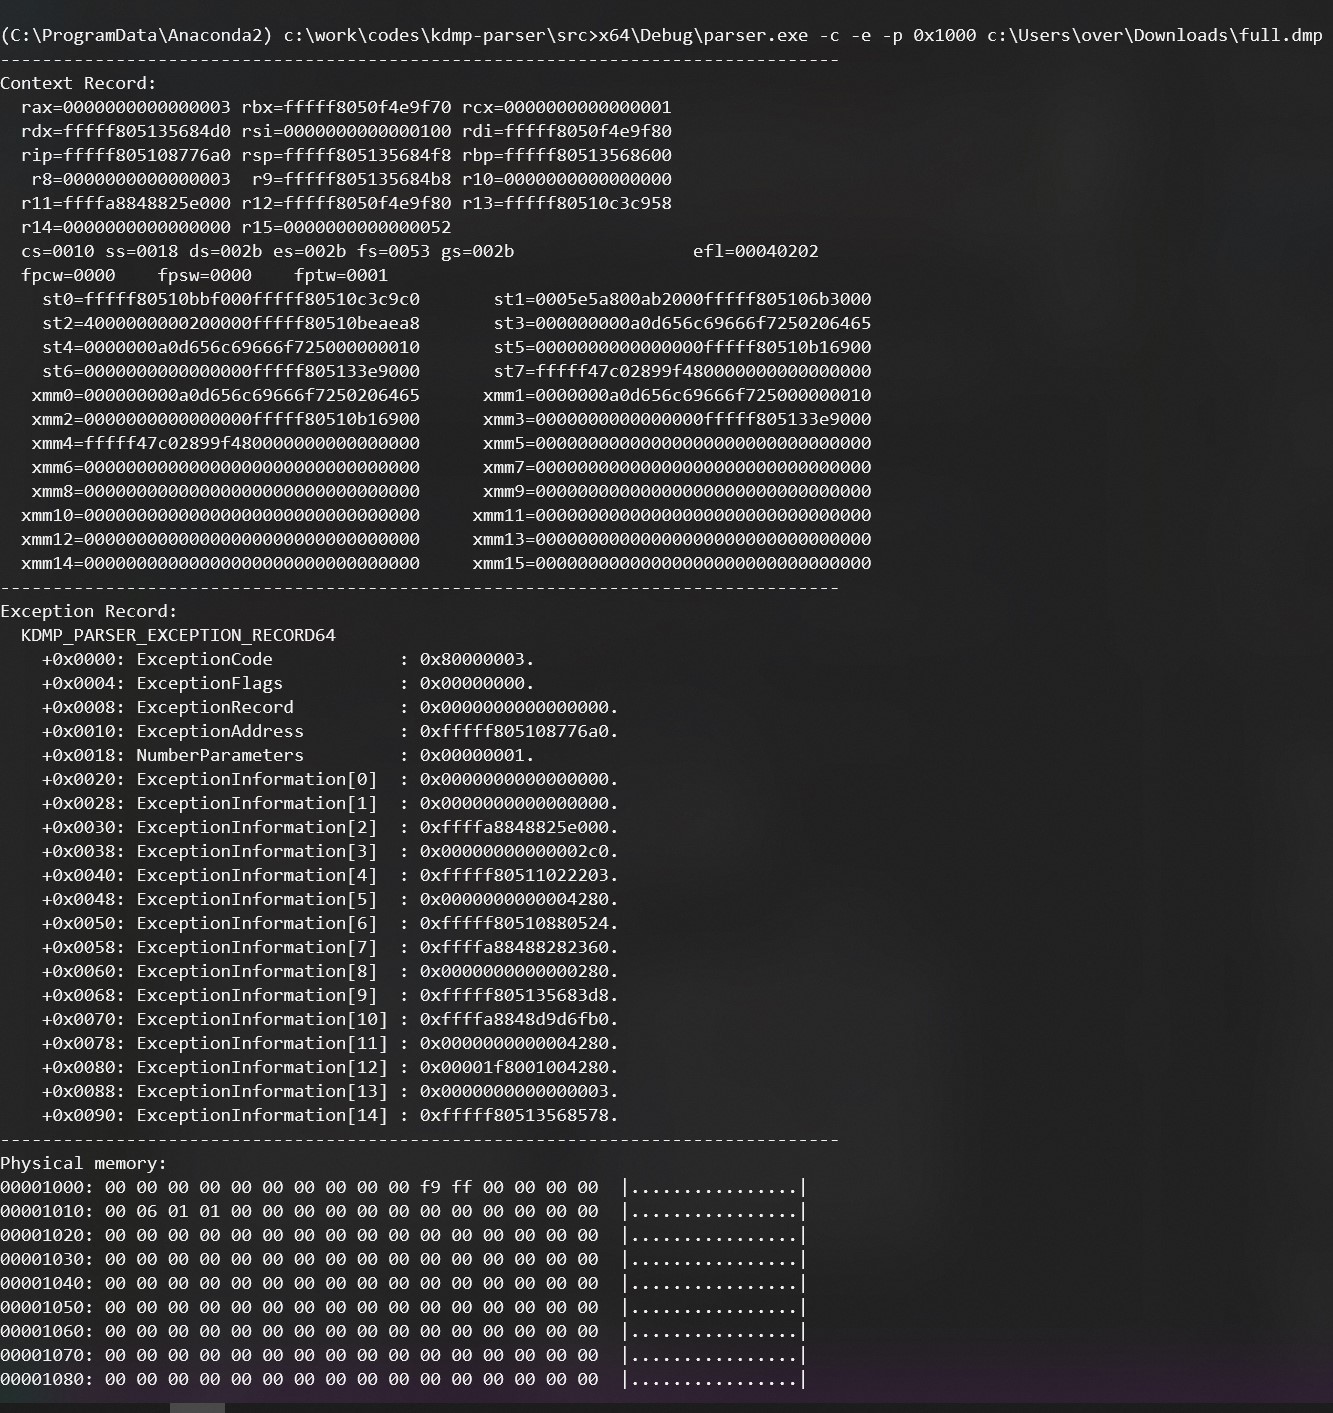 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
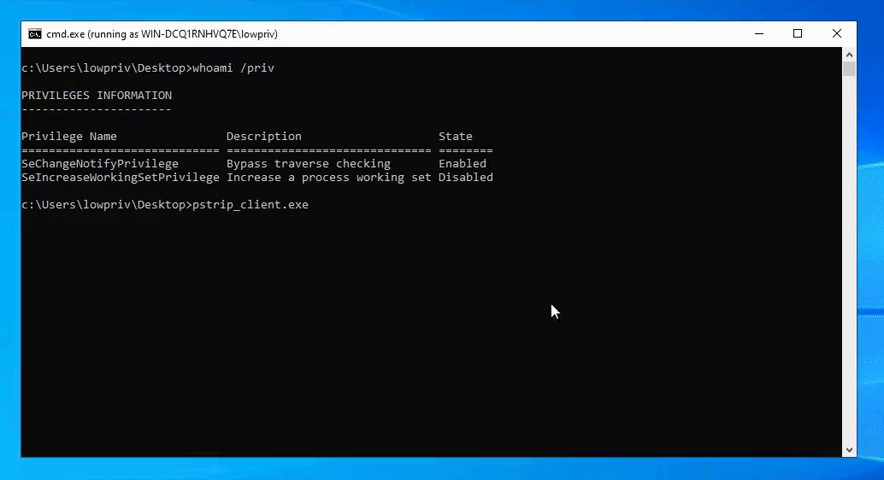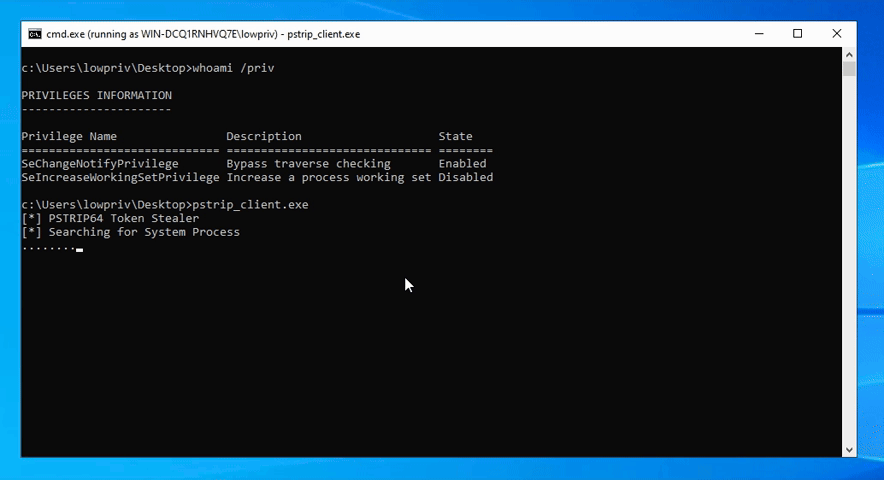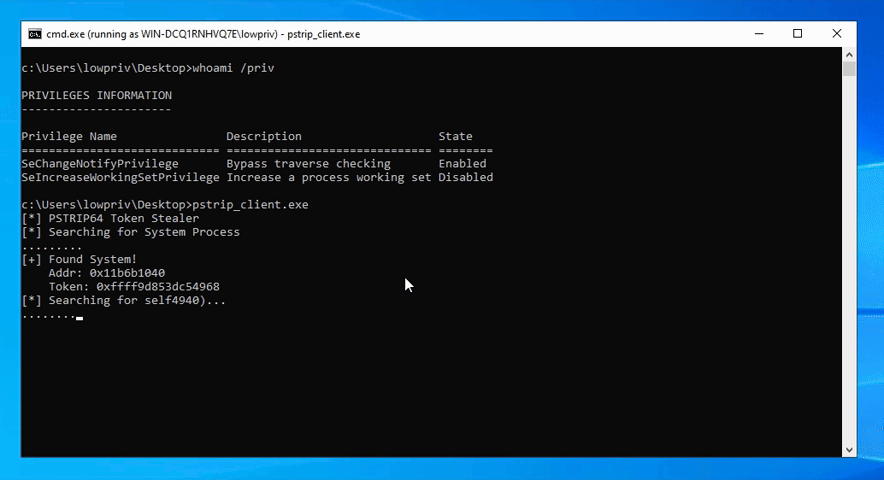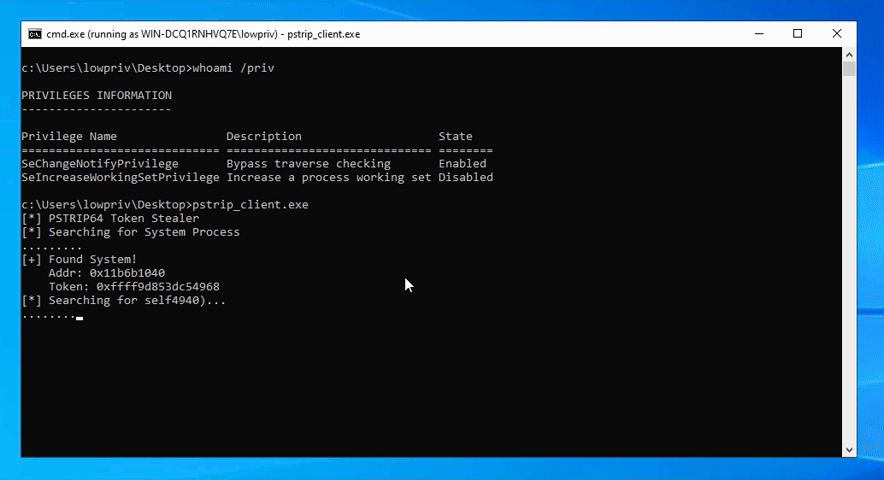 smarttfoxx/cve-2026-29923
The pstrip64.sys kernel driver exposes an IOCTL that allows low-privileged users to map arbitrary ranges of physical memory into their own virtual…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
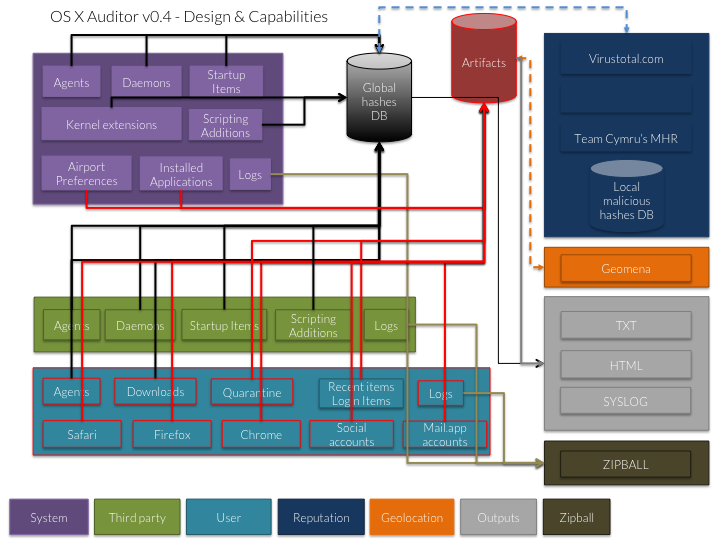 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
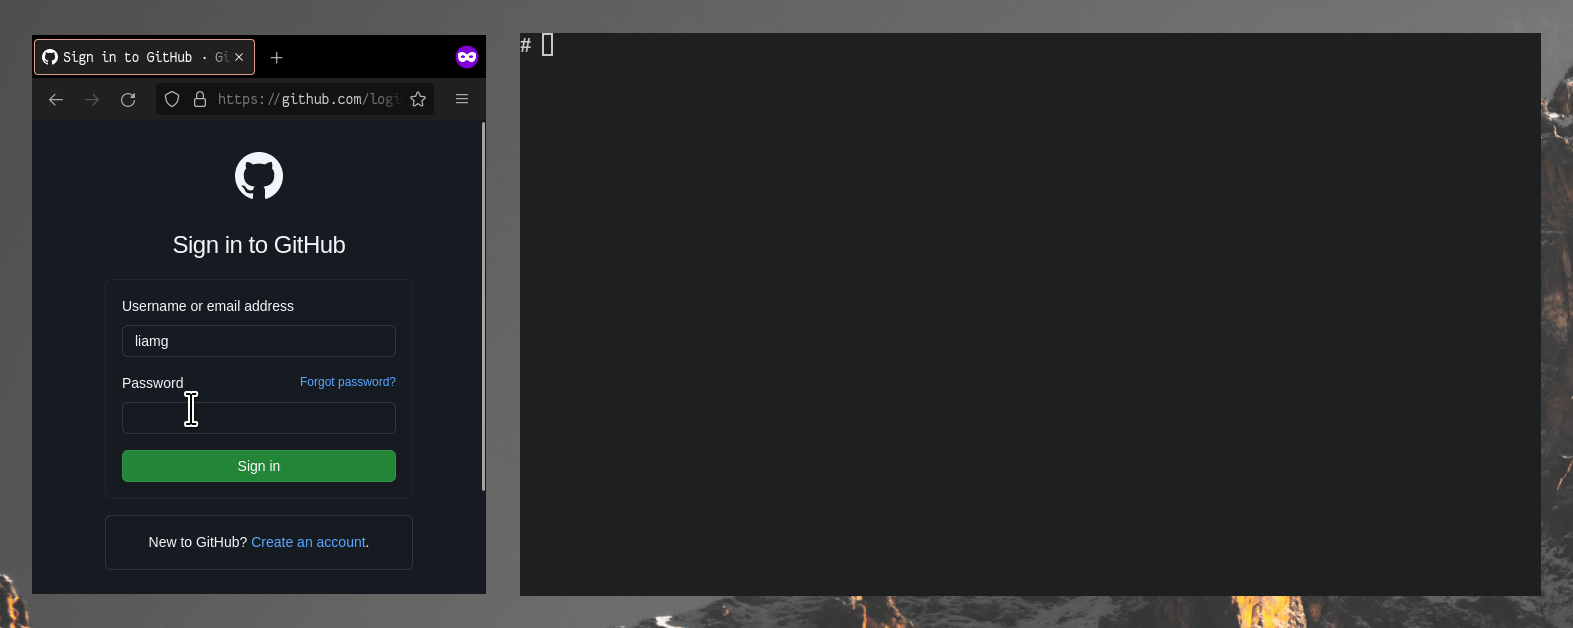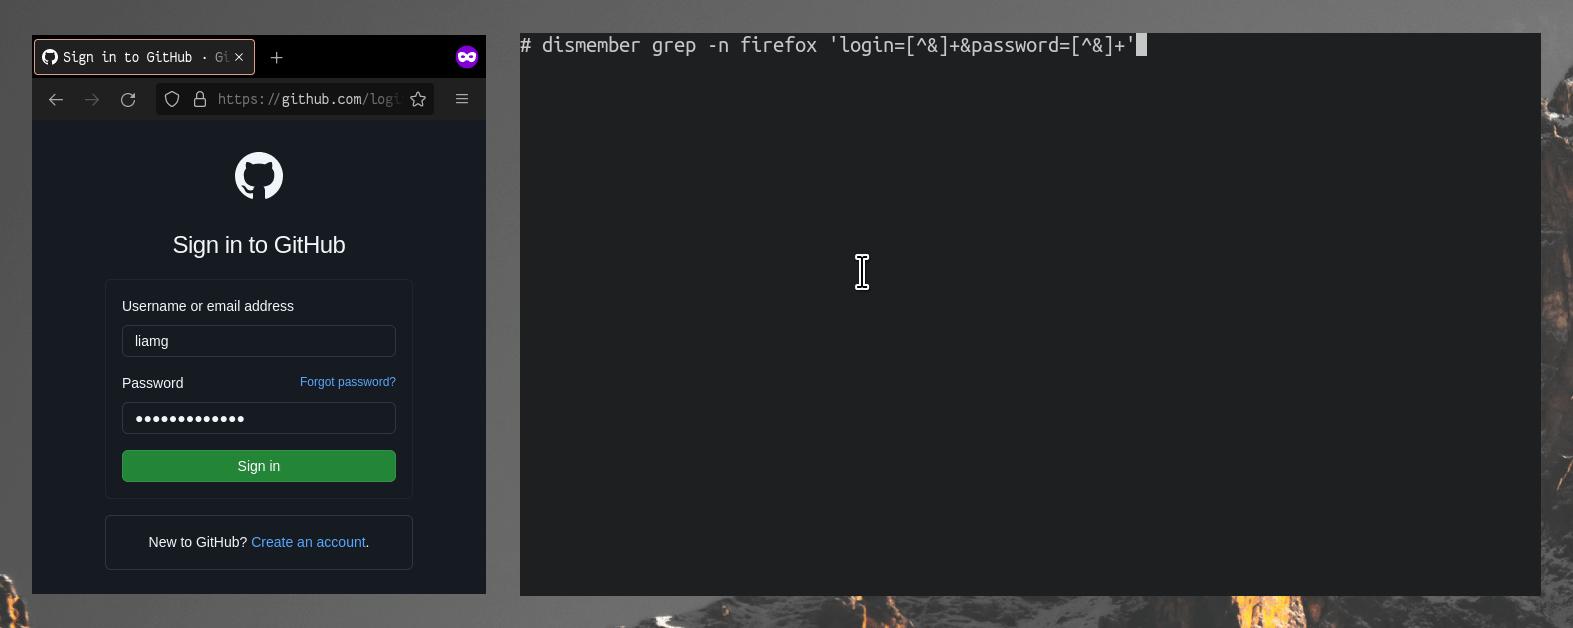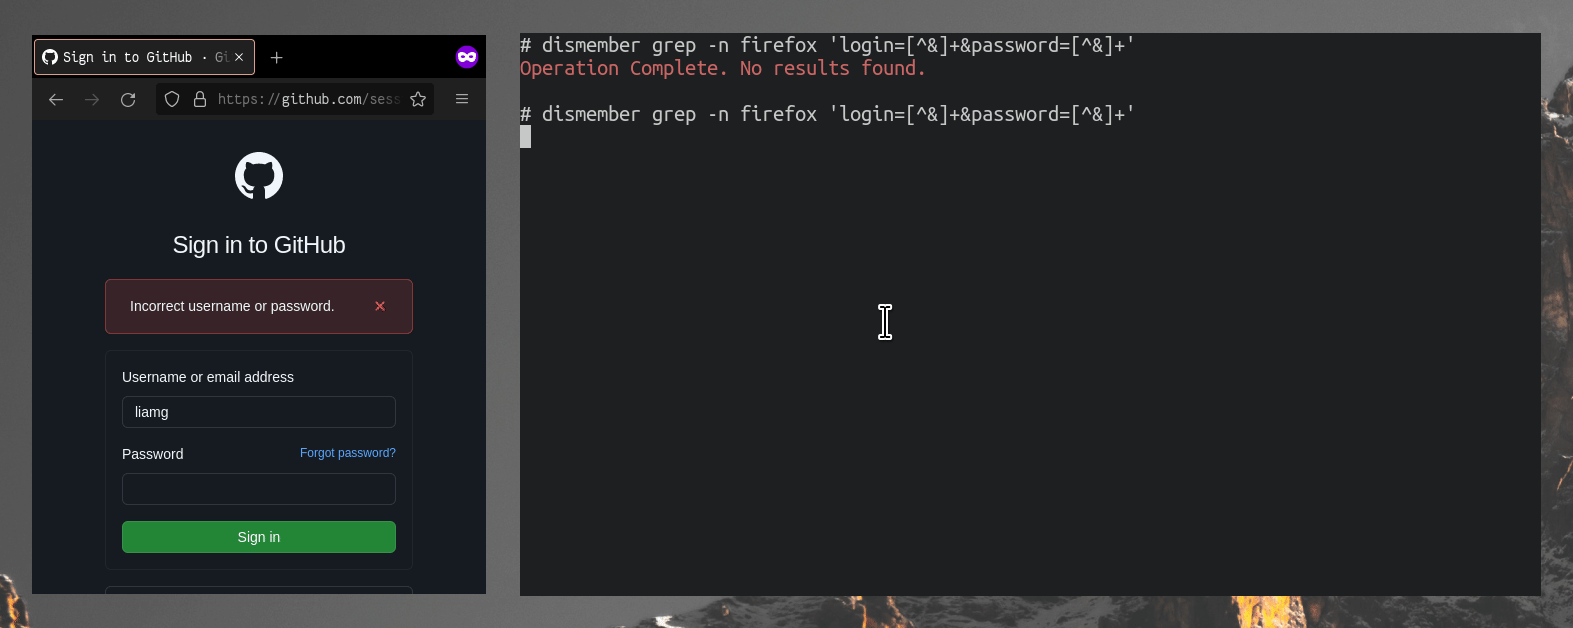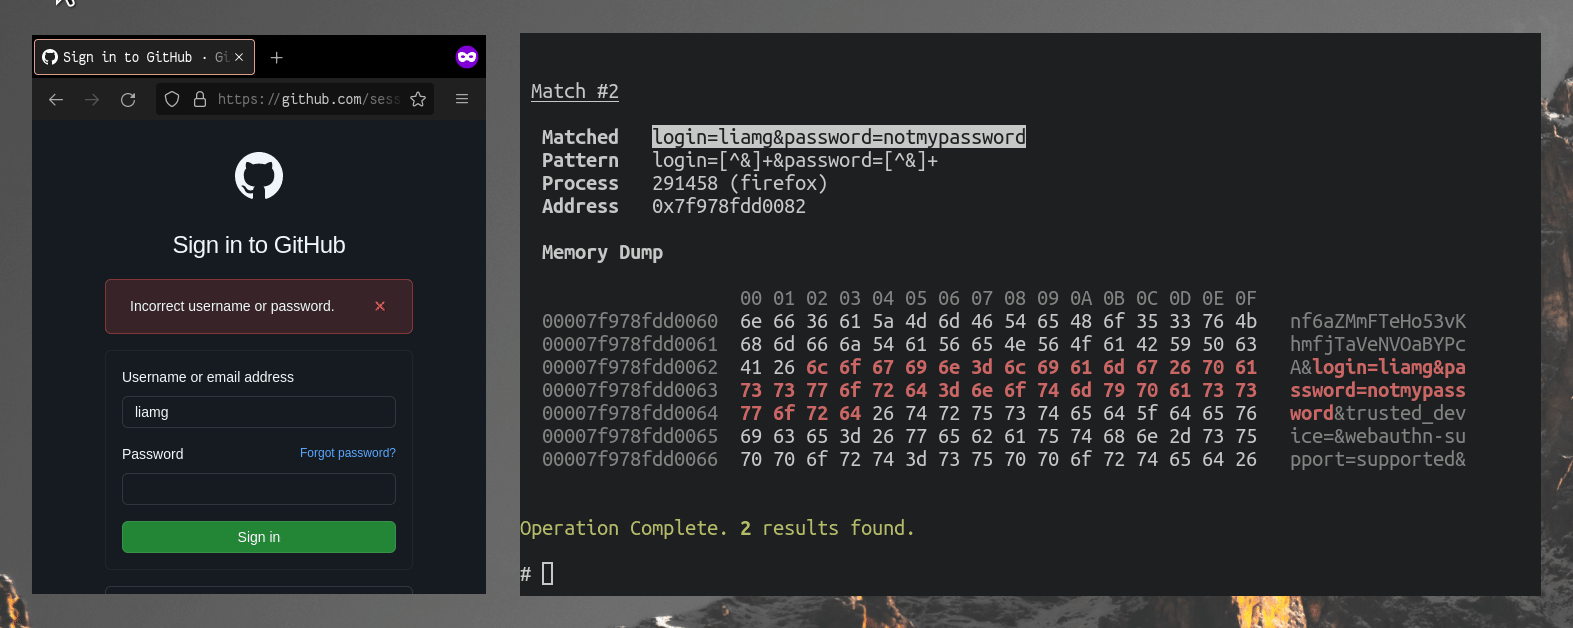 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints