

DMA-ProcessDumper
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
data-exfiltrationforensicshardware-hacking+3
gmh5225/dma-processdumperSimple Process Dumper using DMA over a PCIe FPGA device
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 lsw29475/cve-2020-17057
Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
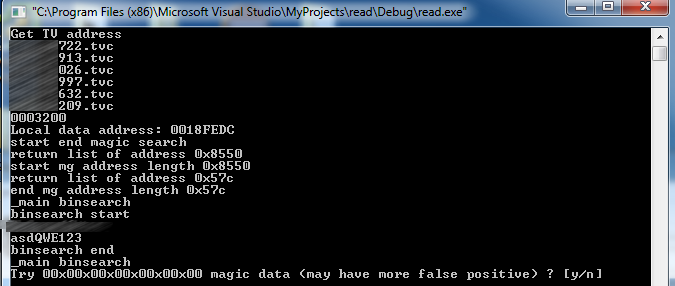 vah13/extracttvpasswords
tool to extract passwords from TeamViewer memory using Frida
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 eugnis/spectre-attack
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 m4g1xx/cve-2024-36971
Poc for CVE-2024-36971
 jajangjaman/cve-2021-41160
FreeRDP is a free implementation of the Remote Desktop Protocol (RDP), released under the Apache license. In affected versions a malicious server…
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 crowthearchfiend/rtcore64-probe
A tiny cpp program to test reading memory using a vulnerable RTCore64.sys driver/device (CVE-2019-16098). It tries to read a "secret" from its own…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 bytehackr/cve-2022-0853
Demonstrates a memory leak in JBoss client when using UserTransaction repeatedly, with a PoC and analysis for CVE-2022-0853.