

WHFB-PinCapture
 ivancabrera02/whfb-pincapture
Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
debuggersinformation-gatheringmemory-forensics+5
6
ivancabrera02/whfb-pincaptureCaptures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
 abraxas/php-oom-longjmp
PHP 8.4.26 - Critical - Remote - OOM longjmp - CVE-2026-109618 PHP2Shell. Unauth chunked multipart hits memory_limit before app code on Apache…
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
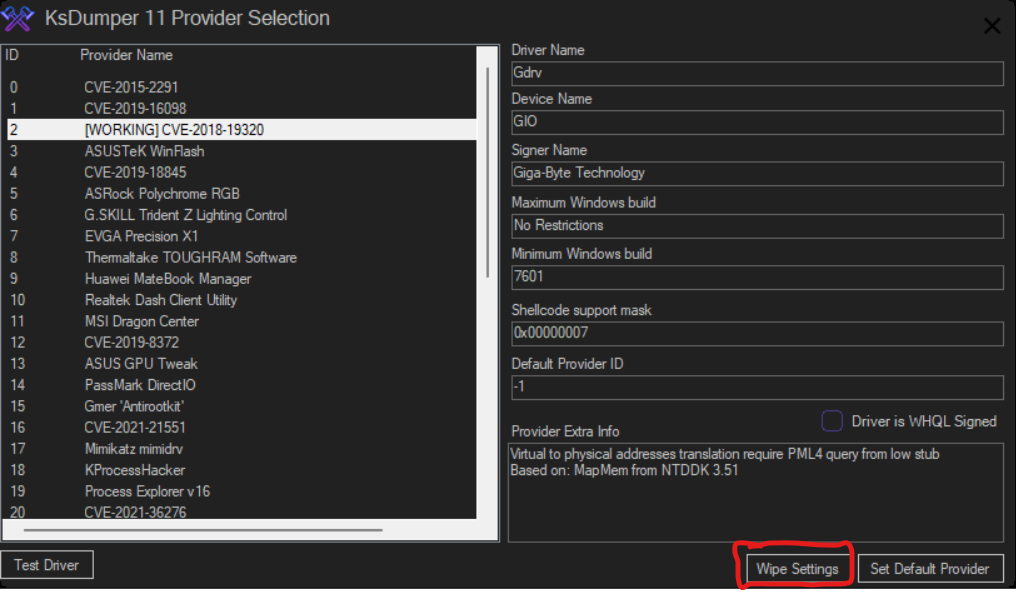 mastercodeon314/ksdumper-11
A revival of the classic and legendary KsDumper
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
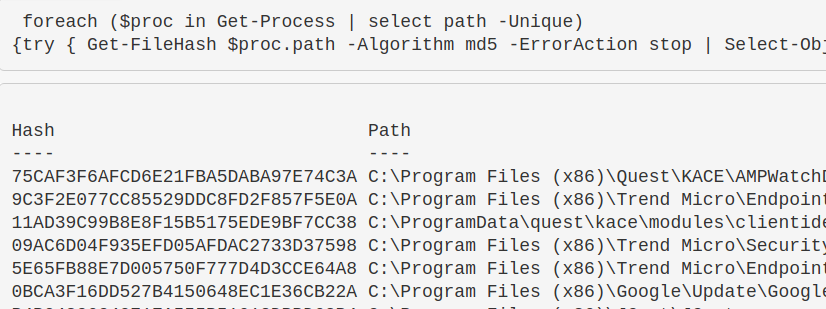 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 jailbreaks/empty_list
empty_list - exploit for p0 issue 1564 (CVE-2018-4243) iOS 11.0 - 11.3.1 kernel r/w
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 sharif-bot-cmd/quantum-silicon-core-loader
Executes at the silicon boundary
 tamirzb/cve-2017-13253
PoC code for CVE-2017-13253
 chunzhennn/cve-2023-21987-poc
Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
 asdyxcyxc/cve-2020-1362
writeup of CVE-2020-1362
 spydomain/cve-2021-22555-poc
Heap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 artemcyberlab/project-field-analysis-and-memory-leak-demonstration
The objective of this project was to assess a remote host for the Heartbleed vulnerability (CVE-2014-0160), verify its presence, and exploit it to…
 idov31/novahypervisor
Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…