
lpe-study-notes
 jadedfella/lpe-study-notes
A slow, from-zero walk through a Linux kernel privilege-escalation bug (CVE-2026-98260)
android-securitybinary-exploitationcurated-resources+6
1
jadedfella/lpe-study-notesA slow, from-zero walk through a Linux kernel privilege-escalation bug (CVE-2026-98260)
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 0x36/pixel_gpu_exploit
Android 14 kernel exploit for Pixel7/8 Pro
 tamirzb/cve-2017-13253
PoC code for CVE-2017-13253
 feliam/cve-2014-4481
Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…
 somisomair/cve-2026-43655-applem2scalercscdriver-uaf
Public disclosure for CVE-2026-43655 AppleM2ScalerCSCDriver use-after-free
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
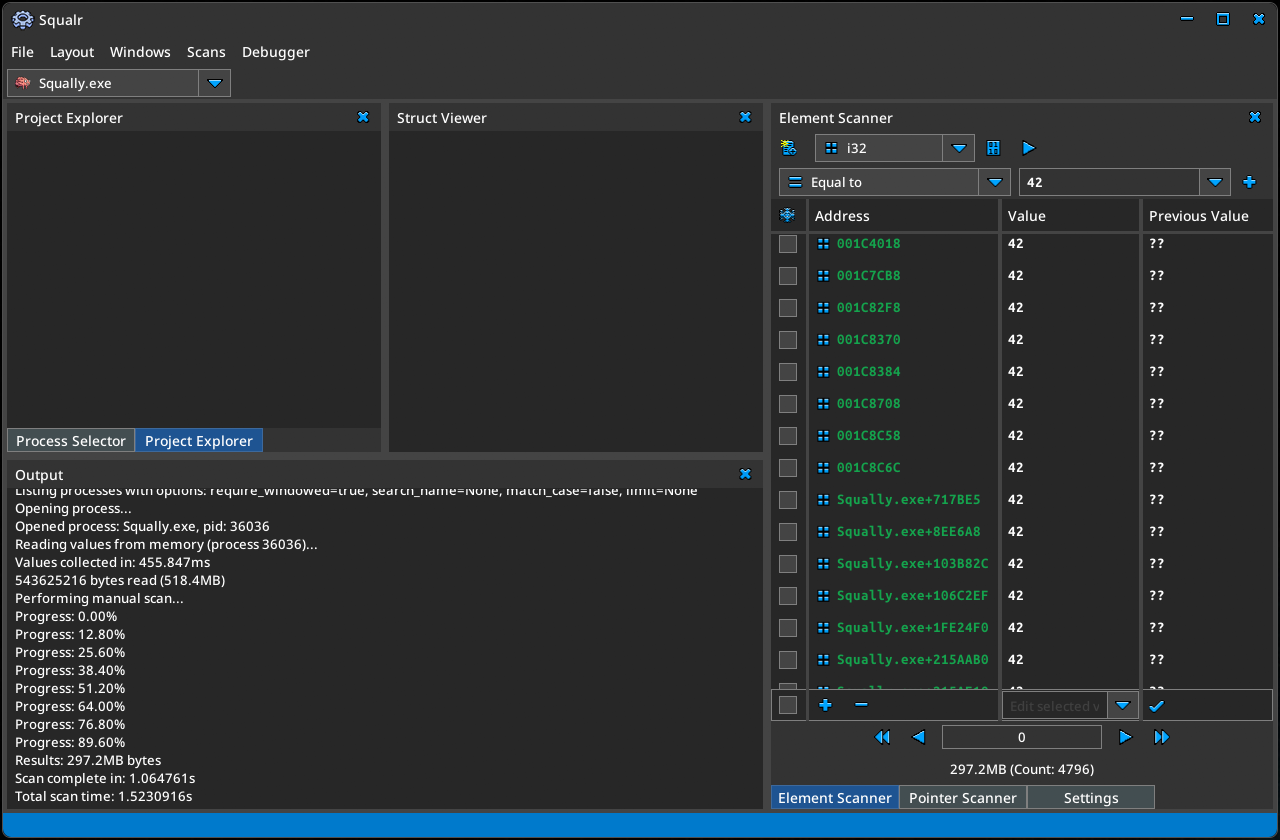 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…