
CVE-2026-65343-e7eb2ed
 hidayat-tanjung/cve-2026-65343-e7eb2ed
PoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…
binary-exploitationexploitationios-security+6
hidayat-tanjung/cve-2026-65343-e7eb2edPoC for CVE-2026-65343, an AppleKeyStore kernel OOB read on iOS 26.6 that leaks kernel pointers to defeat KASLR from a sandboxed app via…
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 bobikl/cve-2026-43499-t807d
Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…
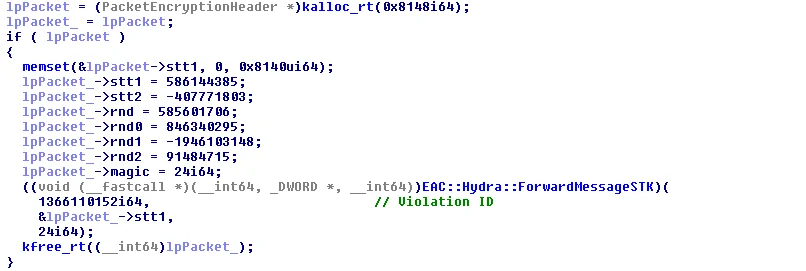 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 harshrajsinghania/cve-2026-90781-alsa-lib-oob
Standalone reproducer for CVE-2026-90781: 1-byte OOB write in alsa-lib __snd_ctl_ascii_elem_id_parse() name= parsing (quoted and unquoted)
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 harshrajsinghania/cve-2026-86547-mrubyc-op-enter
Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
 abraxas/cve-2025-38502-linux-lpe
Research repository for CVE-2025-38502, a Linux kernel BPF cgroup local storage out-of-bounds access via tail calls enabling local privilege…
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 abhinavagarwal07/gdcm-security-poc
Private end-to-end sanitizer reproduction package for six GDCM findings