
salt
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
binary-analysisdebuggerseducation+2
paolomonti42/saltSALT - SLUB ALlocator Tracer for the Linux kernel

 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 alessandroz/lazagne
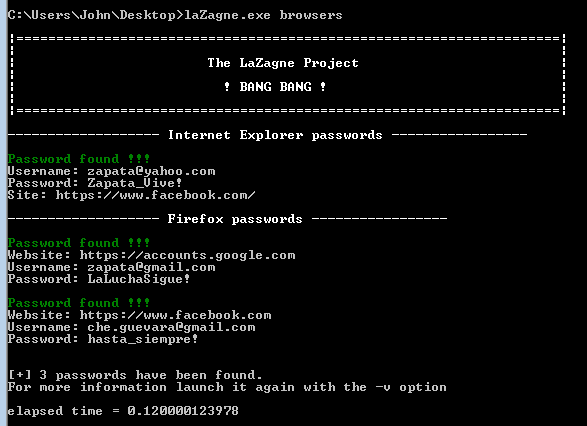
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 zodiacon/alltools
All reasonably stable tools
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
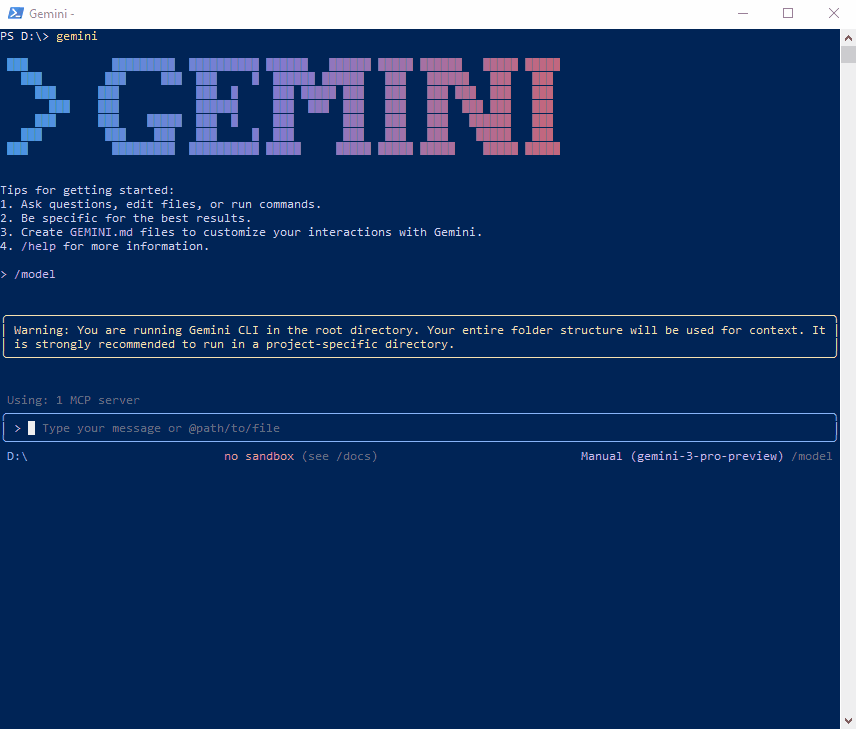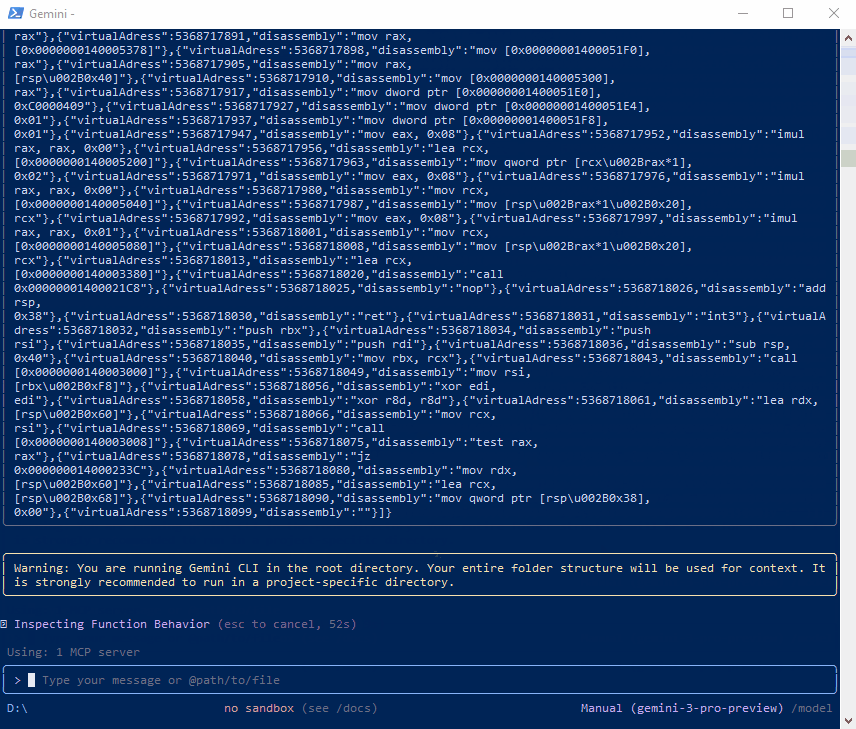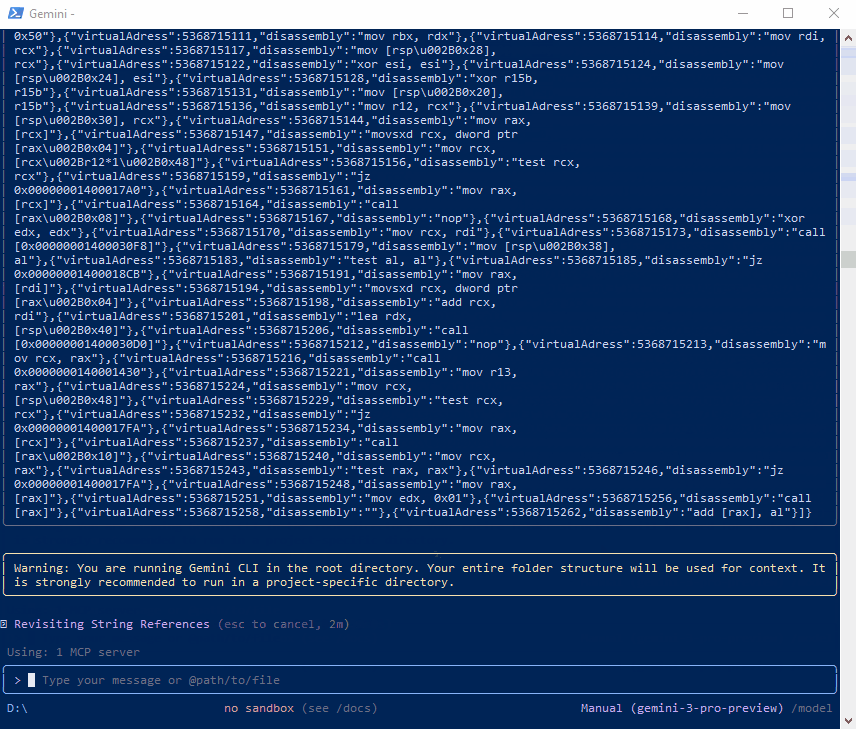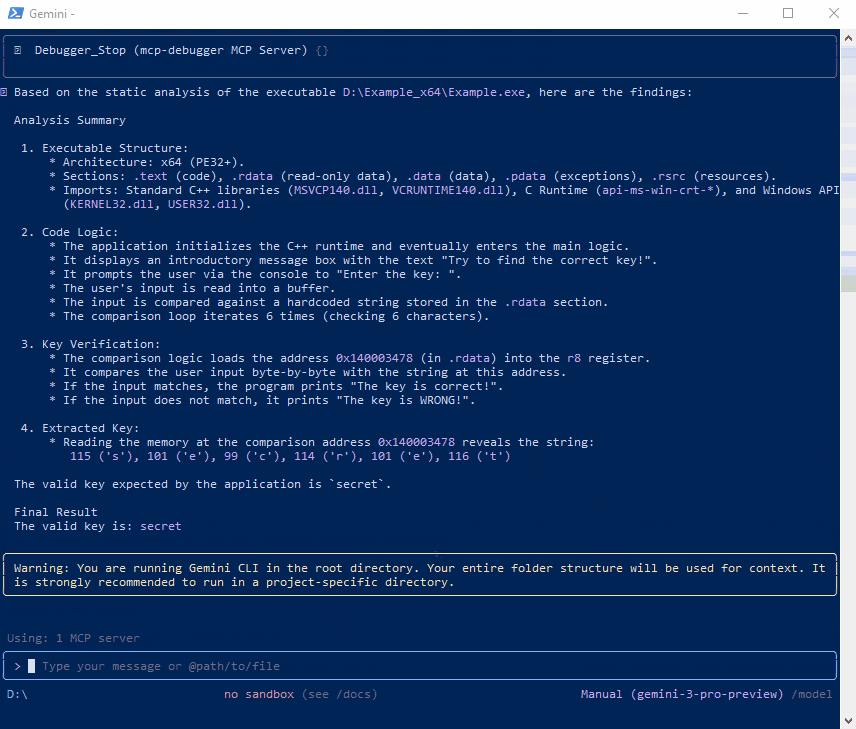 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 pinksawtooth/how_to_become_a_malware_analyst
Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…
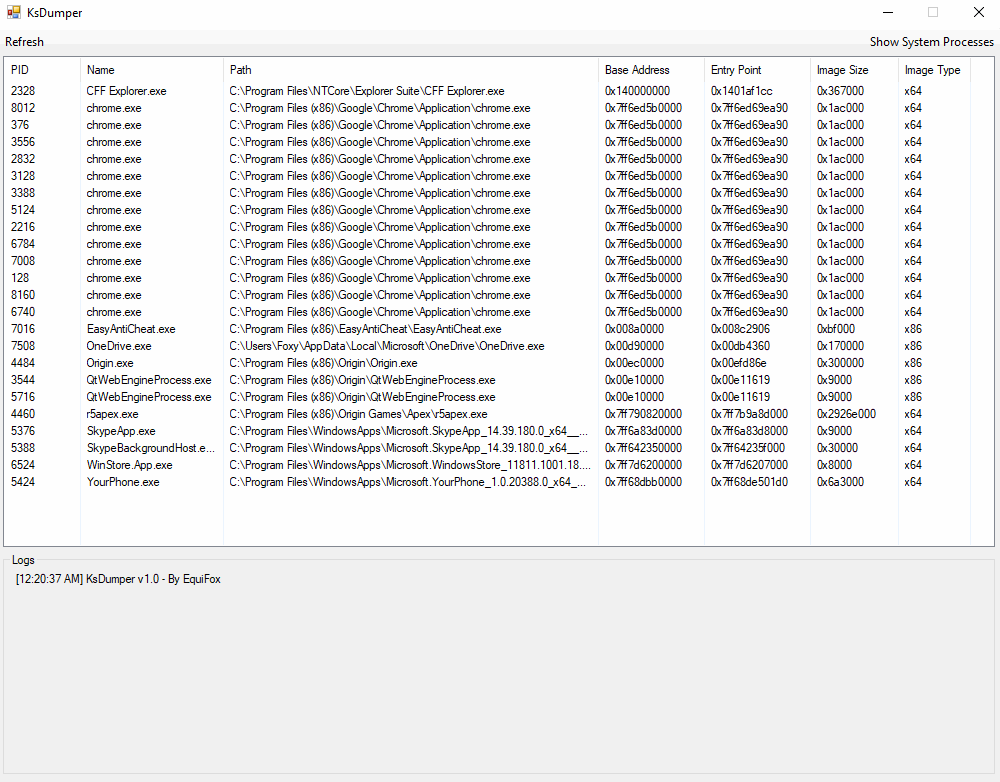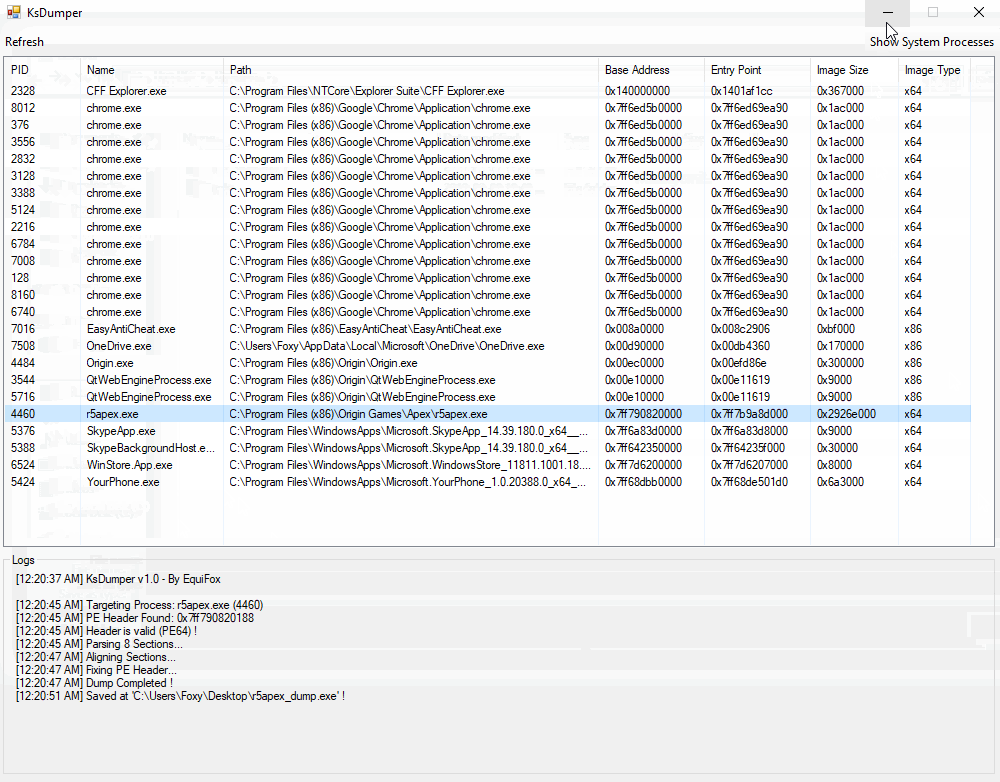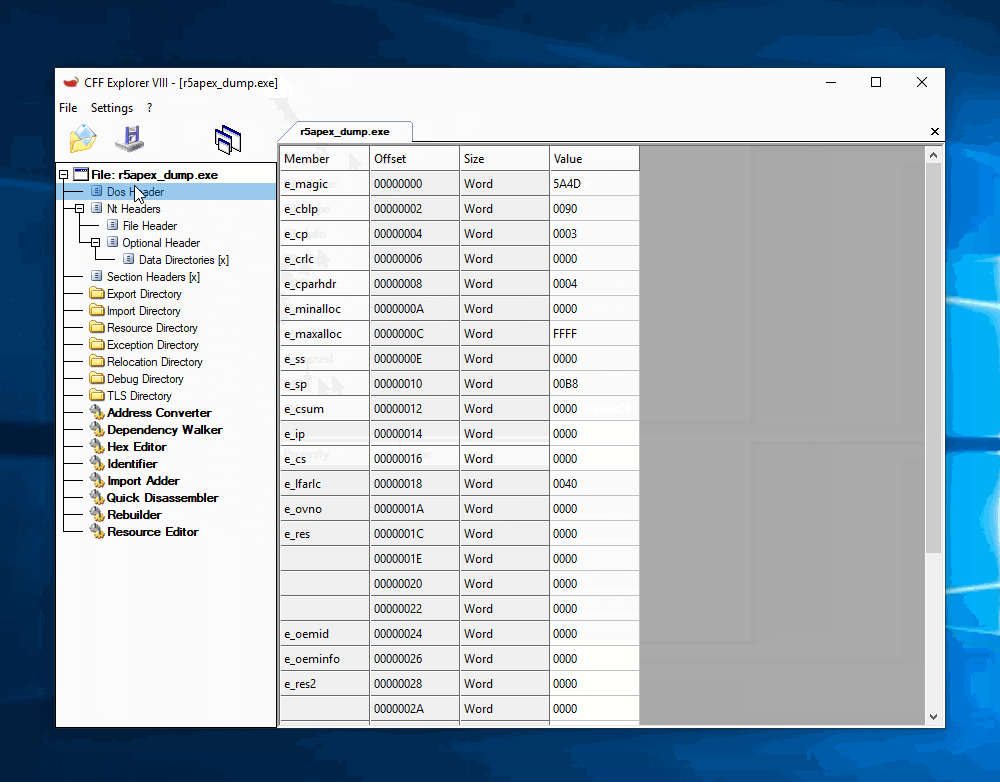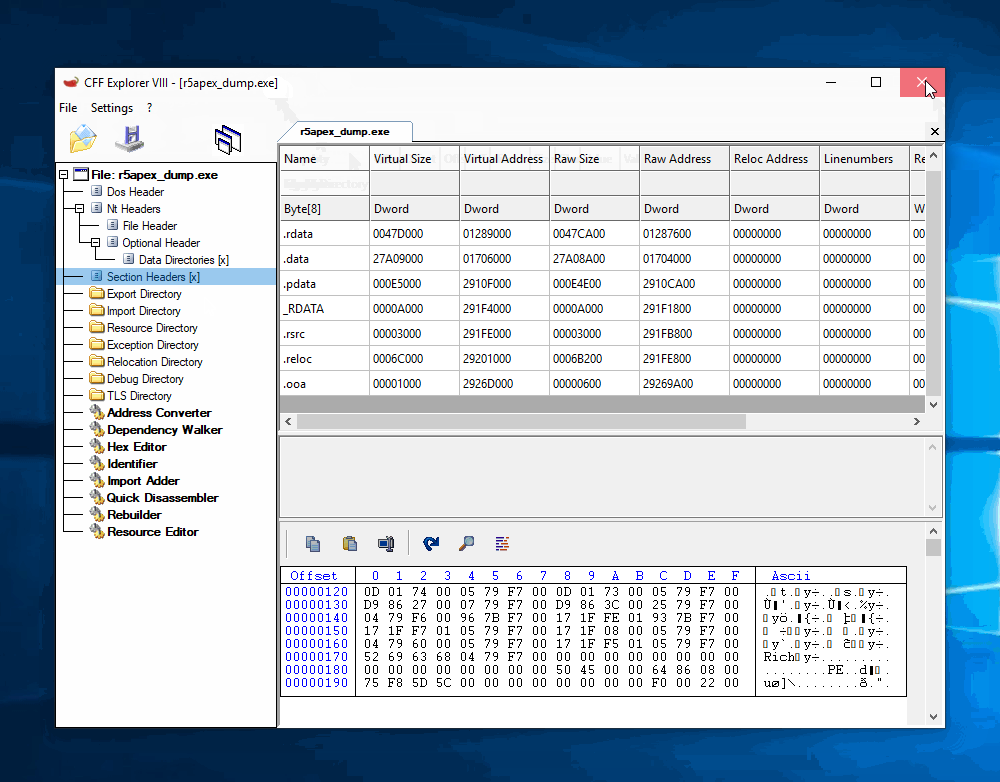 equifox/ksdumper
Dumping processes using the power of kernel space !
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 rshipp/awesome-malware-analysis
Defund the Police.
 velocidex/winpmem
The multi-platform memory acquisition tool.
 0linear/cve-2026-62958
Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.