
ATMMalScan
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
digital-forensicsdisk-forensicsincident-response+2
57
fboldewin/atmmalscanCommand-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
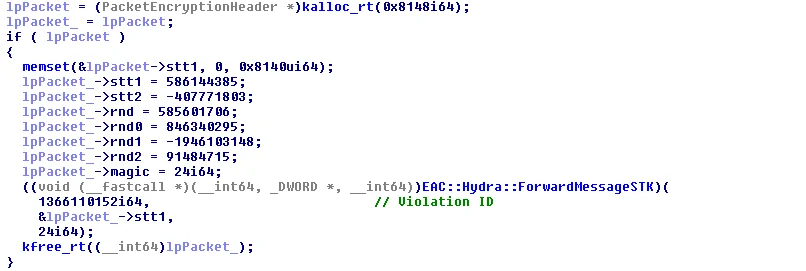 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…