

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 0neday/multi_path
CVE-2018-4241: XNU kernel heap overflow due to bad bounds checking in MPTCP for iOS 11 - 11.3.1released by Ian Beer
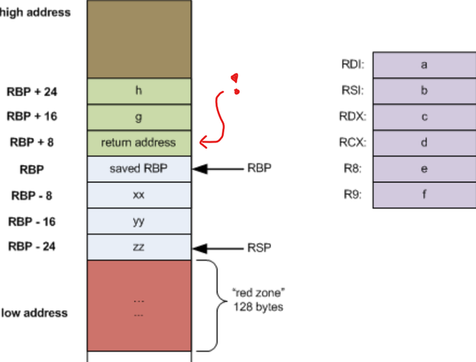 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 kyleavery/aceldr
Cobalt Strike UDRL for memory scanner evasion.
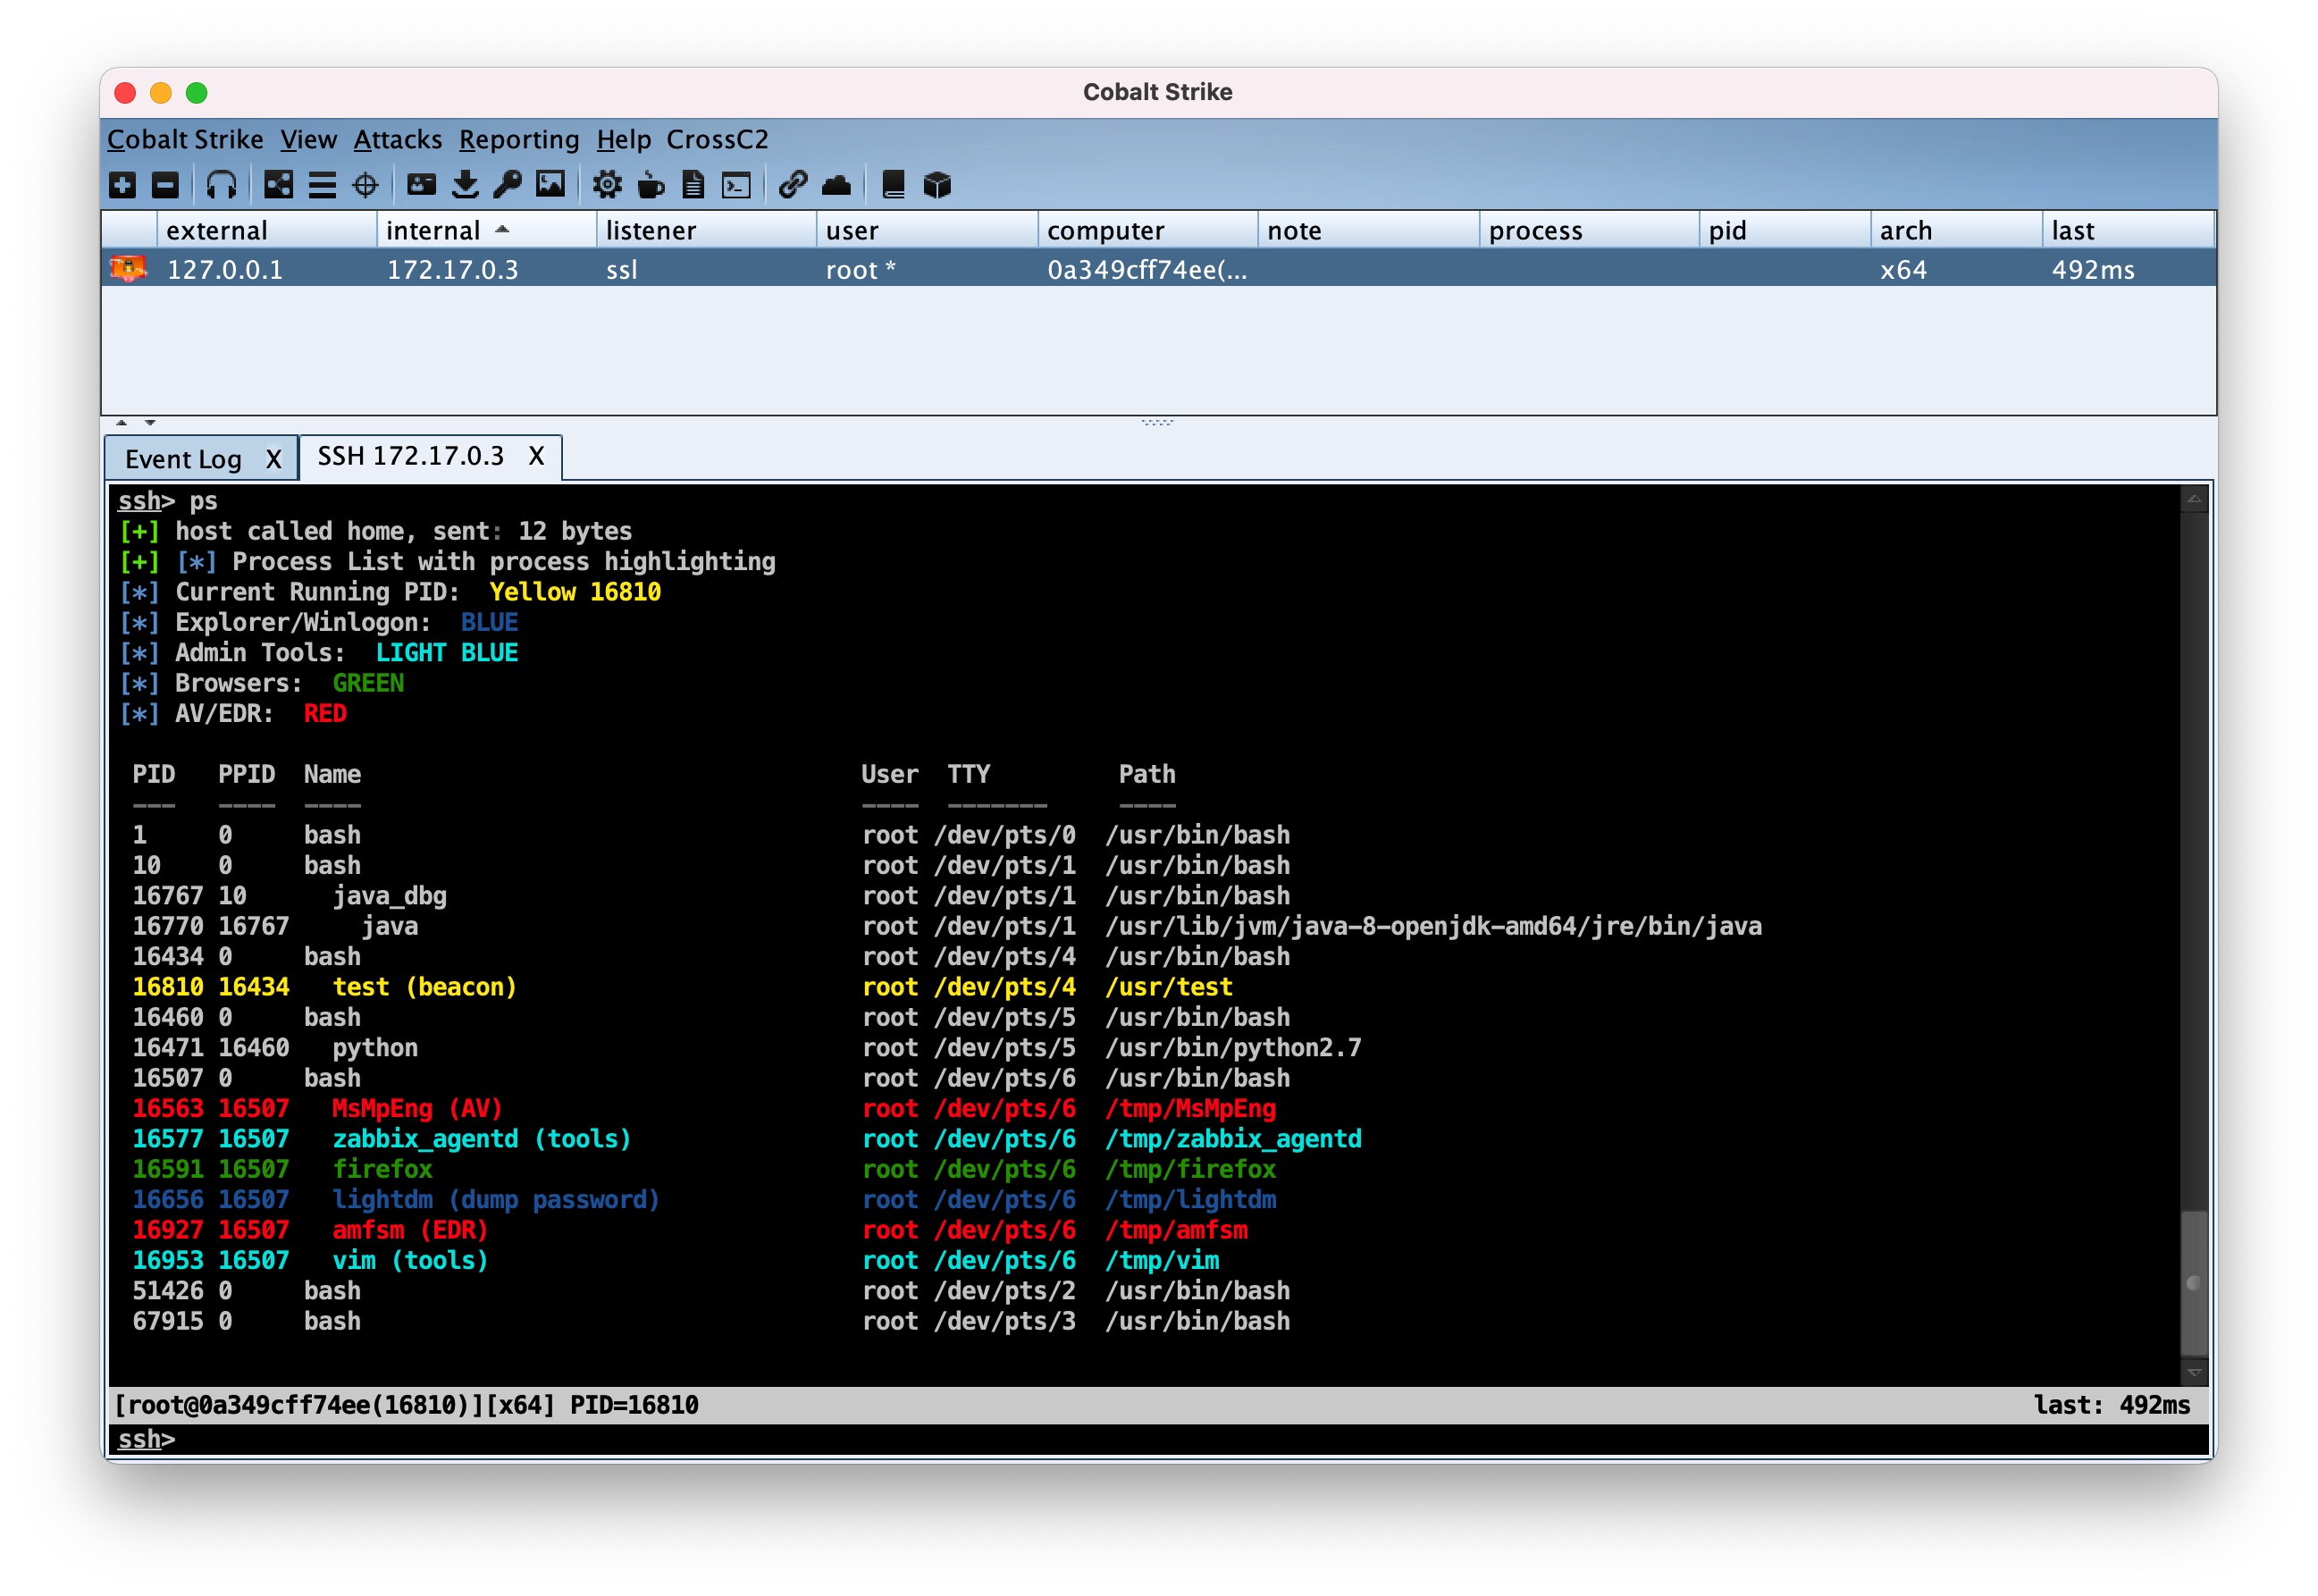 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 kudaes/shelter
ROP-based sleep obfuscation to evade memory scanners
 feliam/cve-2014-4481
Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 hexrom/imagemagick-cve-2017-15277
Proof-of-concept exploit for ImageMagick CVE-2017-15277 memory leak vulnerability, designed for use with the gifoeb fuzzing framework.