

php2shell-poc
 ikow/php2shell-poc
CVE-2026-109618/109619 PHP session.upload_progress Exploit Research — POC & Analysis
exploitationlabs-practicememory-forensics+5
1342 days ago
ikow/php2shell-pocCVE-2026-109618/109619 PHP session.upload_progress Exploit Research — POC & Analysis
 9bie/php2shell-bypass-aslr-exp
Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618 / CVE-2026-109619 audit: session poisoning to command execution reproduced; BGCTX OOM precondition reproduced; claimed progress-array…
 vardhan0257/upb-any-recursion-audit
Audit harness testing whether the CVE-2026-0994 Any-unwrapping recursion bug class affects upb's C core in Ruby and PHP protobuf bindings, with…
 eness/php2shell-cve-2026-109618-cve-2026-109619-poc
Proof-of-Concept (PoC) exploit for php2shell (CVE-2026-109618 / CVE-2026-109619), demonstrating remote code execution in vulnerable PHP environments.…
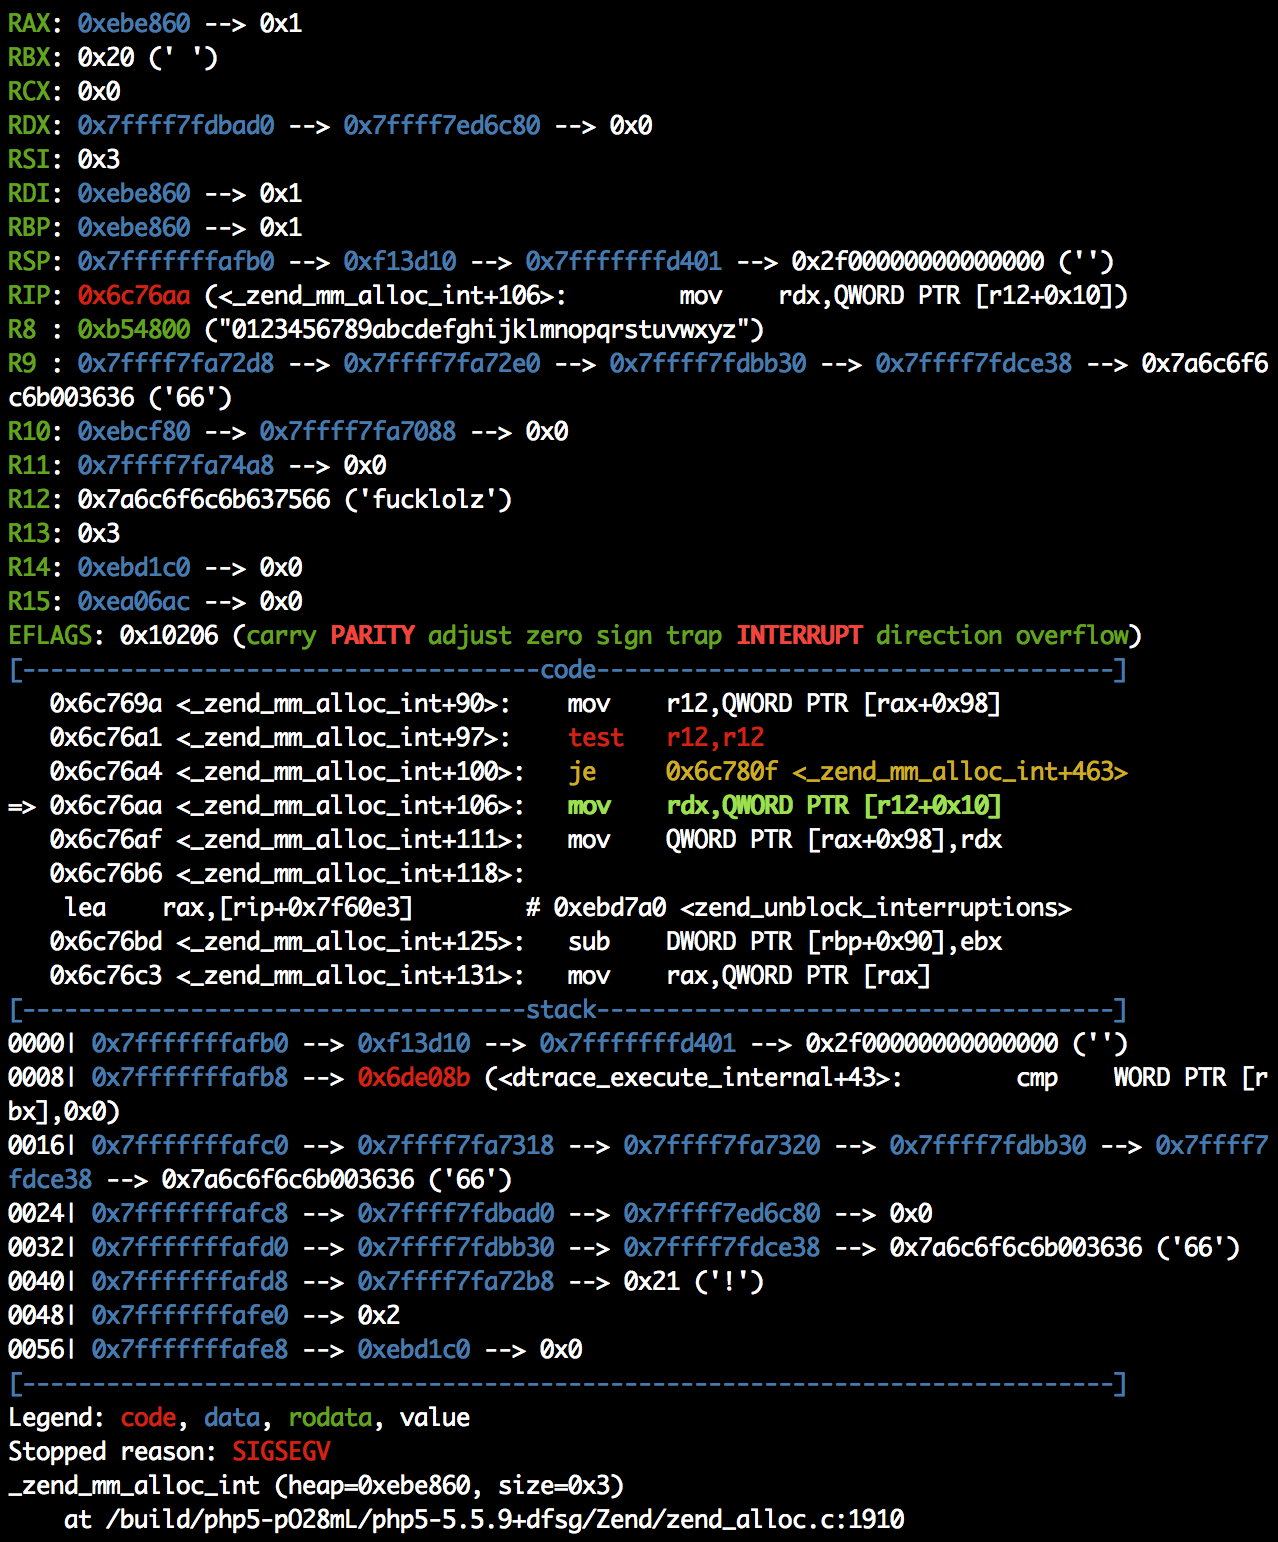
 cookiengineer/actual-php2shell
🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)