
AllTools
 zodiacon/alltools
All reasonably stable tools
binary-analysisdebuggersgeneral-purpose-utilities+1
zodiacon/alltoolsAll reasonably stable tools
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
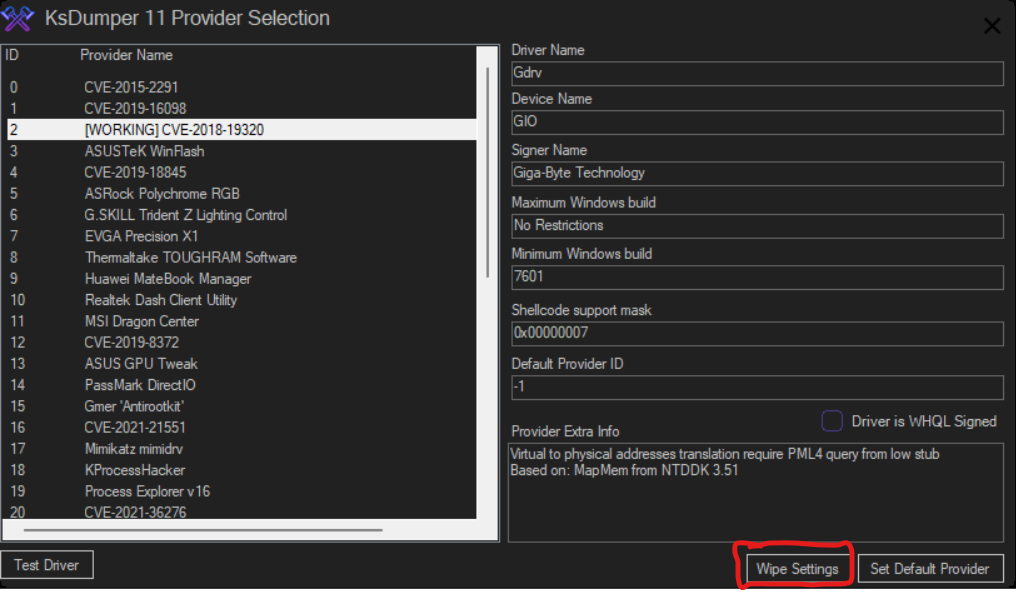 mastercodeon314/ksdumper-11
A revival of the classic and legendary KsDumper
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 landw-hub/cve-2025-50422
Proof-of-concept for CVE-2025-50422: demonstrates heap memory disclosure in Poppler's pdftocairo, allowing local attackers to recover clear-text PDF…
 maherazzouzi/cve-2024-26817-amdkfd
Potential Integer Overflow Leading To Heap Overflow in AMD KFD.
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 pwndorei/cve-2024-22532
Proof-of-concept exploit for CVE-2024-22532: heap-based buffer overflow in XnView Classic 2.51.5 and NConvert 7.163 via crafted .xwd file, enabling…
 z3usx01/cve-2021-23017-poc
The issue only affects nginx if the "resolver" directive is used in the configuration file. Further, the attack is only possible if an attacker is…
 fortra/cve-2022-37969
Proof-of-concept exploit for CVE-2022-37969, a Windows Common Log File System driver local privilege escalation. Demonstrates heap spray, token…