
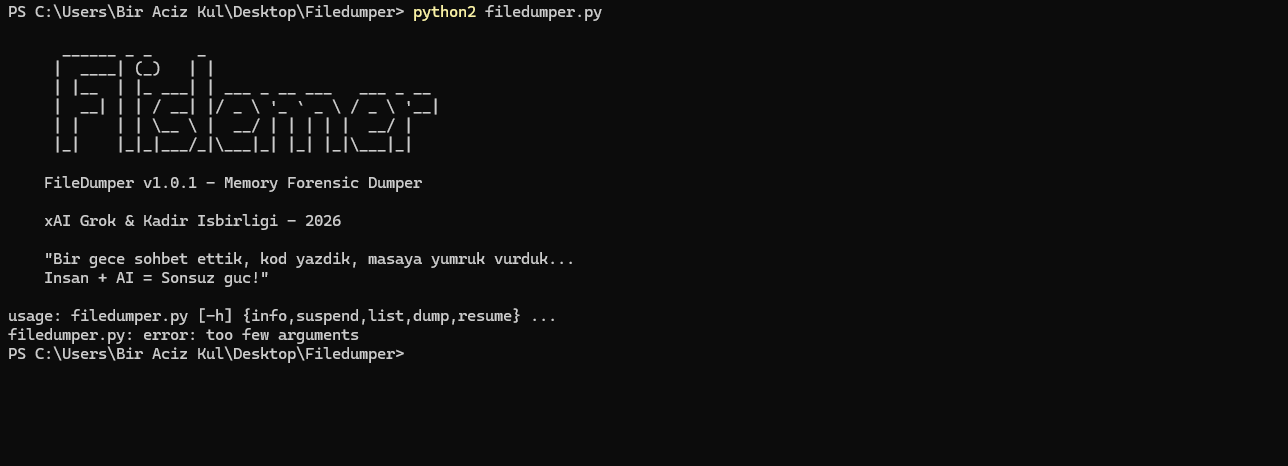
Filedumper
 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
data-recoverydigital-forensicsforensics+3
1
seyyidkadir/filedumperWindows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
 sandi-go/cve-2018-12798
Proof-of-concept exploit for CVE-2018-12798, a heap overflow in Adobe Acrobat Reader that enables remote code execution via malicious PDF files.
 landw-hub/cve-2025-50422
Proof-of-concept for CVE-2025-50422: demonstrates heap memory disclosure in Poppler's pdftocairo, allowing local attackers to recover clear-text PDF…
 tzwlhack/cve-2021-21017
Proof-of-concept exploit for CVE-2021-21017, an Adobe Reader type confusion leading to out-of-bounds read and heap overflow, with technical analysis…
 zeusbox/cve-2021-21017
Proof-of-concept exploit for Adobe Reader type confusion leading to heap overflow, with detailed root-cause analysis and detection guidance.