
LiME
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
digital-forensicsforensicsincident-response+2
2.0k
jtsylve/limeKernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
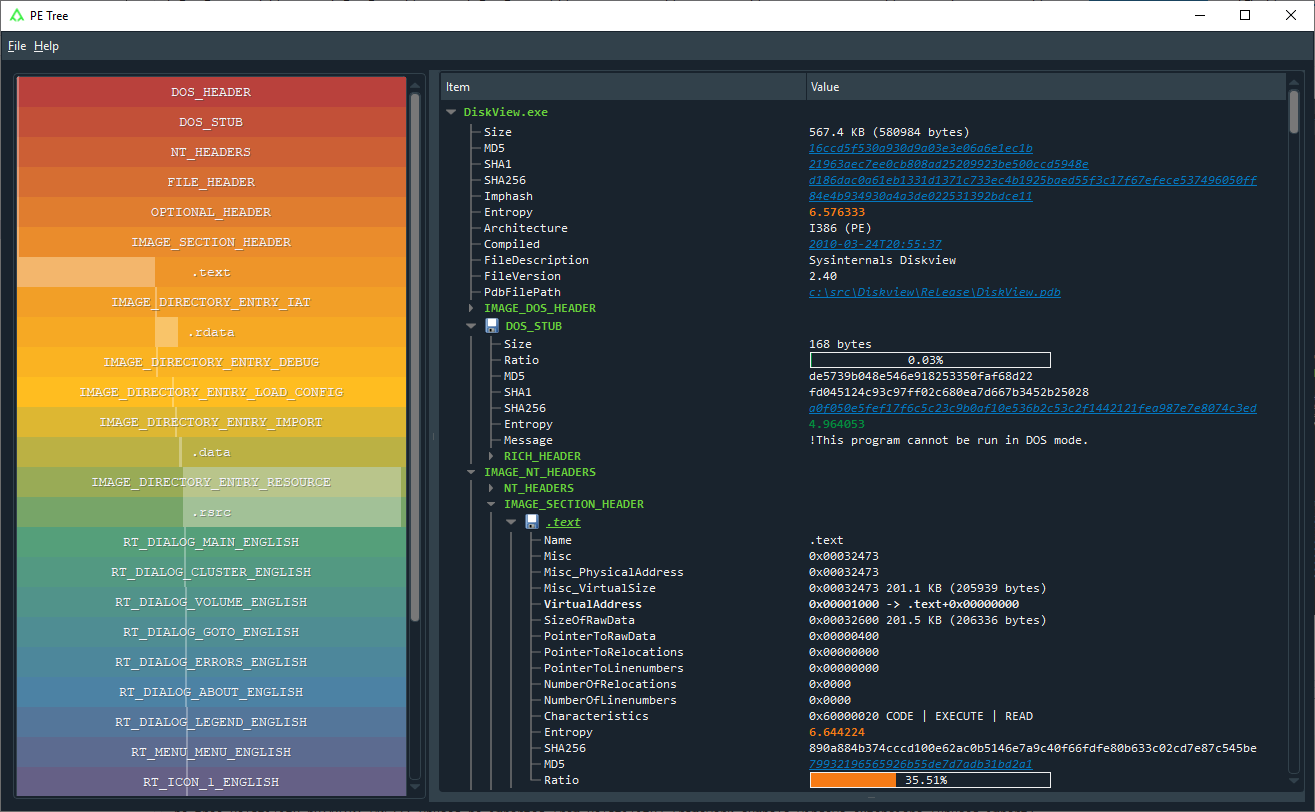 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 ymsniper/umbra
External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 3nou9h/cve-2026-9256-poc
Demonstrates CVE-2026-9256 heap buffer overflow in nginx's ngx_http_rewrite_module with PoC scripts for heap/libc leaks and worker crash.
 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 fysac/cve-2019-20326
Heap buffer overflow in GNOME gThumb and Linux Mint Pix
 spydomain/cve-2022-0435-poc
Stack overflow exploit for CVE-2022-0435 in the TIPC module, providing local privilege escalation to root on Ubuntu kernels.
 gmh5225/linux-kernel-debugger
Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.