

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.2k
19h 2m ago
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel

binary-analysisdebuggerseducation+2
1578 years ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.4k3 days ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
digital-forensicsforensicsioc-management+3
8492 years ago
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
1964 days ago
WinPmem preview

WinPmem

GitHubvelocidex/winpmem

The multi-platform memory acquisition tool.

digital-forensicsforensicsincident-response+1
1.1k11 months ago
fibratus preview

fibratus

GitHubrabbitstack/fibratus

Security sensor for realtime threat detection and protection
defensive-toolsforensicsincident-response+3
2.6k10 days ago
volatility preview
Archived

volatility

GitHubvolatilityfoundation/volatility

An advanced memory forensics framework
digital-forensicsforensicsincident-response+4
8.1k1 year ago
lmg preview

lmg

GitHubhalpomeranz/lmg

Script for automating Linux memory capture and analysis
digital-forensicsforensicsincident-response+1
2756 years ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.5k21 days ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
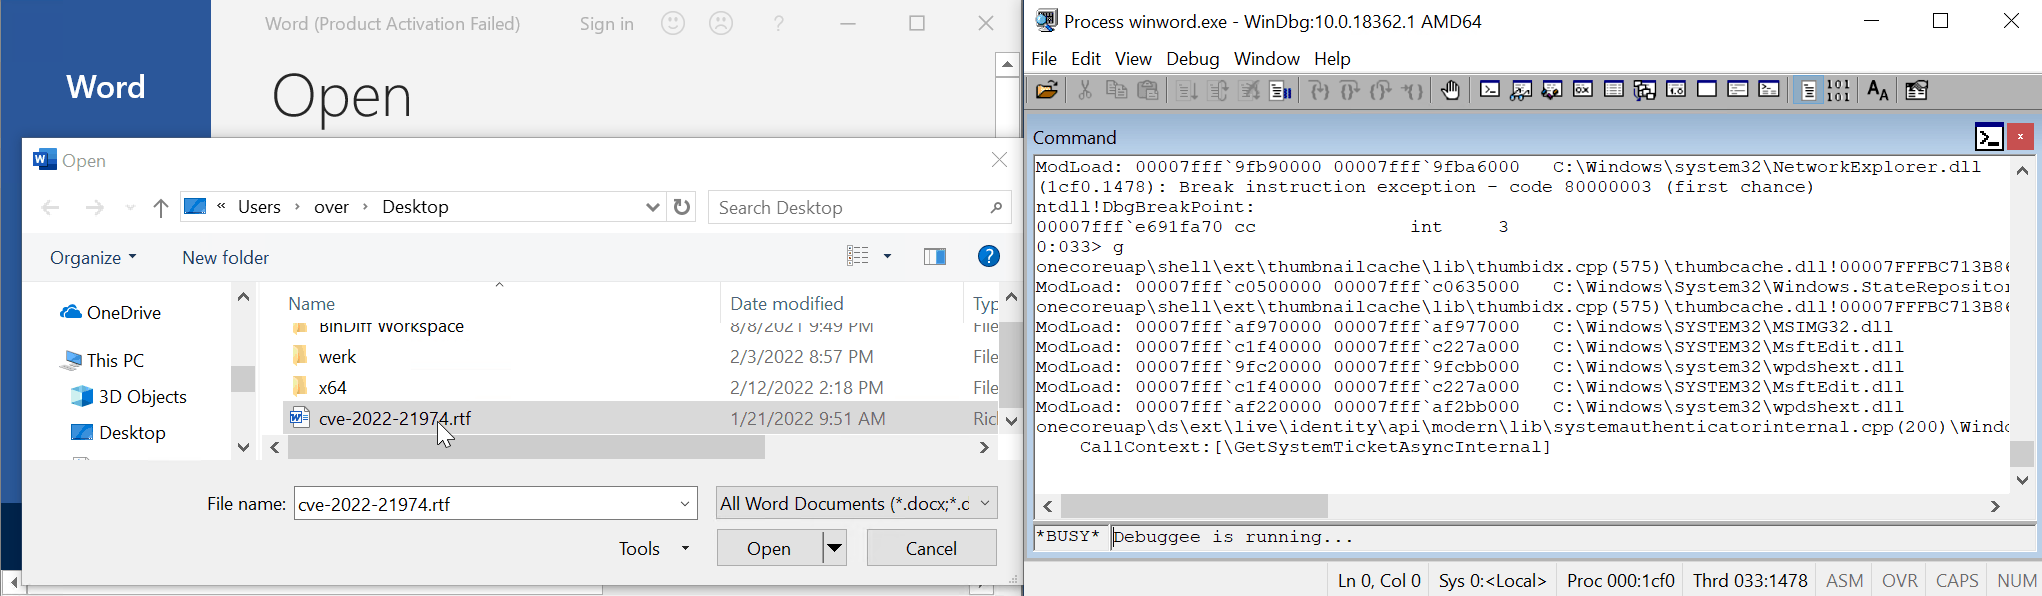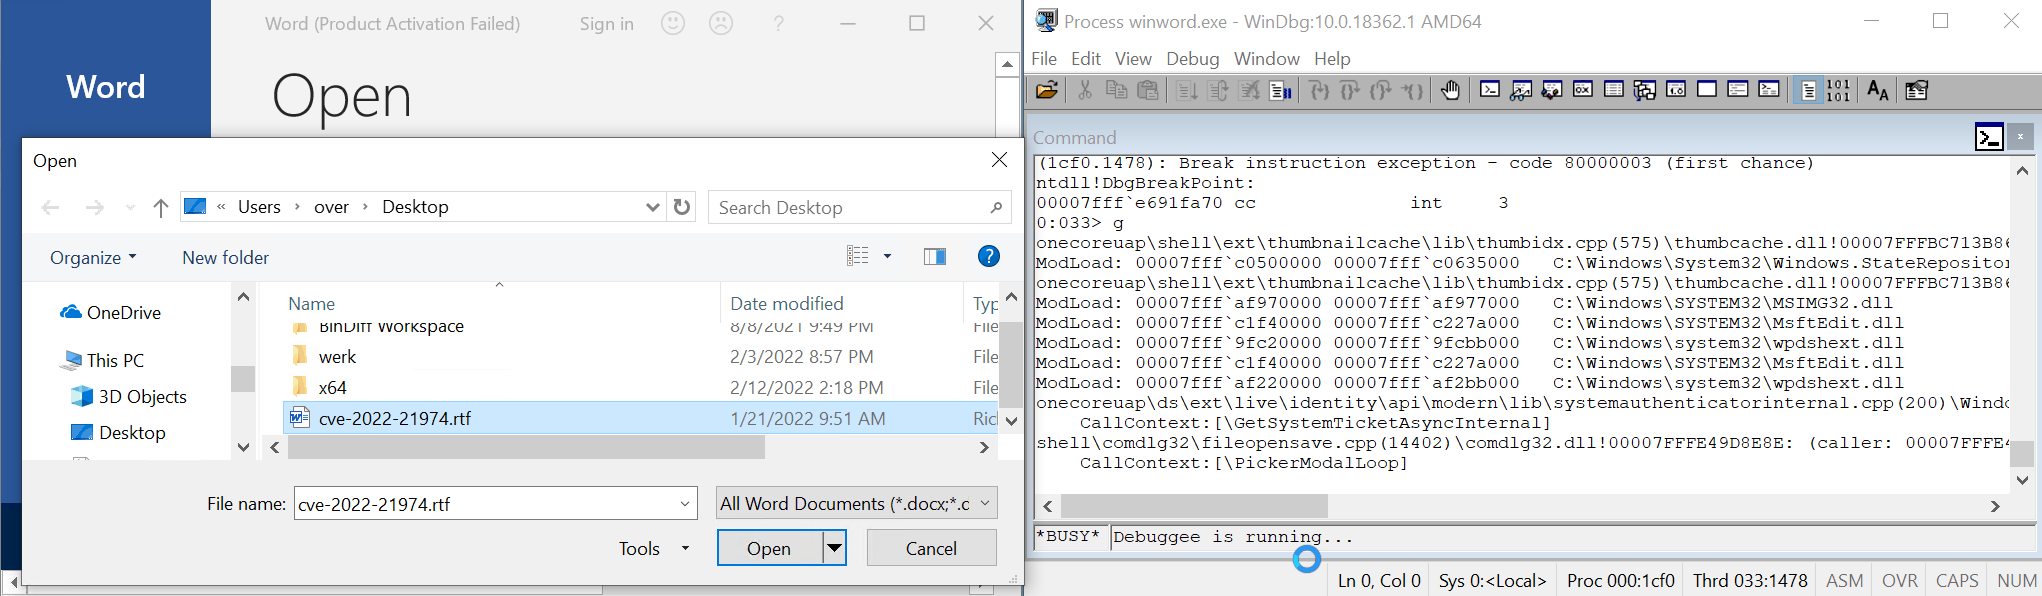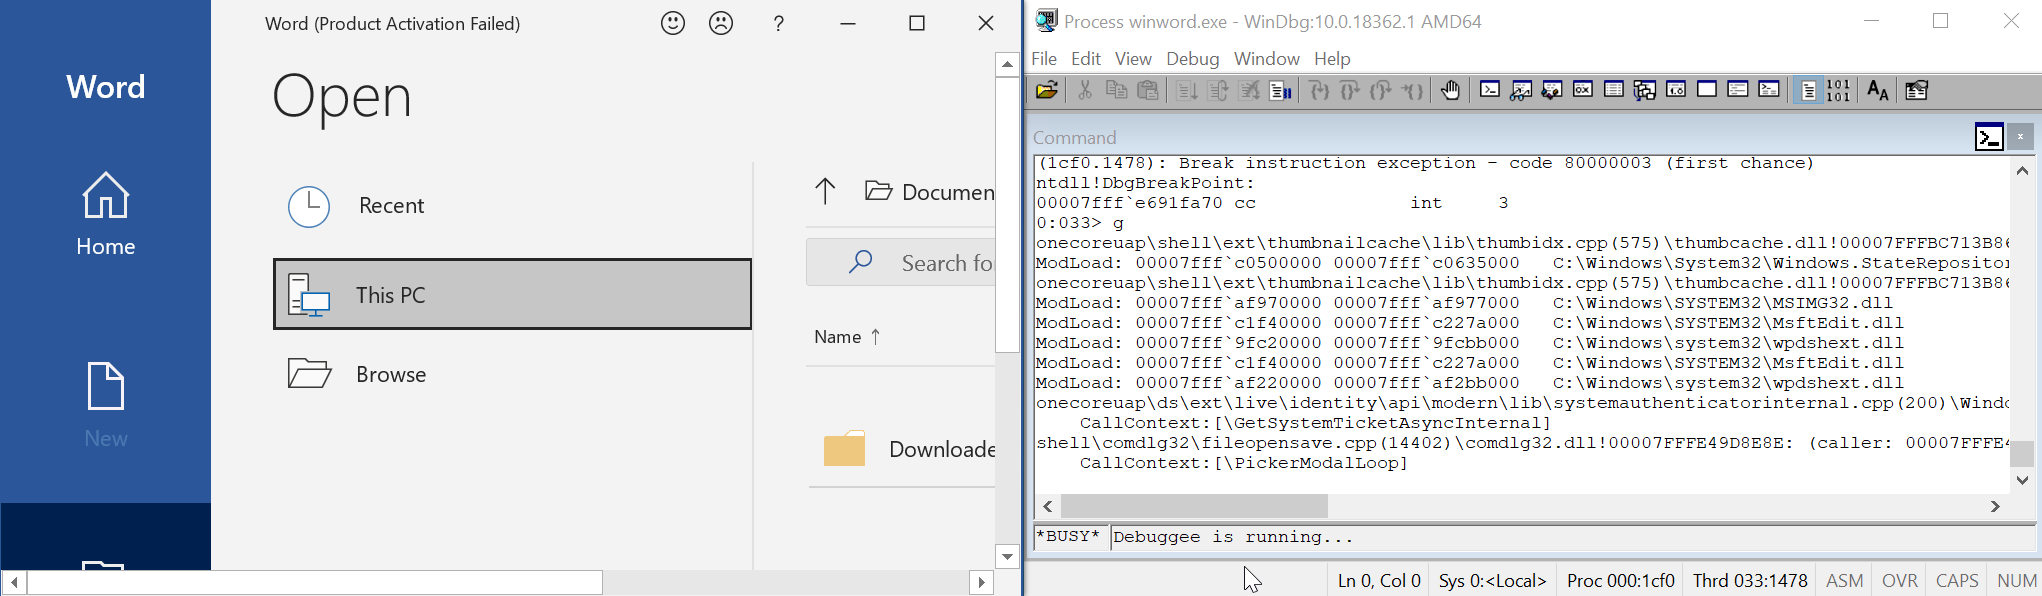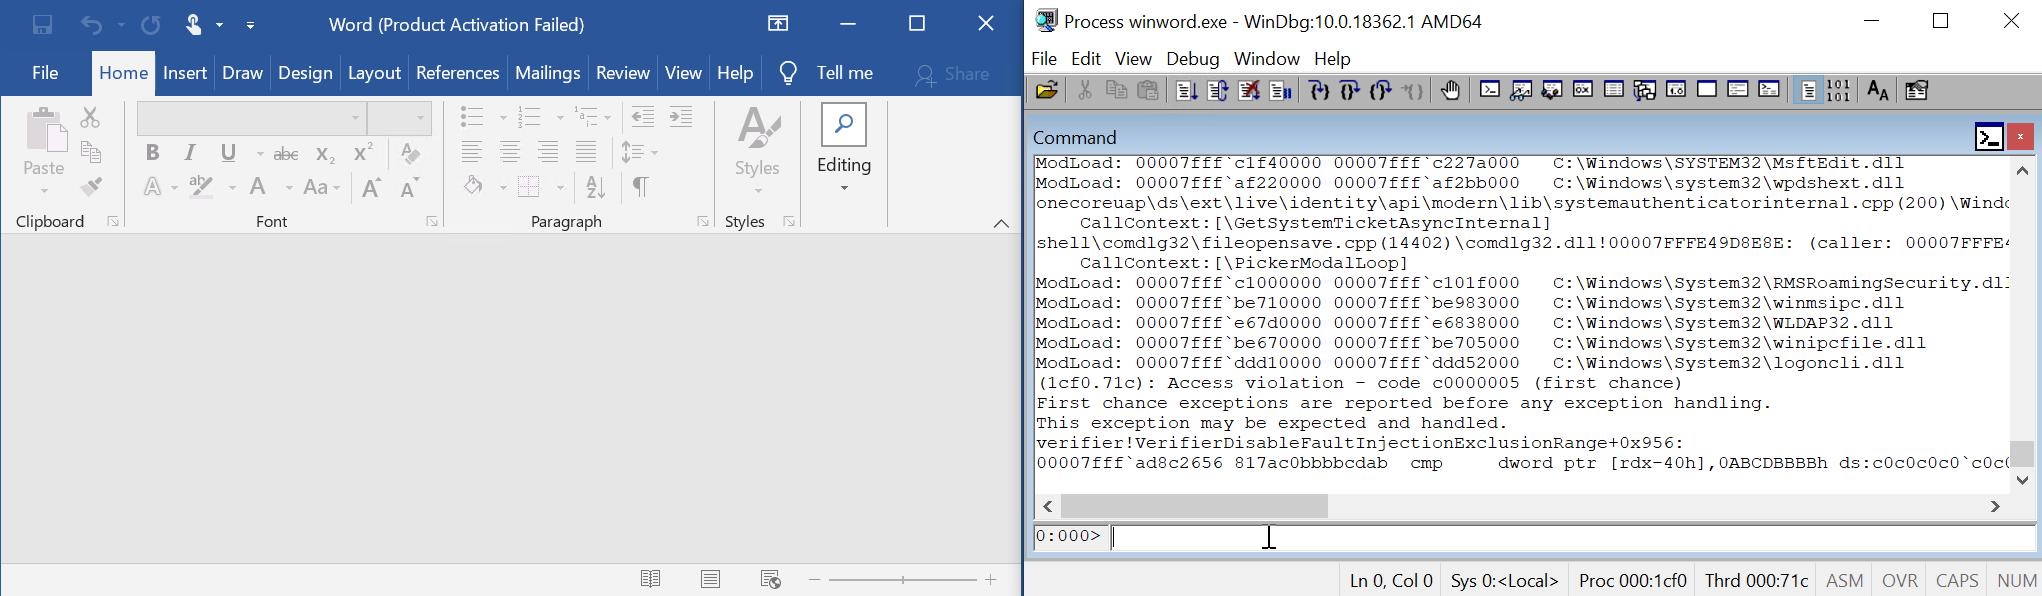
digital-forensicsforensicsincident-response+4
2188 years ago
CVE-2022-21974 preview
Archived

CVE-2022-21974

GitHub0vercl0k/cve-2022-21974

PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
binary-exploitationdebuggersexploitation+3
574 years ago
LiME preview

LiME

GitHubjtsylve/lime

Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
digital-forensicsforensicsincident-response+2
2.0k6 months ago
ios.CVE-2026-84616-84607 preview

ios.CVE-2026-84616-84607

GitHubping-2o/ios.cve-2026-84616-84607

research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607

binary-analysiseducationexploitation+6
1122 days ago
avml preview

avml

GitHubmicrosoft/avml

Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
digital-forensicsforensicsincident-response+1
1.1k1 day ago
aftermath preview

aftermath

GitHubjamf/aftermath

Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…

digital-forensicsforensicsincident-response+3
6001 year ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
digital-forensicsforensicsincident-response+3
1.5k29 days ago
rekall preview
Archived

rekall

GitHubgoogle/rekall

Rekall Memory Forensic Framework

digital-forensicsforensicsincident-response+3
2.0k5 years ago
Previous1234Next