Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
21 results
ghostlock-cve-2026-43499-4.19-k40 preview

ghostlock-cve-2026-43499-4.19-k40

GitHubccp-p/ghostlock-cve-2026-43499-4.19-k40

Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.

android-securitybinary-exploitationexploitation+6
9
1 month ago
DeepSleep preview

DeepSleep

GitHubtheflink/deepsleep

A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC

exploitationmemory-forensicspayload-development+1
3744 years ago
CAPEv2 preview

CAPEv2

GitHubkevoreilly/capev2

Malware Configuration And Payload Extraction

debuggersdynamic-analysis-sandboxingeducation+6
3.6k13h 24m ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

binary-analysiscommand-and-controldata-exfiltration+6
62 months ago
ReflectiveDLLInjection preview

ReflectiveDLLInjection

GitHubstephenfewer/reflectivedllinjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…

exploitationmemory-forensicspayload-development+2
3.4k13 years ago
samsung_tizen_tv_root preview

samsung_tizen_tv_root

GitHubcommit-regrets/samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

binary-exploitationembedded-systems-securityexploitation+8
151 day ago
JYso preview

JYso

GitHubqi4l/jyso

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…

command-and-controlctfexploit-frameworks+5
1.8k4 months ago
nanodump preview

nanodump

GitHubfortra/nanodump

The swiss army knife of LSASS dumping

exploitationmemory-forensicspayload-development+4
2.1k2 years ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…

command-and-controldata-exfiltrationmalware-analysis+4
12 months ago
CVE-2026-43499-T807D preview

CVE-2026-43499-T807D

GitHubbobikl/cve-2026-43499-t807d

Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…

android-securitybinary-exploitationexploitation+7
2 months ago
-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis- preview

-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis-

GitHubkaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-

"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…

api-securitybinary-analysisdynamic-analysis-sandboxing+8
23 months ago
zombieant preview

zombieant

GitHubdsnezhkov/zombieant

Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.

memory-forensicspayload-developmentpost-exploitation+2
2267 years ago
Shelter preview

Shelter

GitHubkudaes/shelter

ROP-based sleep obfuscation to evade memory scanners

exploit-frameworksmemory-forensicsred-teaming
3901 year ago
KslKatzBof preview

KslKatzBof

GitHubprinciplecheck/kslkatzbof

Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…

exploitationmemory-forensicspayload-development+4
911 month ago
PageTableInjection preview

PageTableInjection

GitHubkkent030315/pagetableinjection

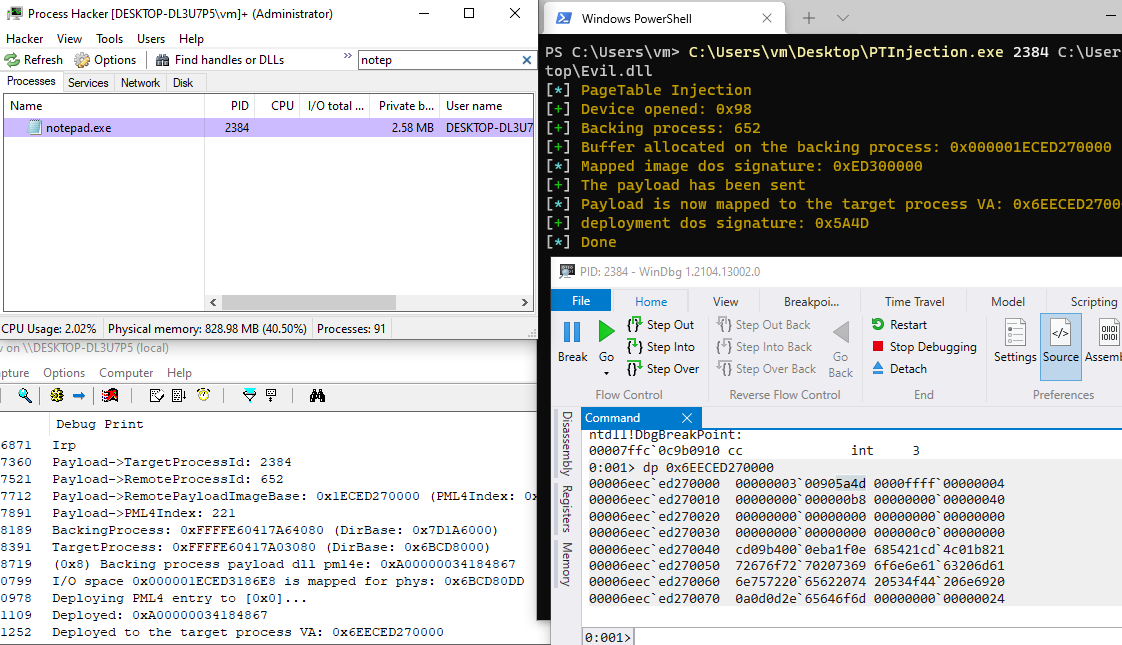
Code Injection, Inject malicious payload via pagetables pml4.

binary-exploitationexploitationmemory-forensics
2485 years ago
RustChain preview

RustChain

GitHubkudaes/rustchain

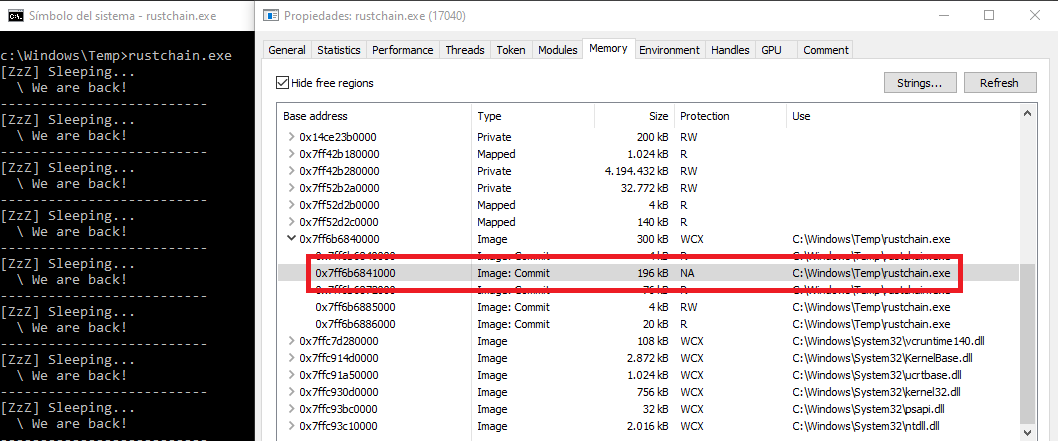
Hide memory artifacts using ROP and hardware breakpoints.

exploitationmemory-forensicspayload-development+1
1523 years ago
PixelSmash preview

PixelSmash

GitHubse1ims/pixelsmash

Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.

binary-exploitationeducationexploitation+6
1 month ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.

exploitationforensicsmalware-analysis+5
2292 years ago
Previous12Next