

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 angr/angr
A powerful and user-friendly binary analysis platform!
 volatilityfoundation/volatility
An advanced memory forensics framework
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
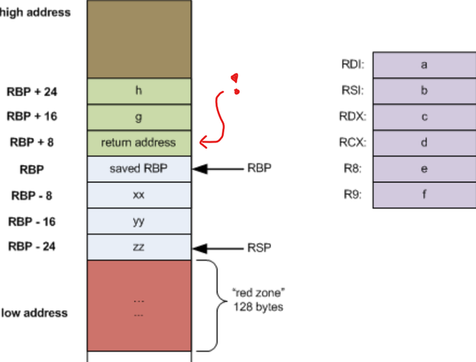 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 0neday/multi_path
CVE-2018-4241: XNU kernel heap overflow due to bad bounds checking in MPTCP for iOS 11 - 11.3.1released by Ian Beer
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
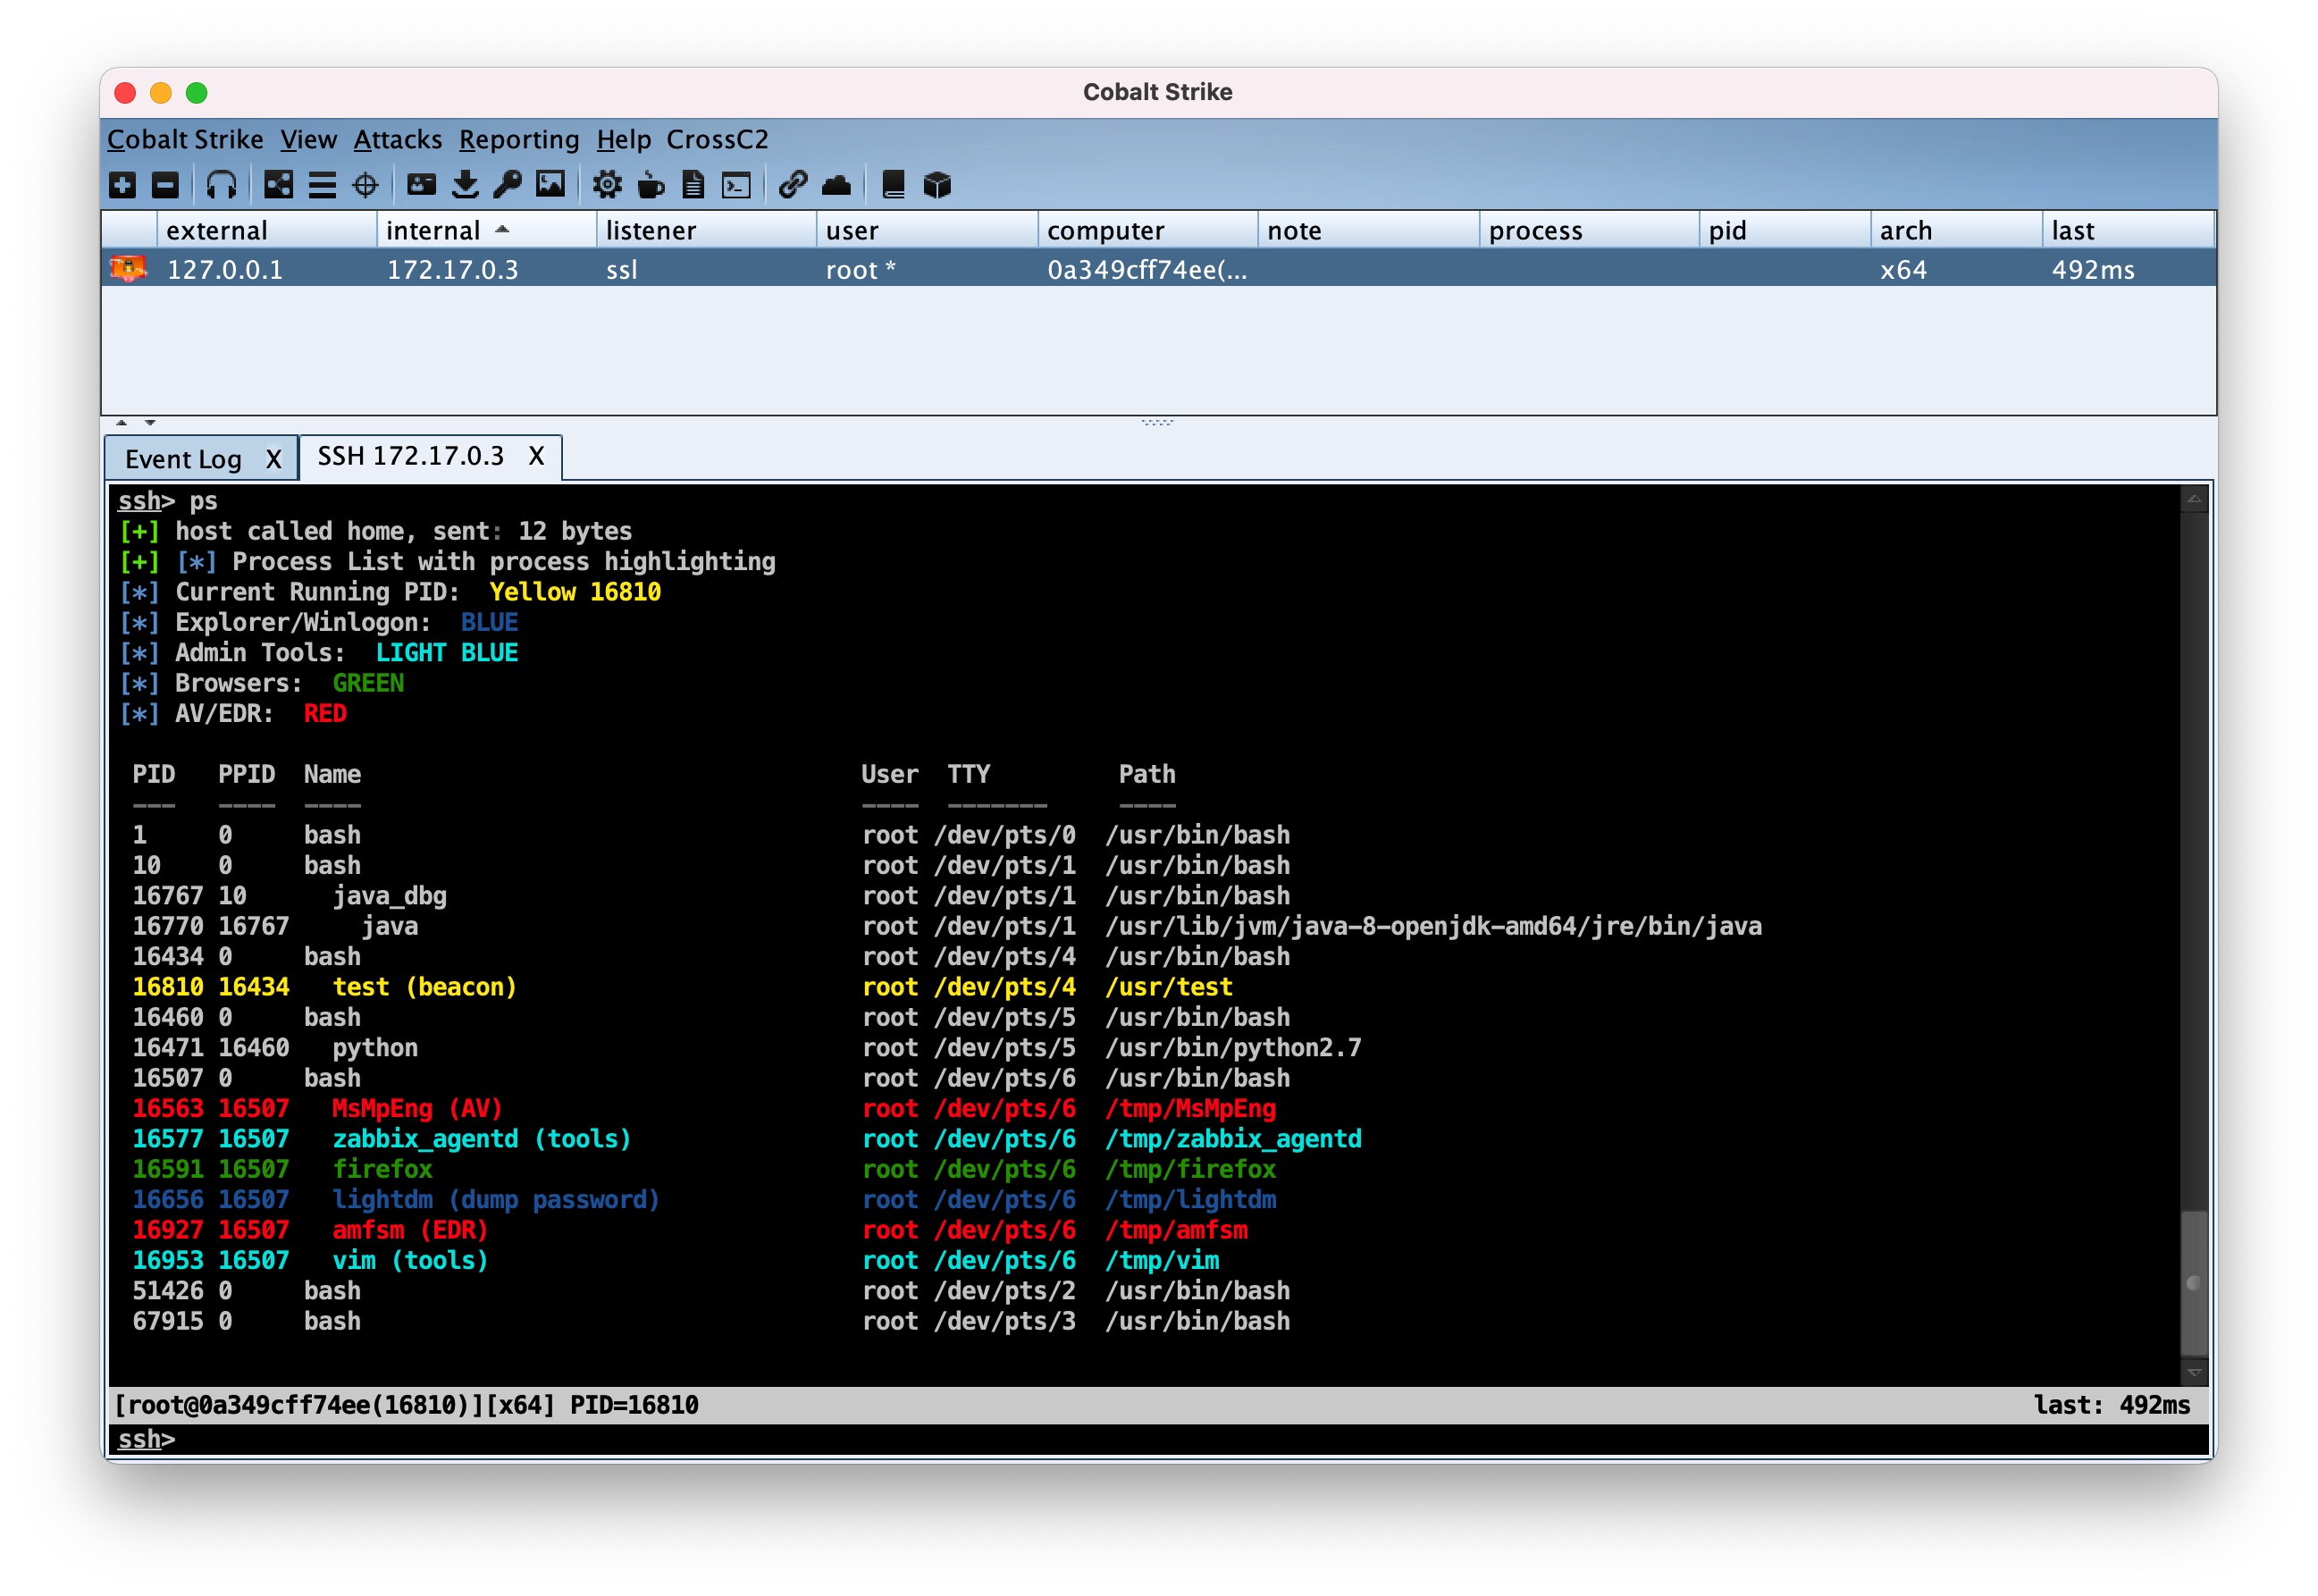 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 kyleavery/aceldr
Cobalt Strike UDRL for memory scanner evasion.