

Process-Dump
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k1 month ago
glmcdona/process-dumpWindows tool for dumping malware PE files from memory back to disk for analysis.
 dawnl3ss/cve-2023-32784
Retrieve the master password of a keepass database <= 2.53.1
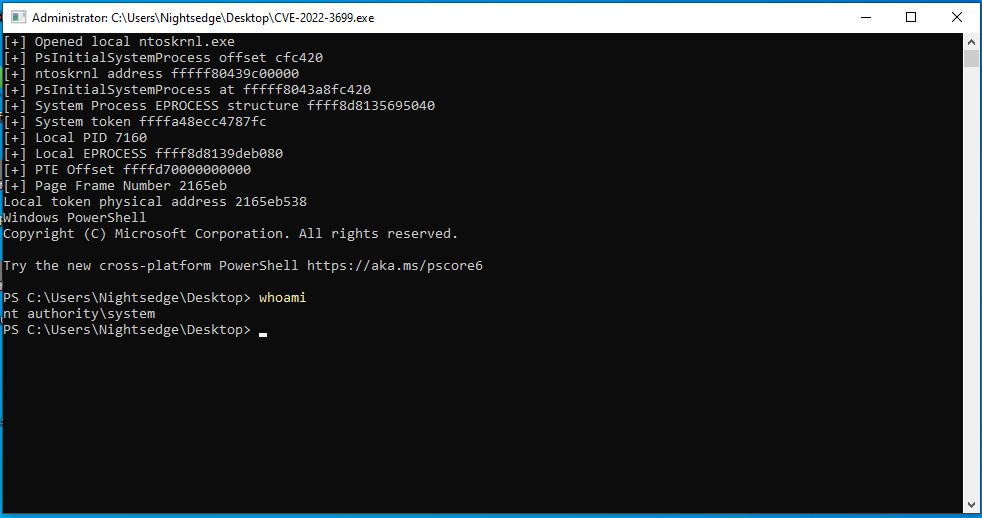 eap2468/cve-2022-3699
Proof of Concept exploit for CVE-2022-3699
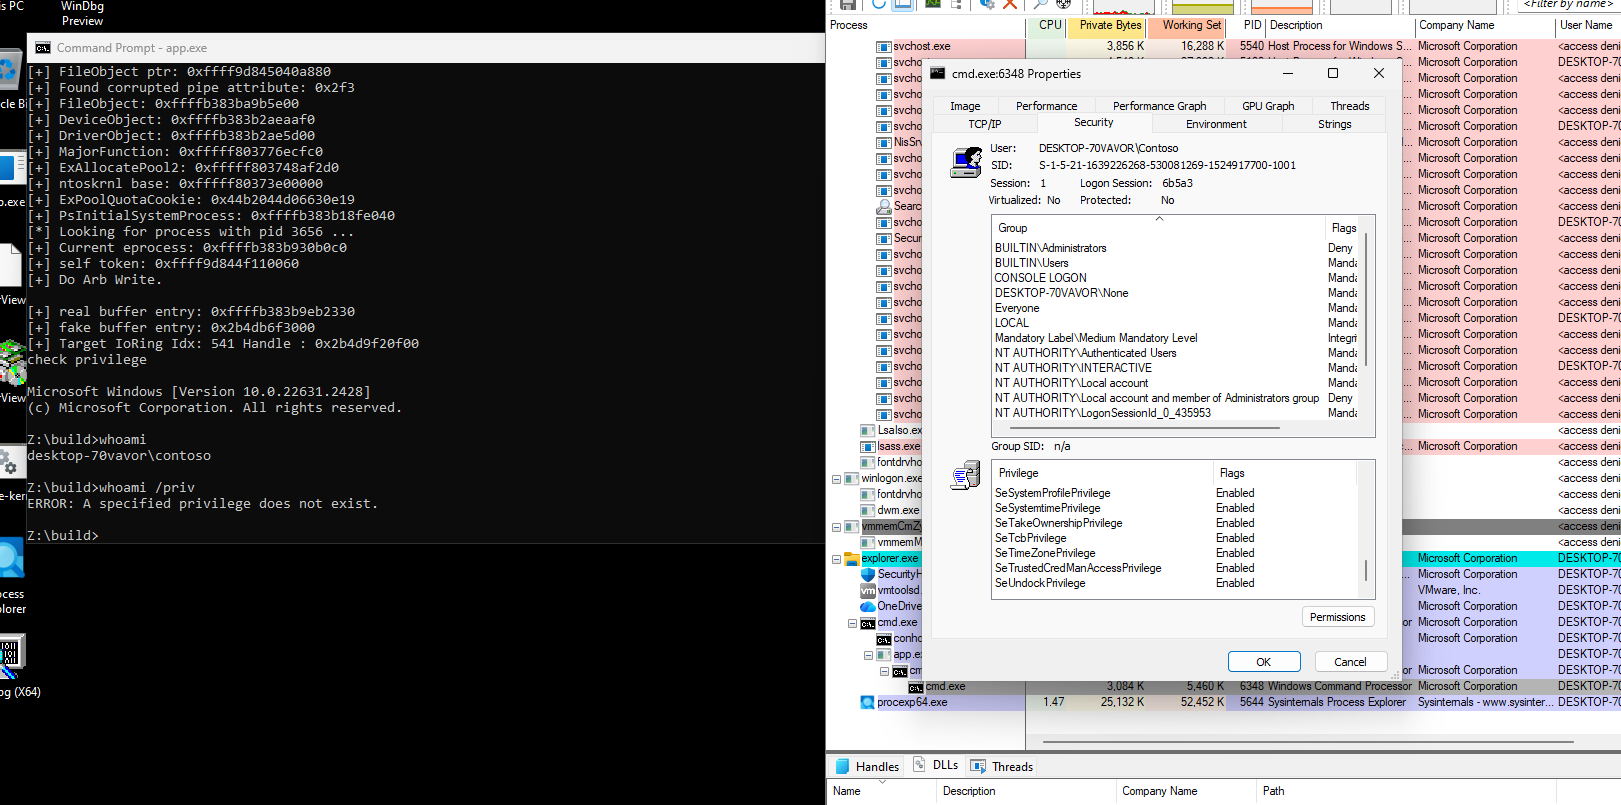 nu1lptr0/cve-2025-21333
LPE due to integer truncation in vskrnlintvsp.sys
 jedai47/cve-2017-16994
Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…