
DeepBlueCLI
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…

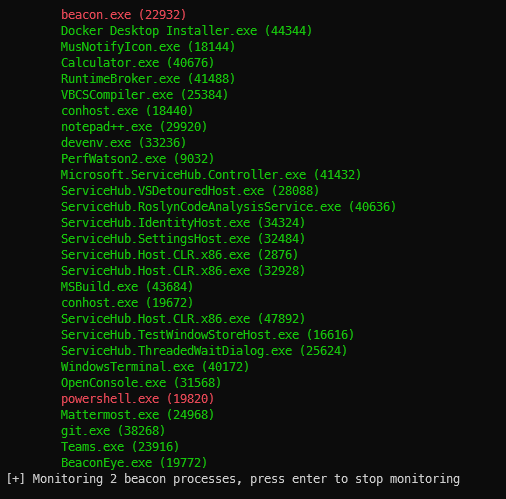
Hunts out CobaltStrike beacons and logs operator command output

Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…

Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.

Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…

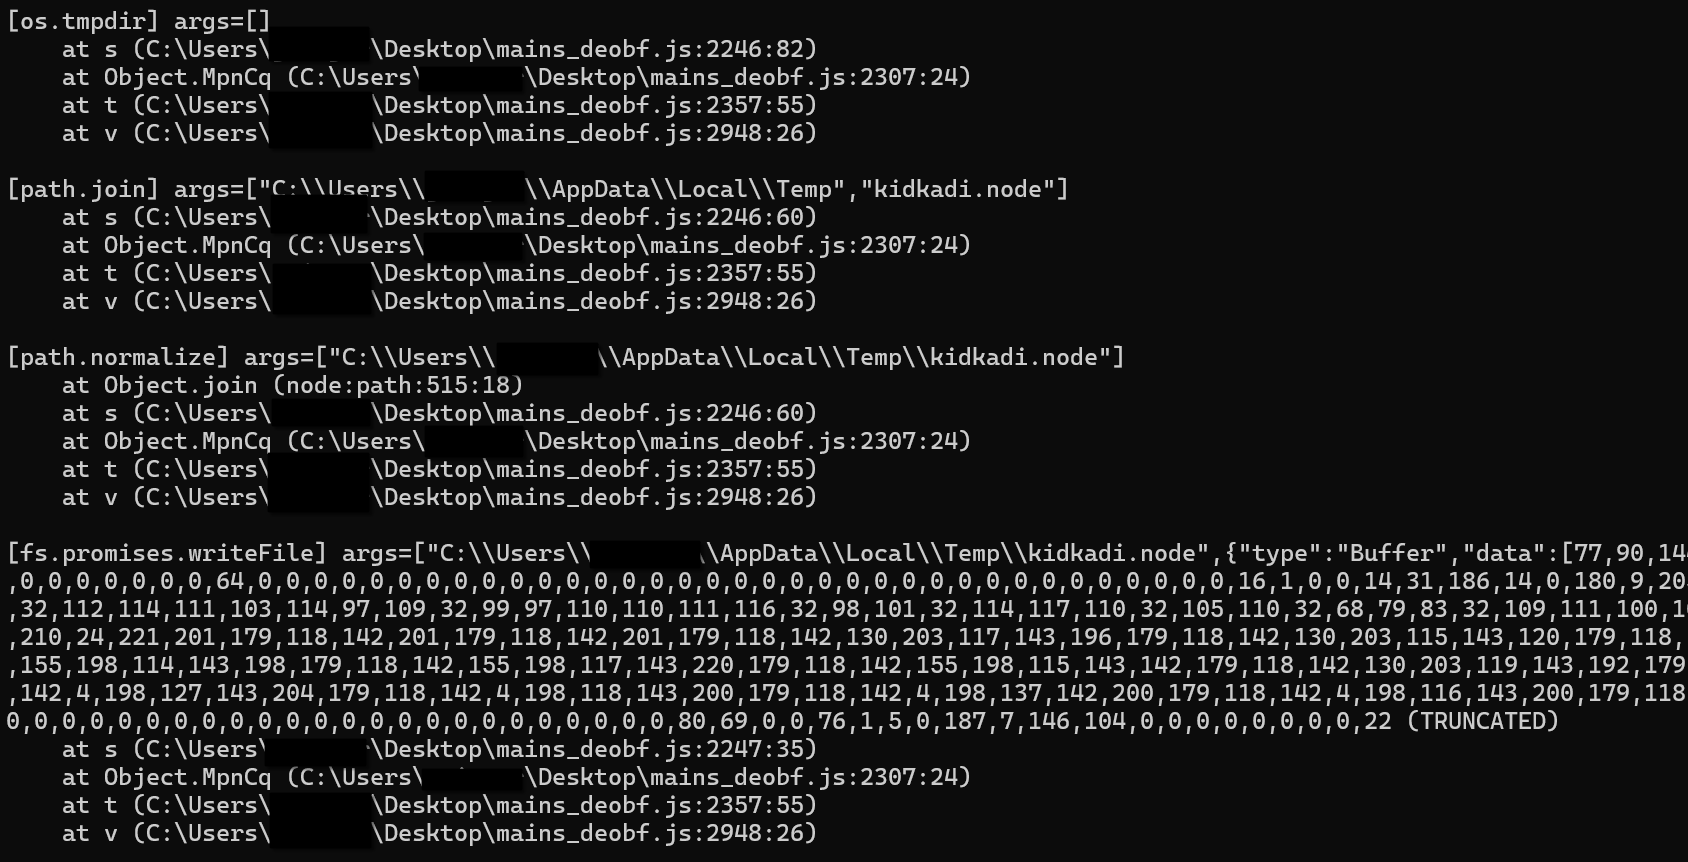
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…

Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.

Repository of Yara Rules

Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.

Some Rust program I wrote while learning Malware Development

Documented incident response case for CVE-2024-49138 exploitation, featuring log analysis, hash validation, C2 detection, and containment procedures…

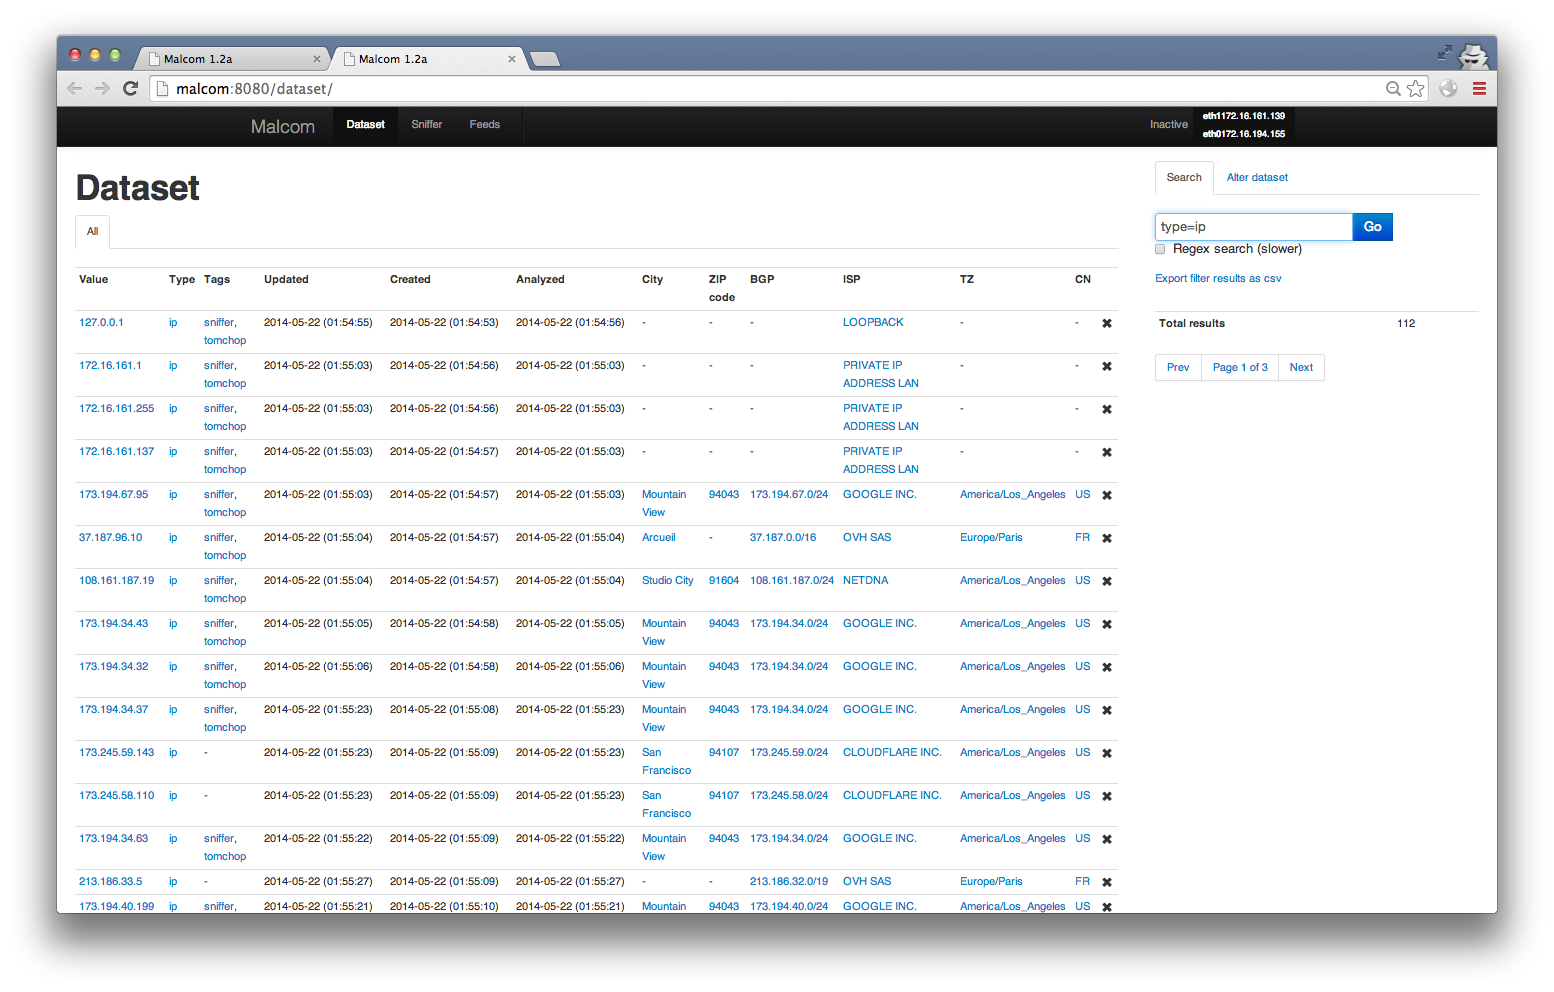
Malcom - Malware Communications Analyzer

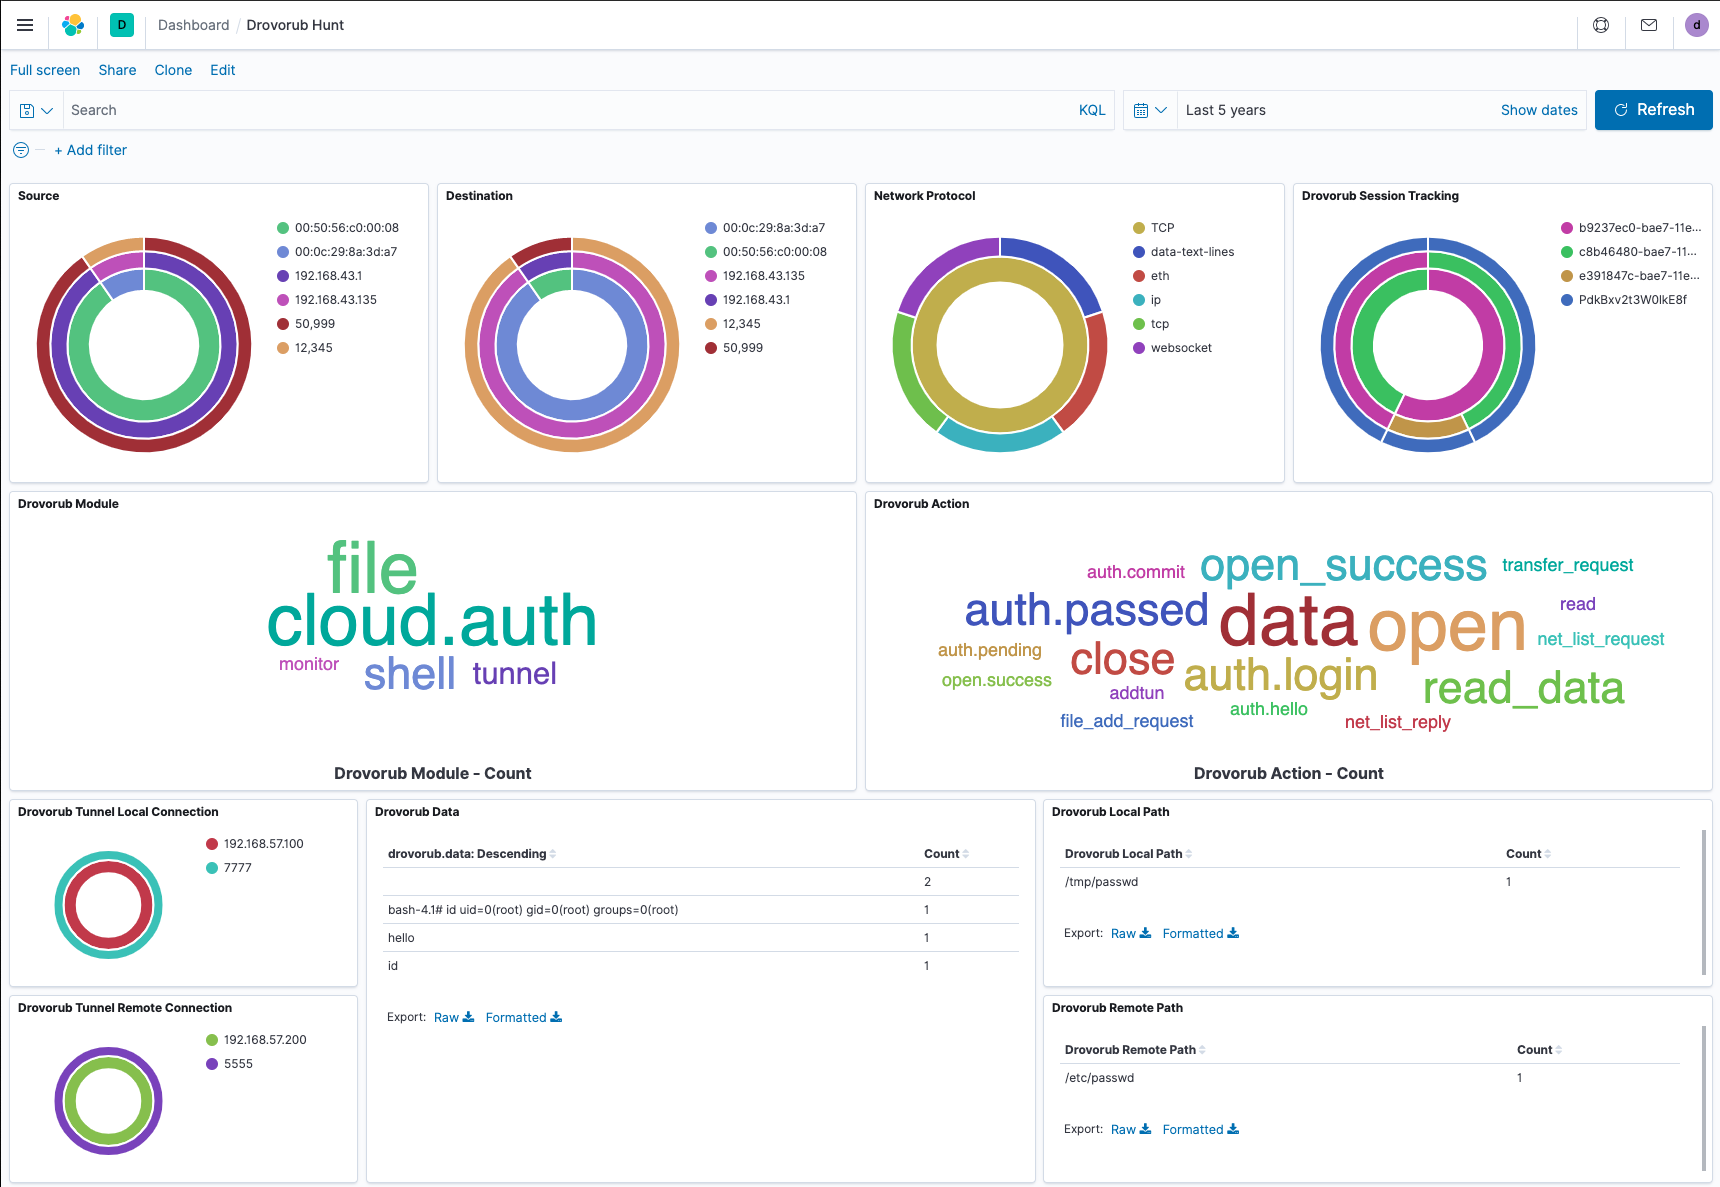
A tool to assist with network-based hunting for GRU's Drovorub malware c2