
dissect.cobaltstrike
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
binary-analysiscommand-and-controldigital-forensics+4
198
fox-it/dissect.cobaltstrikePython library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 airbus-cert/ditto
Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 umpolungfish/byvalver
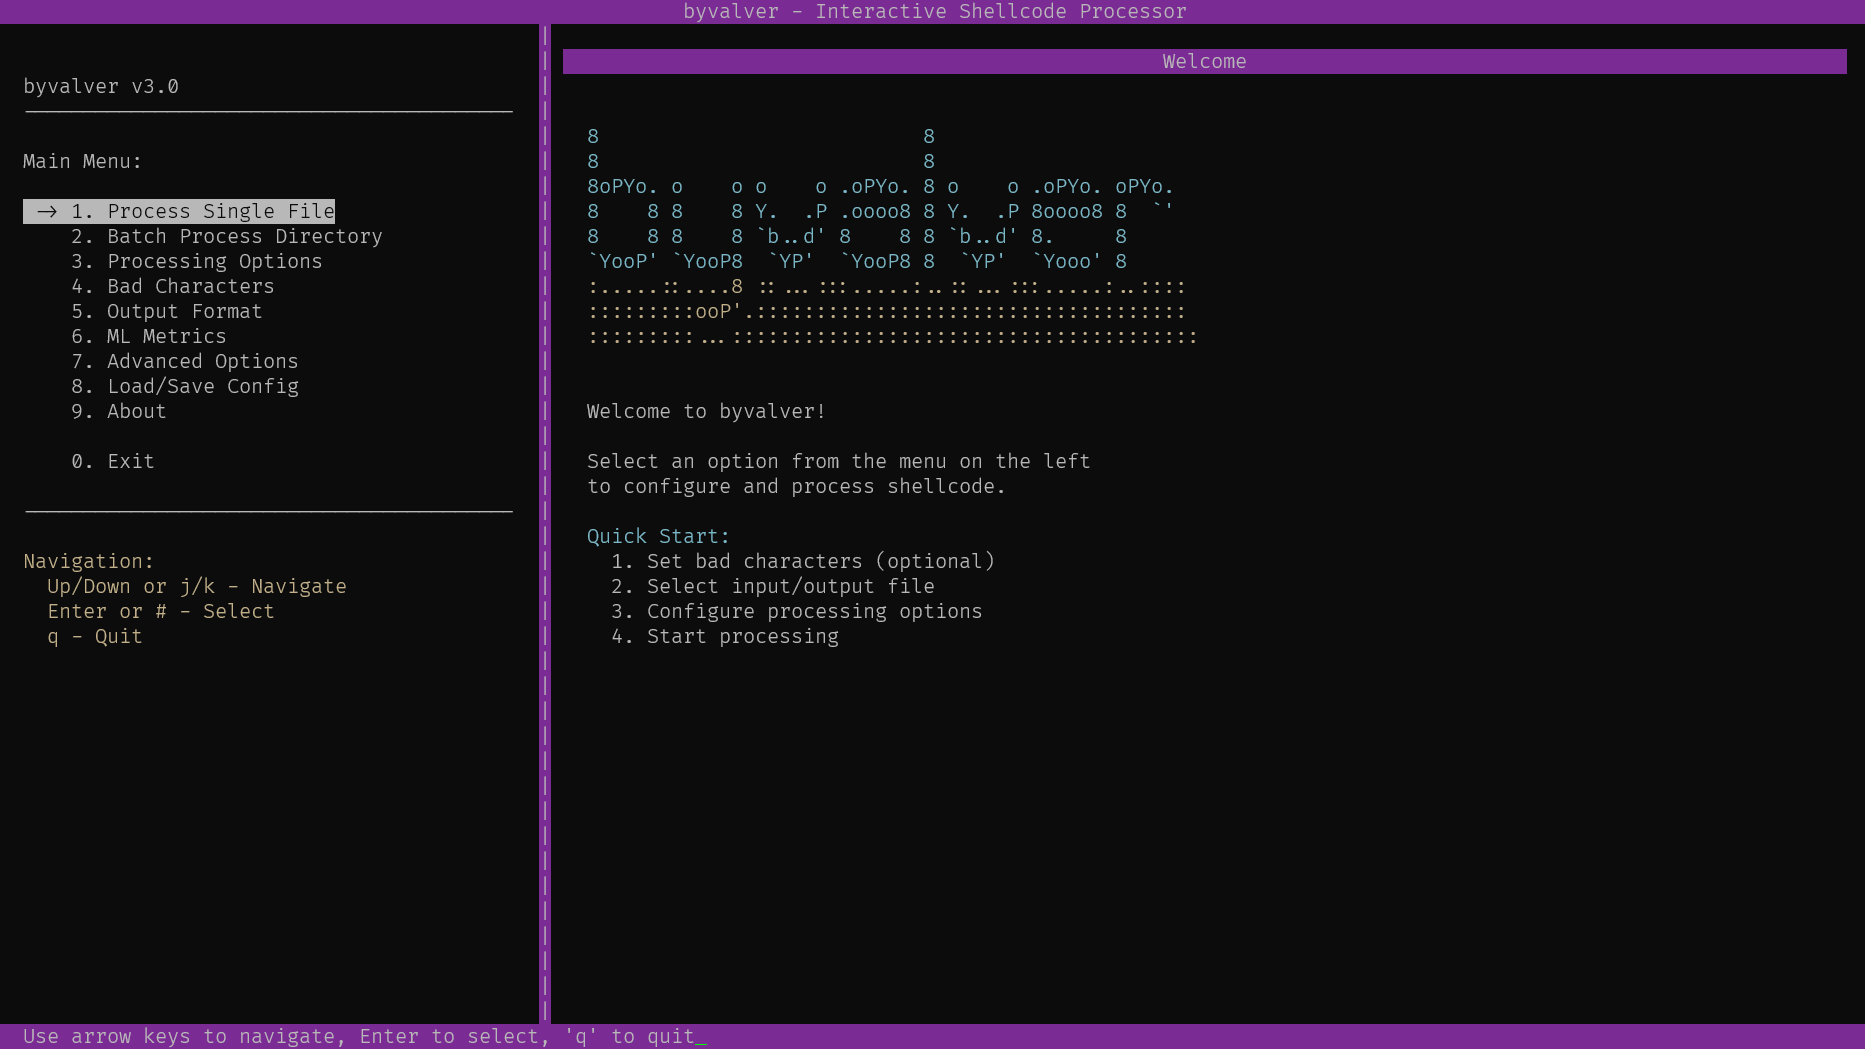
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities