
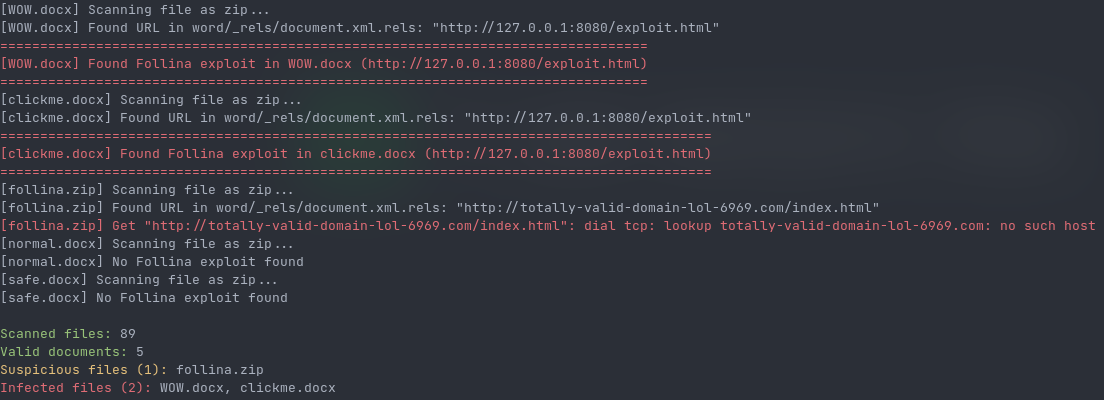
FollinaScanner
 errornointernet/follinascanner
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
code-analysismalware-analysisstatic-analysis+2
23
errornointernet/follinascannerA tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
 rythmstick/amsitrigger
The Hunt for Malicious Strings
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 jacobsoo/rtf-cleaner
Extracts URLs from malicious RTF files exploiting CVE-2017-0199 and CVE-2017-8759 for malware analysis and threat intelligence.
 urule99/jsunpack-n
Automatically exported from code.google.com/p/jsunpack-n
 capesandbox/cape-parsers
CAPE core and community parsers
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…