Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
astaroth-deobfuscator preview

astaroth-deobfuscator

GitHubdodo-sec/astaroth-deobfuscator

IDA python script for deobfuscating Astaroth/Guildma injector DLL
binary-analysismalware-analysisreverse-engineering+1
83 years ago
CVE-2023-38831-Exploit-and-Detection preview

CVE-2023-38831-Exploit-and-Detection

GitHubml-k-eng/cve-2023-38831-exploit-and-detection

This repository has both an attack detection tool and a Proof-of-Concept (PoC) Python script for the WinRAR CVE-2023-38831 vulnerability.
defensive-toolsexploitationincident-response+3
3 years ago
AutoIt-Ripper preview

AutoIt-Ripper

GitHubnazywam/autoit-ripper

Extract AutoIt scripts embedded in PE binaries
binary-analysisdigital-forensicsmalware-analysis+1
2436 months ago
detect_CVE-2026-21509 preview

detect_CVE-2026-21509

GitHubdecalage2/detect_cve-2026-21509

YARA rule and python script to detect potential exploits for the CVE-2026-21509 vulnerability in MS Office
forensicsmalware-analysisvulnerability-analysis
38 months ago
python-exe-unpacker preview

python-exe-unpacker

GitHubwithsecurelabs/python-exe-unpacker

A helper script for unpacking and decompiling EXEs compiled from python code.
binary-analysisdynamic-analysis-sandboxingforensics+2
1.0k2 years ago
CVE-2023-21036 preview

CVE-2023-21036

GitHubinfobyte/cve-2023-21036

Detection and sanitization for Acropalypse Now - CVE-2023-21036

data-recoverydigital-forensicsencryption-decryption-tools+3
803 years ago
CVE-2025-20260-POC preview

CVE-2025-20260-POC

GitHubalex-acero-security/cve-2025-20260-poc

Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
binary-exploitationexploitationfuzzing+3
4 months ago
CVE-2026-31431-Copy-Fail preview

CVE-2026-31431-Copy-Fail

GitHubrecofu/cve-2026-31431-copy-fail

Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…

container-escapeexploitationexploit-frameworks+3
5 months ago
Hybrid Submit preview

Hybrid Submit

GitLabkaysec/hybrid-submit

A script that automatically submits files to Hybrid Analysis (API)
api-securitymalware-analysisscripting-automation
3 months ago
PESTO preview

PESTO

GitHubelevenpaths/pesto

Extracts and analyzes PE file security characteristics (ASLR, DEP, CFG, NO_SEH) from DLLs and EXEs across directories, storing results in a SQLite…
binary-analysismalware-analysisstatic-analysis+1
266 years ago
IATelligence preview

IATelligence

GitHubfr0gger/iatelligence

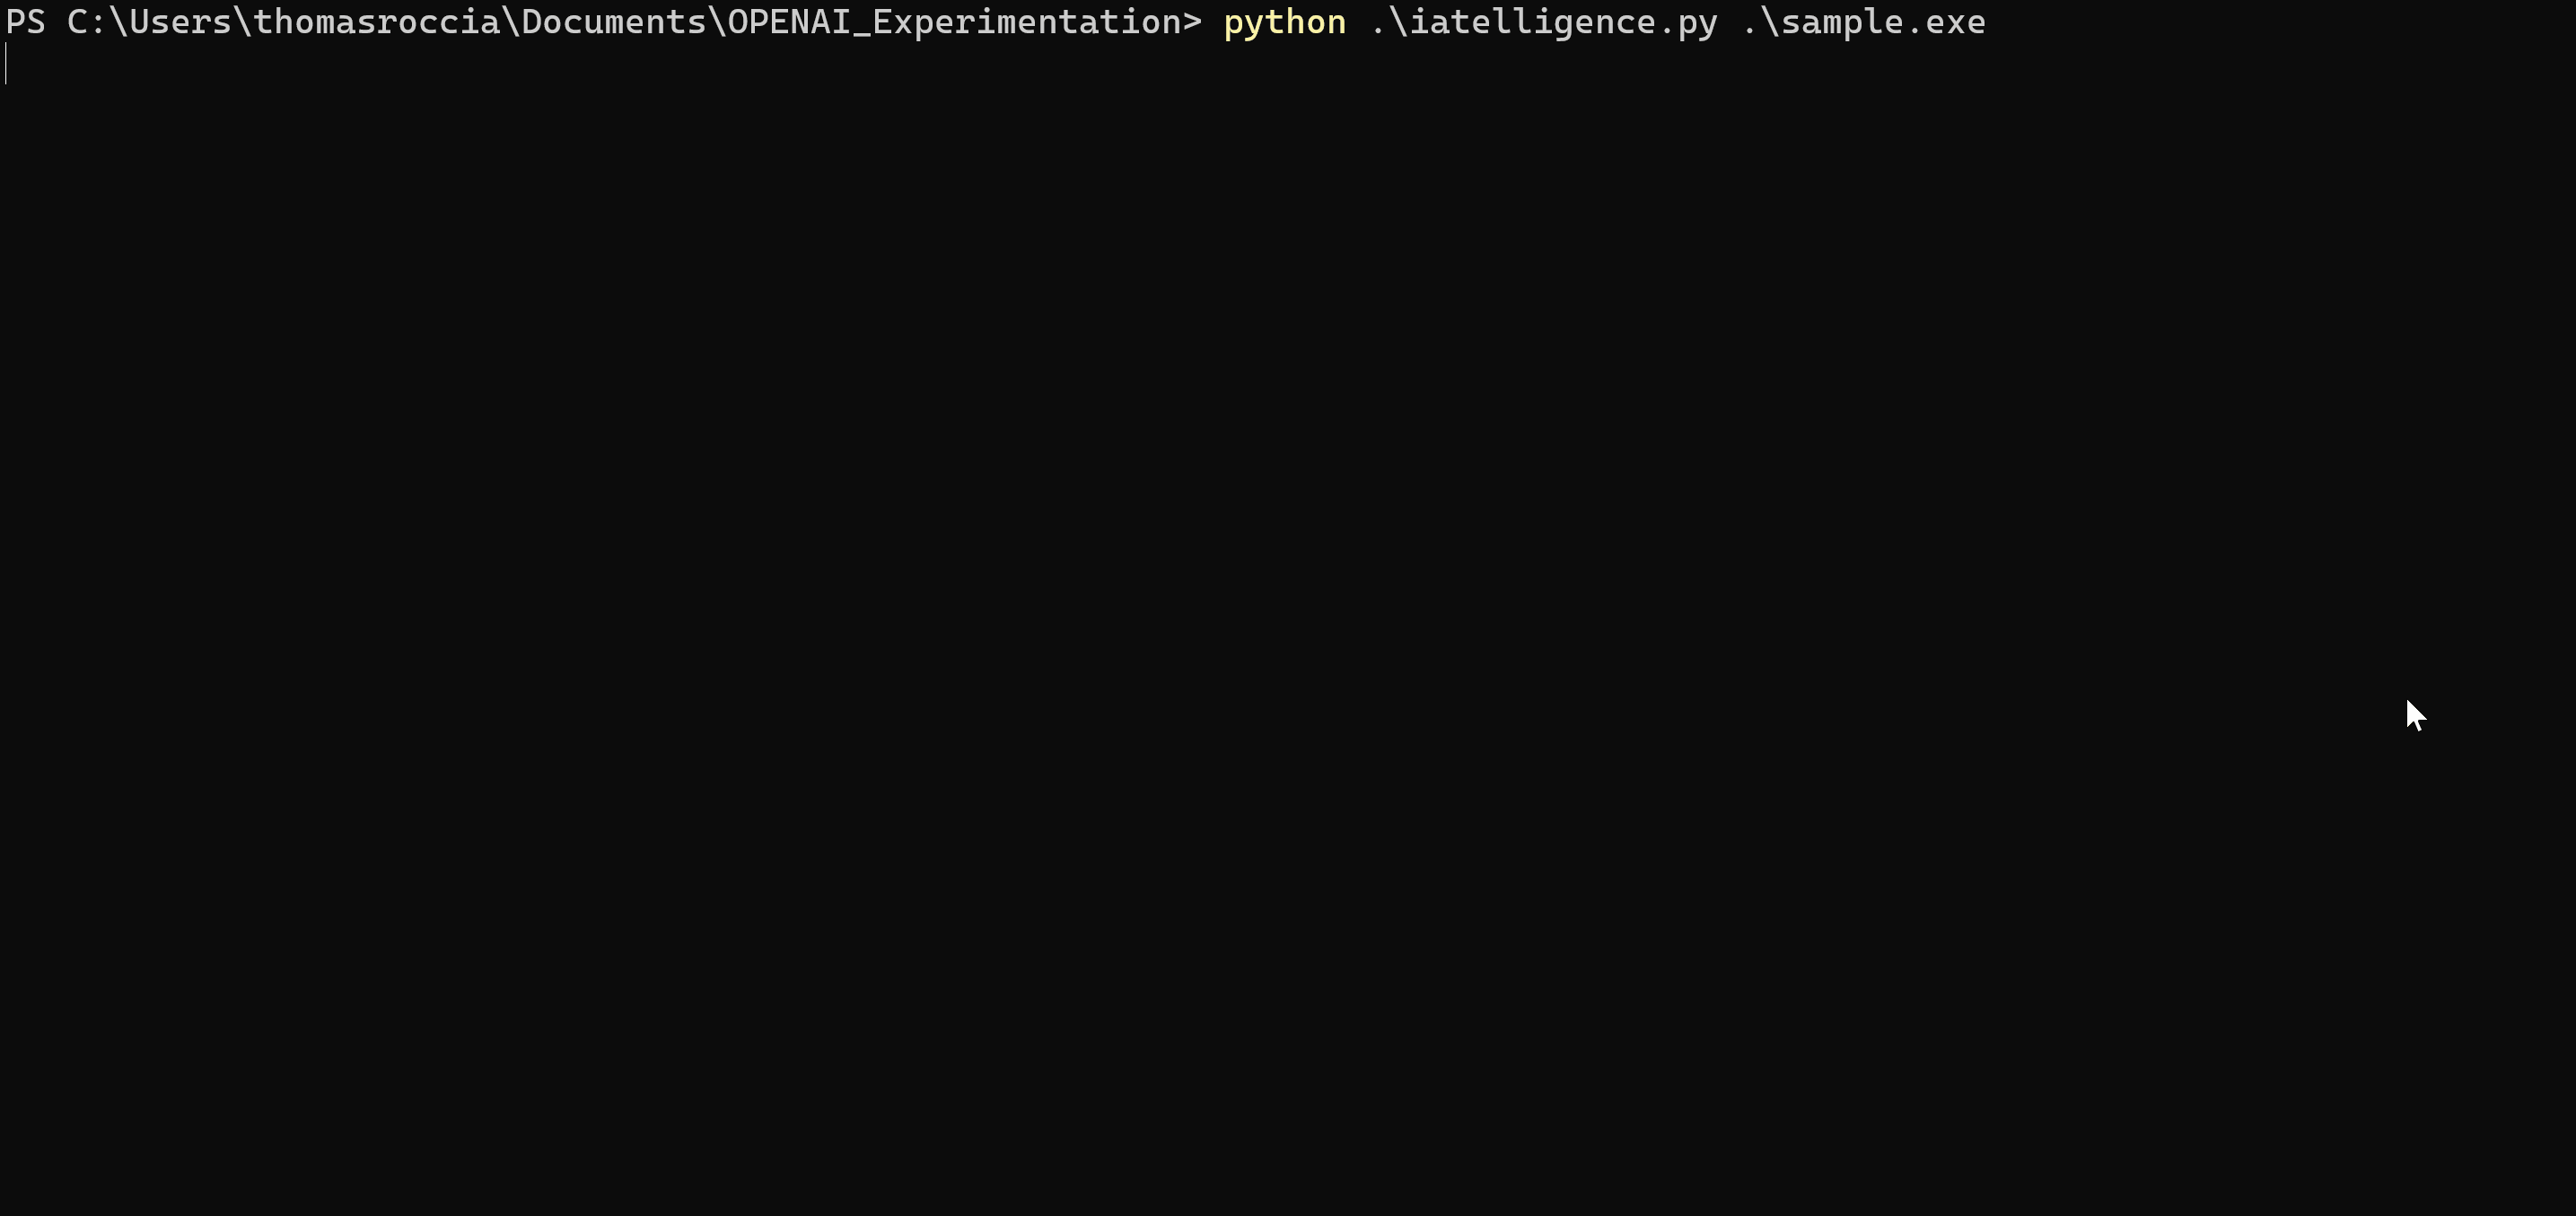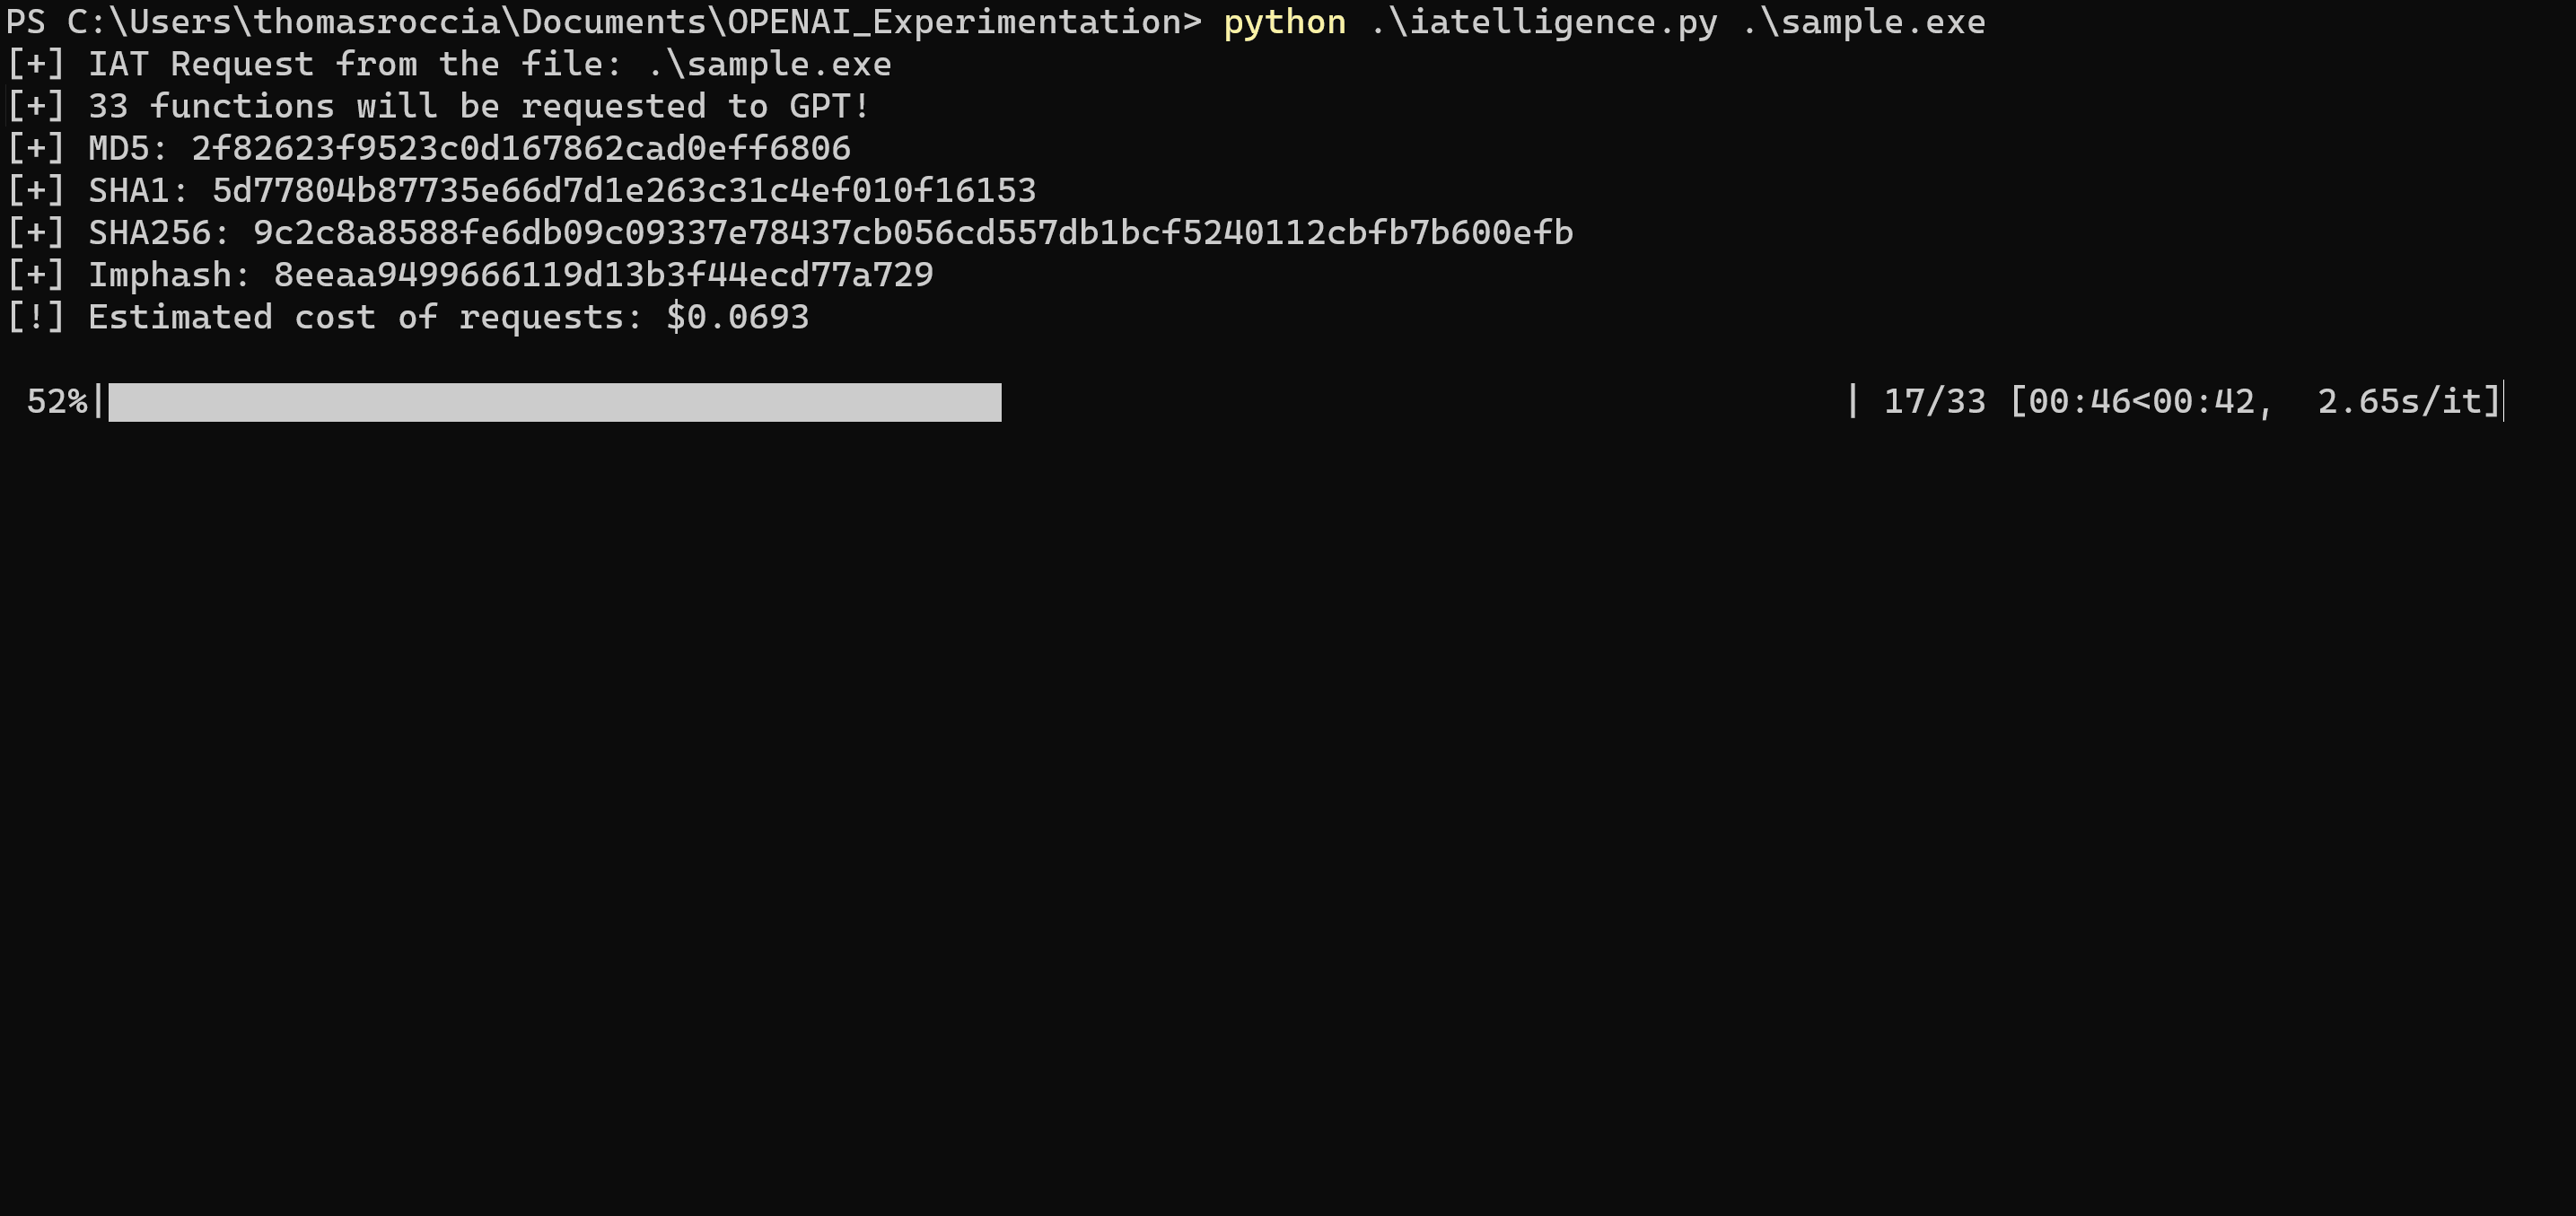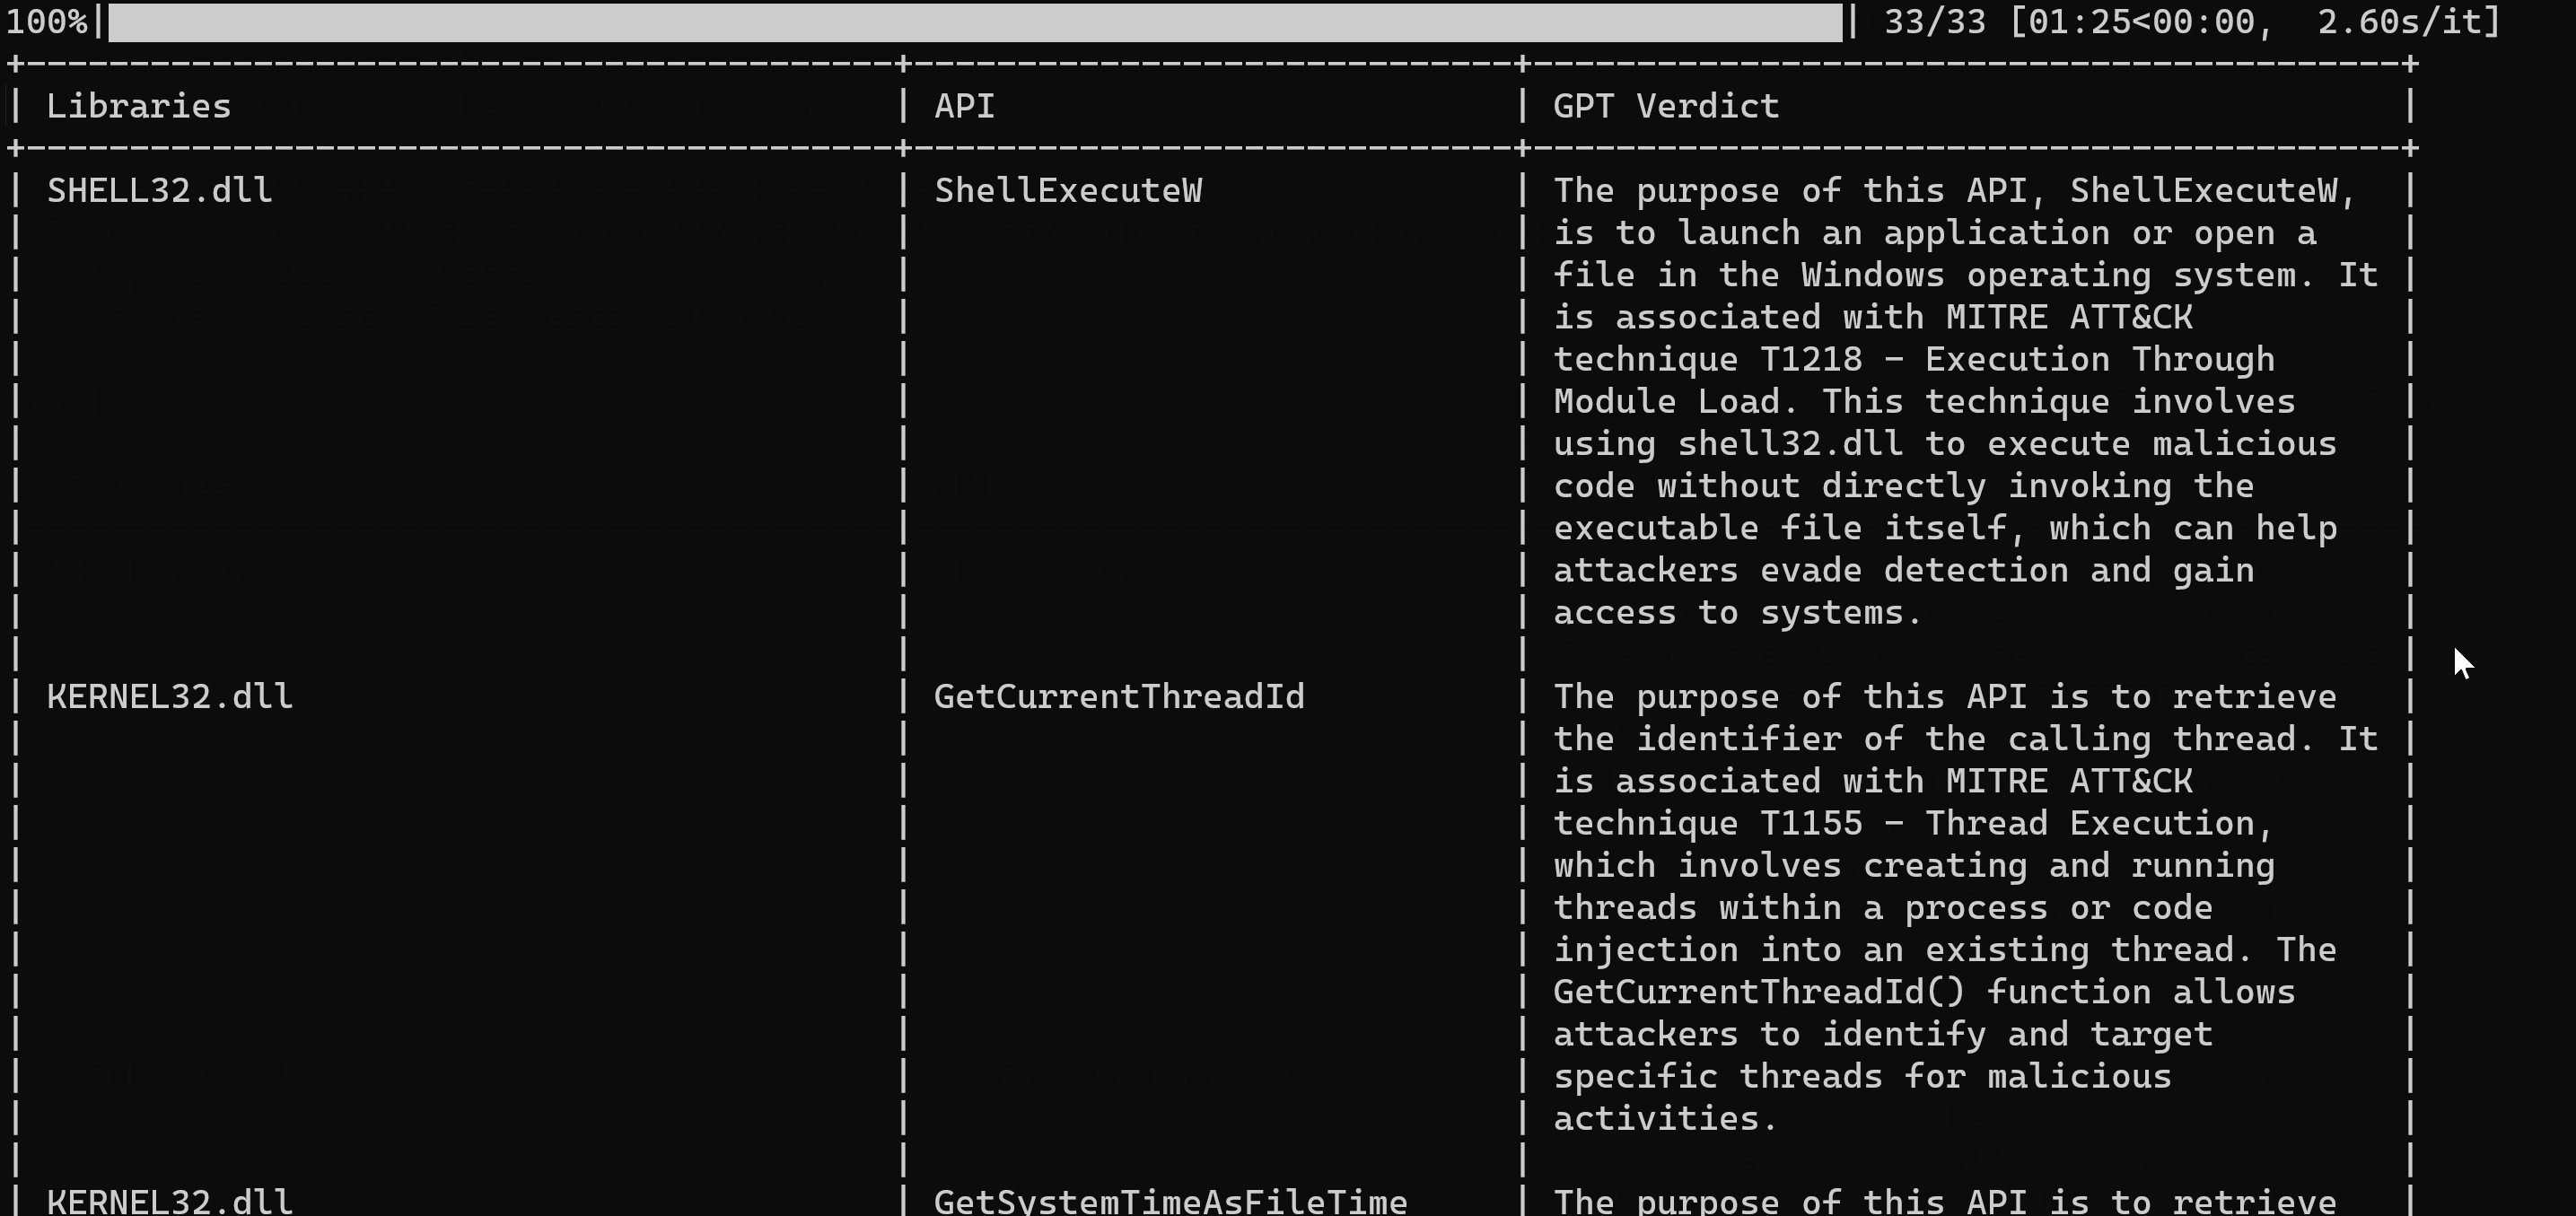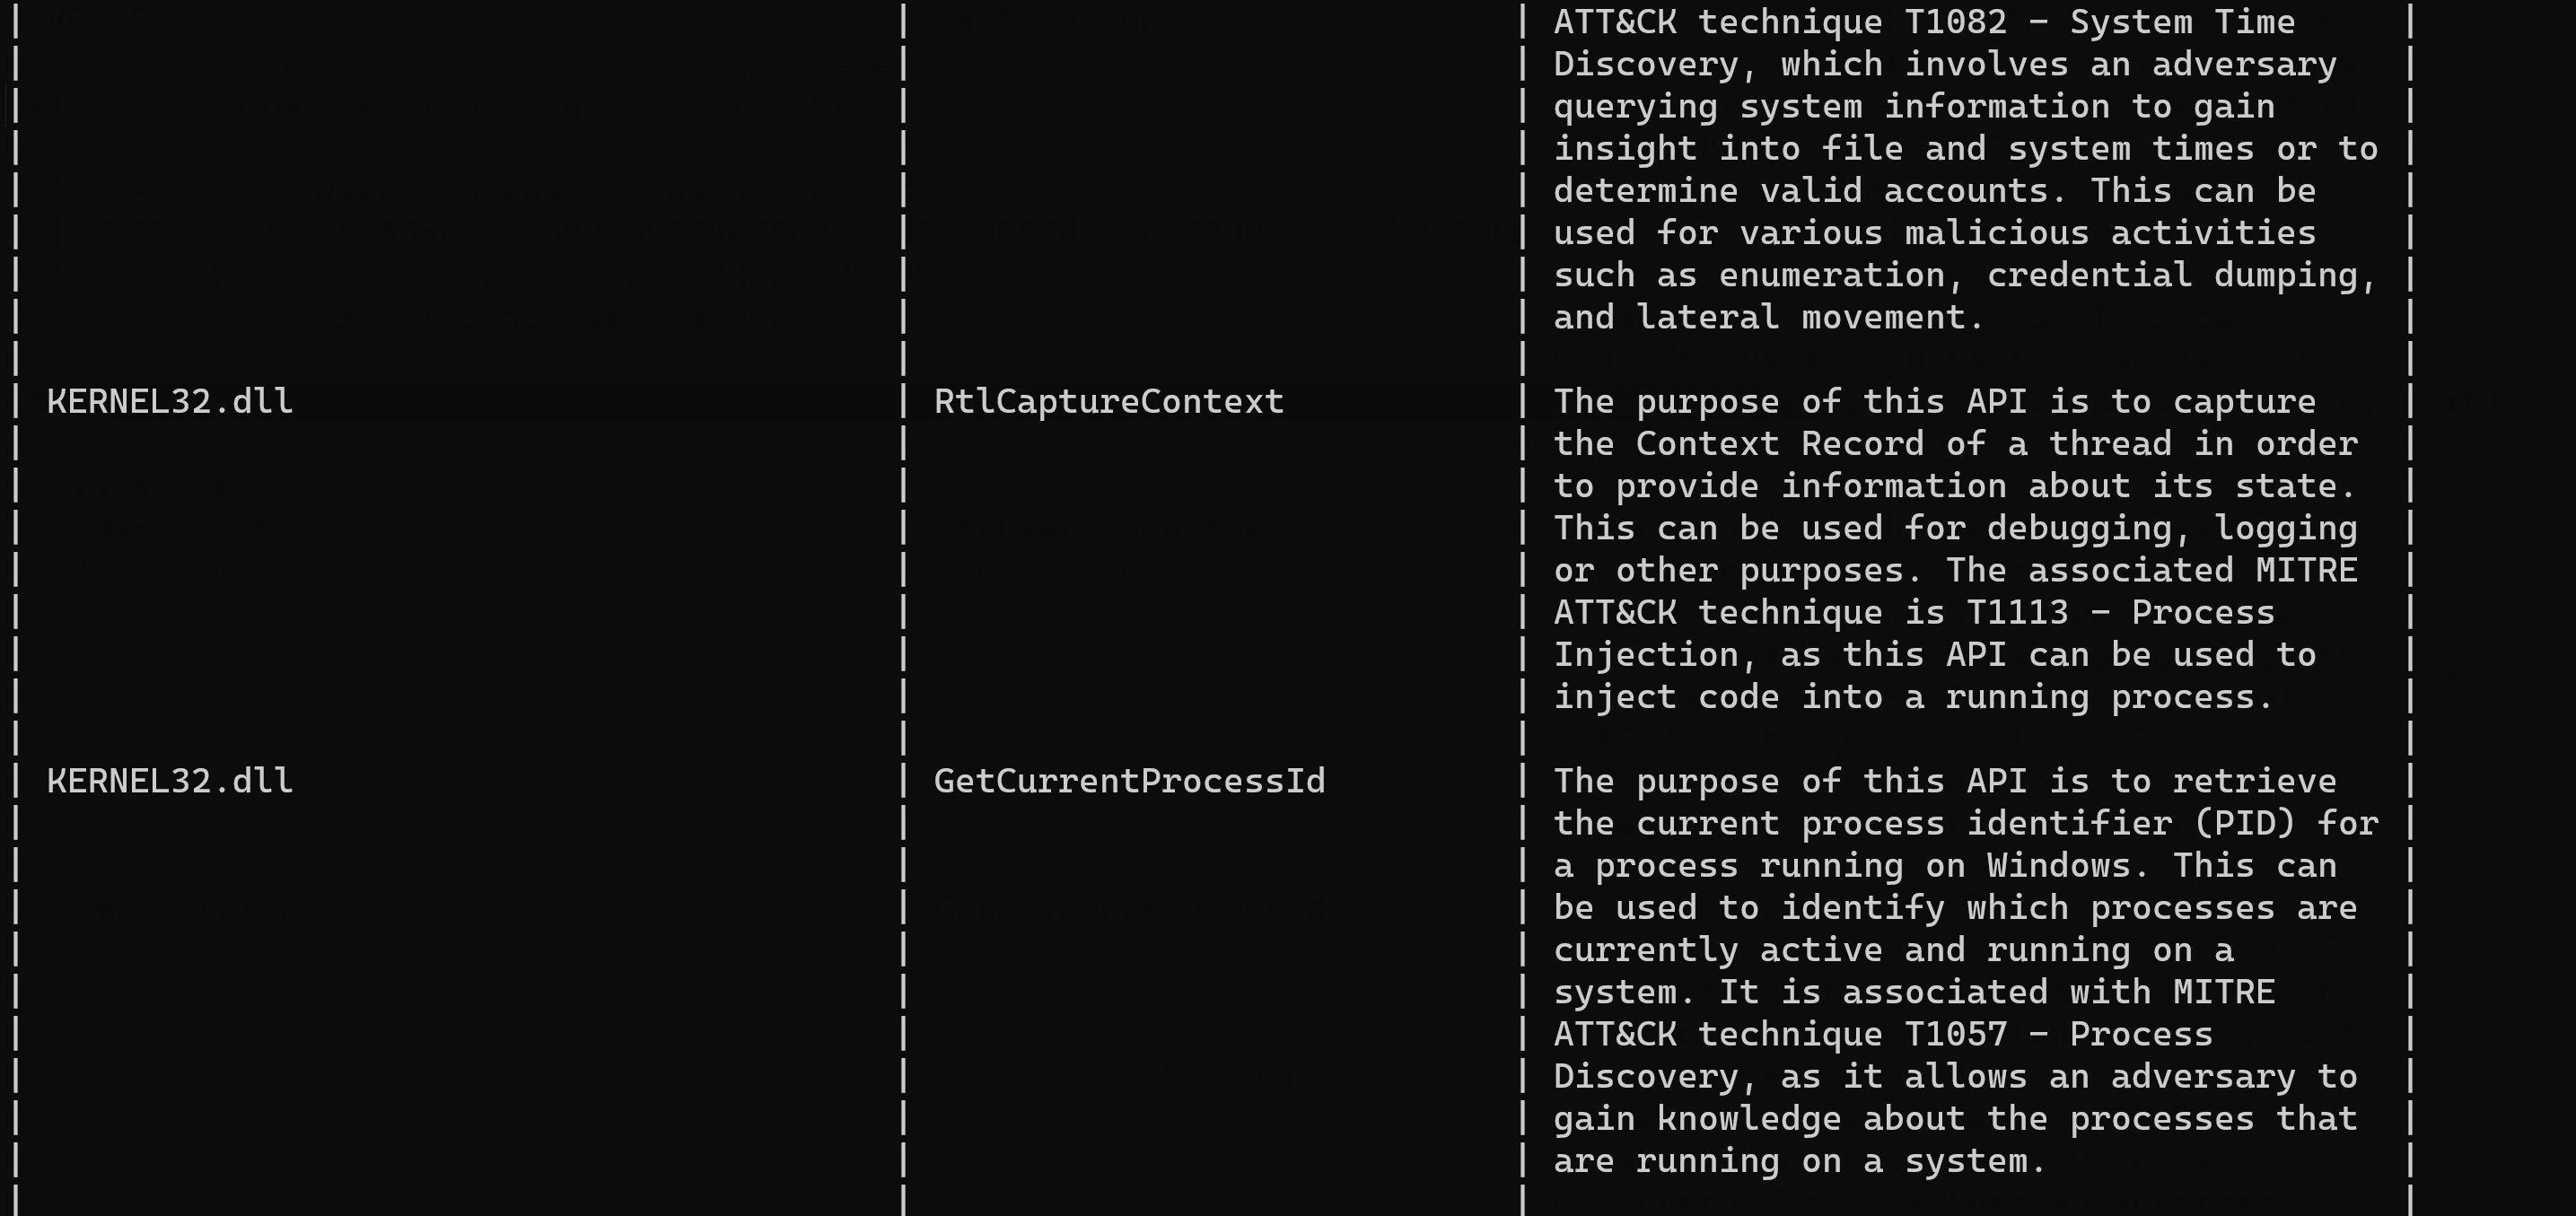
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
ai-assisted-reversingbinary-analysismalware-analysis+3
3863 years ago
TinyProcessor preview

TinyProcessor

GitHubgoatmilkkk/tinyprocessor

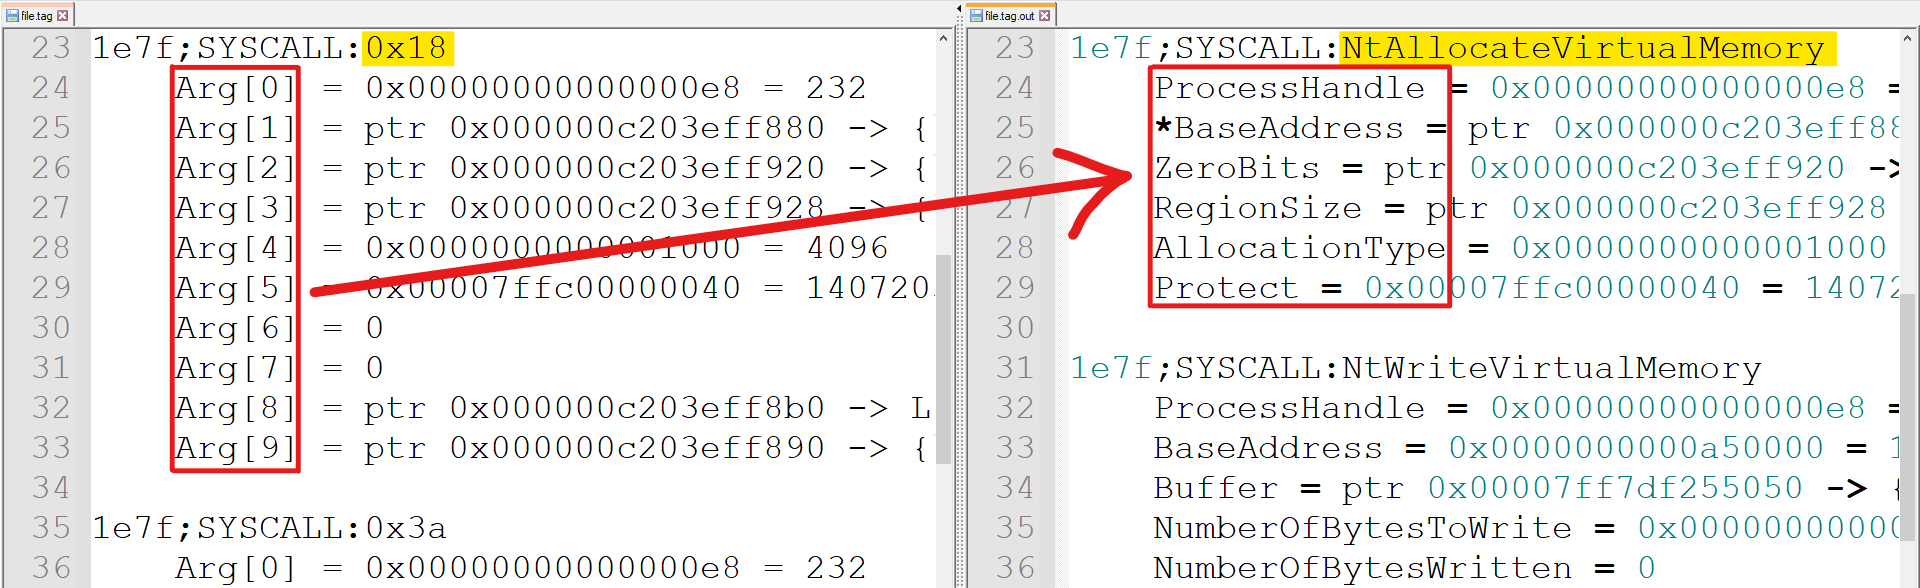
A post-processing script for TinyTracer

log-analysismalware-analysisreverse-engineering
403 years ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.
digital-forensicsforensicsincident-response+2
2682 years ago
cuckooautoinstall preview

cuckooautoinstall

GitHubbuguroo/cuckooautoinstall

Auto Installer Script for Cuckoo Sandbox
dynamic-analysis-sandboxingmalware-analysisscripting-automation+1
1648 years ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
data-exfiltrationdigital-forensicsforensics+5
139 years ago
pridelocker-analysis preview

pridelocker-analysis

GitHubsynacktiv/pridelocker-analysis

This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule
binary-analysismalware-analysisreverse-engineering+2
13 years ago
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

digital-forensicsdisk-forensicsforensics+5
915 months ago
plugxdecoder preview

plugxdecoder

GitHubkcreyts/plugxdecoder

Decodes PlugX traffic and encrypted/compressed artifacts

digital-forensicsencryption-decryption-toolsforensics+3
3813 years ago
Previous123Next