

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
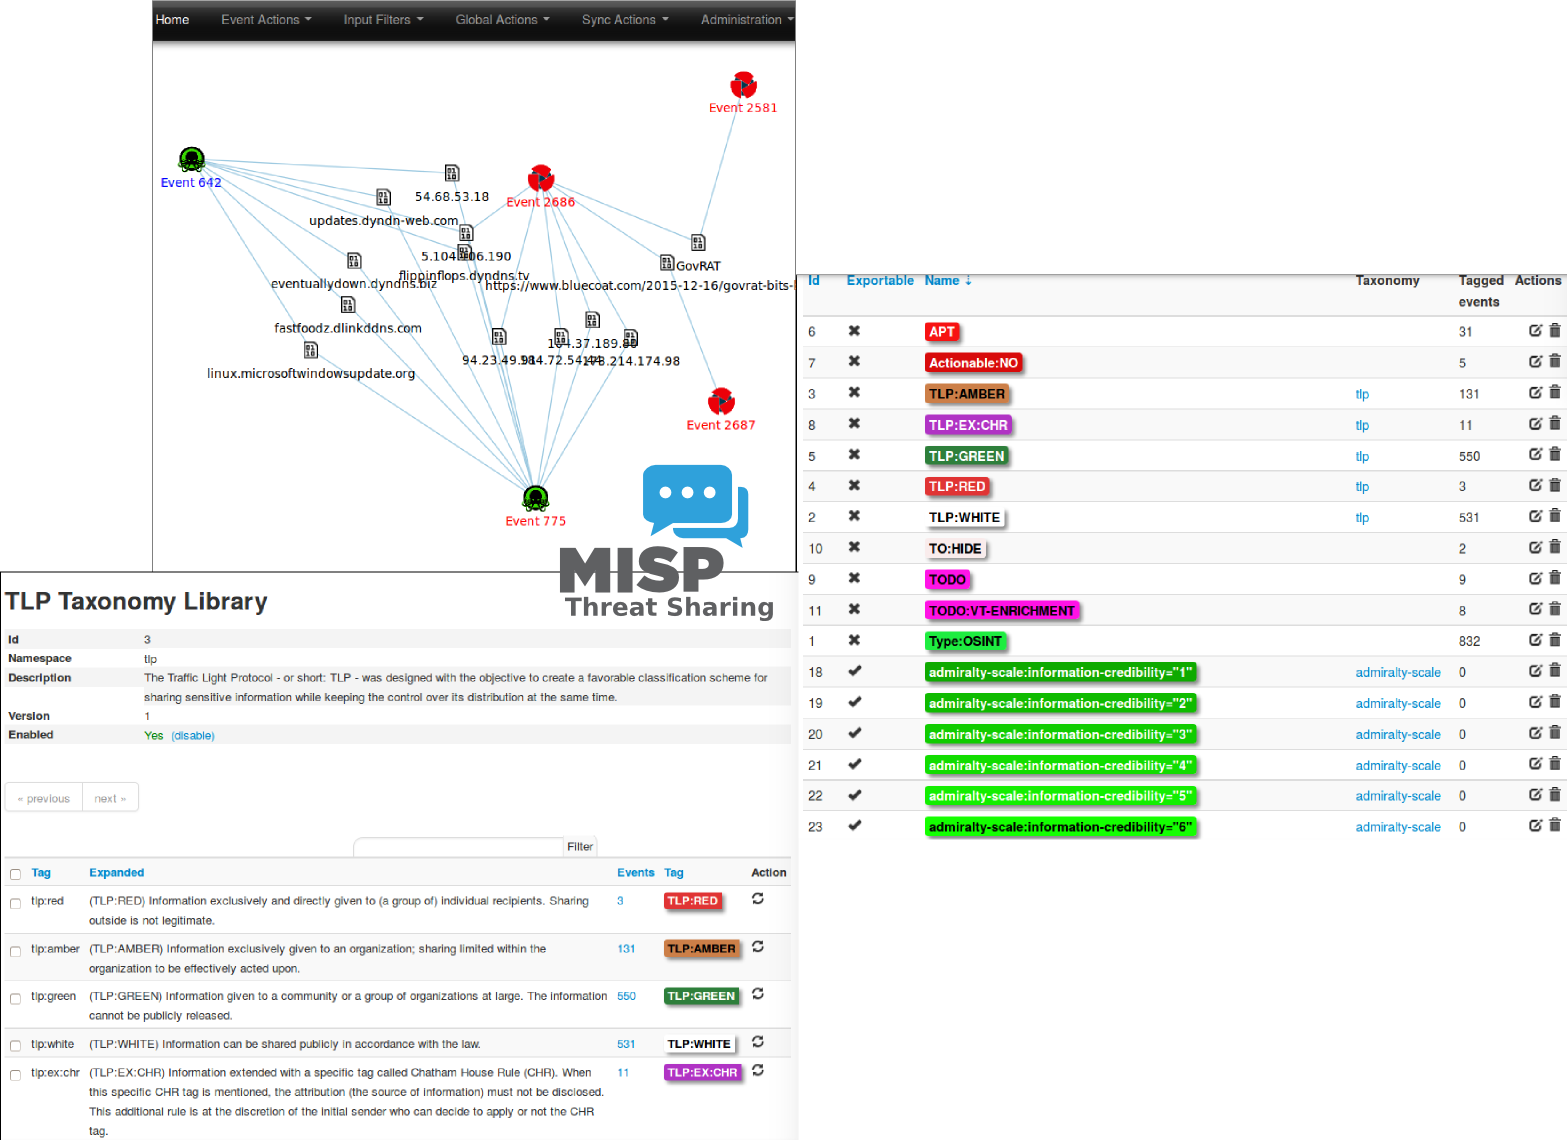 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 lan1oc/cve-2023-34312-exp
Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.
 matank001/asclepius
Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
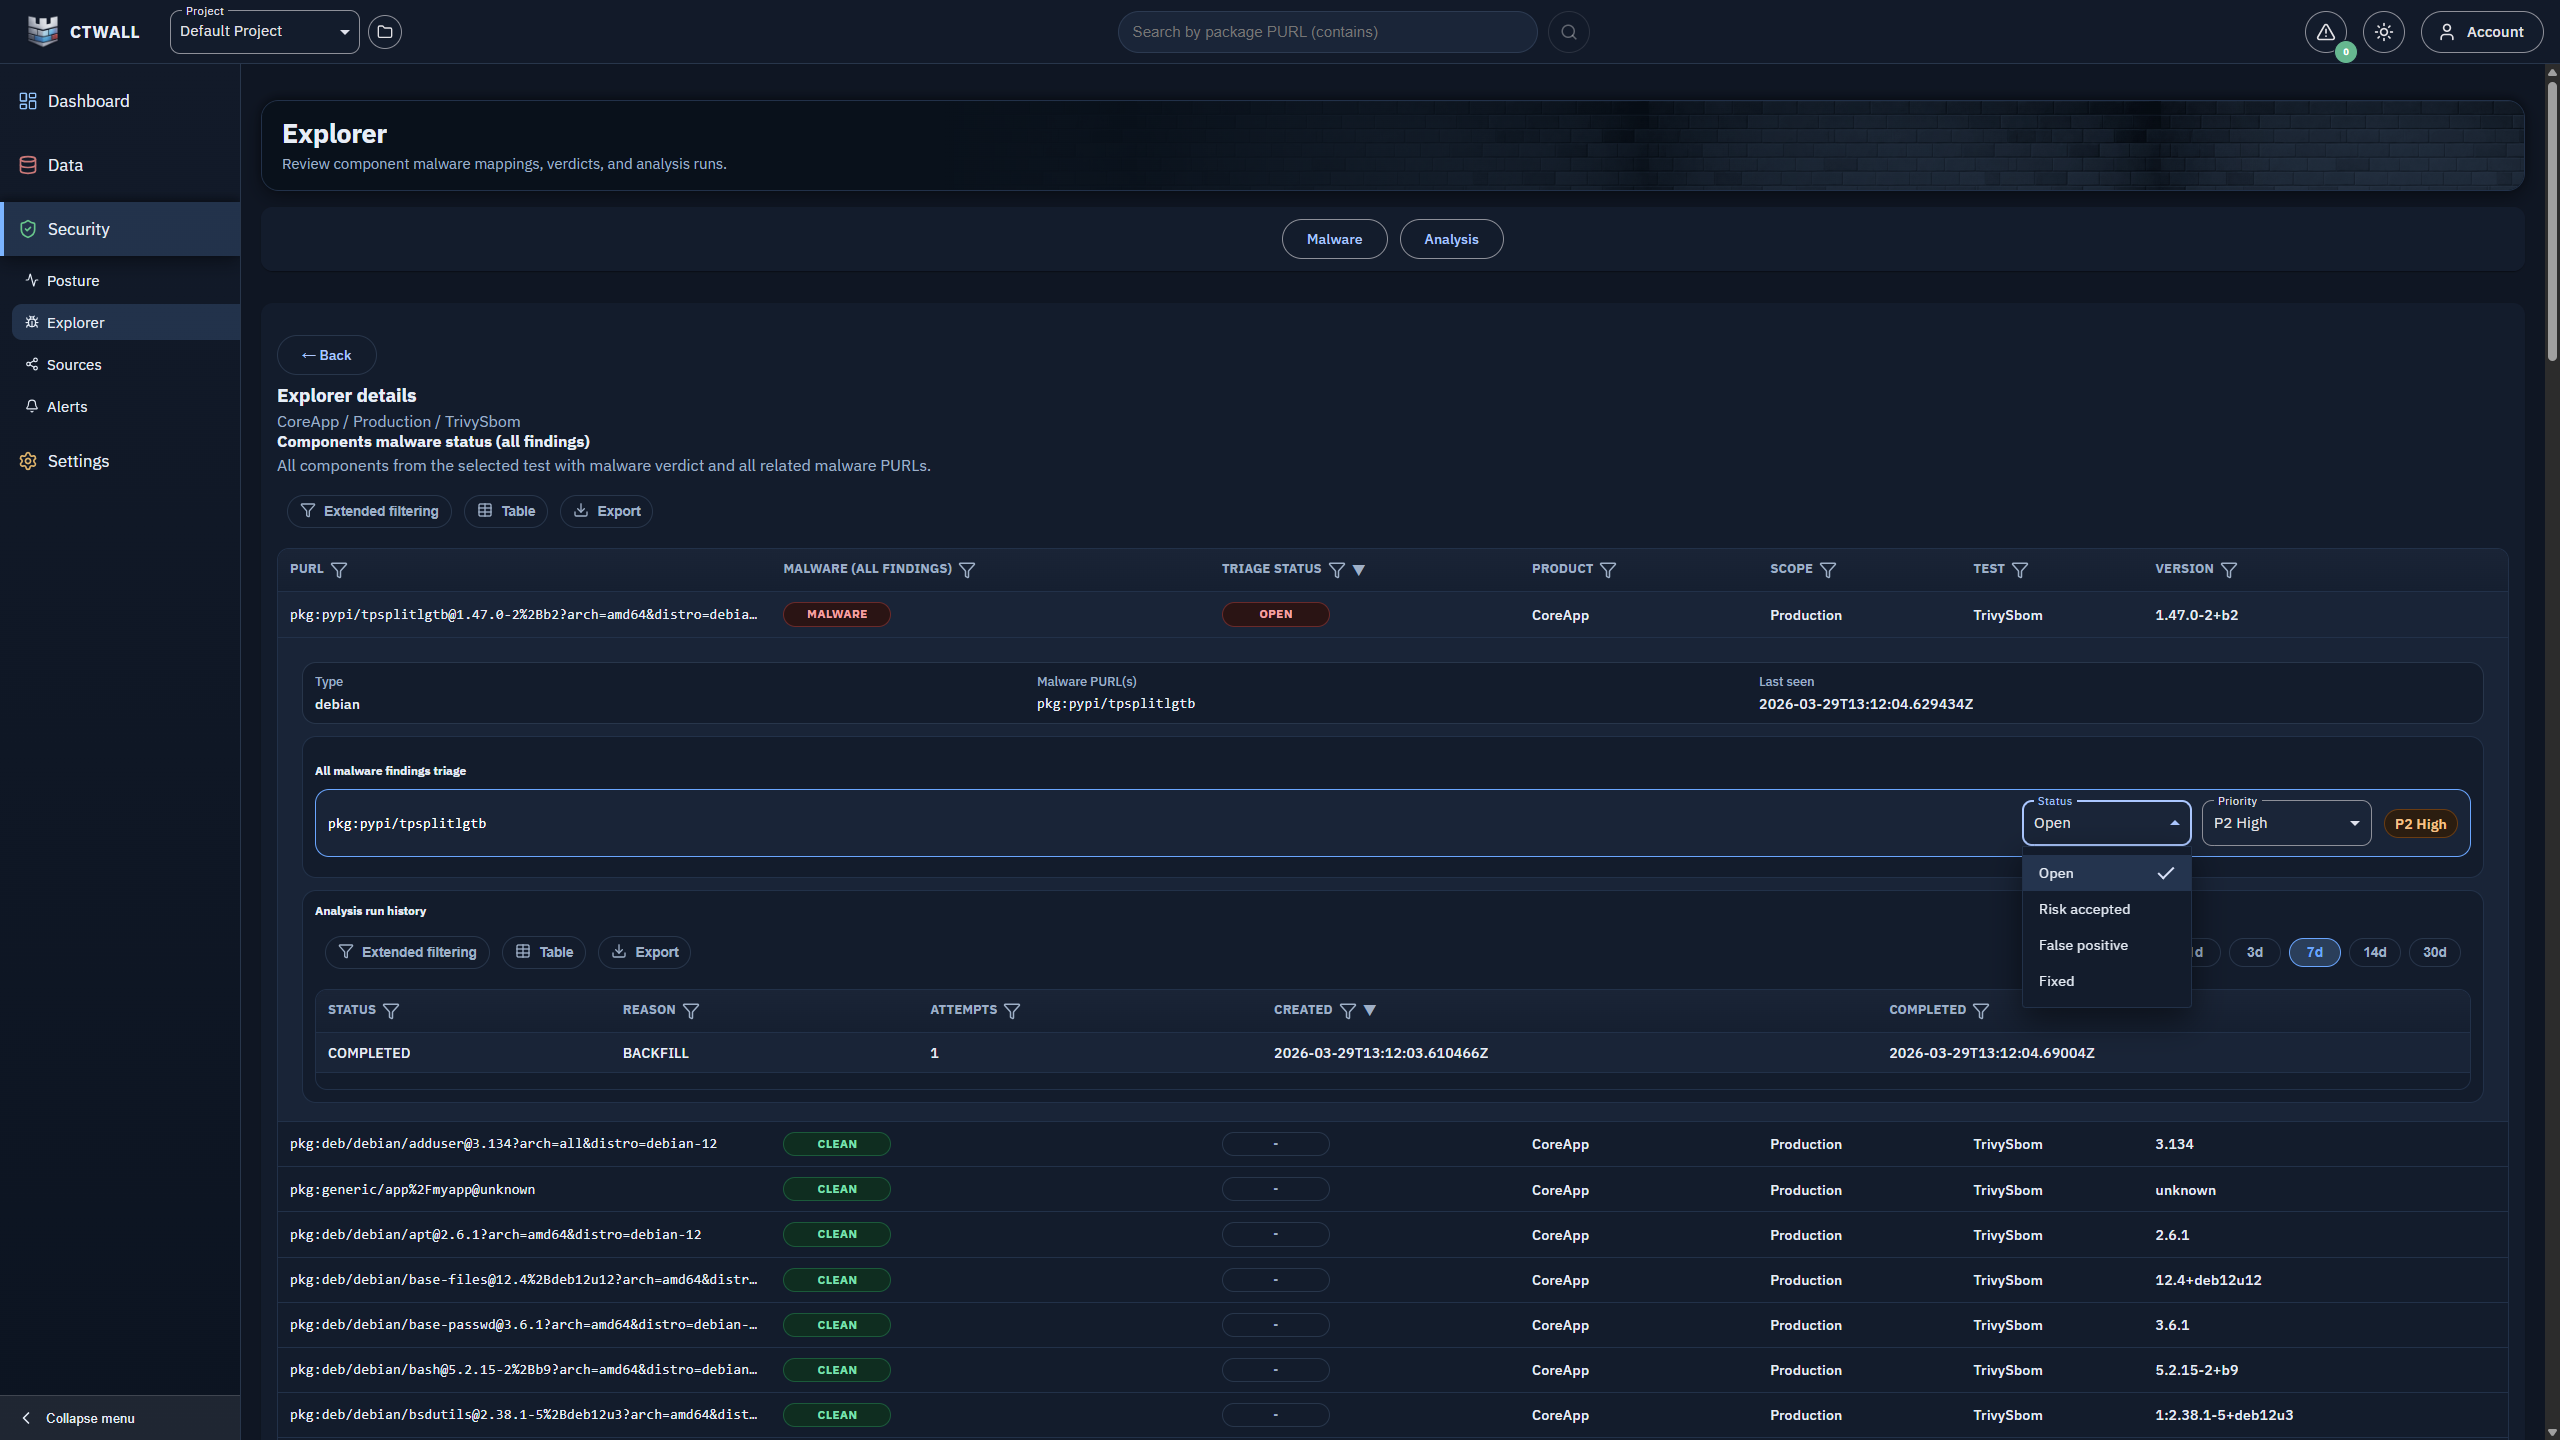 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 indominusrexes/cve-2025-4322-exploit
Critical CVE-2025-4322 exploit for Firefox on Windows enabling sandbox escape and arbitrary code execution. Includes download link and technical…
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
 morfeen01/cve-2017-1182-tn
Malware Analysis Testing
 idanr1986/cuckoo-droid
CuckooDroid - Automated Android Malware Analysis with Cuckoo Sandbox.
 sslab-gatech/avpass
Tool for leaking and bypassing Android malware detection system
 ammaraskar/vscode-github-token-grab-extension
Extension to grab github token from VSCode
 airbnb/binaryalert
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection.
 rythmstick/amsitrigger
The Hunt for Malicious Strings
 cert-polska/mquery
YARA malware query accelerator (web frontend)
 malwaretech/tinyxpb
Windows XP 32-Bit Bootkit