
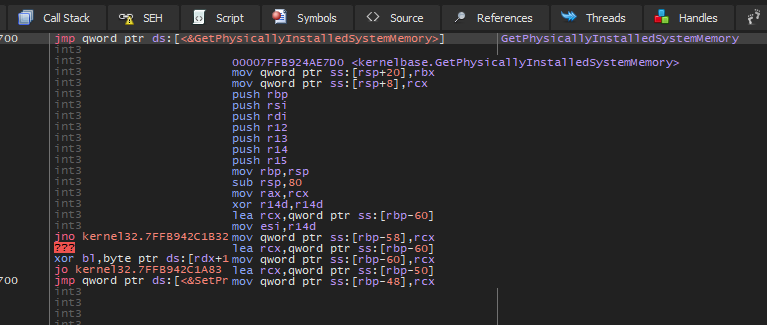
Bypass-Sandbox-Evasion
 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
anti-botbinary-analysisids-ips-evasion+1
140
zeromemoryex/bypass-sandbox-evasionC++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 alphadelta/secure-desktop
Anti-keylogger/anti-rat application for Windows
 roxanne_ardary/safeforge
SafeForge is an open-source mobile app hub built on GitLab that enables developers to build, upload, and share applications in a secure, AI-verified…
 malrev/abd
Course materials for Advanced Binary Deobfuscation by NTT Secure Platform Laboratories
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
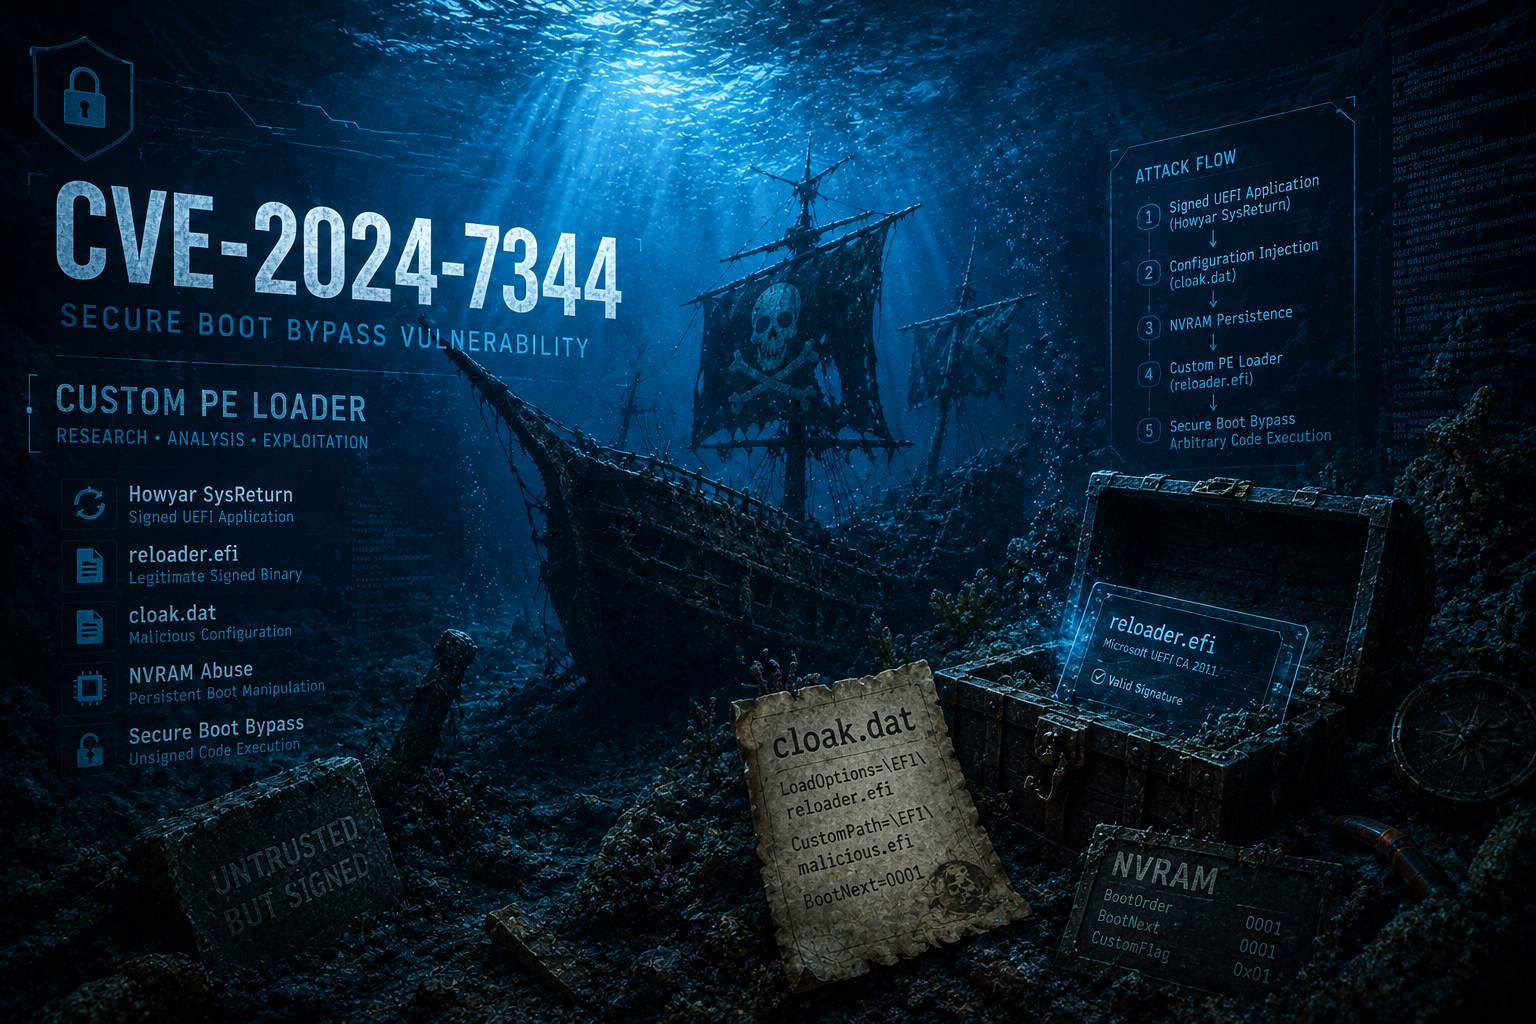 themalwareguardian/cve-2024-7344
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 hassan-pouladi/cisco-fmc-honeypot
Originally a Honeypot for CVE-2026-20131

 not-matthias/amd_hypervisor
Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.
 memn0ps/illusion-rs
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)