
thematrix
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
api-securitydebuggersdynamic-analysis-sandboxing+2
enkomio/thematrixa PE Loader and Windows API tracer. Useful in malware analysis.
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 ashishb/android-security-awesome
A collection of android security related resources
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework

 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
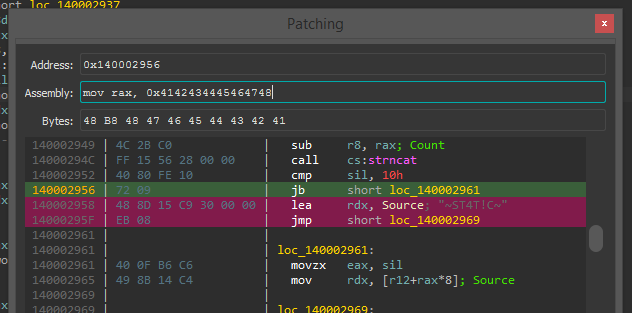 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework