

DarkFox
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
command-and-controlmalware-analysispayload-development+2
25
federicochieregato/darkfoxRemote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
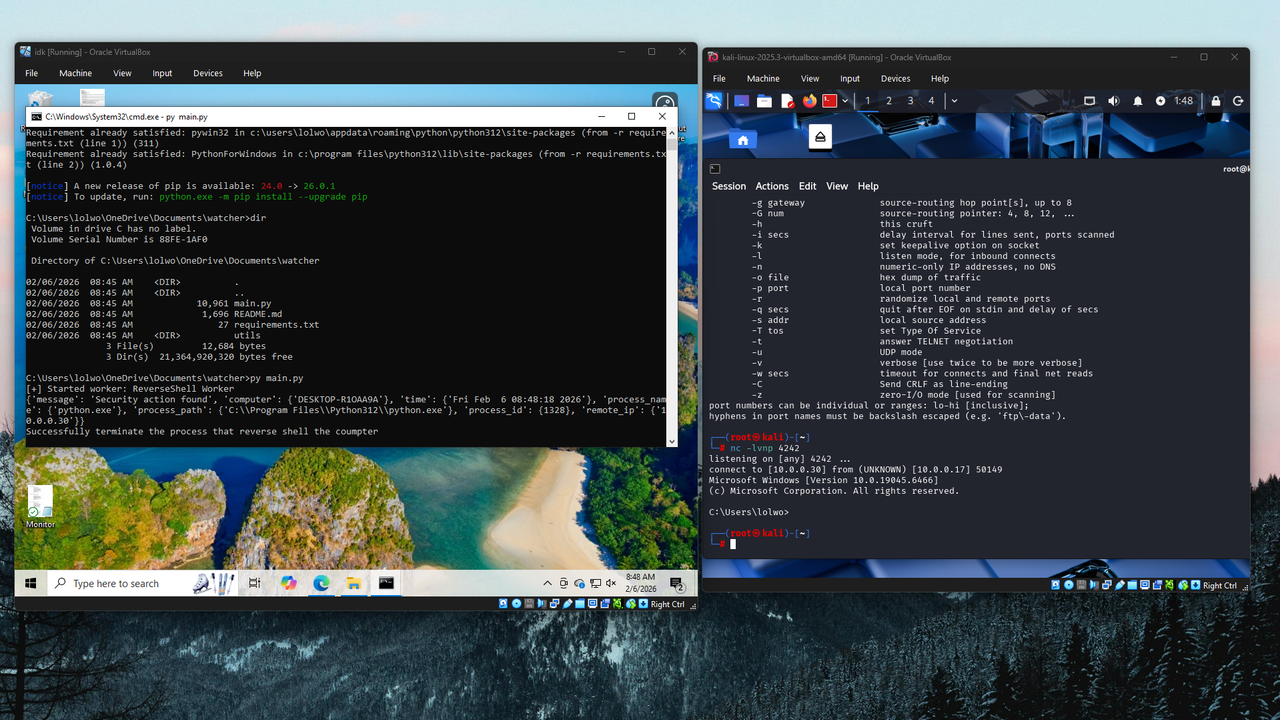 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
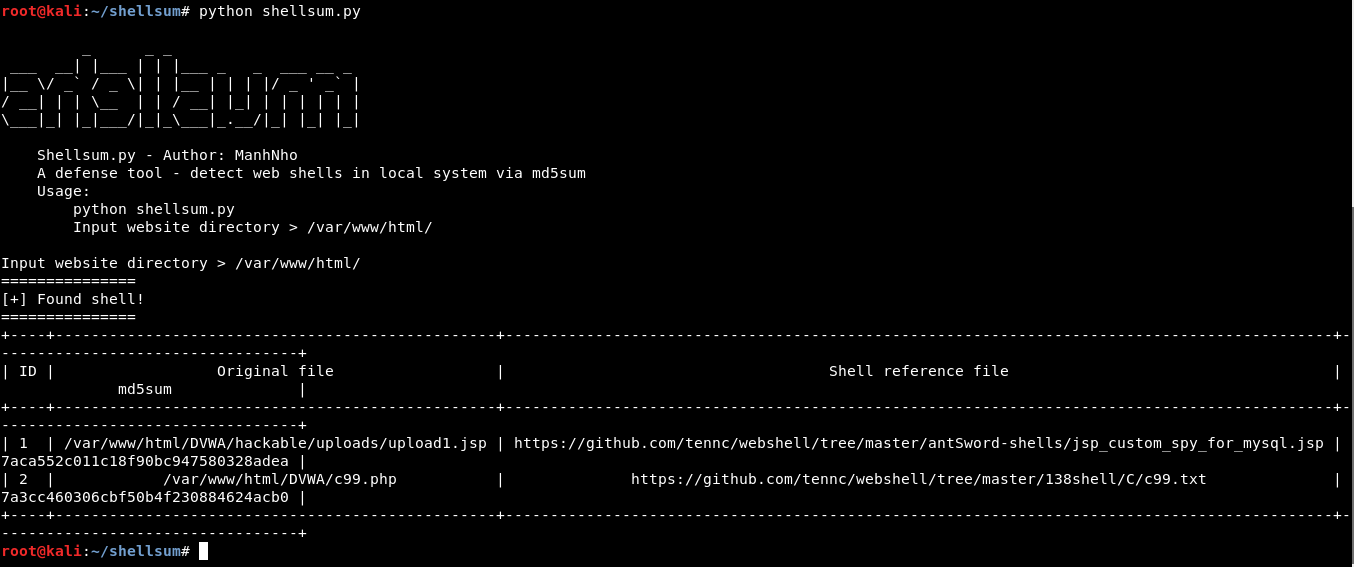 manhnho/shellsum
A defense tool - detect web shells in local directories via md5sum
 emposha/php-shell-detector
Web Shell Detector – is a php script that helps you find and identify php/cgi(perl)/asp/aspx shells. Web Shell Detector has a “web shells” signature…
 hackerschoice/bincrypter
Pack/Encrypt/Obfuscate ELF + SHELL scripts
 tstillz/webshell-analyzer
Web shell scanner and analyzer.
 devjanger/cve-2024-3094-xz-backdoor-detector
Shell script to detect the CVE-2024-3094 backdoor in XZ Utils by checking for malicious code in liblzma build artifacts and identifying affected…
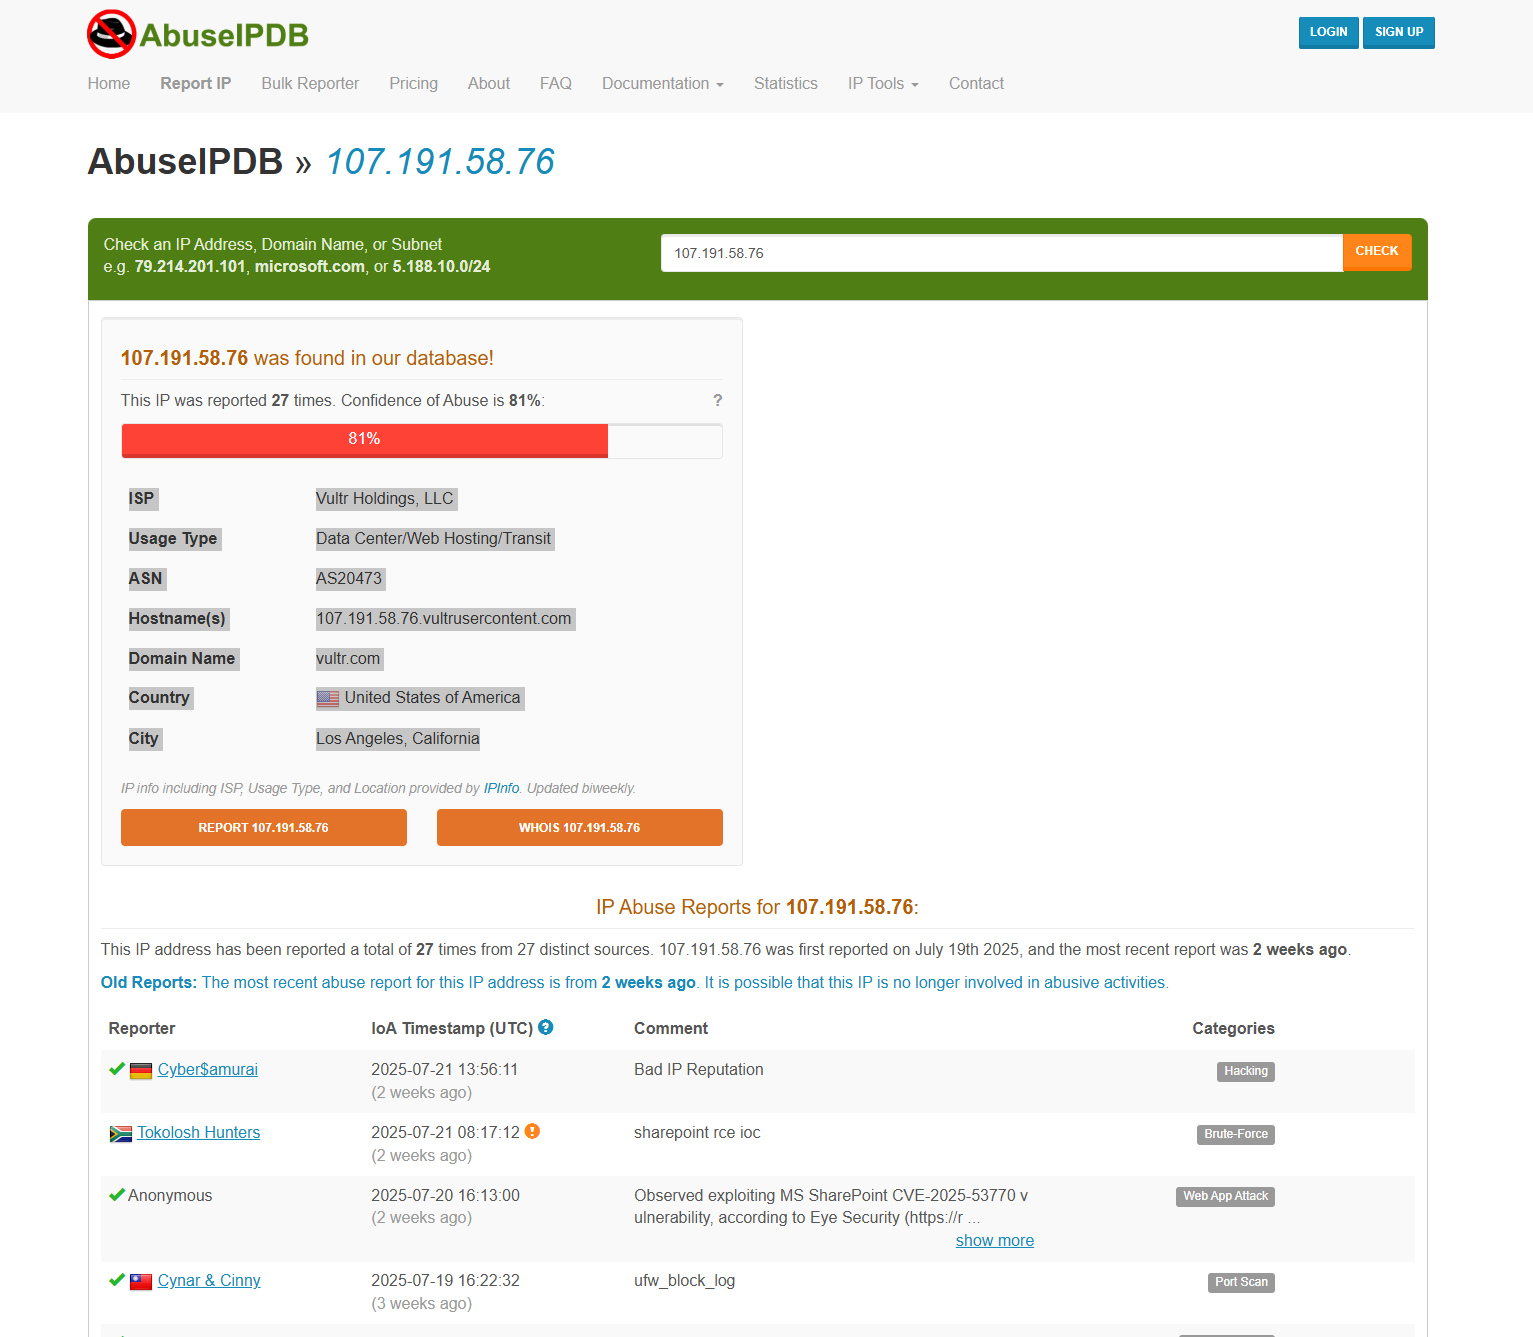 cyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend
Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
