

iMonitor
 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
forensicsintrusion-detectionmalware-analysis+1
835
wecooperate/imonitorEndpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 cdong1012/idapython-malware-scripts
Scripts for automating malware analysis and reverse engineering workflows in IDA Pro, covering binary inspection, static analysis, and code…
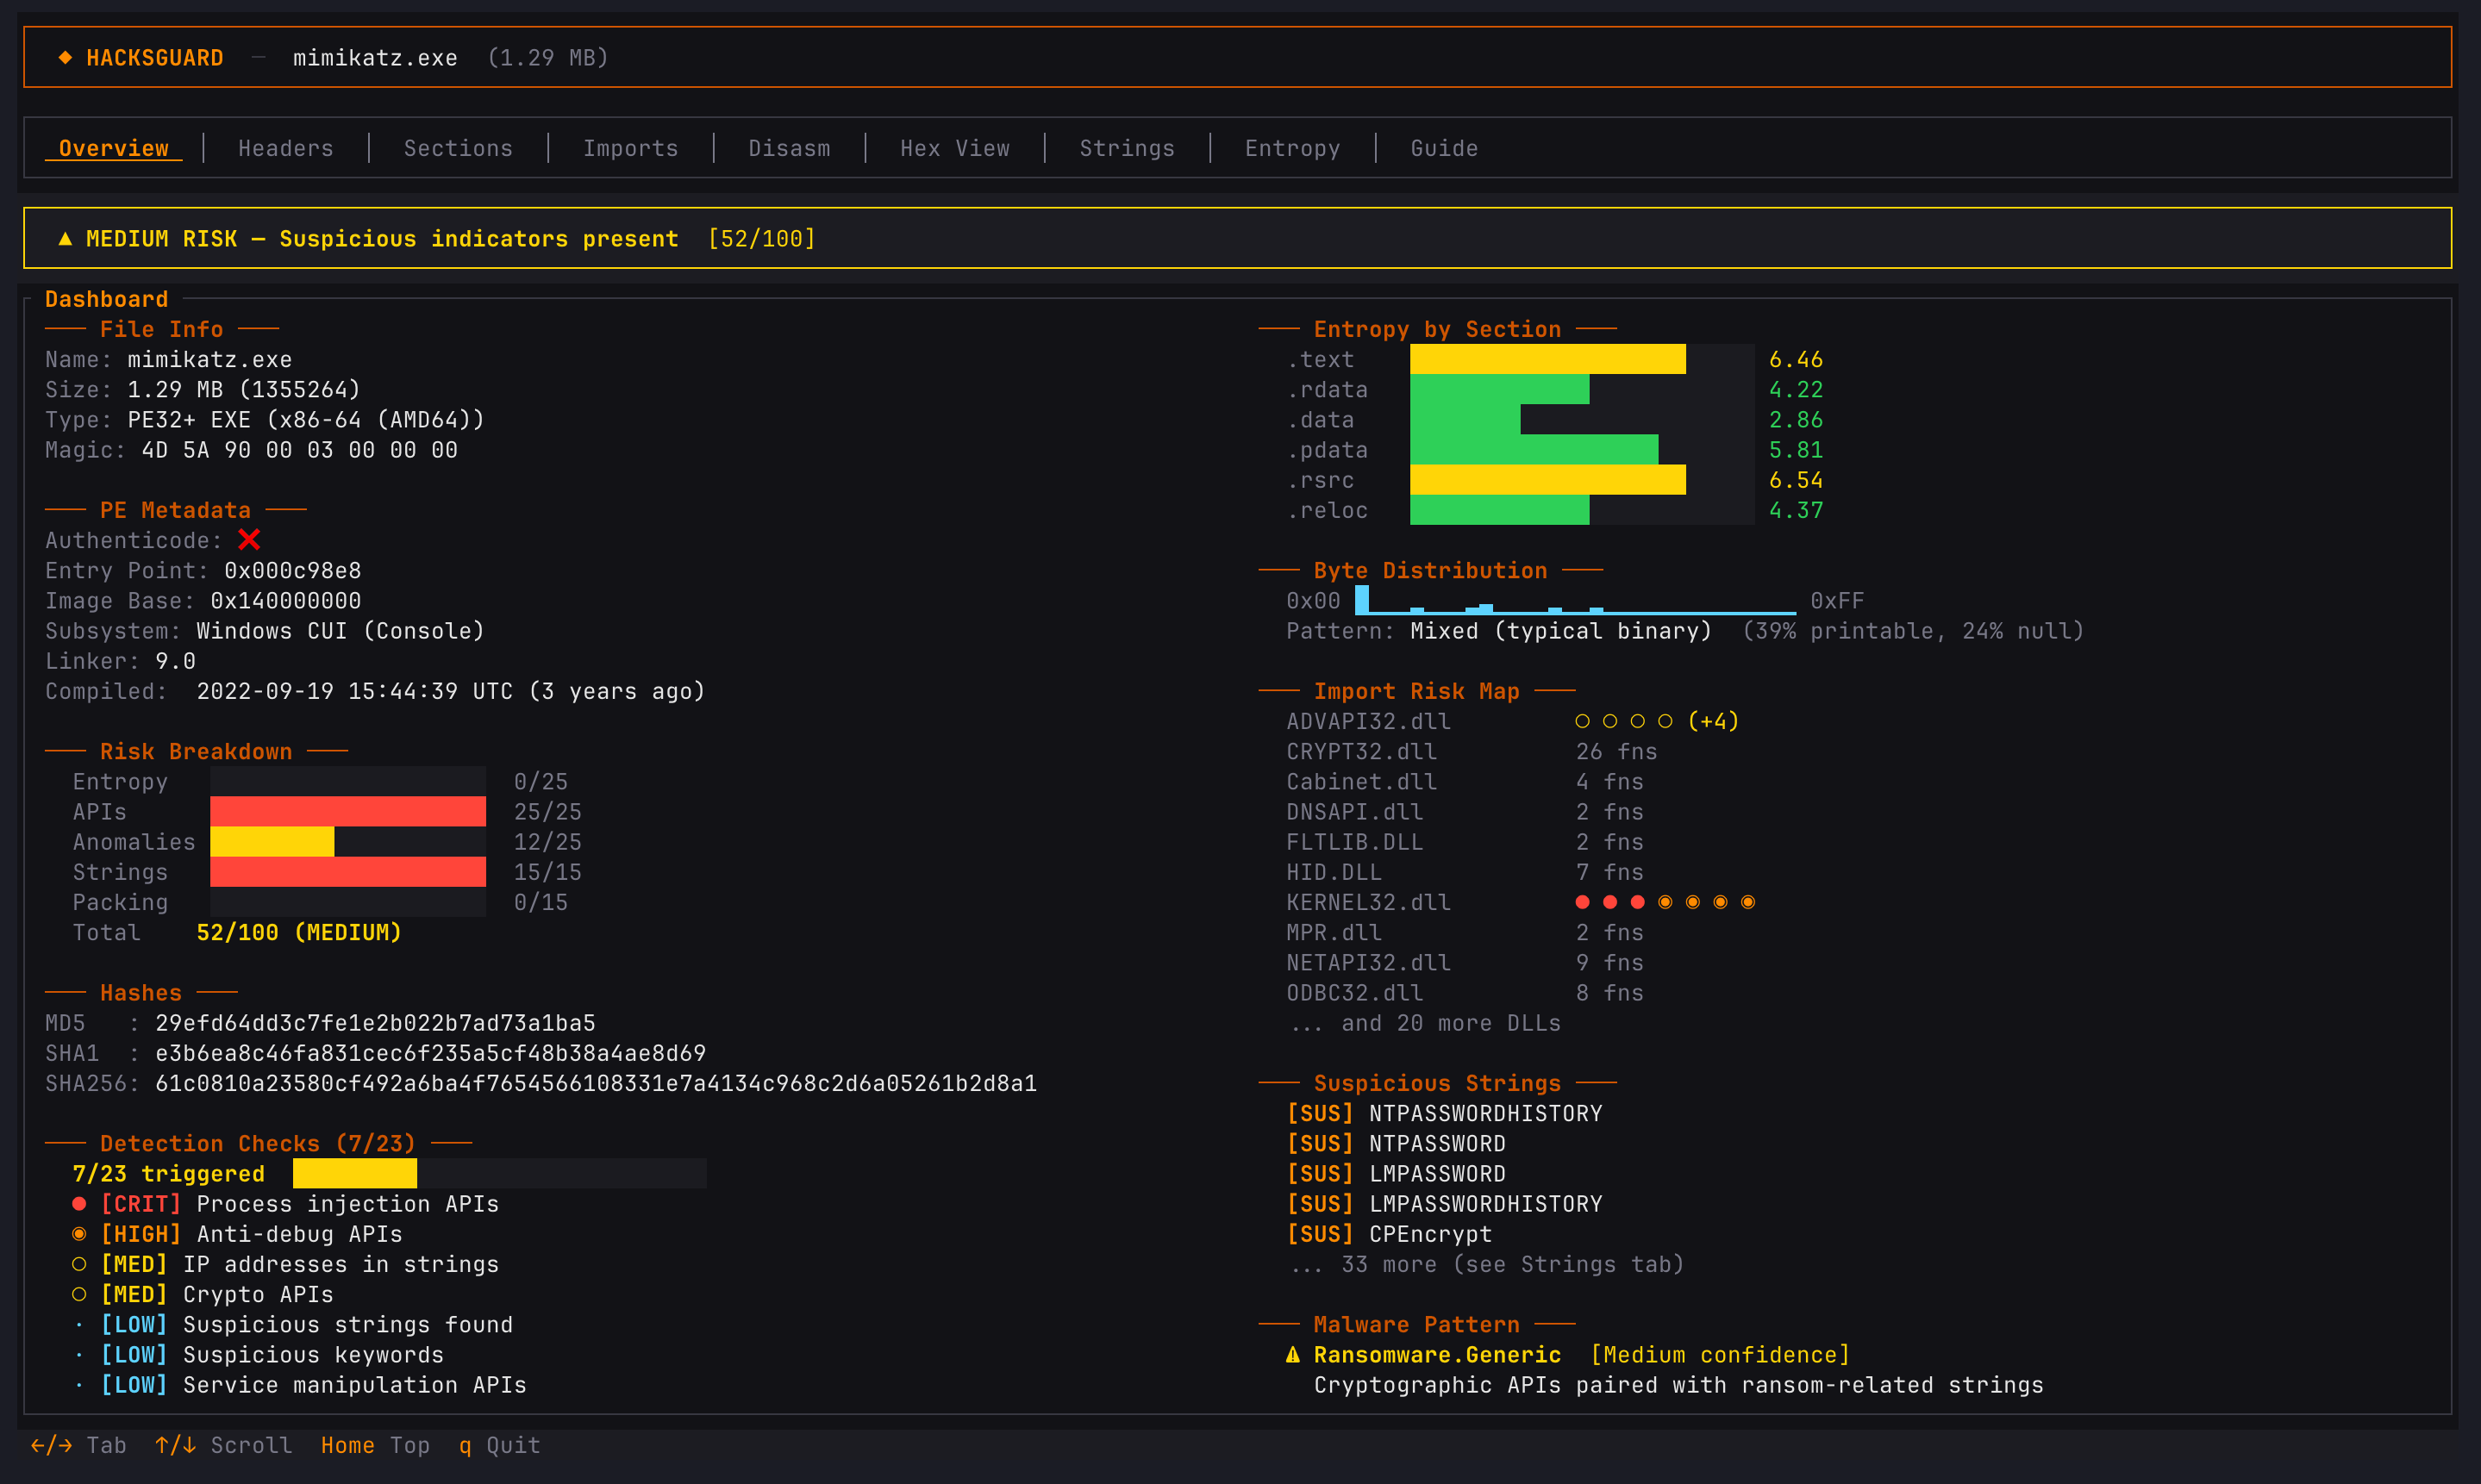 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 ercihan/cve-2026-34621_pdf_sample
Technical analysis of a multi-stage Adobe Acrobat PDF JavaScript sample, detailing environment triage, Acrobat API abuse, and in-memory payload…
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.
 endgameinc/xori
Xori is an automation-ready disassembly and static analysis library for PE32, 32+ and shellcode
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.