
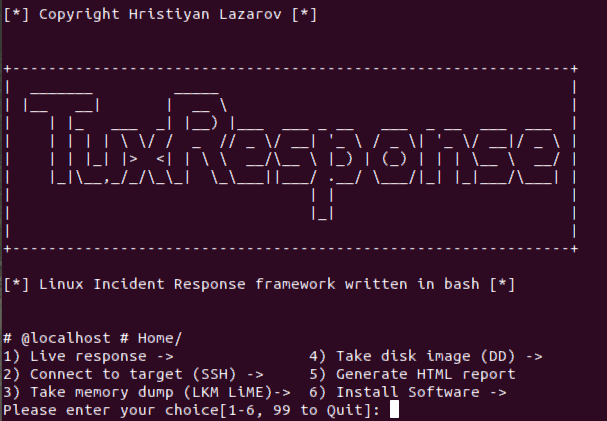
TuxResponse
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
digital-forensicsdisk-forensicsforensics+5
91
la3ar0v/tuxresponseAutomated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 sobri3195/pegasus-malware-scan
Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
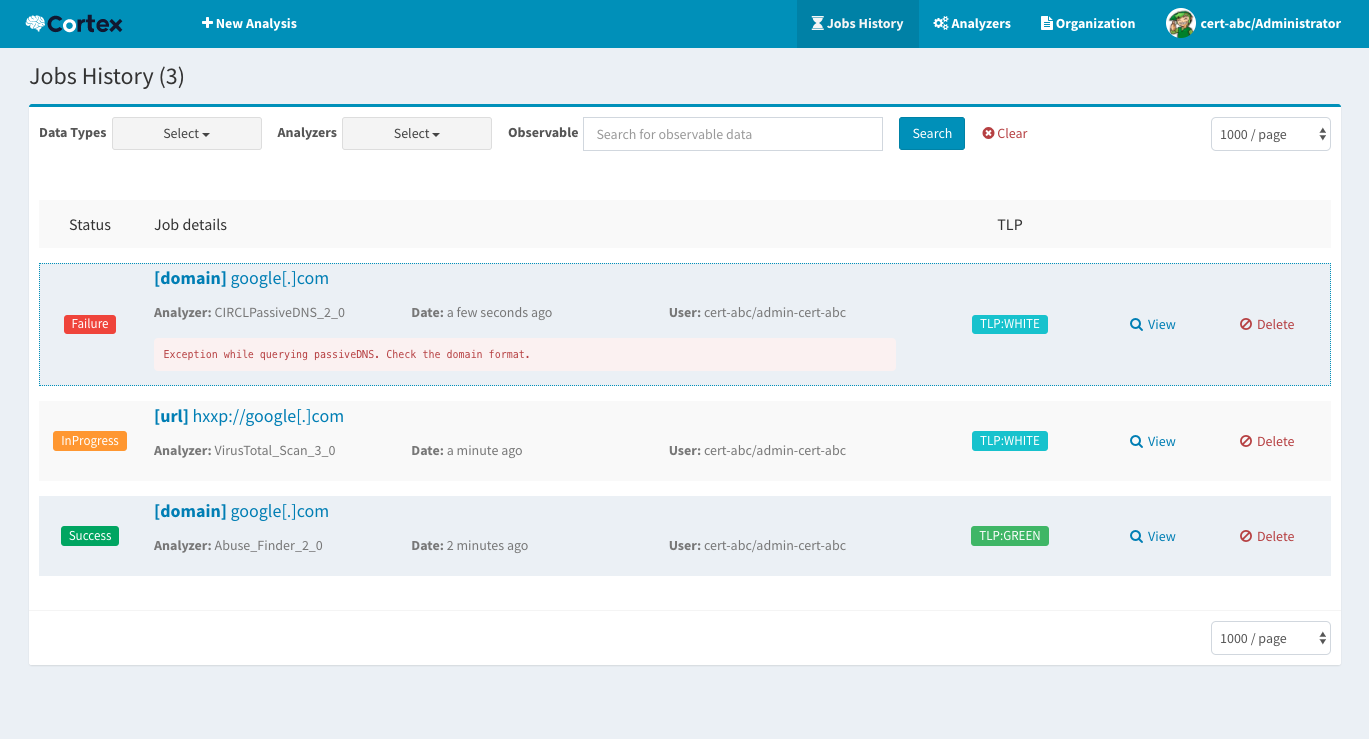 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 techgaun/cve-2025-55182-scanner
Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
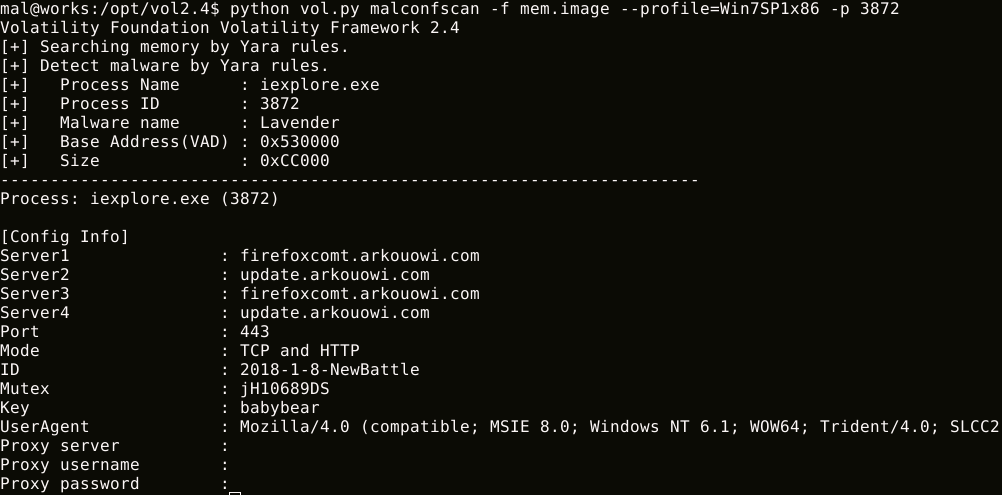 jpcertcc/malconfscan
Volatility plugin for extracts configuration data of known malware
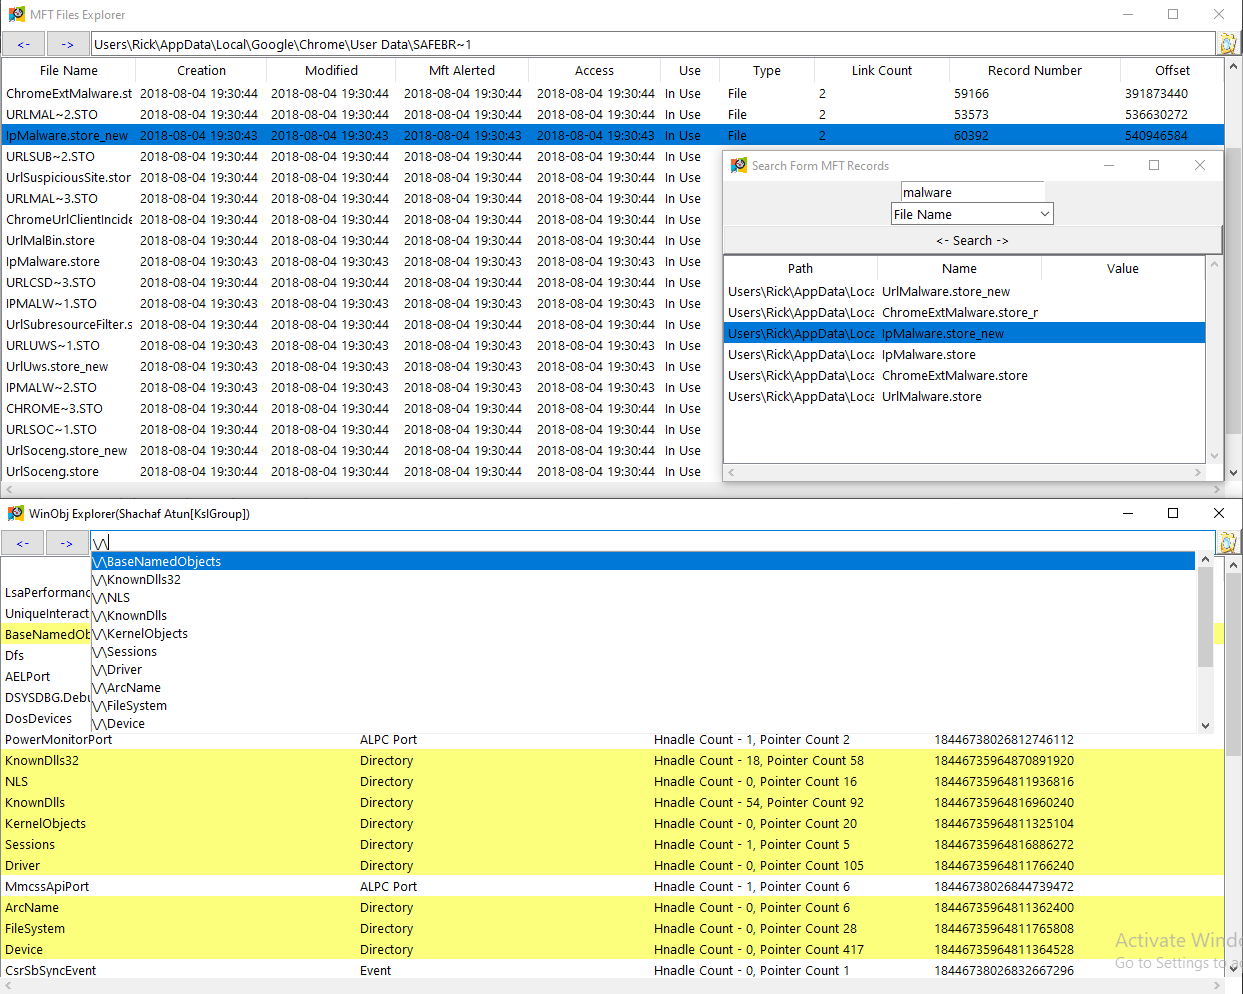 memoryforensics1/volexp
volatility explorer (volatility 2)
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
 tadash10/detect-cve-2024-0762
Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.